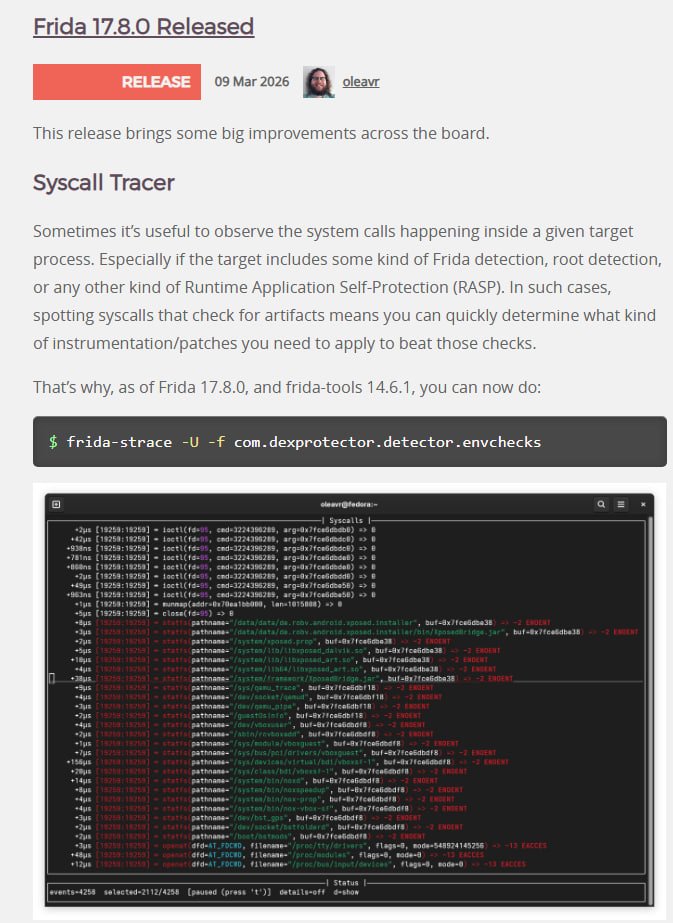
Syscall Tracer🔥🔥
Sometimes it’s useful to observe the system calls happening inside a given target process. Especially if the target includes some kind of Frida detection, root detection, or any other kind of Runtime Application Self-Protection (RASP).
https://t.co/IEl1hTmPjV
#RootlessJailbreak#Detection#Dopamine
We explore 10 real-world iOS detection techniques apps use to detect rootless jailbreaks like Dopamine — from XPC tricks to filesystem checks.
We built a Frida script to dynamically work around each one!
Watch now: https://t.co/Nghh3vDgg3
Introducing https://t.co/NghsaMWaBM, a lightweight Android library designed to detect signature bypass capabilities commonly used by tools such as MT Manager, NP Manager, LSPatch, and others. Enhance app's security by preventing unauthorized modifications. #AndroidSecurity
Ever wondered how iPhones can be hacked remotely?
Watch my latest YouTube video right here on Twitter. My goal with this video is to give you a sense of the insane amount of skill and (engineering) effort that is required to find vulnerabilities in iPhones.
At the end of the video, I hope you’ll appreciate the complexity of the task, while realising it’s not simply magic.
We’ve been cooking a fantastic new IDA Pro Training Program, and it is now available on our website! Check the schedule and register today 🌐 https://t.co/zv5nIlbuL2
#LearnIDA#idapro
To facilitate reverse-engineering of large programs, vulnerability research and root-cause analysis on iOS, Android, and other major platforms, @myr463 and @Hexabeast released Frinet, a tool combining Frida with an enhanced version of Tenet.
https://t.co/d0epwjylji
Hex-Rays @HexRaysSA released a tool to simplify mba expressions but no published blog right now.
".. achieve orders-of-magnitude better performance than existing state-of-the-art solutions." (looking at you d810 😆)
https://t.co/Sl5WbYrSe2
Uploaded a new video where we have tried to explain few techniques for bypassing frida using frida itself. For explaining these techniques, we have used r2pay android app from MSTG crackme.
@enovella_@fridadotre#frida#antifrida
https://t.co/P3MusZdTct
It's a pleasure to announce the release of open-obfuscator: a free and open-source solution
for obfuscating Android and iOS applications (Java/Kotlin, C/C++/Objective-C)
https://t.co/nBYleNkcdA
https://t.co/epzNK1fqKW