📢📢📢 Attention bug hunters!
Want to know more about how brutecat found a vulnerability in Google’s internal APIs, bypassing authorization to exploit the GFile library to gain access to internal filesystems and storage?
If yes, check out his blog post 👇
https://t.co/ehwrnqHJlX
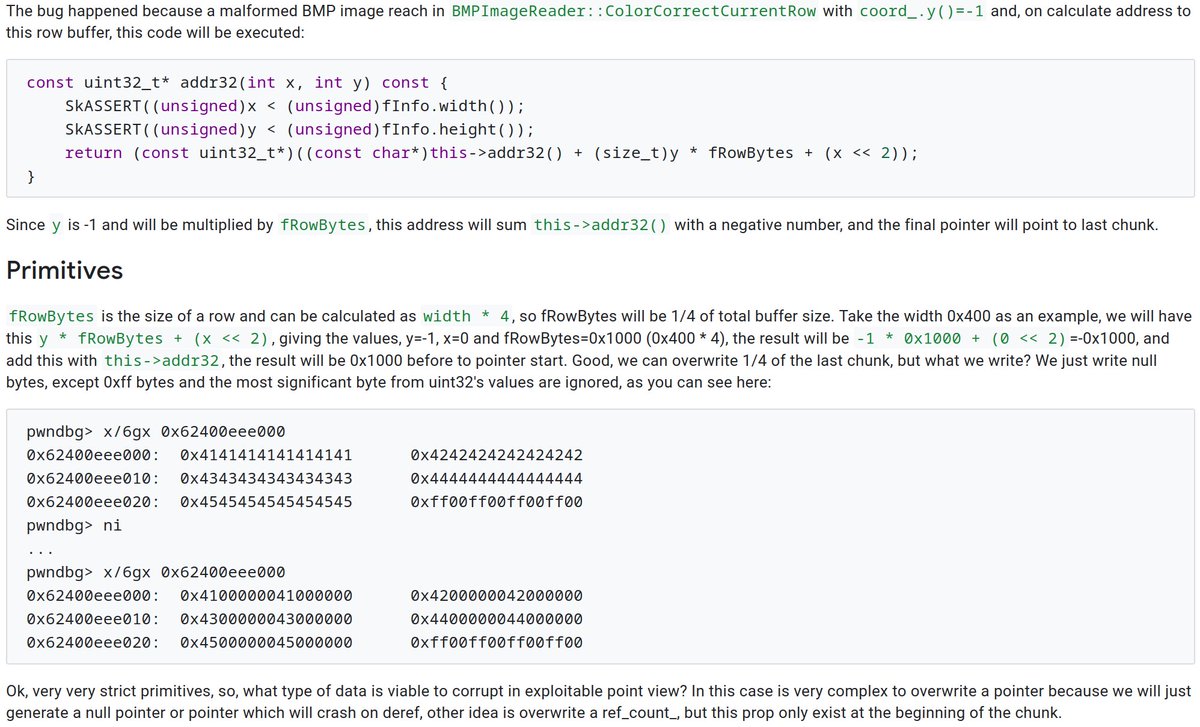
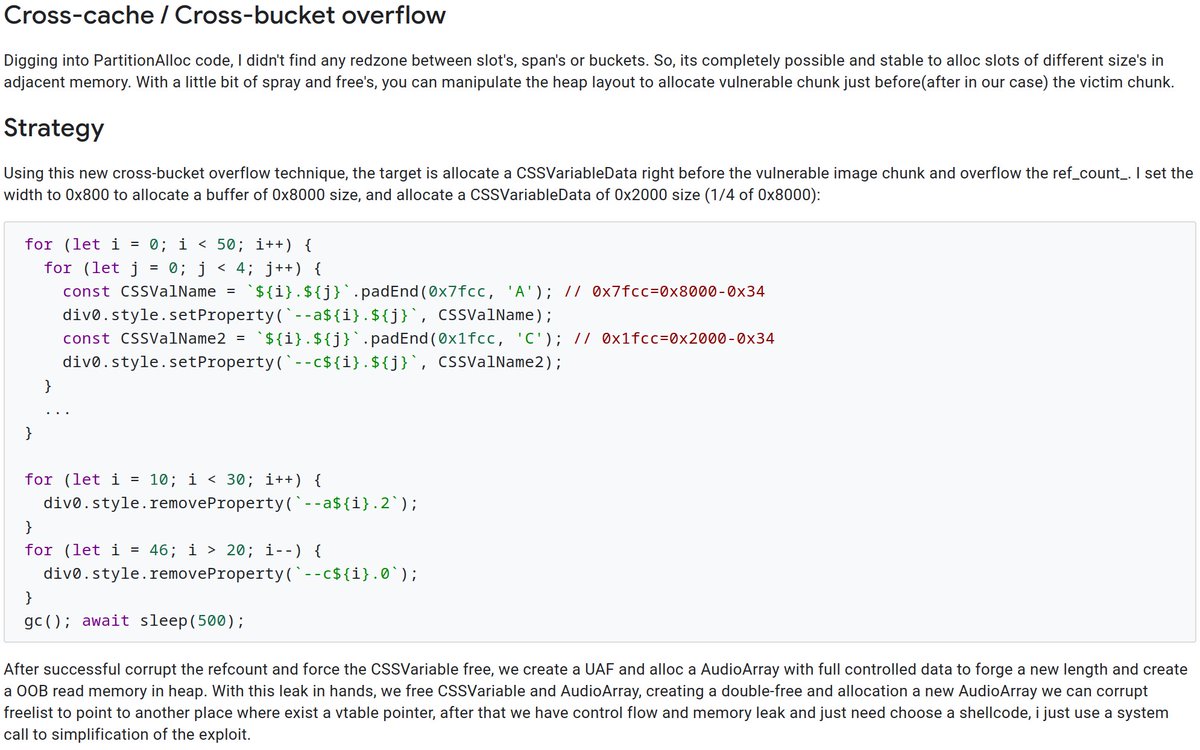
(CVE-2024-1283)[1521893]Heap buffer overflow in Skia(crash when a BMP image contains an unnecessary EOF code) is now public with RCE exploit and novel cross-cache technique.
https://t.co/VcE917EJqS
https://t.co/yaHTKKKAWy
@r3tr074
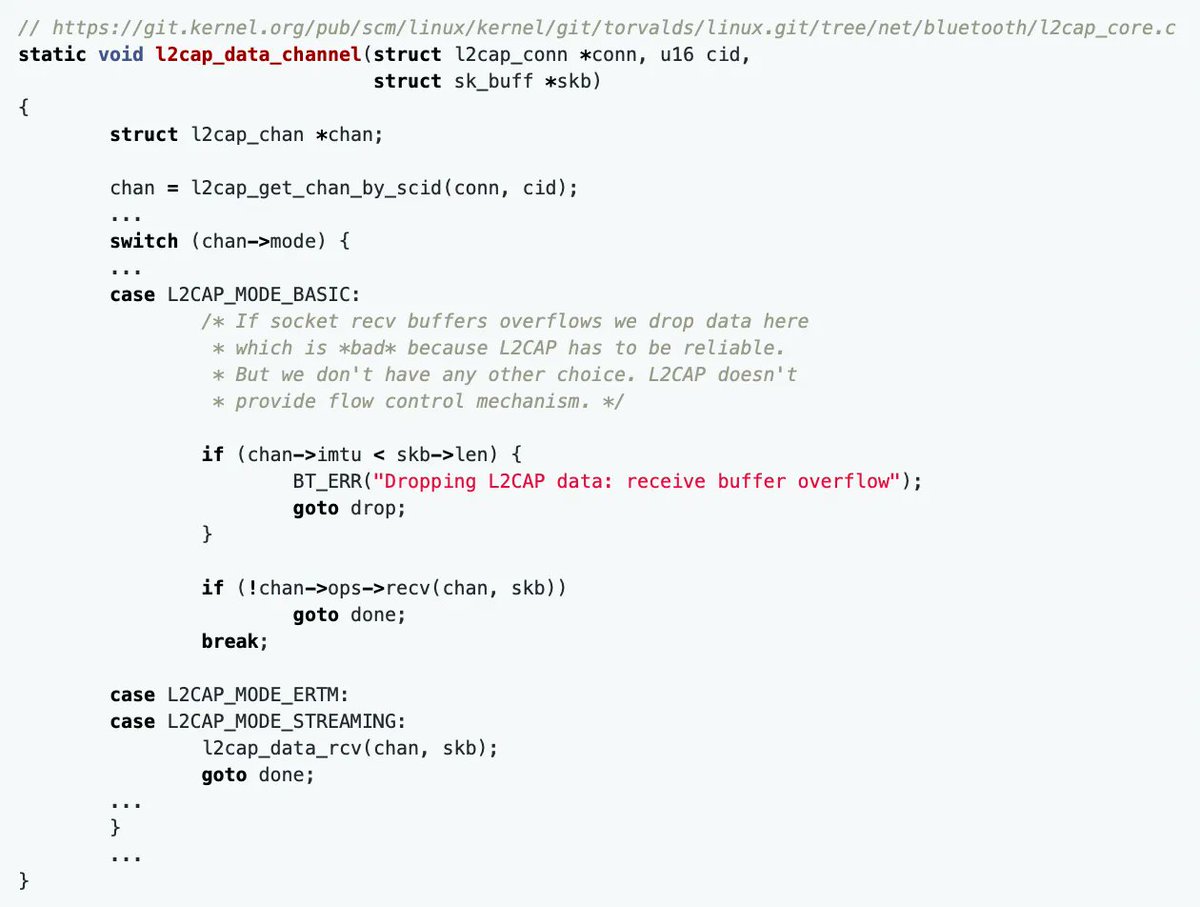
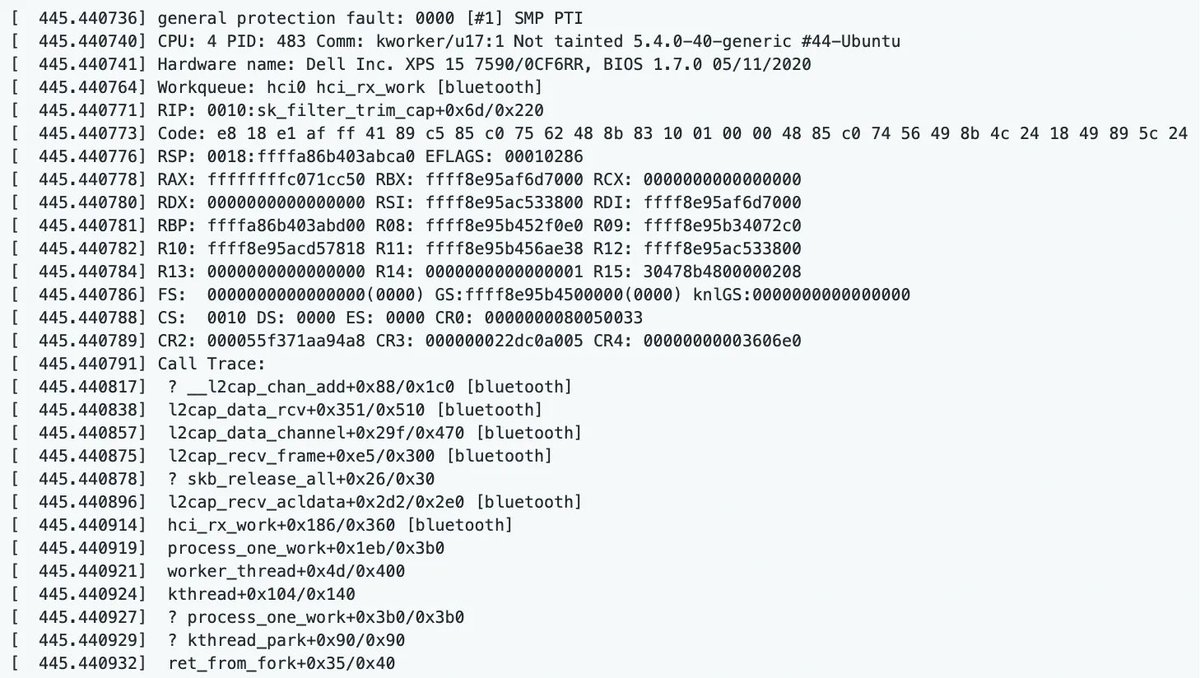
BleedingTooth: Linux Bluetooth Zero-Click Remote Code Execution.
BleedingTooth is a set of zero-click vulnerabilities in the Linux Bluetooth subsystem that can allow an unauthenticated remote attacker in short distance to execute arbitrary code...
PoC
https://t.co/TnaR0LU6UH
Video of my PoC for CVE-2023-43641: out-of-bounds array access in libcue. libcue is used by tracker-miners, which automatically scans new files in ~/Downloads, so the bug is triggered by downloading a file.
New @Qualys#Security#Advisory!
Looney Tunables: Local Privilege Escalation in the glibc's https://t.co/dKBAL8la7D
(CVE-2023-4911)
https://t.co/SNVHiFUrxk
#Fortinet published a patch for CVE-2023-27997, the Remote Code Execution vulnerability @DDXhunter and I reported. This is reachable pre-authentication, on every SSL VPN appliance. Patch your #Fortigate. Details at a later time. #xortigate
Random exploit dev tip of the day: If you want to do JOP on ARM, take a look at the "scatterload" function. Allows you to call arbitrary functions with arbitrary arguments. In a loop. A pretty powerful and a rather generic primitive that I didn't see mentioned anywhere else.
Demonstrating CVE-2022-37958 RCE Vuln. Reachable via any Windows application protocol that authenticates. Yes, that means RDP, SMB and many more. Please patch this one, it's serious!
https://t.co/ikOrTvQIJs