😬😬😬😬
“Microsoft has notified customers that it’s missing more than two weeks of security logs for some of its cloud products, leaving network defenders without critical data for detecting possible intrusions.”
https://t.co/gU7fQi1jRI
Viktig spleis i nærområdet, til en raus men fattig klubb som prøve å gjøre en sosial innsats for byen. Sagene IF - Stjerner i striper https://t.co/KDaV4J2sPi
How do you draw a pride flag? 🤔
With SCIENCE!
This flag is a composite of NASA imagery of phenomena from Earth and far, far beyond it. Details below ⬇️
Credit: Rachel Lense
As you've come to expect from @thegrugq, his words ring true in all things hacking. His keynote on Systems Alchemy: The Transmutation of Hacking at the t2 conference in Finland is brilliant and worthy of your time of this excites you
https://t.co/jIcbxXhUck
A critical vulnerability (CVE-2024-24919) has been discovered in Check Point Security Gateways with Remote Access VPN enabled, also referred to as the 'Mobile Access' blade.
We've observed attempts of exploitation in customer environments since April 30: https://t.co/qlrezFm6lK
mnemonic has responded to an incident involving adversary use of Visual Studio Code's remote development extensions: https://t.co/dRNP9WQX0g
#mnemonicblog
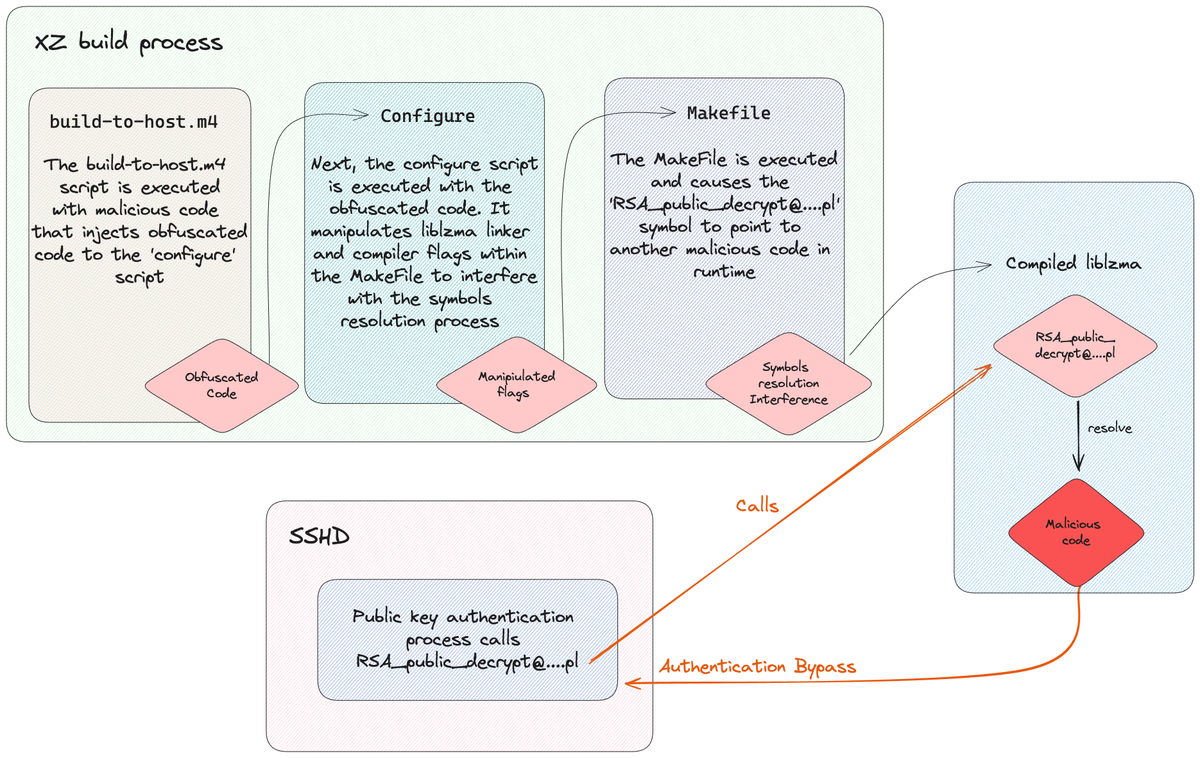
I've been looking into how the xz backdoor works and drew this sketch to make it easier to understand.
I'll update it as new information comes to light ✨
In what it calls an “unprecedented global threat,” Microsoft says Russian hackers who breached its network in Jan. have expanded their access in follow-on attacks that are targeting customers & have compromised the company's source code & internal systems
https://t.co/tFCEOCvT1c
Late night blog! Following Volexity's discovery of 2 zero days in Ivanti Secure Connect/Policy Secure announced yesterday CVE-2023-46805/CVE-2024-21887 , @Mandiant is sharing details and Yara for a stealthy passive espionage backdoor ZIPLINE. https://t.co/qSkb6wjwyB
With it being near impossible for foreign journos to report from Gaza, and local journos under bombardment, it's been difficult to cover this conflict. Still, media orgs have published imp investigations that shed light on how Israel has been conducting this war.
A thread:
🚨 Absolutely insane breach info out of Microsoft.
Now that the Storm-0558 flurry has slowed down I wanted to deep dive into what we know and what we don't. 👇
mnemonic researchers found a 0-day RCE #vulnerability within Ivanti Sentry tracked as CVE-2023-38035.
Exploitation allows an unauthenticated threat actor to read and write files to the Ivanti Sentry server and execute OS commands as root:
https://t.co/UbUZQMxN6B
#mnemonicblog