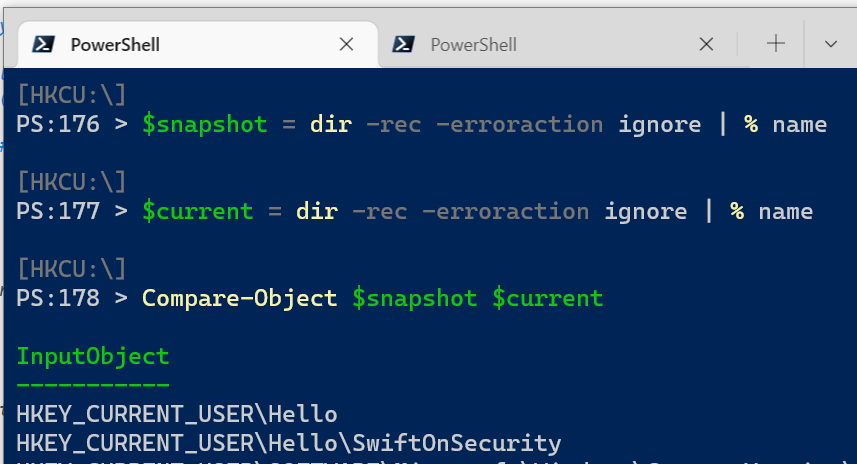
If I could run a Windows command on multiple end systems, collect & process the results, I would probably run a REG QUERY [..] for this key in my network, put all the results into a list, sort (|unique) it & just scroll over it.
This would be a hunt that goes far beyond #Follina
Here some good sources to learn malware development.
https://t.co/Mq41nkcxpy - Windows malware dev
https://t.co/gXYDjcHTVG - Linux Rootkit malware dev
https://t.co/uG5sNpxc8E - Windows malware dev
Huge thanks to all the blog authors
My talk, Python for Threat Intelligence, is now available to watch on YouTube. Check it out if you want a look how my team leverages Python for our day-to-day analysis, some of the packages we use, and how we approach development in general. https://t.co/6GR8PlQ00i
Would you be interested if I do a video series on basic OS Internals? #DFIR#Cybersecurity
If this poll reaches at least 1K of interaction, I will start recording. Feel free to drop suggestions, otherwise I'll prepare a draft ToC. Focus will be on the Windows Operating System.
as M$ said, IE should be totally removed from Win11 & redirect to M$ Edge.
Fun Fact: attackers still can launch IE on Win11 by COM interface {0002DF01-0000-0000-C000-000000000046}
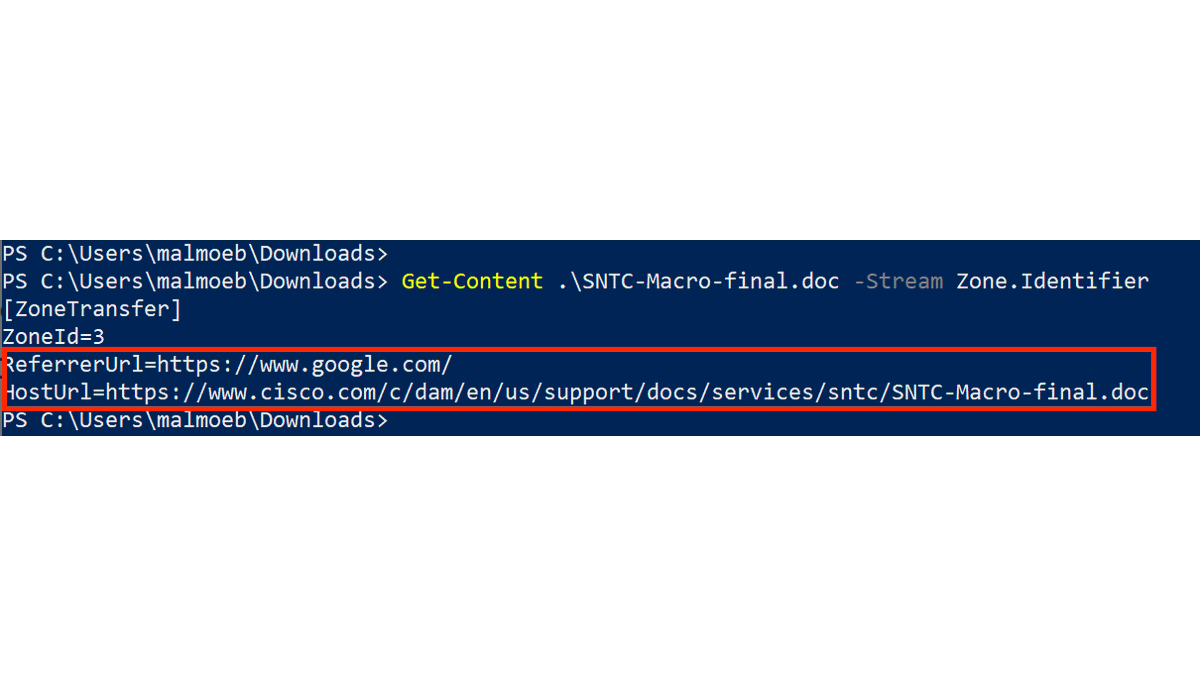
1/ Have you known that the "Zone.Identifier" Alternate Data Stream (ADS) not only records whether a file was downloaded from the Internet (ZoneId=3), but also from which URL and the Referrer from which the page was visited?
PS> Get-Content <filename> -Stream Zone.Identifier