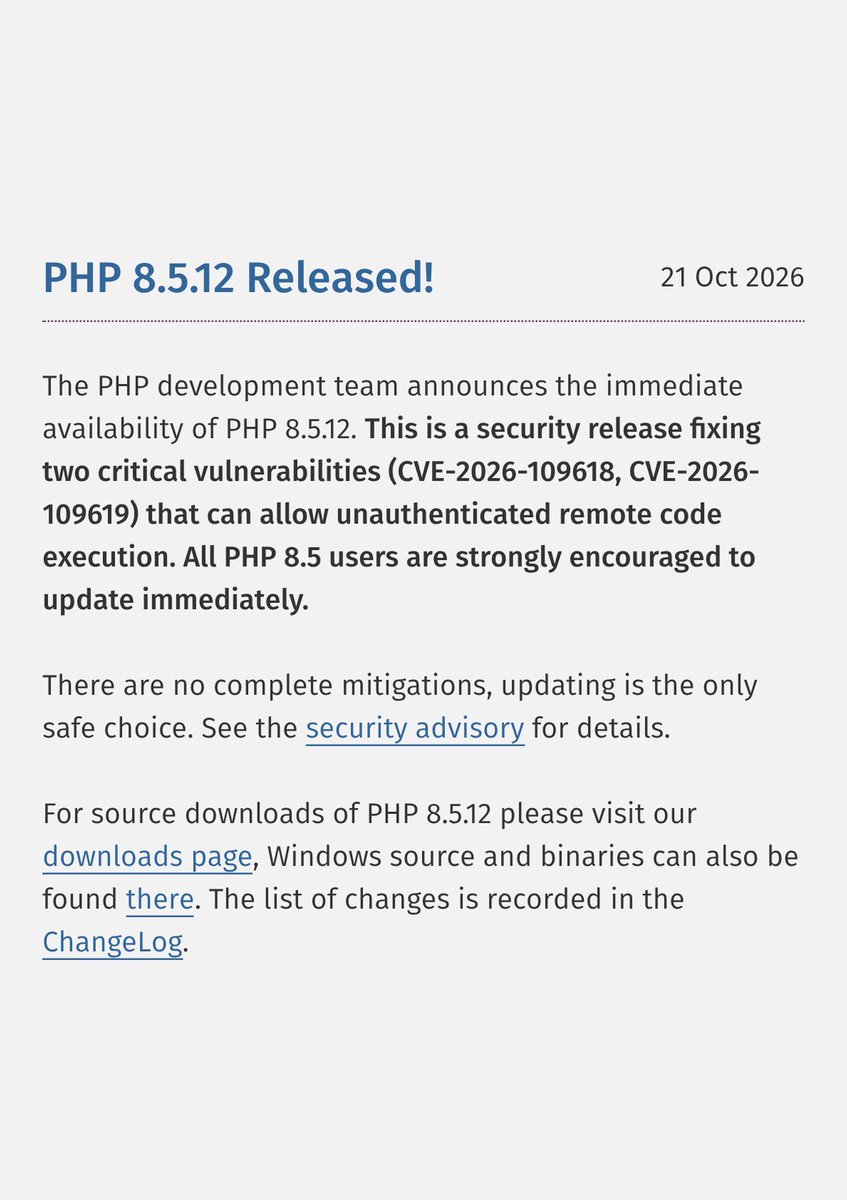
‼️BREAKING: PHP has released its fix for the two leaked flaws, which can let attackers run code on servers without logging in.
"There are no complete mitigations, updating is the only safe choice," PHP says.
Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now.
PHP says Apache with mod_php is most at risk, with a demonstrated exploit that fires before any application code runs.
PHP 8.1 and older get no official update, though PHP has published source backports for 7.4, 8.0 and 8.1.
Imagine you wake up and:
- PHP has two critical vulnerabilities, rated 9.2, and exploitation has already started, even before the fix was published. There's not fix for old versions... https://t.co/OrhEWKjwDz
- Node.js has four high vulnerabilities, including arbitrary code execution. https://t.co/LQdFMWmNPE
- Eight TLS intermediates have private keys of 3 to 8 bits. I don't believe in conspiracy theories, but... https://t.co/syUV8gdZoI
All of this is in the field. Millions of machines are vulnerable. Most of them will not be patched in the near future and you can't really trust TLS anymore...
The state of security is really, really frightening. And it won't get better anytime soon. 🫠
PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free.
We are seeing early attacks emerging and are updating mitigations as new vectors show up.
This is a STOPGAP only. Patch as soon as @ThePHPF releases the update at 14:00 UTC today.
🚨 Many websites and apps may go dark as PHP prepares critical fix.
Nearly 70% of all websites including Govt systems, banks, telcos could be at risk of getting compromised.
🚨 10:00 AM ET: A 15-MINUTE BATTLE FOR THE ENTIRE INTERNET BEGINS.
Today, a critical zero-day vulnerability (CVSS 9.2) in PHP—the backbone running nearly 80% of the web—goes public at 10:00 AM ET / 7:00 AM PT.
Forget the technical jargon. Here is what actually happens:
The second the patch drops, hackers will use AI to reverse-engineer the fix in seconds and unleash automated exploits worldwide within 15 minutes.
This is not just a problem for developers.
When e-commerce sites, apps, and platforms collapse, your leaked home address, passwords, and credit card numbers flood the dark web.
⚔️ The brutal reality today:
Engineering teams deploying patches in minutes vs. Oblivious companies gutted before lunchtime.
🛡 3 things you must do to protect yourself right now:
1. Turn on Two-Factor Authentication (2FA) across all critical accounts.
2. Stop password reuse immediately.
3. Beware of fake "emergency password reset" phishing emails flooding inboxes today.
Cyber warfare changes forever this morning.
Bookmark and share this to keep your team and family safe.
In the last 24 hours alone, I've seen.
1. iPhone 11 through 16 are apparently vulnerable to remote attacks.
2. SSL certificates are broken until browsers remove eMudhra CA.
3. PHP RCE (php2shell)
One is a leaked remote unlock capability for the most common phones on the planet.
One is a broken link in the certificate authority system that underpins the entire encrypted web and another is a core language vulnerability that affects a huge fraction of the internet’s servers.
This is the pace now.
AI does not have to "take over" for the environment to become unmanageable by traditional human processes. It only has to make discovery, weaponisation, and automation faster than the average organisation’s inventory, patching, and monitoring cycle.
If your plan was still "wait and see how AI plays out in security," I hope you have loyal religiously loyal customers and a hell of an insurance policy.
Inventory what you run (especially PHP and anything that trusts public CAs), prepare to patch at the speed these things now appear, and start treating AI-assisted detection and response as table stakes rather than a future project.
The window for comfortable observation is closed.
‼️ PHP UPDATE: The Dutch parliament, the Dutch national cyber agency and Finland's central government have pulled websites offline ahead of the PHP patch.
Finland's state IT centre Valtori is shutting down public-facing central government web services. The National Land Survey of Finland is already down.
In the Netherlands, the Tweede Kamer, the NCSC and the Dutch Data Protection Authority are offline. So are tech site Tweakers and NotuBiz, which runs council information for 100+ local governments.
The University of Vienna switched off its websites, webmail and Moodle. The University of Freiburg and Finland's Haaga-Helia have taken services down too.
Fur Affinity, Pinboard, explain xkcd and every wiki on Miraheze are dark as well.
Valtori says its shutdown is a precaution, not the result of an attack or breach.
PHP was created by Rasmus Lerdorf in 1994, it initially stood for Personal Home Page
PHP's fix is due at 14:00 UTC today.
The NCSC is encouraging UK organisations to prepare for immediate updating of systems using PHP. Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated.
For more⬇️
https://t.co/l6TDtVurJN
Biar betul ... Privacy semua sapu habis⁉️
1. Other Usage data
2. Credit & Fraud
3. Name
4. Payment info
5. Precise Location
6. Phone Number
7. Advertising Data
8. Physical Address
9. Device ID
10. Financial Info
Tuju Ko nak ni data semua untuk BUAT APA⁉️⁉️Skodeng⁉️
Cloudflare has deployed emergency WAF rules for two critical PHP vulnerabilities: CVE-2026-109618 and CVE-2026-109619, both reportedly rated CVSS 9.2.
The risks affect WordPress, Laravel and other PHP-powered applications.
If your site is behind Cloudflare, there’s an extra layer of protection. Cloudflare says its initial rules are available to Free-plan customers too, as early attacks emerge.
But don’t treat that as a fix:
• Verify your traffic passes through Cloudflare.
• Check your PHP version and hosting provider’s patch status.
• Update PHP as soon as the official security fixes are available.
WAF rules are a stopgap, not a substitute for patching.
Cloudflare update: https://t.co/Wyo6GYEC7N
‼️BREAKING: Security firm Calif appears to have a working exploit for the leaked PHP flaws, hours before the patch.
A briefly posted video credited to Calif shows it running commands on a WordPress 7.1.3 site on PHP 8.5.4. Kevin Beaumont says a screenshot from it is real.
A separate public PoC is also circulating, but its own author now says one of its attack chains is dead and code execution is unreliable.
Admins have two stopgaps until the fix lands at 14:00 UTC today.
Turning off session.upload_progress.enabled in php.ini disables the feature the leaked details point to. The only cost is upload progress bars.
Blocking every request with a multipart Content-Type at the web server goes further, but breaks file uploads.
Neither is official. Gina Peter Banyard, a PHP core developer at the PHP Foundation, says "the only mitigation is patching / upgrading PHP."
If you can afford to switch a server off for a day, she says, that might be the most sensible thing to do.
"I sadly know too much," she wrote.
🛑 Attackers hijacked over 300 Tor exit relays to intercept SSH connections and steal login passwords.
A researcher found 333 exits redirecting SSH traffic to 12 interception servers.
The Tor Project has since blocked the affected relays.
Here's how the attack worked: https://t.co/eJsVNeh5xA
🚨TW: Violence
A 16-year-old male student allegedly carried out a knife attack at an international school in Kuching, injuring a female teacher.
Sarawak police confirmed that the weapons found were a penknife and an axe.
🧵1
Ada orang tulis kat Threads, macam mana nak cepat jadi kaya. Rafizi Ramli balas kata jadi ahli politik. Ada benarnya, harini berlegar di internet bank statement Bung Mokhtar ada duit sejumlah RM 1 bilion. Hebat
‼️BREAKING: Cloudflare says it is already seeing early attacks on the two leaked PHP flaws, hours before the patch.
Its CTO Dane Knecht says WAF rules for the known exploit vectors are live for all customers, including free plans, but calls them "a STOPGAP only".
Websites are going dark while they wait. NotuBiz, used by 100+ Dutch local governments, pulled council information sites offline, including those of Den Bosch, Breda and Eindhoven.
explain xkcd and the Star Citizen Wiki are down too.
PHP ships the fix at 14:00 UTC today.