

Top Tweets for #upcrypter

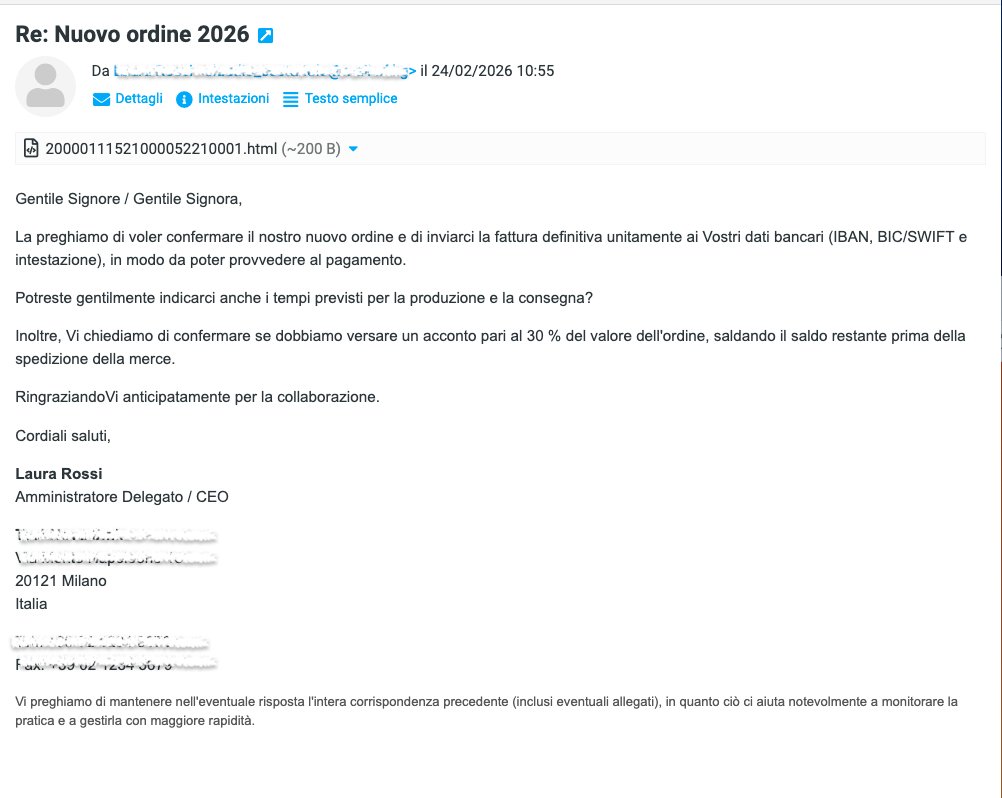
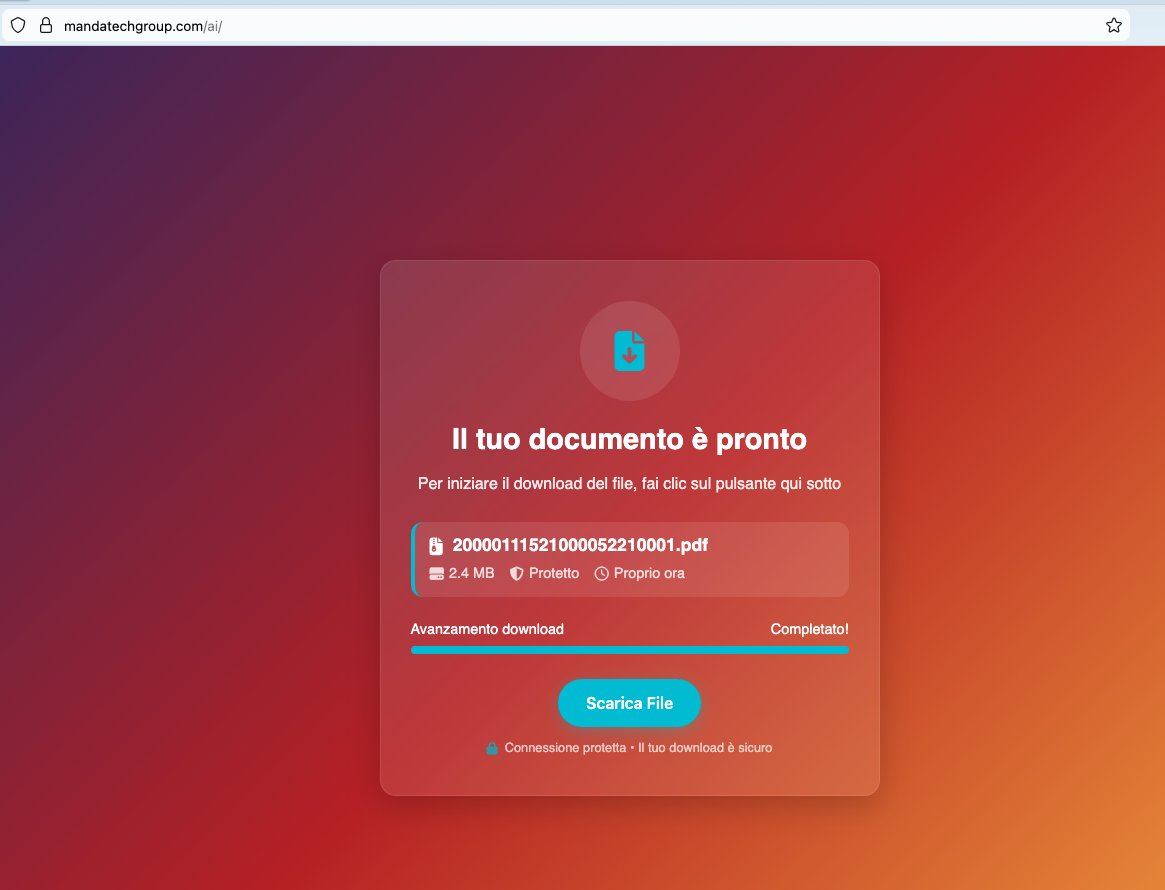
Since February 2026, an Italian invoice-themed phishing campaign has been targeting users with HTML attachments, fake download pages, JavaScript droppers, PowerShell stages and #UpCrypter, ultimately deploying #NeptuneRAT / #MasonRAT.
Analysis:
https://t.co/qOBTFrIe0l
🚨 Distribuito il malware #UPcrypter in #Italia
Email: “Nuovo ordine 2026” con allegato HTML malevolo.
Apertura → redirect → JS offuscato → download payload → contatto C2.
IOC:
mandatechgroup[.]com/ai/
eventul[.]com/it/i[.]php
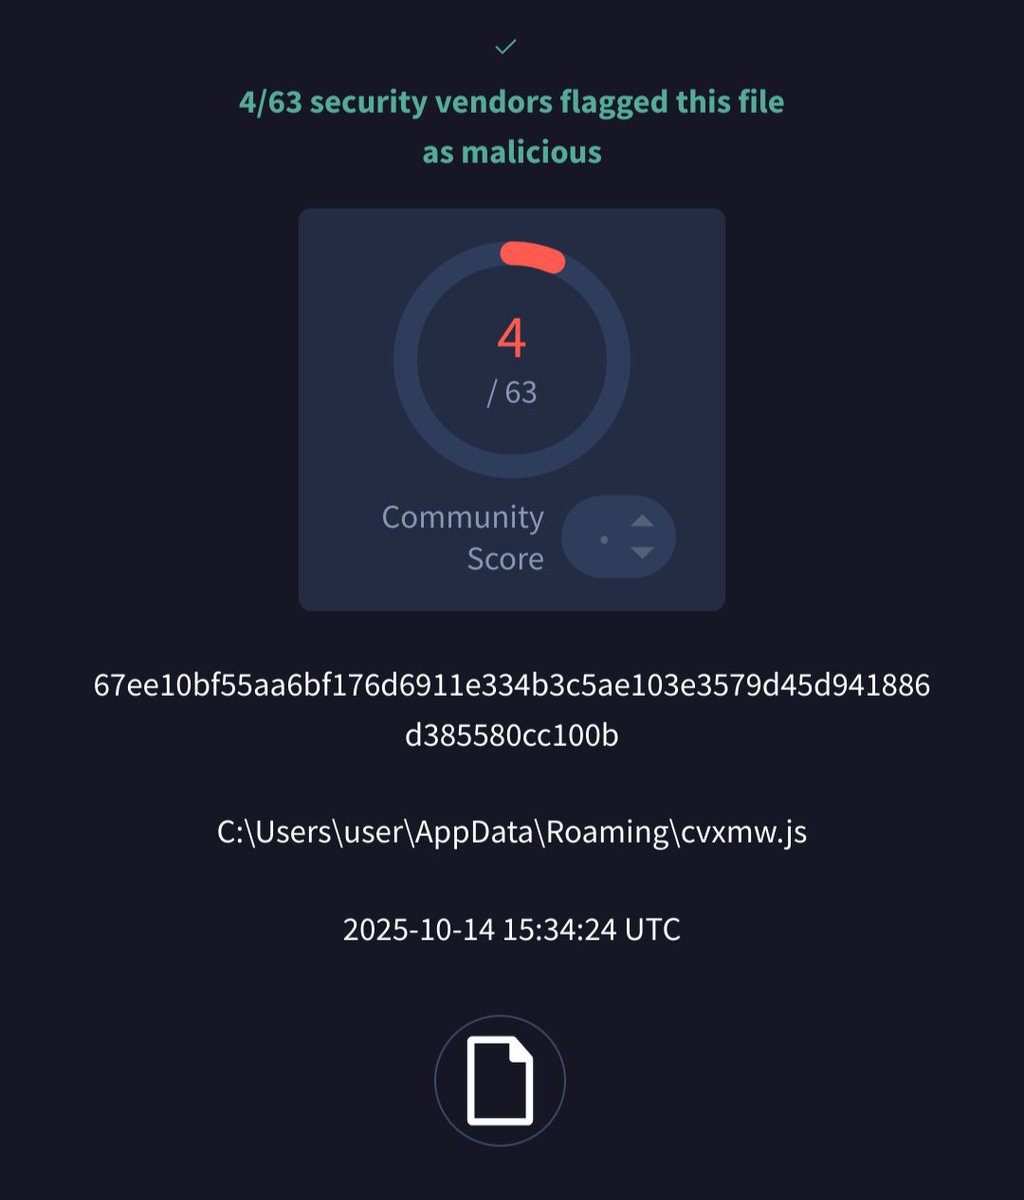
JS: 06ba9a11d693b8ab94e61f696e46faaf


'Flight Itinerary details.vbs' from Germany @abuse_ch
https://t.co/lMSNqN6CFu
Source URL: hxxps://cloudup(.)com/files/iFBgVqLn1bF/download
Contacted URL: hxxps://009423af623840eb89fb1759543879431.1851946.meusitehostgator(.)com(.)br/tqvxk_04/03.txt
https://t.co/3QOZBcPYn9

👾 #UpCrypter is one of the fastest growing cyber threats of 2025.
This loader spreads via #phishing as a JS file and delivers malware like #DCRat & #PureHVNC to infected systems.
Discover its attack chain in our analysis: https://t.co/Hl99CxDMxM


Phishing Campaign Uses UpCrypter in Fake Voicemail Emails to Deliver RAT Payloads https://t.co/K5b2txcBTl #Phishing #Cybersecurity #Malware #UpCrypter #RAT

FortiGuard Labs uncovers a global phishing campaign using UpCrypter to deliver obfuscated JavaScript droppers that execute PowerShell and MSIL loaders, deploying PureHVNC, DCRat, and Babylon RAT in Windows systems. #UpCrypter #WindowsThreats
https://t.co/tFXty8g0dq


Watch out, fake invoice and voicemail phishing emails are leading to the installation of the new #UpCrypter malware on Windows devices worldwide.
Read: https://t.co/DfJ6GKDivg
#CyberSecurity #Phishing #Windows #Malware

@JAMESWT_WT @guelfoweb @JAMESWT_WT something similar reported by @Fortinet in this #upcrypter campaign …
https://t.co/oE2p3B8BZG


❗️ #Upcrypter (by #Pjoao1578) activo en ataques para distribuir #DcRat 👁️
HTML adjunto conduce a un "captcha" en https://adiinthelife[.]com/w/, al resolver, redirige a un sitio que muestra un supuesto mensaje de audio que resulta ser un archivo ZIP con un VBS en su interior.
ZIP se descarga desde: https://hospitalsanbernabe[.]mx/sw/s.php (POST)
⛓️ El archivo VBS inicia el flujo de infección:
1.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos01.txt
2.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos012txt
3.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos03.txt
4.- https://capitalestates[.]es/dc.txt
5.- C2: https://7elyseehomes[.]com/externalSecuredefaultSqldbtrafficPublic.php (also mentioned here https://t.co/UumtgCyJTP @skocherhan @smica83).
[+] https://t.co/uUEJk7SDUr
@malwrhunterteam
![1ZRR4H's tweet photo. ❗️ #Upcrypter (by #Pjoao1578) activo en ataques para distribuir #DcRat 👁️
HTML adjunto conduce a un "captcha" en https://adiinthelife[.]com/w/, al resolver, redirige a un sitio que muestra un supuesto mensaje de audio que resulta ser un archivo ZIP con un VBS en su interior.
ZIP se descarga desde: https://hospitalsanbernabe[.]mx/sw/s.php (POST)
⛓️ El archivo VBS inicia el flujo de infección:
1.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos01.txt
2.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos012txt
3.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos03.txt
4.- https://capitalestates[.]es/dc.txt
5.- C2: https://7elyseehomes[.]com/externalSecuredefaultSqldbtrafficPublic.php (also mentioned here https://t.co/UumtgCyJTP @skocherhan @smica83).
[+] https://t.co/uUEJk7SDUr
@malwrhunterteam](https://pbs.twimg.com/media/GtLfE1vWAAAl24k.jpg)
![1ZRR4H's tweet photo. ❗️ #Upcrypter (by #Pjoao1578) activo en ataques para distribuir #DcRat 👁️
HTML adjunto conduce a un "captcha" en https://adiinthelife[.]com/w/, al resolver, redirige a un sitio que muestra un supuesto mensaje de audio que resulta ser un archivo ZIP con un VBS en su interior.
ZIP se descarga desde: https://hospitalsanbernabe[.]mx/sw/s.php (POST)
⛓️ El archivo VBS inicia el flujo de infección:
1.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos01.txt
2.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos012txt
3.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos03.txt
4.- https://capitalestates[.]es/dc.txt
5.- C2: https://7elyseehomes[.]com/externalSecuredefaultSqldbtrafficPublic.php (also mentioned here https://t.co/UumtgCyJTP @skocherhan @smica83).
[+] https://t.co/uUEJk7SDUr
@malwrhunterteam](https://pbs.twimg.com/media/GtLfE08W4AEfqY3.jpg)
![1ZRR4H's tweet photo. ❗️ #Upcrypter (by #Pjoao1578) activo en ataques para distribuir #DcRat 👁️
HTML adjunto conduce a un "captcha" en https://adiinthelife[.]com/w/, al resolver, redirige a un sitio que muestra un supuesto mensaje de audio que resulta ser un archivo ZIP con un VBS en su interior.
ZIP se descarga desde: https://hospitalsanbernabe[.]mx/sw/s.php (POST)
⛓️ El archivo VBS inicia el flujo de infección:
1.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos01.txt
2.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos012txt
3.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos03.txt
4.- https://capitalestates[.]es/dc.txt
5.- C2: https://7elyseehomes[.]com/externalSecuredefaultSqldbtrafficPublic.php (also mentioned here https://t.co/UumtgCyJTP @skocherhan @smica83).
[+] https://t.co/uUEJk7SDUr
@malwrhunterteam](https://pbs.twimg.com/media/GtLfE06WUAAO0Pf.png)
![1ZRR4H's tweet photo. ❗️ #Upcrypter (by #Pjoao1578) activo en ataques para distribuir #DcRat 👁️
HTML adjunto conduce a un "captcha" en https://adiinthelife[.]com/w/, al resolver, redirige a un sitio que muestra un supuesto mensaje de audio que resulta ser un archivo ZIP con un VBS en su interior.
ZIP se descarga desde: https://hospitalsanbernabe[.]mx/sw/s.php (POST)
⛓️ El archivo VBS inicia el flujo de infección:
1.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos01.txt
2.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos012txt
3.- https://desckvbrat[.com[.br/Upcrypter/01/MeusArquivos03.txt
4.- https://capitalestates[.]es/dc.txt
5.- C2: https://7elyseehomes[.]com/externalSecuredefaultSqldbtrafficPublic.php (also mentioned here https://t.co/UumtgCyJTP @skocherhan @smica83).
[+] https://t.co/uUEJk7SDUr
@malwrhunterteam](https://pbs.twimg.com/media/GtLfEwEWQAAtwbq.png)

7elyseehomes[.]com
#DCRat

Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers