According to @TenableSecurity, a remote, unauthenticated #cyberattacker could exploit the @Cisco#VPN#bug by sending a specially crafted HTTP request to a vulnerable device, resulting in arbitrary code-execution and #DoS. #cybersecurity
https://t.co/aFsuAKd3me
Adversary Village at @defcon 29
Gil Biton Presenting a Talk on "Scaling Up Offensive Pipelines"
Twitch live stream: https://t.co/ReI4ntBsj2
YouTube live stream: https://t.co/ZhLLa7KqFX
Join the live Q&A @defcon - #adversaryVillage > #adv-voice.
#AdversaryVillage#defcon29
@VessOnSecurity Word on the street is they can even add things to the operating system itself. And the operating system can see literally everything you do.
An incredibly dangerous and outrageous threat.
Wait until you hear that Apple can forcibly install on and forcibly remove apps from your iOS device.
And so can Google on Android, of course, but at least the are limited to removing Store-installed apps only. For Apple, there is no alternative.
Me: I wrote a web scanner used by 20 million people, the most referenced TLS guidelines on the internet, and Firefox's certificate viewer.
Interviewer: That's great, but in five minutes can you find the flaw in this non-functioning code stolen from a bad CTF a decade ago?
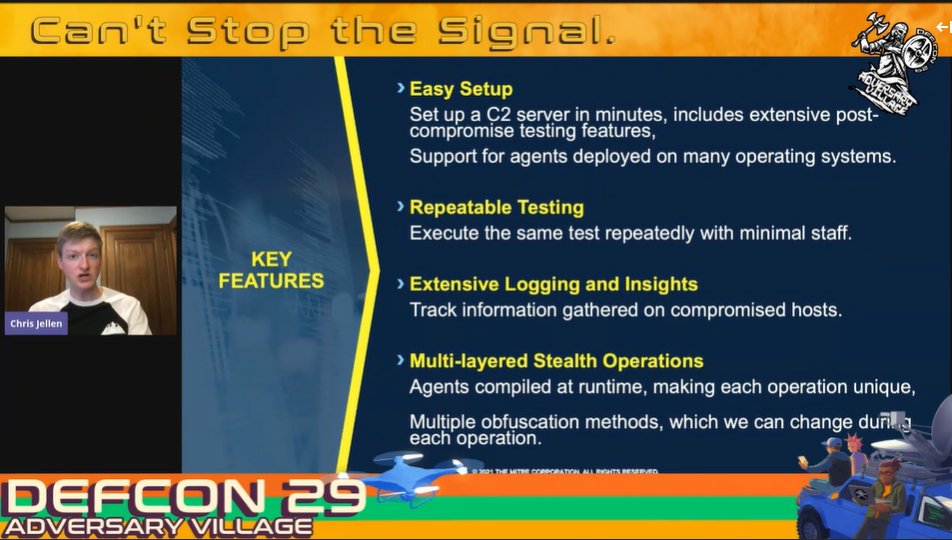
Chris Jellen is live - Workshop: CALDERA: Emulating your first adversary
DEFCON Adversary Village
YouTube: https://t.co/xosDCK4iJj
Twitch: https://t.co/lZ7dNZx4hL
@MITREengenuity @defcon#DEFCON#AdversaryVillage
Shout-out to every Microsoft job interviewee in the 2010's who switched to Windows Phone before flying out to Redmond for full-day interviews and still didn't get the position.