#reversing#repost
Windows Inter Process Communication:
A Deep Dive Beyond the Surface
Part 1 - IPC Roadmap - https://t.co/xXndRaEU7C
Part 2 - RPC Architecture Overview - https://t.co/976LmFavNf
Part 3 - Handles and binding - https://t.co/F3x5Kt5c8q
Part 4 - RPC Security - https://t.co/AEcP1Gdi2t
Part 5 - Securing the interface and endpoint - https://t.co/scfQ1a0OLy
Part 6 - Endpoint Multiplexing - https://t.co/vX1PeXGPnc
Part 7 - RPC Research Tools - https://t.co/oyqpIo2QYS
Part 8 - Reverse engineering an RPC server - https://t.co/ogBqjoo8mz
Part 9 - High-level reverse engineering - https://t.co/tJoe1GuKNz
GIVEAWAY!! 🔥
We’re giving away 1 seat of @AlteredSecurity Certified Evasion Techniques Professional (CETP) – Evasion Lab. 🚀
👉 How to participate:
1️⃣ Like 👍 this post
2️⃣ Repost🔁
3️⃣ Comment 💬 what makes it useful to you
4️⃣ Follow @nikhil_mitt & @AlteredSecurity
A random winner will be announced on Monday, 8th September 2025.
🔗 https://t.co/jUUjo8gC5M
#EvasionWithAltSec #CETP #AlteredSecurity #RedTeam #Pentesting #InfoSec #CyberSecurity #Giveaway
GOADv3 🏰 is almost ready !
You can now try the v3-beta version 🥳
📂 Repository : https://t.co/efjhSZddsa
📖 Documentation :
https://t.co/85kBU6q95u
What's new ? 🧵👇
It took me almost 3 years, but I finally restructured the Practical Malware Analysis section of my site. This is now broken up into more digestible sections, and I've also revamped the MITRE ATT&CK tests to come with appropriate categories and tagging.
https://t.co/LDjOg5PObk
Recently, I've been developing a repository called RustRedOps, focused on security techniques and malware development using the Rust language. I can say that it has been one of the most enriching journeys and I have learned a lot.
I would like to express my gratitude to all the amazing people whose techniques and approaches inspired me to create this fantastic project. Thank you so much for sharing your knowledge, which has served as a reference and motivation for me. Your contributions to the community are spectacular! :)
@C5pider@NUL0x4C@hasherezade@mrd0x@_EthicalChaos_@trickster012
@memN0ps
@vxunderground@chvancooten
Link: https://t.co/rjdrUFyW6l
#hacking #rust #malware #redteam
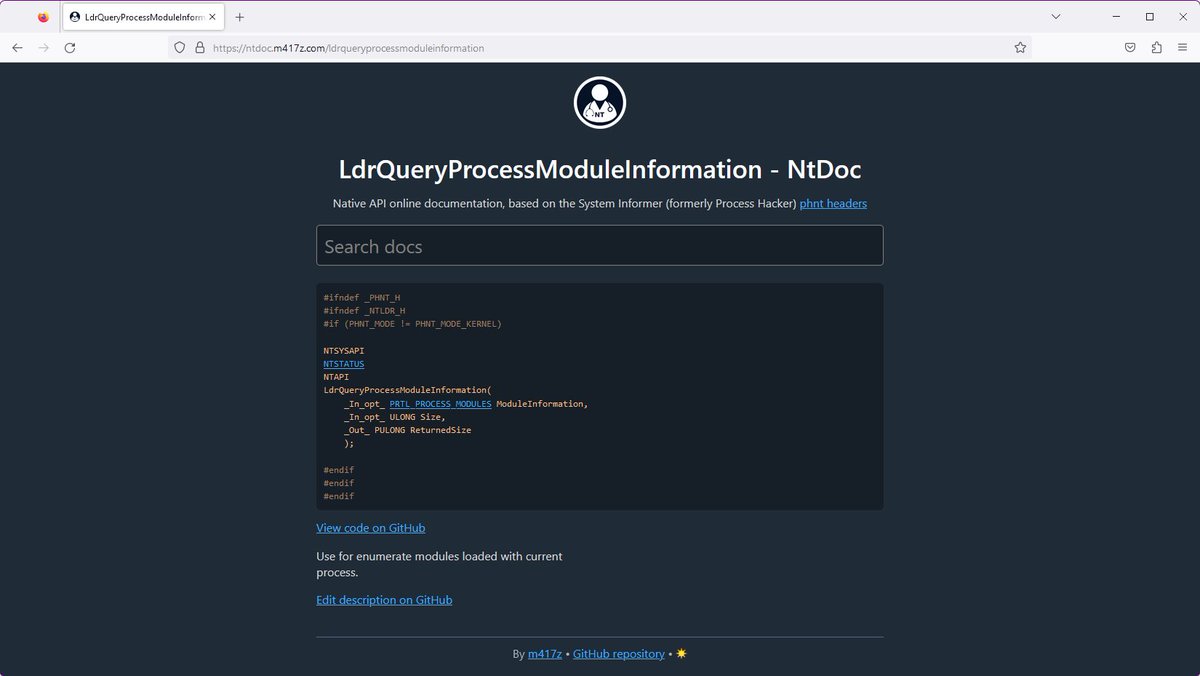
It's common knowledge that the best source for Windows native API definitions is the collection of System Informer (formerly Process Hacker) phnt headers. Surprisingly, there were no online docs for them, so I created a simple website:
https://t.co/WHU55QVZQl
Part 2 of the Malware Analysis Project 101. Complete overview to set up an isolated analysis lab in VirtualBox or AWS. This is in preparation for the analysis of the prolific Zeus Banking Trojan in our next step.
https://t.co/jGW2wQQk90
TCM Security revamped their hacking Active Directory in their practical ethical hacking course. All their original content on AD is now free. Go forth and learn to hack my friends.
https://t.co/AHEq3xPJG1
Me and @Her0_IT did a fair bit of research against one of the leading EDRs in the sector. This first post will hopefully be the start of a long saga, documenting all of our findings.
This first part was dated back in 2020:
https://t.co/CiKGG5RxMo
📖 Container Security Workshop - Slides!
Learn about security features & pitfalls of containerization tools
* Containers basics
* Securing and breaking into containerized workflows
* Docker and Kubernetes security
By @smarticu5 & @raesene
https://t.co/FhlAzJsR4P