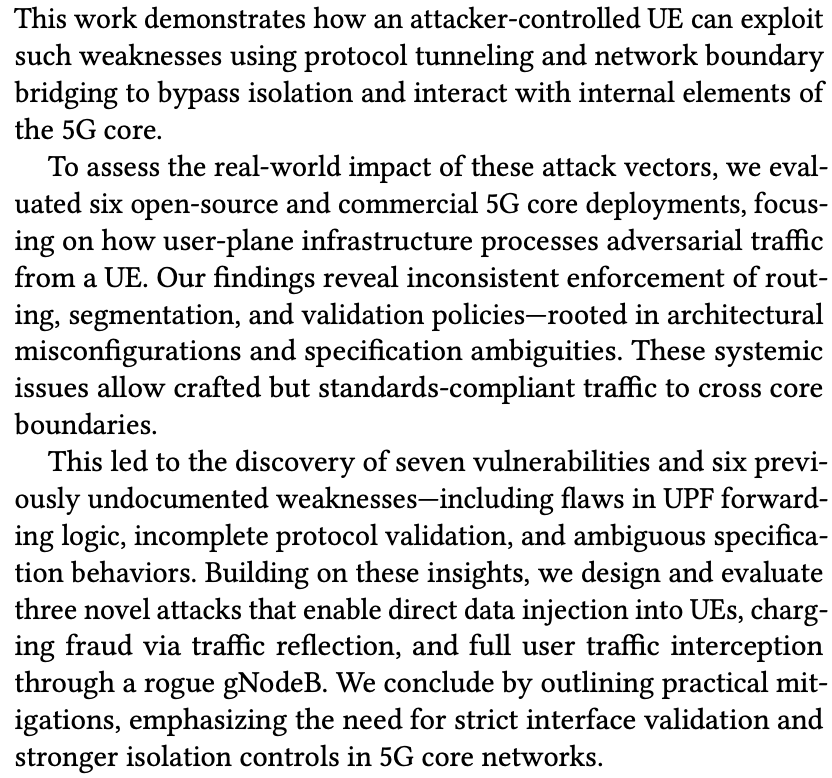
🔥 Microsoft fixed a high severity data exfiltration exploit chain in Copilot that I reported earlier this year.
It was possible for a phishing mail to steal PII via prompt injection, including the contents of entire emails and other documents.
The demonstrated exploit chain consists of techniques that didn't even exist 2 years ago. 🔥
In particular, it involves:
1. Prompt Injection 💉
2. Automatic Tool Invocation (without human in loop) to bring PII into chat context ⚙️
3. ASCII Smuggling 🫣
4. Rendering of benign link + invisible text 👀
5. (Optional) Conditional instructions to only trigger when certain users view the content ☝️
Discussing two demos (stealing sales data and MFA codes), including the videos I had shared with MSRC in February.
@simonw@goodside@llm_sec
https://t.co/G0xpiwYfOZ
Andy was the CISO for Maersk Line when they were hit by Notpetya in 2017. He told what really happened to the audience of the t2 conference this May. Video here:
https://t.co/SBY9ZSvjX0
I built a real-time intelligence gathering tool and it's accessible online. Open Source Surveillance has 18 features including social media, cameras, #IoT, #ICS, transportation and more. #osint#intelligence#infosec#privacy
TIL: The CIA “The Simple Sabotage Field Manual” from WWII suggested enforcing the bureaucracy at companies that delivered to the enemy as a viable sabotage technique.
https://t.co/oXwNRERaCt
Not fan of "awesome" lists in general, however these maturity models collected by @Eliyahu_Tal_ can turn out to be pretty useful
https://t.co/mg82DcHCZ0
I've developed some maturity models myself in the past, and I found them to be a valuable infosec tool (if used properly).
What are your top security Antipatterns? (opposite of best practice)
(https://t.co/fuHxuOgpFg)
I have these so far
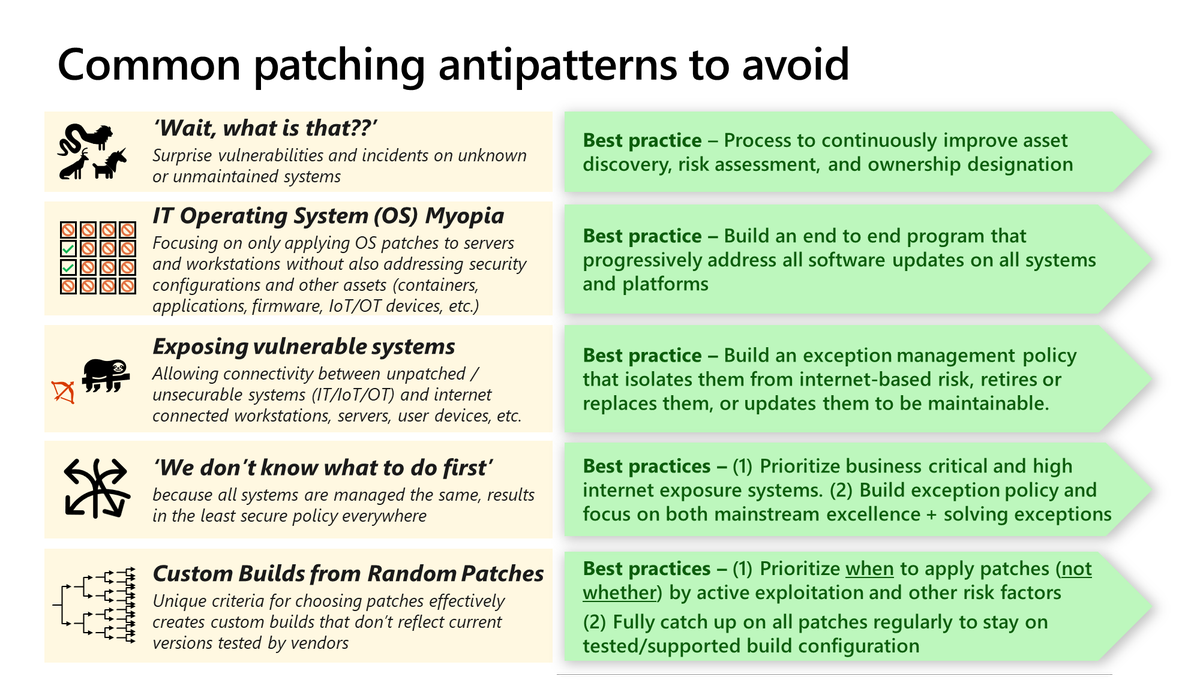
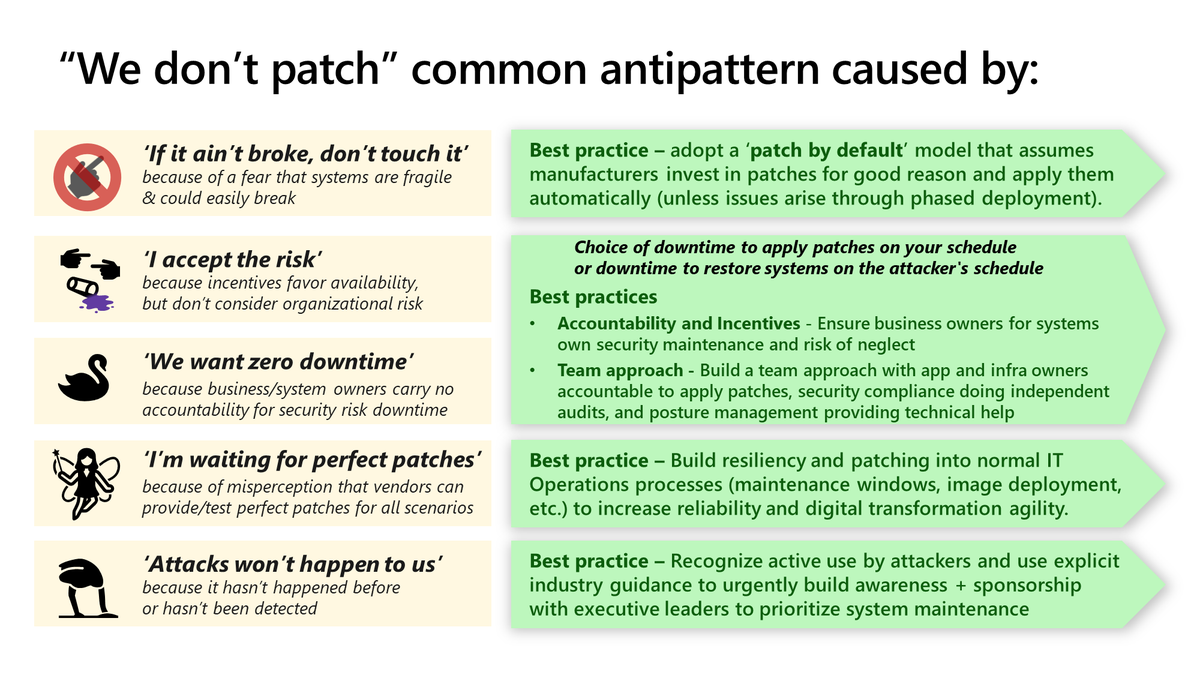
- 10 patching antipatterns
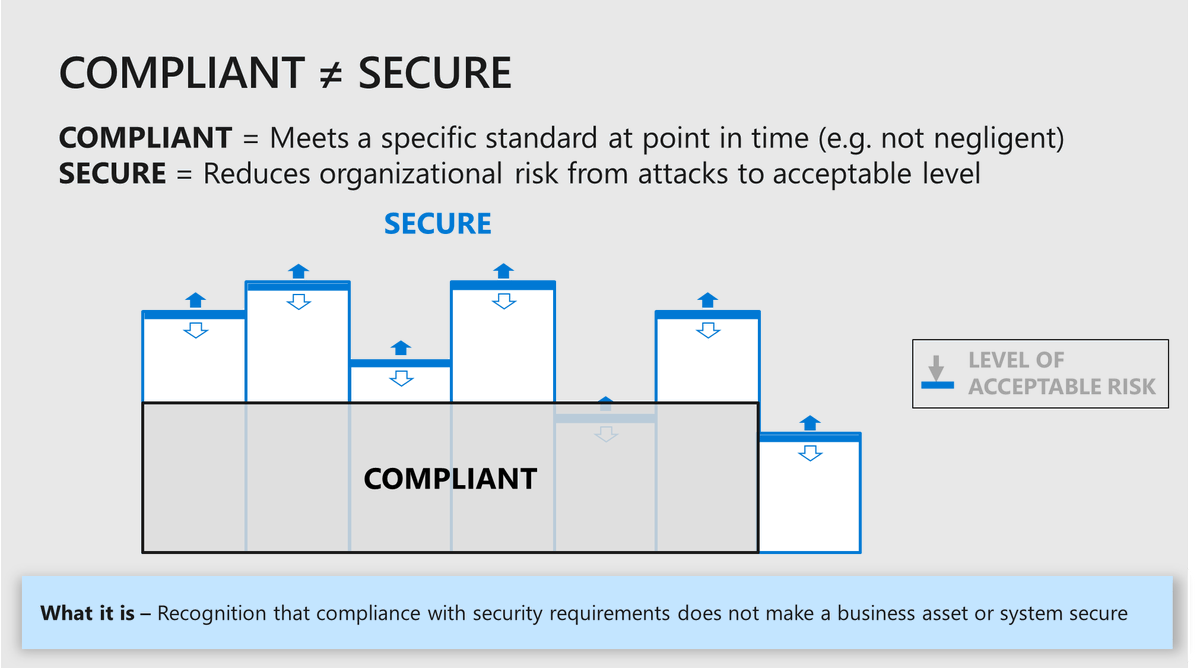
- "compliant is not secure" @scritches
- "Collection is not detection" for log data
- re-using the same password
what else?