The founder of Clawdbot is not lucky.
He built 43 side projects to achieve success with Clawdbot:
- Lock in with vibecoding
- Explore every tool, library, and domain (web3, AI, etc.)
- Prompt, build, fail
- Learn from every failed project
- Prompt, build, succeed
There is no shortcut.
Did you know Claude models have a "magic string" to test when a model refuses to respond? If that string enters prompt context, it can be abused to break LLM workflows until context is reset.
It's the EICAR test string of the AI age. Details:
https://t.co/thkhIo85Nl
You want to use clawdbot or some other ai personal assistant. Super cool! While you’re setting it up, here’s some security recommendations to keep you a bit safer.
1. Run it on a completely isolated/dedicated machine
A physical machine, VM or even in the cloud. The goal here is that it cannot touch or access any other production (personal) system. Also consider your home network design. Keep the machine on a separate network from other things you care to protect.
2 Use separate accounts
Create fresh Google, Microsoft, Apple, etc. accounts exclusively for this purpose. And for all that is good and holy don’t give it access to your primary password manager. Setup a completely separate password manager just for this.
3. Give it the permissions you would give a brand-new IT help desk person on day 1
Extremely limited. Start small. As it becomes more trustworthy grant a little more. Start read only and over time as needed give write access.
4. Don’t put it on the internet with unfettered access
For the sake of your Security, privacy and sanity, use cloudflare tunnels or tailscale or something. This is going to bite a lot of people setting these up at home.
I know this is not much, but it’s a start. It’s really a wild space to be in right now especially from a security perspective.
There’s just not really a lot of great options to secure these things well, just yet.
As a Security / 98% AI YOLO Maximalist with Guardrails guy, I'm asking you to please listen to this.
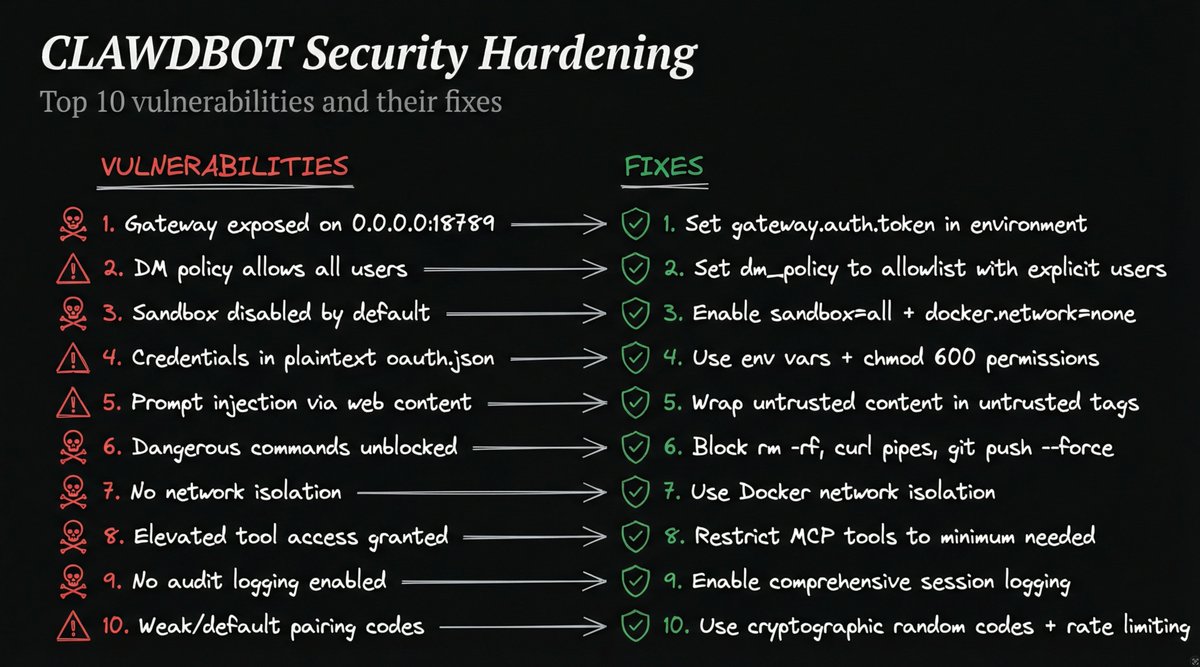
Here are some of the top security issues with https://t.co/yCq4RmE7lB that you all should be avoiding.
Don't avoid the project. It's great. But please be safe with it!
Security teams, I have good news and bad news.
The good news is that executives are suddenly very interested in security controls.
The bad news is, they're not interested for reasons you probably hoped when you dreamed this day might come...
Are you interested in becoming a Detection Engineer? 🕵️♂️🔎
Detection Engineers play a crucial role in identifying and preventing security breaches in organizations. But what skills do you need to become one? Here's a road map to guide you. #DetectionEngineer#CyberSecurity
NEW #DFIR BLOG POST | #AWS Cloud Log Extraction by #FOR509: Enterprise #CloudForensics & # Incident Response course co-author @megan_roddie
This blog post discusses the acquisition of AWS CloudTrails logs stored in S3 buckets.
Read it now 👉 https://t.co/cIFEsRnnqD
@DebugPrivilege sigma is pretty useful for easy cloud IR since a lot of it is api calls but when i need something more advanced for statistical and anomaly stuff, hopefully they got logs in splunk or i can ship em out to elk