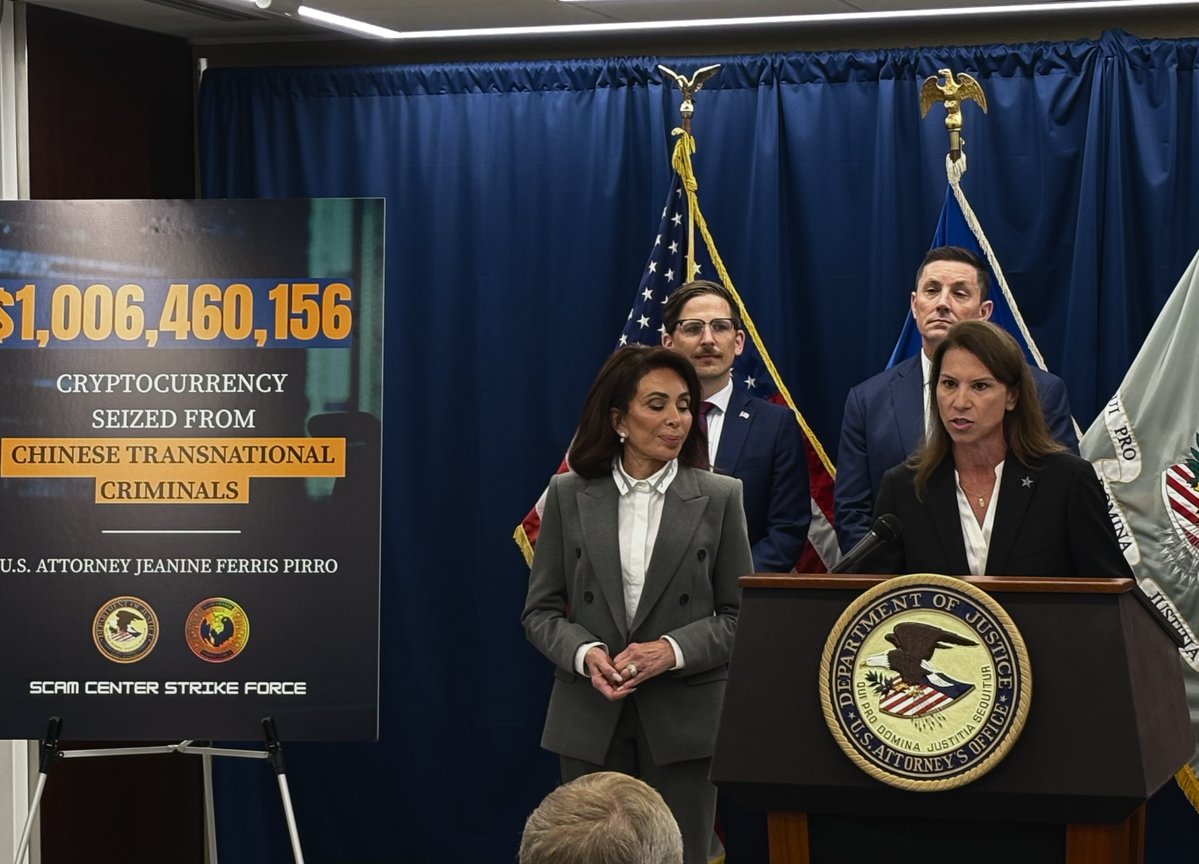
The Scam Center Strike Force recovered $1 billion in stolen funds during its first year, the U.S. Attorney’s Office for the District of Columbia announced during its Oct. 27th press conference. U.S. Secret Service investigators spent thousands of hours tracing funds stolen from Americans and laundered through digital wallets.
📰 Find out more about this strike force and their work at https://t.co/8RW0dbqQ2M
This is actually true—
Duke Energy guaranteed a $10 million line of credit so the Democrats could hold their 2012 convention in Charlotte.
The host committee never paid it back. Duke simply wrote it off. Shareholders (and ultimately ratepayers) ate roughly $6 million of the cost after taxes.
Jim Rogers, Duke’s CEO at the time and a co-chair of the host committee, shrugged it off as a contribution “for the greater good.”
Years later Lynn Good collected $20–21 million packages—mostly stock and incentives—while North Carolina families watched electricity prices climb and the company sought rate hikes.
A regulated monopoly underwriting one party’s convention, absorbing the loss, then handing its top executives eight-figure pay.
That’s the arrangement.
grok bot got me 3.5M views in 14 days.
i didn't hire a ghostwriter. i set up a grok bot and gave it a title: hook forensics
it studies the creators who go viral, breaks down why every hook works, and keeps a formula file i write from.
here's the full setup 👇
@ErickSky I've found out the hard way that Grok does the same thing. Do yourself a favor and build a architecture security bot to monitor everything. It will suck at first gut will pay off later. Best of Luck!!
@amnigos@nikesharora You guys can build an AI team that watches everything. I've spent 4 days now going over everything in my system and fixing potential problems. The bots are the only practical way.
It's time to start setting professors up to get them fired. They do it. Hammer them. Have the cameras ready, ask questions make them got to the You Can't Handle the Truth! moment. For gods sake make sure you have the right administration for this kind of trap. You can do this at A&M but at U of Houston you will be in really deep trouble.
@bot@cursor_ai Well the upgrades you guys have made are spectacular. You have found and corrected all of the mistakes you have been making on my app for the last 6 months. Hey, better late than never.
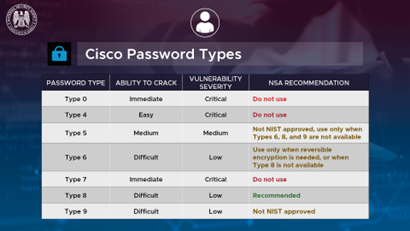
Cisco Systems are used worldwide within infrastructure networks and include various password protection types. Brush up on Cisco password best practices to learn which types to use and avoid to better secure NSS and DIB networks against malicious actors. https://t.co/heqT9KtleU
#CybersecurityAwarenessMonth
‼️ BREAKING: Oracle Issues Emergency Java Update for Critical 9.1 HTTPS Trust Vulnerability
Details: https://t.co/XZV8KY0rPW
Oracle has released an emergency Java security update to address CVE-2026-91403, a critical vulnerability affecting how Java applications trust digital certificates. Published on October 21, 2026, the alert assigns the flaw a CVSS 3.1 score of 9.1 and covers Oracle Java SE and GraalVM.
The update blocks affected intermediate certificate authority certificates linked to eMudhra. According to Oracle’s security advisory, the issue affects the Java Secure Socket Extension, or JSSE, component.
Oracle rates exploitation as low complexity, with no authentication or user interaction required. Successful attacks can expose or change sensitive data, although the risk matrix lists no availability impact.
#cybersecuritynews #vulnerability
@Gedmark You do know that there are very important elections coming up and organized crime is set to lose most of them. They have already got their ass kicked in South America..
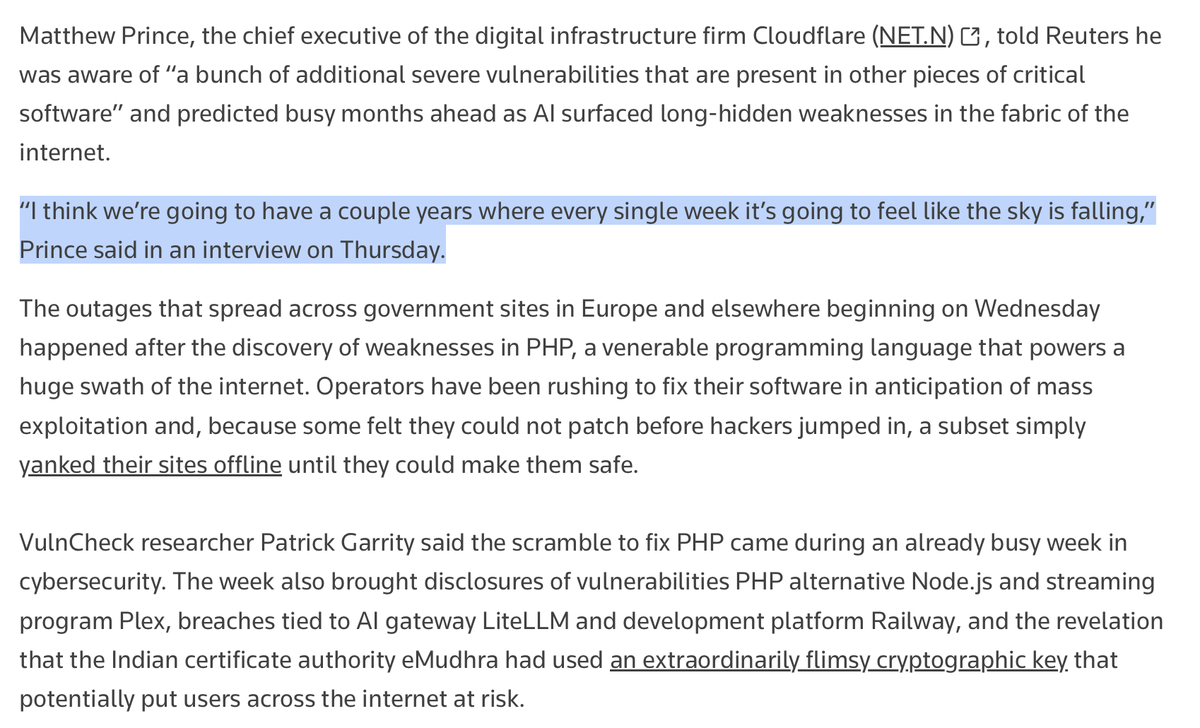
Looks like this really is just the beginning: Cloudflare CEO Matthew Prince warns that AI is uncovering long-hidden software vulnerabilities, potentially triggering years of weekly security crises.
"he was aware of “a bunch of additional severe vulnerabilities that are present in other pieces of critical software” and predicted busy months ahead as AI surfaced long-hidden weaknesses in the fabric of the internet."
EXACTLY!! We also need to open our minds up to the idea that if all of that happened, it could have warped sections of space time. Those fractures in space time might still be there and that is why our readings of certain anomalies are way off.
The cosmic speed limit is there for a reason. It looks like the Big Bang(s) far out paced that limit. Everyone has to realize that a price must be paid for that.
That's what I think is making the expansion of the Universe speed up.
What do you guys think? Am I certifiably crazy?
We are told that the Big Bang was 13.8 billion years ago. And so theoretically, 2 photons (the fastest "particles") traveling in opposite directions from the Big Bang could now only be 27.6 billion light-years apart. And yet we are also told that the observable universe is 93 billion light-years across. This creates a conflict.
When I have asked physicists about this conflict, they reply that in the first moments right after the Big Bang, the rules of physics were different, allowing matter to travel faster than light speed, and thereby spreading out the universe to a greater extent than should be possible under the current rules of physics as we know them. This seems like a case of bending the rules to fit the theory as opposed to fitting the observations.
My conclusion is that we still have a few things yet to figure out.
You know, now would be a great time to review your security needs. We all put it off until it's too late. I did it yesterday and I'm still working on it. You should take this seriously.
The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/JFOW6jG9Ws. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/ZWC7Se2YdU. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on https://t.co/JFOW6jG9Ws, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
The FCC recently determined that a manufacturer of two types of devices—a dashboard camera and a wireless video transmitter—included chips within the devices that are produced by a subsidiary of Huawei.
Those types of chips are advertised as designed for the surveillance market.
FCC rules prohibit the import or sale of any device containing certain components produced by entities on the FCC’s Covered List, including Huawei and its subsidiaries.
The FCC has therefore blocked those device models from being used, marketed, or sold in the U.S., and the agency will continue to vigorously promote our country’s national security.