@jayjig_@Onkkiiie Wouldn't something beyond 900MHz be better for that, especially for bandwidth? The entire FM broadcast is only 20.5 MHz wide, that's less than a standard 40MHz wifi channel.
🚨 Critical OpenSSH flaw allows passwordless account access using any password over 256 characters
https://t.co/gILS1Dxn1w
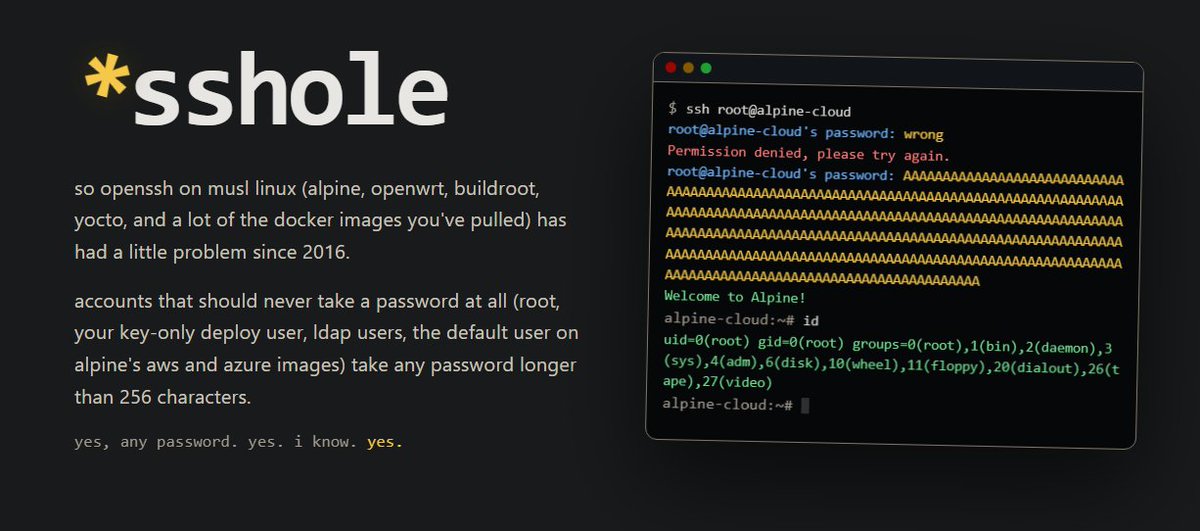
A newly disclosed vulnerability dubbed *sshole has been discovered in OpenSSH installations using musl libc, potentially allowing attackers to bypass authentication and gain access to accounts that should reject password logins entirely.
The flaw affects certain configurations of Alpine Linux, OpenWrt, Buildroot, and Yocto where PAM is disabled and password authentication remains enabled. Under specific conditions, attackers can authenticate to locked accounts using arbitrary passwords between 257 and 1,024 characters.
The researcher demonstrated that affected Alpine Linux cloud images could allow attackers to gain root privileges through a passwordless administrative account.
OpenSSH 10.6p2 addresses the issue. Administrators are urged to update immediately or disable SSH password authentication until patches can be applied.