Now hiring ~5 threat intelligence positions in Europe:
🌍 Threat Intel Analyst (up to 50% remote): https://t.co/os94jWU1up
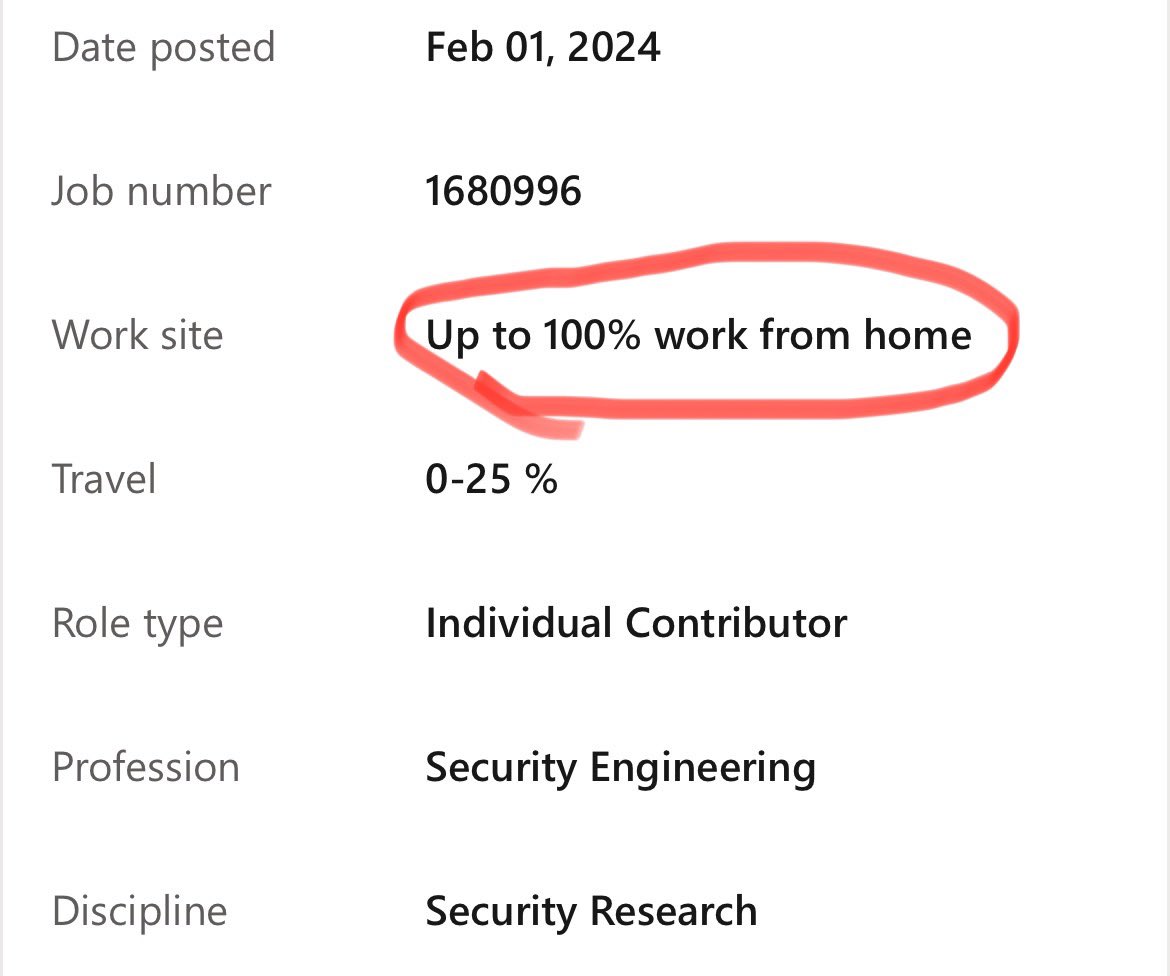
🌍 Senior TI Analyst (up to 💯% remote): https://t.co/cn2FhIrIYr
Not explicitly stated, but based on current trends & corporate priorities, Chinese 🇨🇳 APT tracking experience is crucial.
I am currently looking for an outstanding Security Incident Response Engineer to join our esteemed global security incident response team! This rare opportunity doesn't present itself often. Join us in this exciting role!
https://t.co/Lufm9rmVEJ
Super excited to finally release a project I have been working on for the last few months!
🎊🎊 Introducing the REx: Rule Explorer project and Detection Engineering Threat Report (DETR) 🎉🎉
https://t.co/kR0KBSWH3M
If you found LoFP from https://t.co/BDnfDwOikI useful, this provides significantly more insights via a much more powerful platform (built on the @elastic stack!)
Happy hunting!
#DetectionEngineering #Security #ThreatHunting
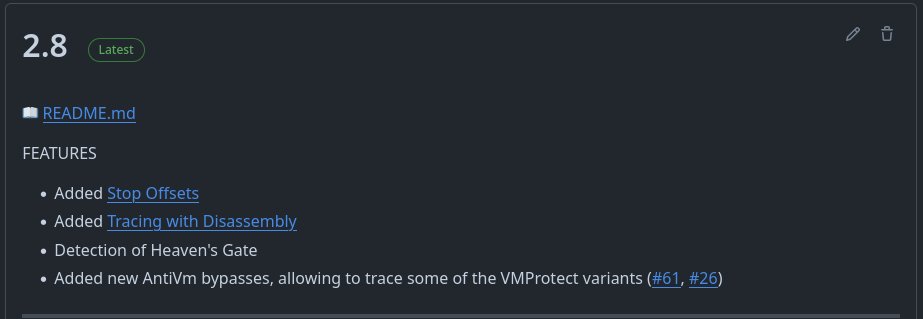
A new version of the cool #TinyTracer helper is out! IAT-Tracer makes tracing functions arguments much easier - it can autogenerate the params.txt file (https://t.co/oTjBfTHnJT) - basing on the application's IAT, or the previous tracelog
We introduce a new way to analyze V8 JavaScript Malware!🥳
In our latest publication we showcase:
🎩The ways threat actors abuse compiled JavaScript
🔬V8 JavaScript malware in the wild
⚒️A new tool for easy analysis: View8
Tool by @MMarelus
Read more:
https://t.co/vYZ0S1kxK7
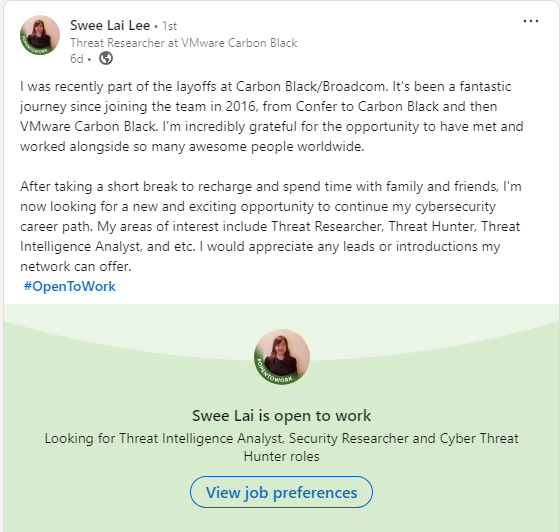
Swee Lai Lee is an extremely talented threat researcher and malware analyst from my team. Laid off after 8 years as part of the Carbon Black acquisition into Broadcom
Based in Malaysia, spoke at RSA, analysis writeups, large-scale malware tests against vendor products
Hire her!
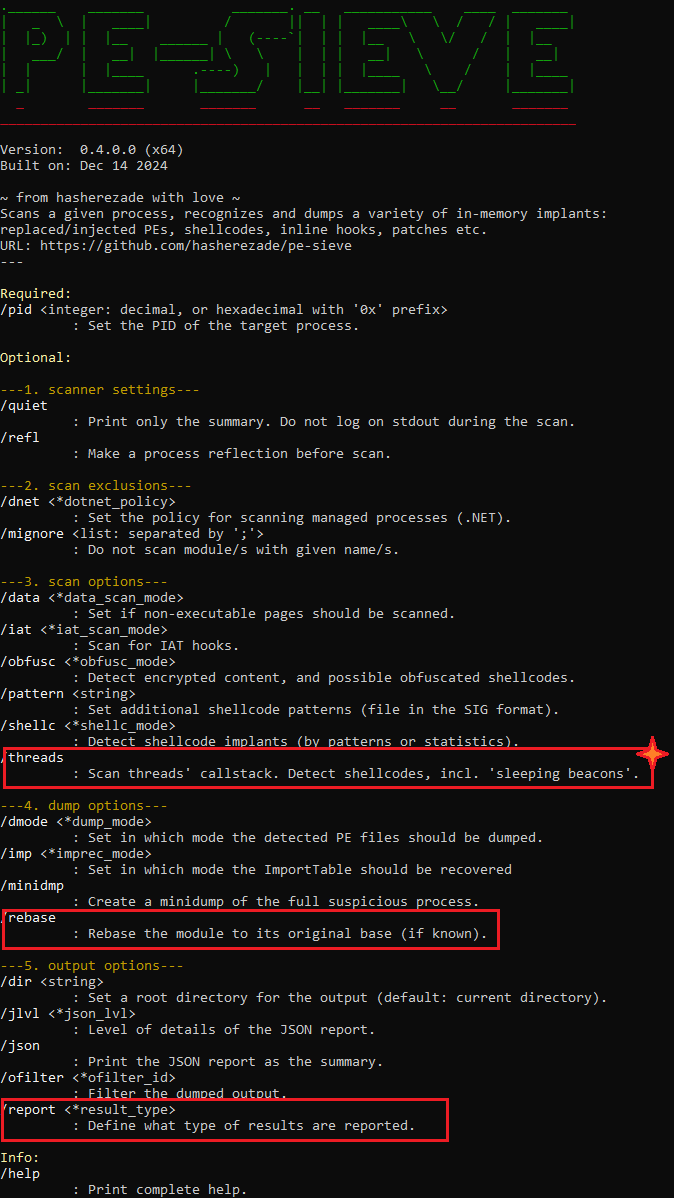
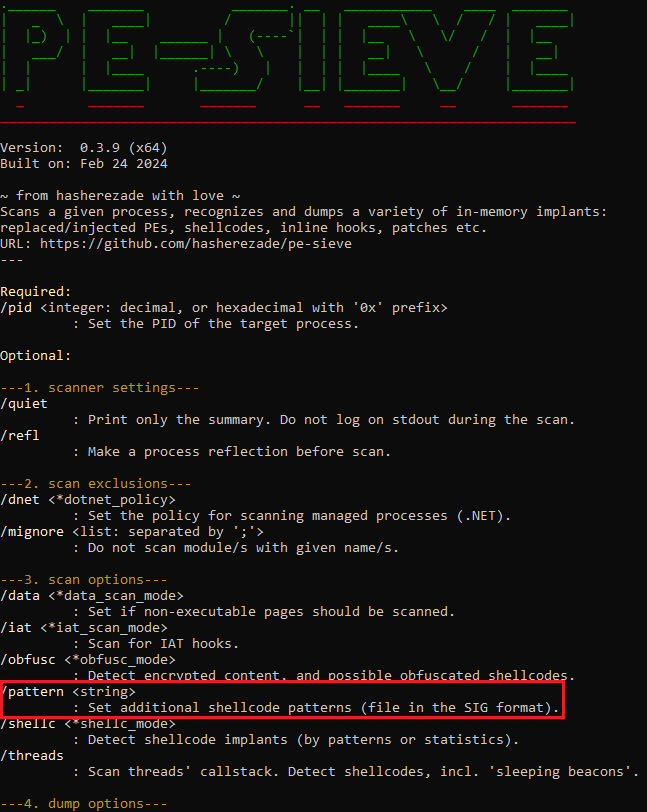
New #PEsieve/#HollowsHunter (v0.3.9): https://t.co/12PiCkKVpA & https://t.co/FBWjtKoAp1 - now you can search for your own signatures in memory. Details: https://t.co/ZWnmc5Mc33. Check it out!
We’re looking for a new Senior Detection Engineer at @huntresslabs.
If you’re eager to grow your skills, take on new challenges and be part of a dynamic team, consider joining us in the hunt 😈
All encouraged to apply today! 💙❤️💜
https://t.co/lGZg41aWK3
Let's decode Powershell Malware with Cyberchef 🧑🍳
New video looking into a simple custom obfuscation routine in a StealC loader, and showing some cool CyberChef tricks for manually decoding 😁
https://t.co/xlaAsxVsYt
#Cyberchef#malwareanalysis#powershell
#pestudio 9.58 now available with following changes:
. Fix an issue when fetching the Virustotal report
. Fix a bug when detecting libraries
. Extend indicators
#Malware#Ransomware#infosecurity#dfir
We are scouting for reverse engineering talent to contribute to Microsoft’s intelligence mission: https://t.co/awiZyJBlal
I can’t guarantee you will understand the vast security data, but I can promise you will often be the first human defender to ever look at a certain malicious code. You have the opportunity (duty?) to create global protections for that malware – for enterprises and home users alike. Quite a few times, you will do this before it causes any harm.
Curiosity & ingenuity as important as technical experience.
If we have worked together (#FLARE 👀 or otherwise), please DM for questions.