Just released ntlmscout, a single-file, zero-dependency recon tool for internet-exposed NTLM endpoints. Combines the best parts of several tools all in one.
Decodes the Type-2 challenge across HTTP/SMB/MSSQL/mail/LDAP/RDP, recovers the internal IP (OXID, IIS host-header, cert SANs), flags DCs, and sprays lockout-safe.
Hack the Planet!
https://t.co/8V8tJM9bzi
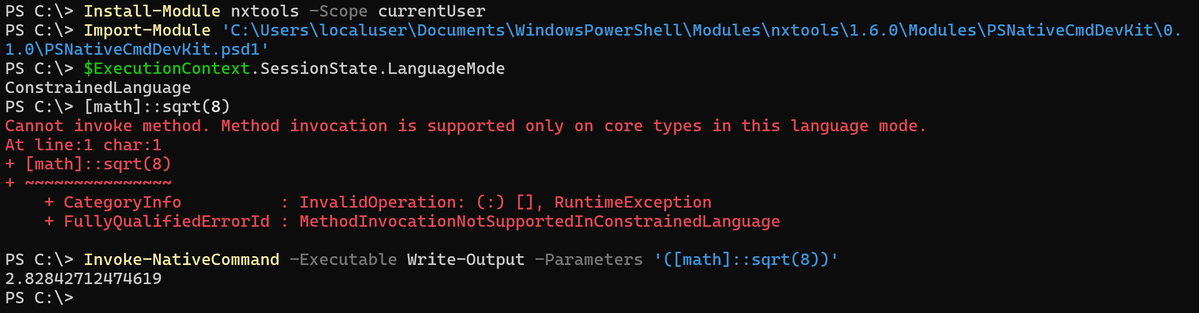
Need to circumvent Constrained Language Mode while operating in an environment with App Control for Business enabled? https://t.co/rxotmrMLEz (Was reported, is by design). Enjoy!
“Tell that dude we hired 6 weeks ago to post that thread about how AI is going to kill everyone. Great. Have the alignment team repost it. Wow, didn’t think it’d go that viral. Feed the NYT a story about us stopping bioweapons. Perfect. Finalize the S1 IPO docs for next week.”
We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: https://t.co/0EJUnYEgfz
Found a critical IDOR on a fintech that leaked every customer's name, email id, phone number, address, bank account number, IFSC, nominee's PAN/DOB/address/phone, and MF folios
Here's how standard testing missed it, and how I found it anyway. 🧵
(1/n)
Been a fan of @hdmoore 's presentations at @defcon for over 25 years. This year the focus was on BMC/IPMI and it was a doozy...oh and there is now and open-source tool called OOBscan too that should now be in every pentesters toolbox.
"So you know, from our perspective, we kind of won,” Moore said. “Like the majority of IPMI devices in the world now, you can go from zero to full authentication to take over the boot process to then take over the host OS.”
https://t.co/WizYxM57nX
A couple of blog posts for learning about Linux process injection
(specifically sshd injection for credential harvesting)
@_xpn_: https://t.co/1eIYm48xIO
@jm33_m0: https://t.co/VQrBwL4b28
#processinjection#redteam#cybersecurity
This week I learned that resource-based constrained delegation can be (ab)used as a means for LPE.
Low priv shell -> create machine account -> Webdav -> coerced auth -> RBCD -> LPE
Special thanks to Adam Crosser from @praetorianlabs for his blog.
Ref: https://t.co/8fUh25za7Q
I found out "C:\Windows\System32\WorkFolders.exe" (signed by MS) can be used to run arbitrary executables in the current working directory with the name control.exe. It's like a new rundll32.exe #lolbin but for EXEs!
I finally got around to posting something I was testing last year. Maybe not ground breaking, but some interesting tidbits I hadn't really seen before.
https://t.co/nXaBrmkIMV
A growing number of cybercriminals are switching from conventional #programming languages to "exotic" languages—such as Go, Rust, Nim, Dlang—for #malware development that can bypass security, and complicate reverse-engineering efforts.
Read: https://t.co/pmL0dBG527
#infosec
New blog: NTLM relaying to AD CS - On certificates, printers and a little hippo https://t.co/MIfNY4Crni
Tool release - PKINITtools: https://t.co/eArMjRDEof
Process Herpaderping - A Method of Obscuring the Intentions of a Process by Modifying the Content on Disk after the Image has been Mapped https://t.co/laNHD1as9o
Added InjectCheck to my https://t.co/1BRSIzmUwH project. InjectCheck is a JXA macOS Process Injection Checker leveraging the codesign APIs. The tool enumerates the Hardened Runtime, Entitlements, and the presence of Electron files to determine possible injection opportunities.
DLL Hijacking persistence by @duff22b, Unauth RCE for HP 💻 Manager from @nickstadb, 🐧 package manager persistence by @pwnshift, malware unpacking methods from @Marco_Ramilli, criticals in 🍎 infra by @samwcyo, DLL hijacking for LM by @domchell, and more! https://t.co/440eBVEhRY