Russia’s Sergey Boytsov proudly holds flag high before RECORD-BREAKING jump from hot air balloon
Stratospheric jump from 7+ miles up, Boytsov hit over 310 mph on descent
bitcoin-only hww, custody: complexity is the enemy of security. many alts don't have multisig or schnorr, one sizel lowest-common-denominator resulted in questionable custody architecture choices. bitcoin has cleanest architected, no alt marketing bullshit, hardcore security tech
A new version of Cuprate (an alternative and independent Monero node software written in Rust) has been released!
'With default settings, users with fast enough internet can expect to sync the blockchain in an hour.'
Tendermint (the consensus protocol for Serai DEX) has been released!
Serai is an innovative DEX that will offer a liquidity-pool-based trading experience for Bitcoin, Ethereum, DAI, and Monero!
Main spam machine had stability issues (previously noted by gingeropolous), causing block sizes to shrink due to insufficient spam volume. Other users continued spamming successfully. jberman targets v2.1 release soon to fix the Windows GUI crash, marginally improve wallet refresh, and resolve double-spend errors. Rucknium added `get.view.keys()` and `kill.wallet.processes()` to xmrspammer (https://t.co/GdPqUHbAB7), with the former useful alongside https://t.co/oTflhXbL5X. FCMP++ / Carrot code is holding up well; remaining issues are uncommon upstream edge cases.
rucknium: 4. FCMP beta stressnet (https://t.co/gkCnlIMPtg).
rucknium: The main machine I use to send tx spam has had some stability issues. gingeropolous referenced them in his update before the meeting.
rucknium: But other users are spamming from their machines. Thank you!
rucknium: Block sizes have gone back to being small because tx spam isn't enough to keep them large.
jberman: Looking to get v2.1 out in the next day (solves windows GUI crash, marginally improves wallet refresh, and will hopefully solve those double spend errors for good)
rucknium: I added a few new features to my xmrspammer package https://t.co/GdPqUHbAB7 . With get.view.keys(), a user can get the view keys of their spamming wallets. Useful for seeing which of your spam wallets are getting txs confirmed if you submit your view keys to https://t.co/oTflhXbL5X
rucknium: And kill.wallet.processes() will kill the monero-wallet-rpc processes associated with a set of wallets. Useful in case you don't want to kill all of the wallet RPC processes running on your machine.
rucknium: Anything else on stressnet?
jberman: Nothing from me, other than that seems like remaining hiccups seem to be uncommon upstream edge cases
jberman: and FCMP++ / Carrot specific code seems to be holding up well
rucknium: jberman: Glad to hear it.
https://t.co/lWTRCdhCCm
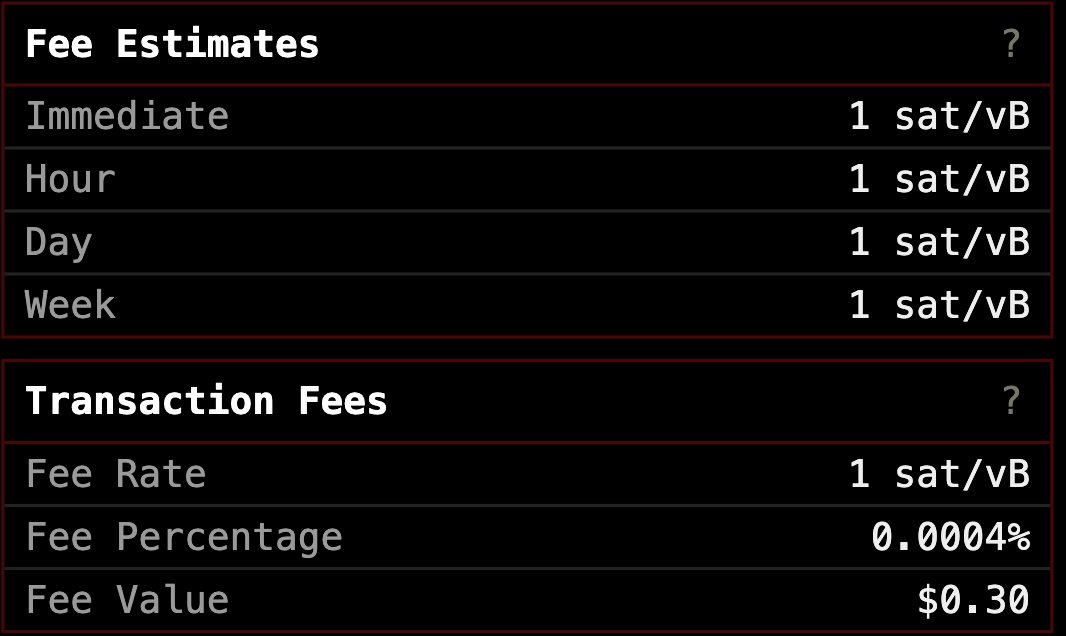
After a decade of blockspace fears and non-monetary-use panics, Bitcoin still has no spam problem. Fees are 1 sat/vB: anyone can move any amount globally with immediate processing for ~$0.30. The free market has always solved Bitcoin’s blockspace challenges. $BTC
emsczkp: this updated version of the paper provides the proofs of the main theorems establishing the security of the BP* folding scheme. In particular, Theorem 1 proves that the modified AC proof for Bulletproofs is complete, HVZK, and special sound. Before introducing the BP* folding scheme, the paper presents an intermediate step, namely the Commit-and-Open (C&O) transform. This defines a new interactive argument by adding an auxiliary commitment at the end of the proof, namely a commitment to the final prover message. Lemma 2 shows that this C&O variant is secure assuming the security of the modified AC proof. Theorem 2 then shows that the BP* folding scheme, built on the NARK C&O variant, is complete and knowledge-sound.
The revised version also includes some changes with respect to the previous draft. In particular, it introduces a new algebraic verifier map V^comm and its relaxed version. This required the introduction of additional error terms in both the accumulator and the accumulation proof.
Overall, the main purpose of this step is the security proof
I've added more details in the GitLab update comment
jberman: sounding like great progress!
rucknium: Thank you, emsczkp. After completing Milestone 2, did you uncover anything that makes Milestone 3 (extend Bulletproofs* to Generalized Bulletproofs) more difficult or easier?
emsczkp: thanks, for the step 3 i think it will be appropriate to go into detail about GBP's relation and security proofs, but the folding scheme now appears to me extendable to GBP
emsczkp: i can't say for sure, but i see good foundations
rucknium: Do you have more discussion of this item or questions for emsczkp at this time?
rucknium: Thank you, emsczkp.
emsczkp: Can I quickly ask about the Milestone ? Do people think another review slot is needed next week, or can we consider the current state sufficient for approval? Thanks
rucknium: IMHO this depends on if anyone plans to spent time reading the revised paper at this point.
rbrunner: Yeah, feedback from one of our cryptographers would be interesting
rbrunner: Even as they are surely quite busy already ...
https://t.co/uWNdFNpsbP
Just so I have this straight
- For 4 years, anyone who understood how Orchard works could have minted infinite untraceable $ZEC out of thin air with no onchain signature
- The bug was discovered this week with a single sentence Claude prompt
- Token supply could theoretically be infinite, but the TX history is private so nobody actually knows
- We're supposed to believe that no one discovered or abused this exploit in 4 years
- And we're also supposed to believe that Zcash pumped 20X in the depths of a bear market for reasons completely unrelated to this multi-billion dollar vulnerability
What am I missing here