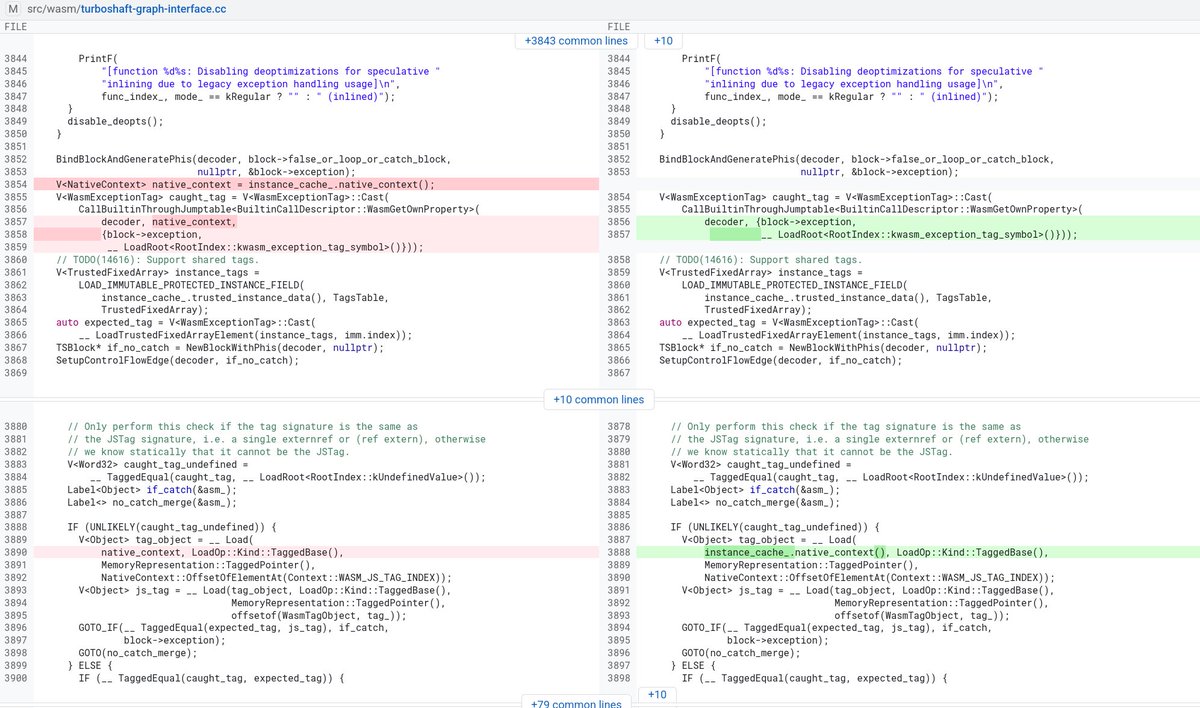
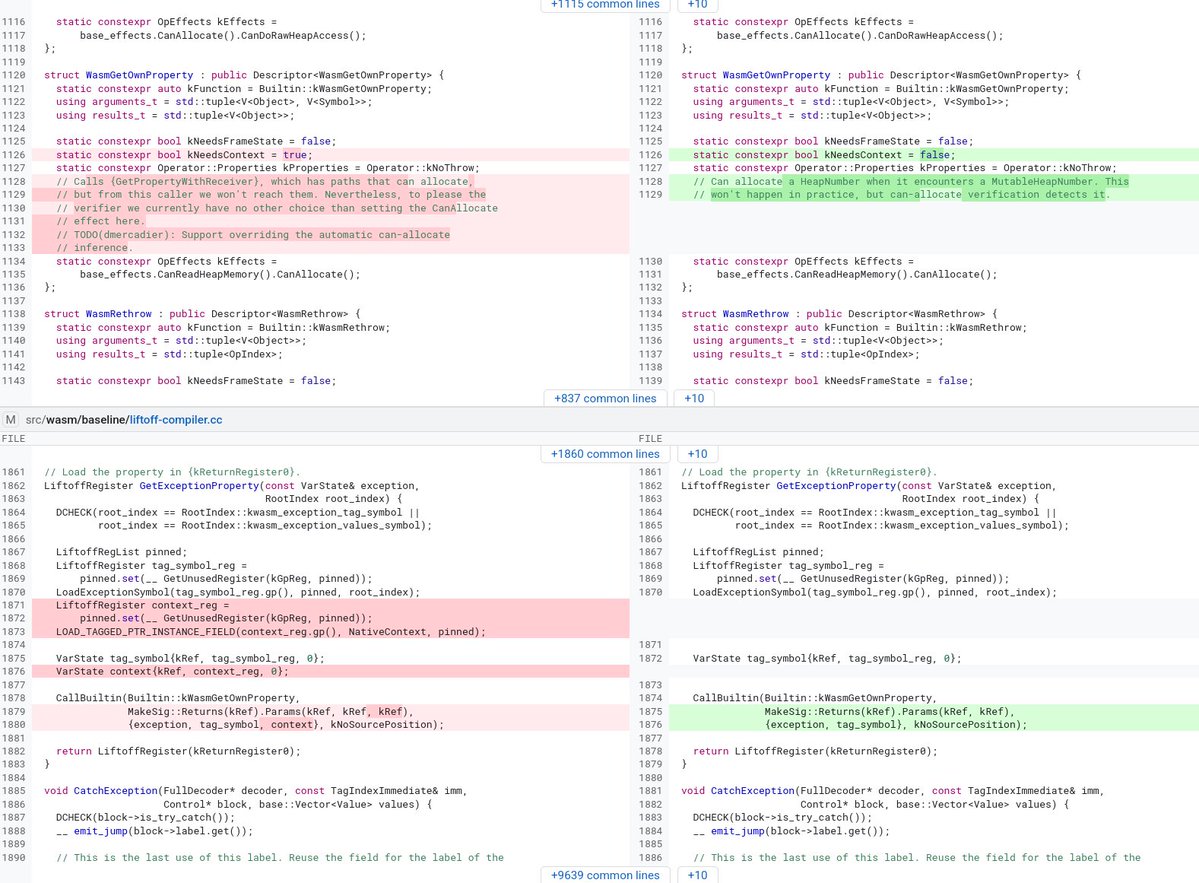
We just received a $250,000 Chrome Full Chain bonus! 🎉
We've claimed the second Full Chain bonus of 2026. Only two remain!
Under the rules, every vulnerability had to be a non-duplicate 0-day, and the entire exploit chain had to be completed before any of them were patched.
Huge thanks to @nebusecurity for discovering a V8 vulnerability in just a single day! Also, a big thank you to @_deayzl for collaborating with me on the V8 Heap Sandbox research.
P.S. KVM escapes have been getting a lot of attention. I actually captured the Full VM Escape flag in KVMCTF about three months ago. Hopefully, I'll be able to share that research soon, too!
this is a very cool bug!
we also found a similar bug but even more impactful, cloudflare team fixed it quiet quickly.
got busy with other work, we will publish soon on our blog and @LiveOverflow’s channel. it’s a insanely cool bug.
Do you know that SSRF might cause local file/cache download and can harm as much as arbitrary write/RCE just from one URL? Making this research just now. Can't wait to share.
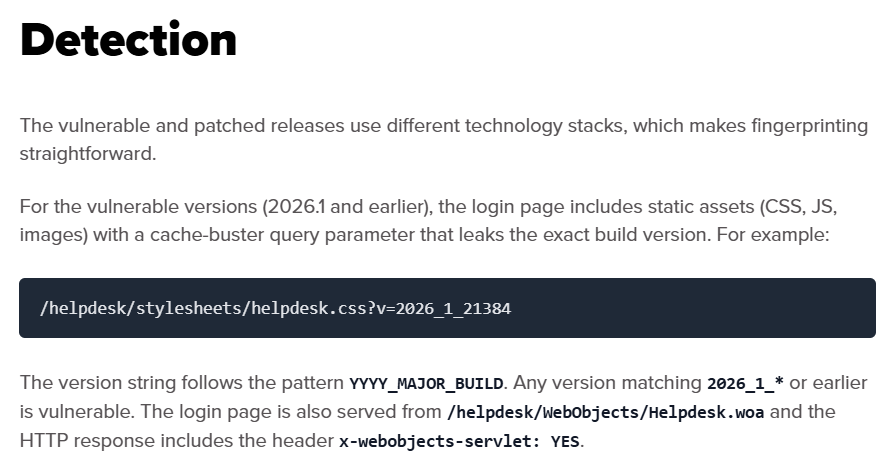
A Writeup on Analysis of CVE-2026-28323 (Signature Optional)
Writeup: https://t.co/K99WHuTisu
Author: @bishopfox [Ronan Kervella, Threat Enablement & Analysis Team]
A few months ago, @SLCyberSec's research team took a look at Goja. It's a JavaScript engine that backs both Zendesk Actions and Nuclei. A simple error in the implementation of two of the TypedArray methods led to RCE. Read more about our research here: https://t.co/1yQfvRuLxa
🇫🇷 #LunarisSec group has identified a vulnerability on https://t.co/CkZs2Xp1HO
Qu'est ce que c'est le "M4SS1VE" : https://t.co/6JnzgddC0T
By CybΞr, Pwn2dd
#Algeria#France#info#snu#M4SS1VE
🔴 LiteLLM / MCP açığı: CVE-2026-59822 — CISA KEV'e eklendi
LiteLLM'in MCP Streamable HTTP endpoint'inde ciddi bir kimlik doğrulama atlatma açığı bulunuyordu.
Saldırganın geçerli bir API/OAuth token'ına sahip olması gerekmiyor, savunmasız sürümlerde rastgele bir Bearer token göndererek MCP oturumu açmak mümkündü.
Örneğin:
Authorization: Bearer a
➡️ Kimlik doğrulama atlatılabiliyor
➡️ MCP araçlarına yetkisiz erişim sağlanabiliyor
➡️ MCP arkasındaki API, veritabanı, e-posta veya diğer araçlar risk altına girebiliyor.
⚠️ CISA, CVE-2026-59822'yi KEV kataloğuna ekledi. Bu, açık halen aktif olarak istismar ediliyor.
Etkilenen: LiteLLM < 1.84.0
Çözüm: LiteLLM 1.84.0 veya üzeri
⚠️ Özellikle internete açık MCP gateway'leri acilen kontrol edilmeli.
MCP kullanan LiteLLM sistemlerinde mesele yalnızca AI modeli değil; agent'ın erişebildiği tüm araçlar risk altında olabilir.
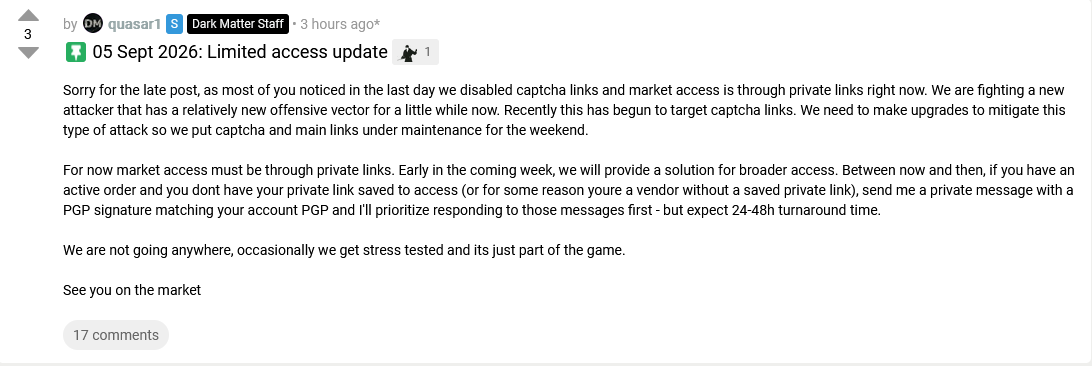
⚠️ Dark Matter Market public links are currently down. Private links are working, but some are complaining that their private links aren't. Treat with caution.
Dread Thread: https://dreadytofatroptsdj6io7l3xptbet6onoyno2yv7jicoxknyazubrad[.]onion/post/598f789643cae0d3f573