A ‘hello world’ milestone for Project Suncatcher 🚀
After launching our prototype satellite a few weeks ago, we’ve now successfully sent a command up to orbit, booted up the TPU, ran the prompt, and received our first complete response back on earth - a haiku!
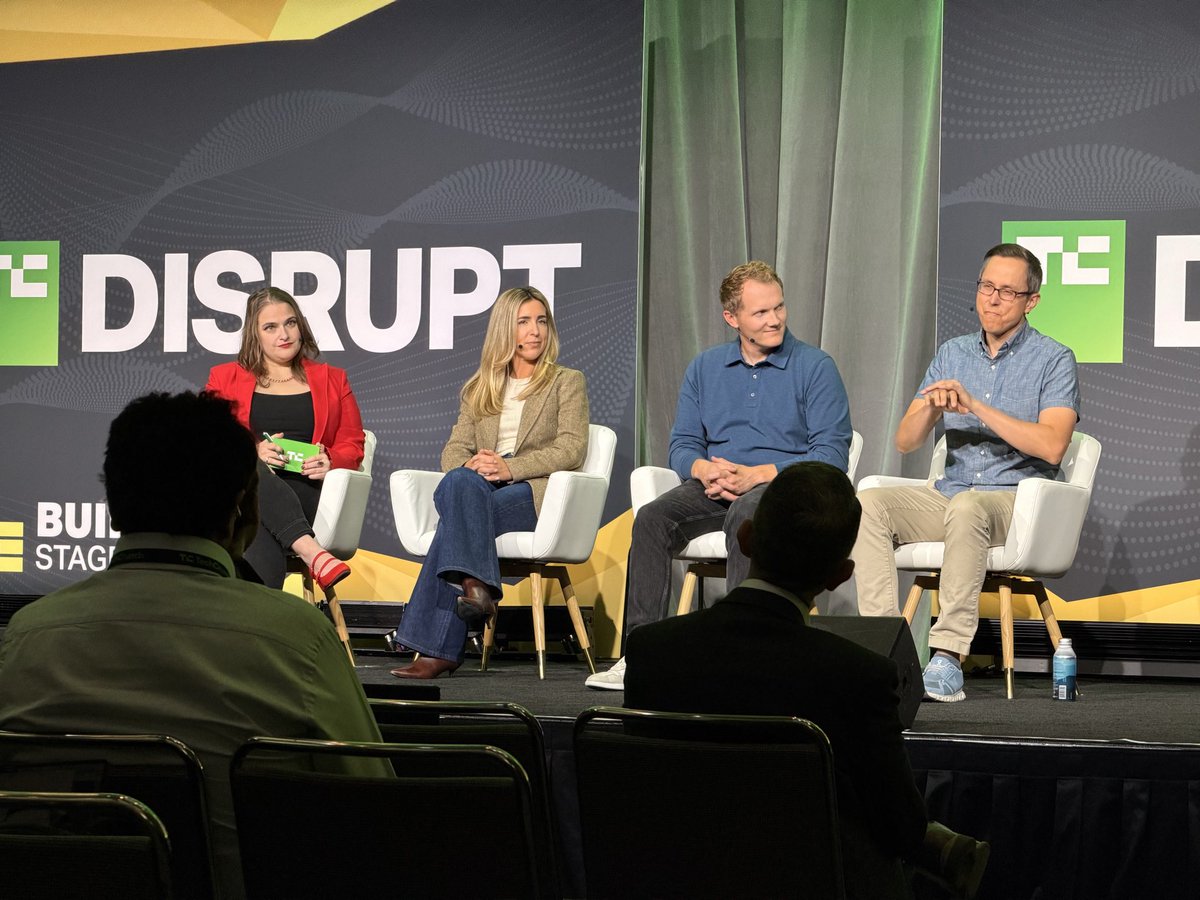
🚀 Wrapping up an incredible experience at TechCrunch Disrupt!
What a great few days connecting with founders, exchanging ideas, and hearing the stories behind the startups — the challenges, the setbacks, the breakthroughs, and the wins. Every conversation was a reminder that building a company is as much about resilience and perseverance as it is about innovation.
A special highlight was hearing from Mark Wahlberg and Bruce Lee about their initiatives focused on longevity, health, and wellness through their gym and wellness center ventures and exchanging perspectives with Ben Cera, founder of Polisia. It was inspiring to see the growing focus on helping people live healthier, longer, and better lives.
I also loved hearing the startup pitches and meeting founders tackling problems across industries. Behind every pitch is a story of ambition, risk-taking, lessons learned, and the determination to keep going.
Events like Disrupt are a powerful reminder that entrepreneurship is not just about building products — it’s about building relationships, learning from each other, and creating meaningful impact.
Leaving energized, inspired, and excited about what’s ahead! 🌱
#TechCrunchDisrupt #Startups #Entrepreneurship #Founders #Longevity #HealthTech #Innovation
🚀 “Yes, It’s Hard to Be a Founder” — Disrupt takeaways
Building a startup is a roller coaster. At #TechCrunchDisrupt, @NoBSNell (Revenge Capital), @dhrosmarin David Rosmarin (Harvard Medical School) & @WithinshawJack Jack Withinshaw (Airspeeder) shared honest lessons:
💪 Protect your health: sleep, exercise, hydrate & stay sober.
🧠 Never make critical decisions when your brain is in overdrive.
🎢 Expect unexpected setbacks—even after a $50M fundraise.
🎉 Celebrate the wins, big and small.
Resilience isn’t just about surviving the lows—it’s about taking care of yourself through the journey.
#TechCrunchDisrupt #Startups #FounderLife
Selling 1x @TechCrunch Disrupt 2026 Founder Pass I bought for a friend who cannot attend— $500(Current site price is $999):
Deadline to allocate/transfer: Oct 2, 11:59 PM PT
Event dates: Oct 13–15, 2026 (Moscone West, San Francisco)
Transfer method: Official transfer via the TechCrunch registrant portal.
Must be a startup founder eligible for the pass verification. First come, first served—DM me if interested!
#TechCrunchDisrupt #TCDisrupt2026 #Disrupt2026
Q2 was an amazing quarter, with our AI investments redefining what’s possible across every part of our business.
Alphabet revenue grew 24% YoY and Google Cloud accelerated to 82% growth. We saw exciting momentum across the board from Search to YouTube to the Gemini app (which reached 950M monthly active users). Our model APIs are processing 22B tokens/min (up from 16B+ last quarter) driven by our workhorse Flash models. We’re also seeing great adoption of Gemini Enterprise, used by 90% of the Fortune 100, as well as strong demand for our security solutions.
Outstanding results and momentum, and such an exciting moment—thanks to all of our partners and employees around the world! 🙌 About to hop on the call!
@AndrewYNg FDEs have existed for long as part of consulting organizations of technology company’s help deploy new technology and adoption. It’s just a. New name for the high tech software engineers working with customers deploying early / new tech.
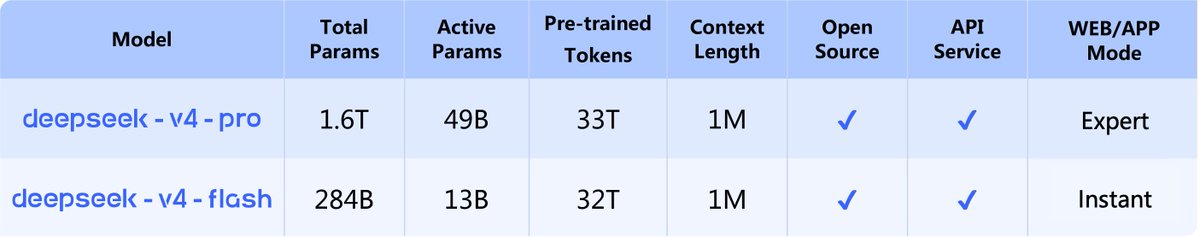
🚀 DeepSeek-V4 Preview is officially live & open-sourced! Welcome to the era of cost-effective 1M context length.
🔹 DeepSeek-V4-Pro: 1.6T total / 49B active params. Performance rivaling the world's top closed-source models.
🔹 DeepSeek-V4-Flash: 284B total / 13B active params. Your fast, efficient, and economical choice.
Try it now at https://t.co/GCdiMzk1Dl via Expert Mode / Instant Mode. API is updated & available today!
📄 Tech Report: https://t.co/drlDrxkYtp
🤗 Open Weights: https://t.co/T13Y8i7SDM
1/n
Great energy at @openclaw#ClawCamp Oakland today.🦞
Had a great time at OpenClaw ClawCamp in Oakland today—surrounded by builders pushing the boundaries of personal AI agents. From hands-on workshops to real conversations on multi-agent workflows, the momentum here is real.
Excited to see how this community continues to shape the future of agentic AI.
#OpenClaw #ClawCamp #AI #AgenticAI #Builders #Startups #Founders
Excited to launch Gemma 4: the best open models in the world for their respective sizes. Available in 4 sizes that can be fine-tuned for your specific task: 31B dense for great raw performance, 26B MoE for low latency, and effective 2B & 4B for edge device use - happy building!
Introducing Critique, a new multi-model deep research system in M365 Copilot.
You can use multiple models together to generate optimal responses and reports.
Software horror: litellm PyPI supply chain attack.
Simple `pip install litellm` was enough to exfiltrate SSH keys, AWS/GCP/Azure creds, Kubernetes configs, git credentials, env vars (all your API keys), shell history, crypto wallets, SSL private keys, CI/CD secrets, database passwords.
LiteLLM itself has 97 million downloads per month which is already terrible, but much worse, the contagion spreads to any project that depends on litellm. For example, if you did `pip install dspy` (which depended on litellm>=1.64.0), you'd also be pwnd. Same for any other large project that depended on litellm.
Afaict the poisoned version was up for only less than ~1 hour. The attack had a bug which led to its discovery - Callum McMahon was using an MCP plugin inside Cursor that pulled in litellm as a transitive dependency. When litellm 1.82.8 installed, their machine ran out of RAM and crashed. So if the attacker didn't vibe code this attack it could have been undetected for many days or weeks.
Supply chain attacks like this are basically the scariest thing imaginable in modern software. Every time you install any depedency you could be pulling in a poisoned package anywhere deep inside its entire depedency tree. This is especially risky with large projects that might have lots and lots of dependencies. The credentials that do get stolen in each attack can then be used to take over more accounts and compromise more packages.
Classical software engineering would have you believe that dependencies are good (we're building pyramids from bricks), but imo this has to be re-evaluated, and it's why I've been so growingly averse to them, preferring to use LLMs to "yoink" functionality when it's simple enough and possible.