@DebugPrivilege I was a big fan before they started ramping up the prices unfortunately. The content of the classes is definitely good and complete, but the impact will depend on where you are in your career, how you tend to learn best and who is paying for it. TL;DR: it depends
@reprise_99 I think one thing you can add is crisis management; it’s something I’ve seen as a necessity at every customer and is also a large part of doing any ransomware IR.
@reprise_99 In the same category I would put the break glass accounts and how to communicate them (e.g. please don’t send them over clear text email) and the various log formats and if they are actually logging what an IR team wants to see/can use.
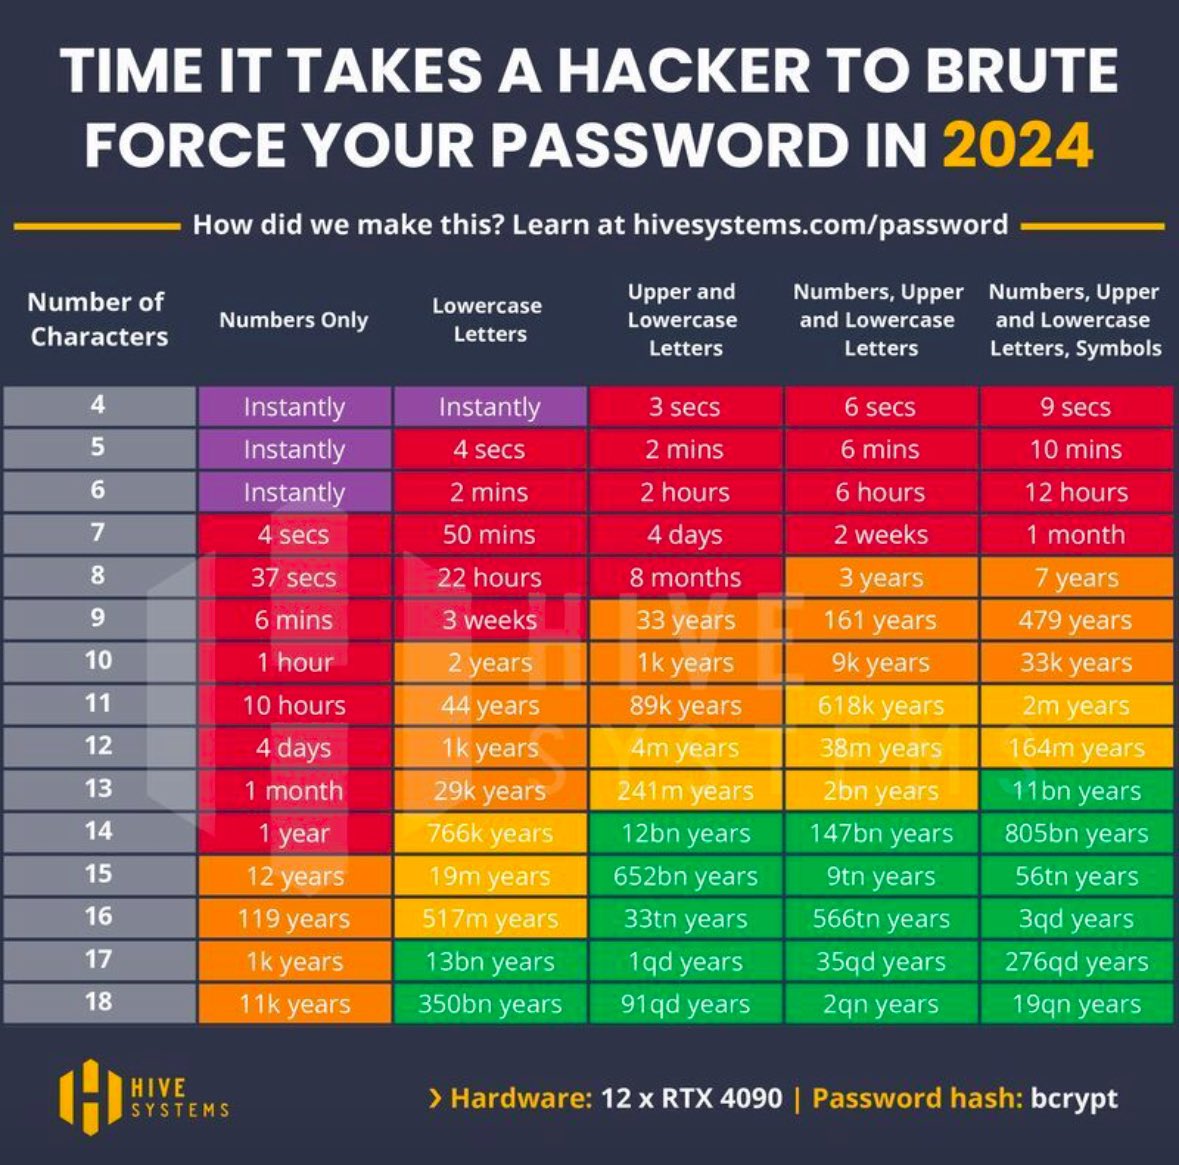
When I look at this table, the first thing I see is that size matters more
I reckon users prefer being told: „use a password with at least 10 letters“ instead of „use at least 8 characters, lower and upper case letters, numbers and symbols“
https://t.co/gl64aVUsiz
Have you been having Kusto Detective Agency withdrawal symptoms? Fear not, there is a special Christmas challenge ready for you, part of the SANS Holiday Hack, good luck!
https://t.co/Bu9EkCyC0a
@reprise_99 I think patching, password hygiene and implementing MFA is part of awareness, it’s not just which emails to click on. Any user awareness training that solely focuses on phishing is probably not worth it.
Join me Wed, Aug 16, 2023 for a FREE workshop entitled "Hands-on Malicious Script Analysis for #Ransomware Response." We'll be covering one of my @sansforensics FOR528 labs in detail, and then some!
Registration @ https://t.co/LvmPcVdPvB
See you there!! #DFIR@SANSInstitute
Hi everyone! Let's do another FREE #Splunk learning weekend! @DThompsonDev@jasonalba@vanillaice
The Complete Splunk Beginner Course
https://t.co/d4dlRYPYQj
The Complete Splunk Certified Admin
https://t.co/kreOJpLmUv
Splunk for Busy People
https://t.co/BOTeEaw46c
@ESETresearch Hey @ESETresearch, seeing this commandline in your blog post "rundll32 <current folder>\<6 random letters>.ocx #1 -s <path to HermeticWizard> – i <target IP>" is that space between the - and i argument suppose to be there or a typo ? might have some impact on detection rules...
Are you in Europe?
Want to take my Pay What You Can (PWYC) Intro to Security class during normal EU daylight hours?
I got you.
I will be up at 4AM MST to teach.
Just for the you EU folks.
Register here:
https://t.co/JwdMRuu6m5