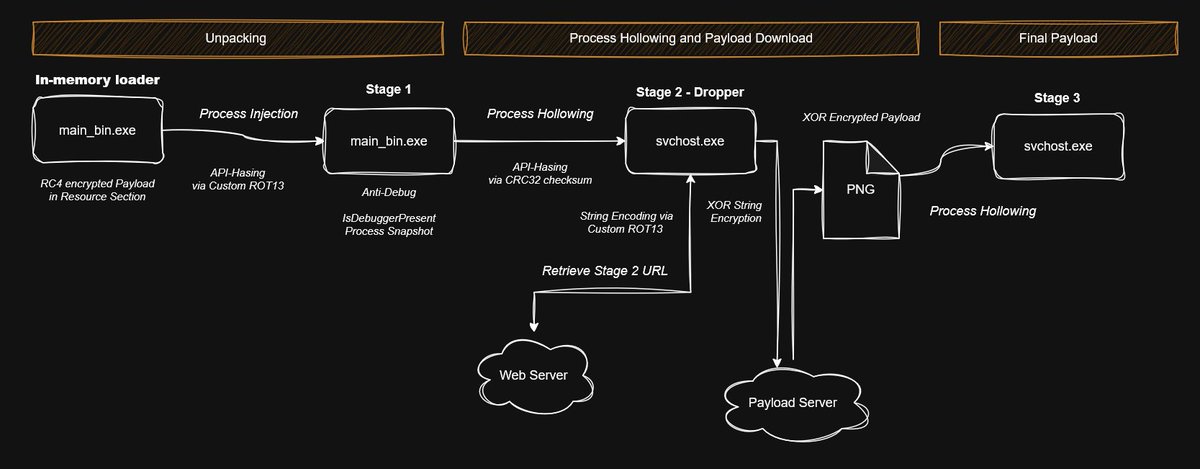
New Writeup: Malware deep dive into Zero2Automated Cruloader, a 3-stage malware using RC4+XOR encryption, API hashing via custom ROT13/CRC32, and process hollowing into svchost.exe. #MalwareAnalysis#ReverseEngineering
https://t.co/SqxgoZUeS3
Don't want to implement your own authentication and access control in your app? You don't have to, I've published a new blog post that deals with the topic of authentication and file access control with authentik for Perlite: https://t.co/ZVFWPZN8bp
#StrelaStealer: My honeypot is being hit with my disclosed login details. Over the past 72 hours, I have logged more than 89000 login attempts from 2500 different IP addresses. They fetching metadata from emails newer then 07.02.2026 https://t.co/Q9K2cgSLac
Ready for takeoff? 🚀
Prepare for the brand-new pieces of content coming to the #HackTheBox platforms this week!
🔴 Atlas, a migrated #Vulnlab Machine created by xct
🔴 Bruno, a migrated #Vulnlab Machine created by xct
🔵 SillyEli, a Sherlock created by GuyEldad95 & Roey
🔴 Global Hyperlink Zone, a Challenge created by DCryp7
🔴 Conversor, an HTB Seasons Machine created by FisMatHack
Get started now on #HTB Labs and Enterprise Platform: https://t.co/n5nAuIhp1S
#Cybersecurity #InformationSecurity #NewRelease #Hacking #CyberSkills
I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: https://t.co/jD6EaGtsn3
I have published a new blog post describing several vulnerabilities that can be chained to get unauthorized RCE in Smart Time Plus < 8.6.
https://t.co/yaH48B9Lmj
new blogpost time!!
this one's a fun writeup on a vulnerability chain i found across multiple google services that earned me a $4133.70 bounty
lots of fun css as usual! i had to recreate a bunch of drive/docs/gmail/youtube UIs c:
have fun!
https://t.co/64ZAIVHoSO