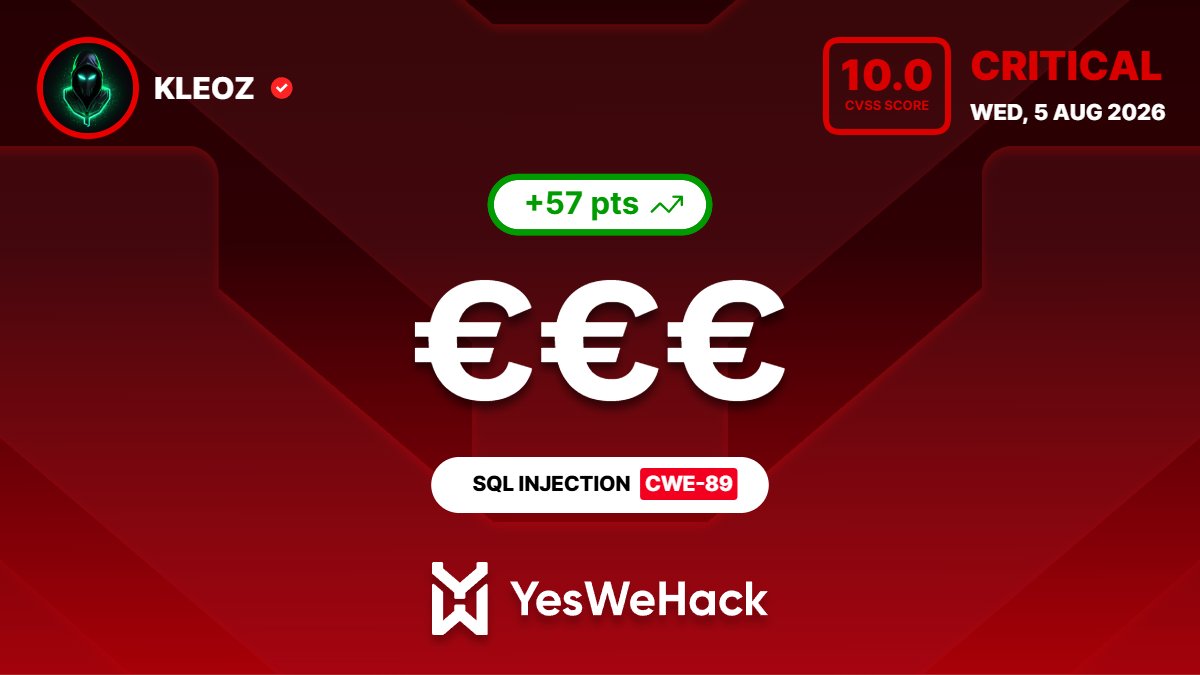
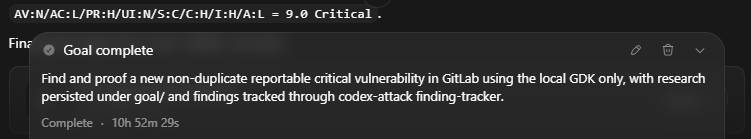
One more on YWH, this time an SQLi Crit!
Wanna join the action?
👉https://t.co/ErlEQXaLv5
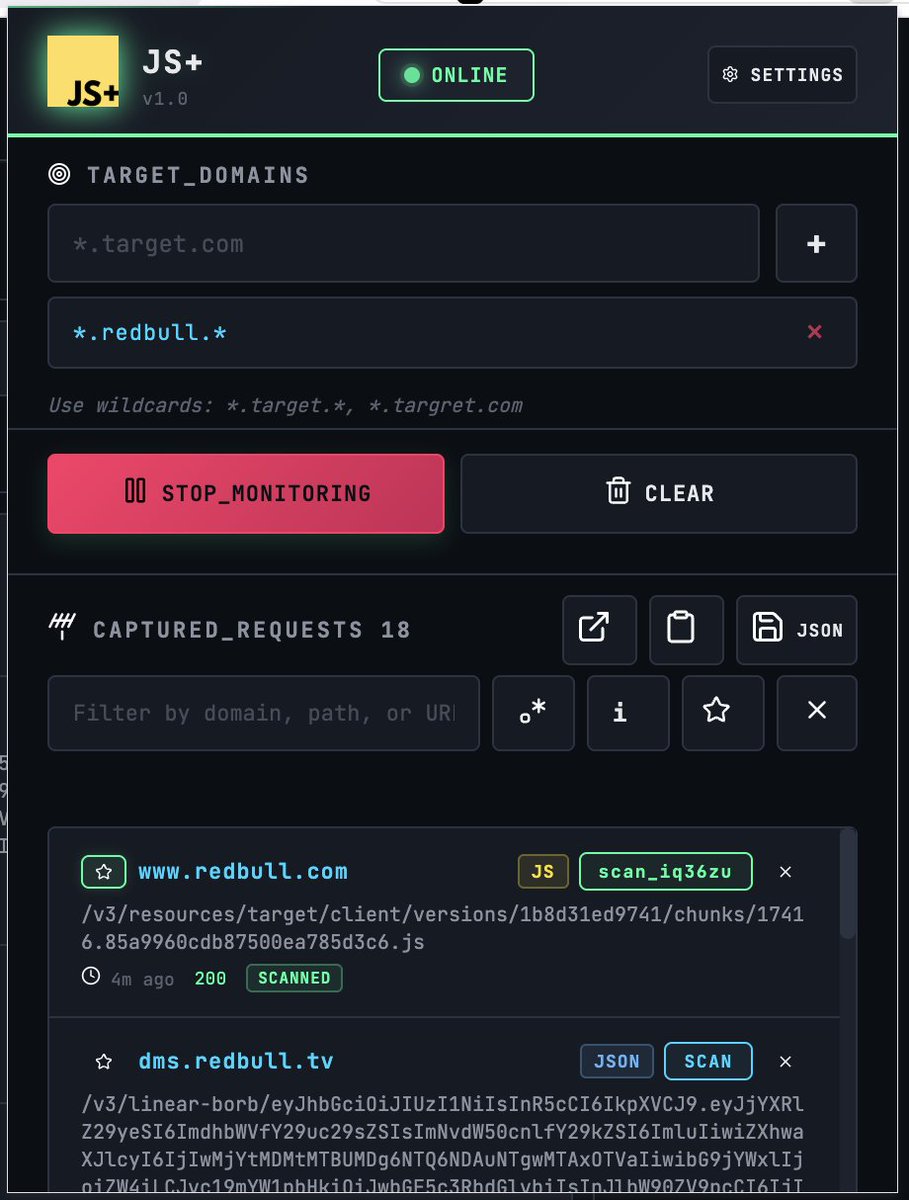
- New program/target live notifications
- Report counts
- Submission fees & rewards
- Target types, API, MCP, WEB
- 22+ different bug bounty platforms and more!
I made $101,388 hunting bugs in 162 days.
Before anyone treats that as a blueprint, I want to be honest about something.
The compute I used to do it cost $199,501.
Hồi học cấp hai, thầy vật lý nói: "Nhỏ vài giọt mực xanh vào chậu nước, sau đó cho quần áo trắng đã giặt sạch vào ngâm một lúc rồi vớt ra phơi".
Nhờ làm theo cách này, mà quần áo tôi bao năm vẫn như mới!
@lcMenci 这种 web fetch 的服务挺多的。我自己给 pi 配置的 provider 就有 https://t.co/aXwrGn70K7, https://t.co/tD4SW9rbEV, defuddle.md 还有 ollama cloud 也提供 web fetch 服务。
但是这些服务都是国外 IP 访问的,有些国内网站是不给国外 IP 访问的
This was a 10k USD simple but critical time-based sqli bug i found a while ago, with the help of https://t.co/IzMYJTVaH1 notifications.
> New target went live -> Instant Discord notification
> Basic recon
> Ghauri against api endpoints
> Full db dump
Sometimes its as simple as being first.
Did you know you can Claude Max using Bountylens MCP
https://t.co/KlKF9BDc4T to hunt on target with the least dupe and highest payout automatically
Run it last week and it came with 2 crits and 2 highs
@BountyLens@Hacker0x01
I published one of the techniques that I've been using against OAuth providers, honetly, it's led me to discover many flaws, and recently I used it to find a 1-click ATO on one of the most widely visited websites,I hope you find it useful :-)
https://t.co/o7OO8Y7e3K
We got frustrated with dealing with vendor dependencies when reverse engineering large applications. @ITSecurityguard from @SLCyberSec’s Sec Research Team built Hyoktesu to solve this problem forever: https://t.co/rQM2ypLLuW - releasing this today! Blog: https://t.co/KCPSTnFjVN
Meet BugSkills.
I built a tool to convert the knowledge and methodology used in your HackerOne reports into AI skills you can use to automate vulnerability discovery.
Thank you @rez0__ for the idea.
https://t.co/Ywb3SXQ2QJ
🚨 We got RCE on Solana 🚨
Finally revealing FULL details about the RCE vulnerability we found 2 years ago.
Found it. Lost it. Exploited it anyway.
🔬 Here’s what real-world bug hunting looks like: https://t.co/k6o6IKtuSW