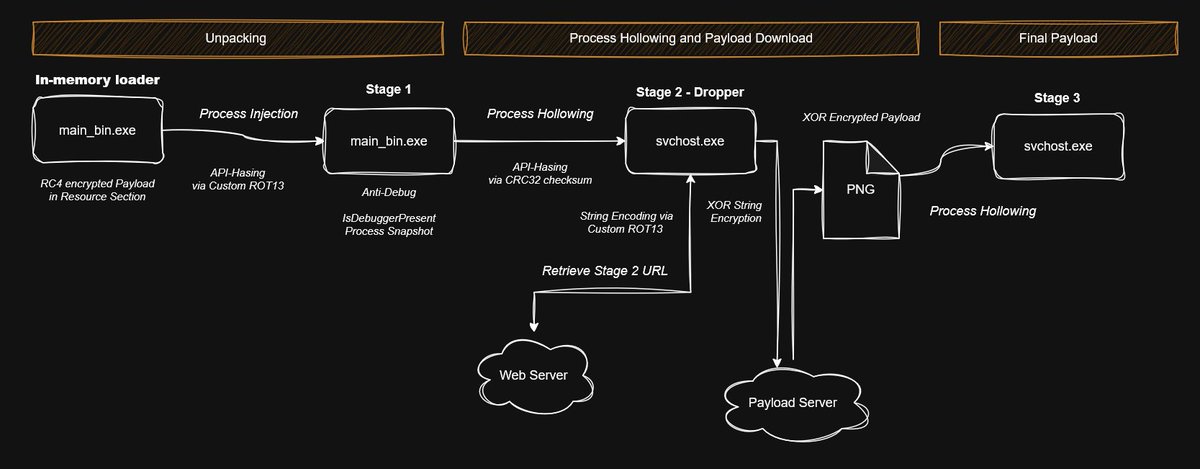
New Writeup: Malware deep dive into Zero2Automated Cruloader, a 3-stage malware using RC4+XOR encryption, API hashing via custom ROT13/CRC32, and process hollowing into svchost.exe. #MalwareAnalysis#ReverseEngineering
https://t.co/SqxgoZUeS3
I have published a new blog post describing several vulnerabilities that can be chained to get unauthorized RCE in Smart Time Plus < 8.6.
https://t.co/yaH48B9Lmj
Sharing a new mini research technique that abuses HTML injection to leak data cross-domain. This blogpost connects couple of client-side concepts and a Chrome/RFC Referrer-Policy bug. Inspired by @garethheyes recent CSP bypass techniques, enjoy :)
https://t.co/BAf0It9yvS
Excited to announce our new blog post on new event handlers to trigger XSS! Huge thanks to @bojanz for making this happen and to @PortSwiggerRes for their awesome XSS cheat sheet, now featuring these techniques.
https://t.co/qnjmn7WKHi
If someone is interested in patching Android apps, I've published a new (beginner) blog post that I wrote some time ago. It's a pretty simple app, but maybe helpful if you've never touched an Android app
https://t.co/qK46ayB06S
@EricaZelic@filip_dragovic It's also possible to relay the authentication to corresponding RPC endpoints: https://t.co/ysCvm3phbY
Thus in addition to protecting the HTTP endpoint, the IF_ENFORCEENCRYPTICERTREQUEST flag should be configured to enforce encryption for ICPR requests (https://t.co/IbxlrG5J7y)
It's been a while since I've solved something on @vulnlab_eu Easter weekend and the new Tengu chain by @0xr0BIT are a good time to start again!
If you get stuck, you can check out my writeup! https://t.co/H2vQlCT3za
Happy Easter! 🐰
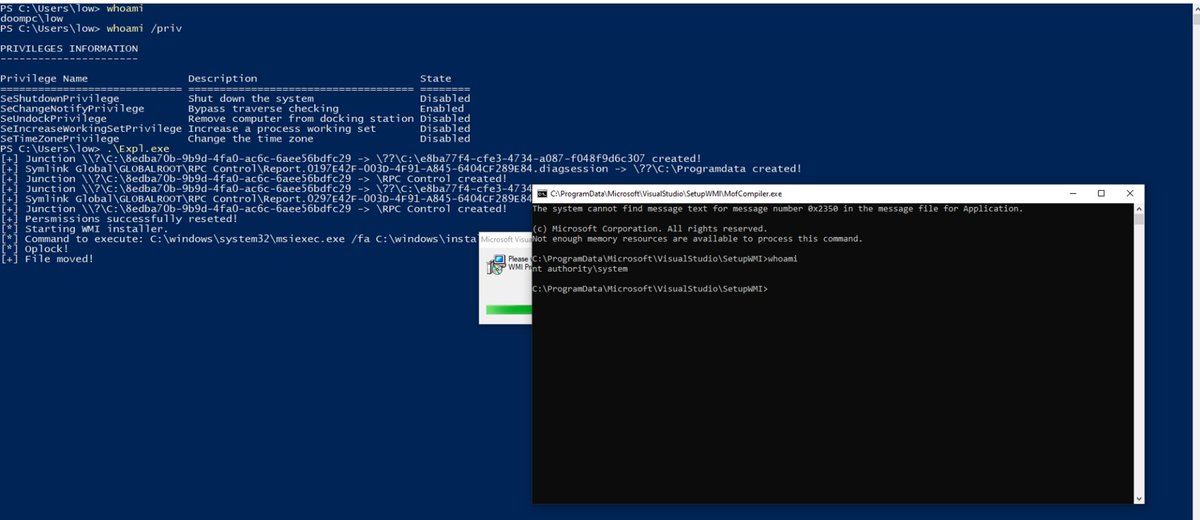
Exploiting CVE-2024-20656, a Local Privilege Escalation in the VSStandardCollectorService150 Service https://t.co/zCj3o31RPn - new research from @filip_dragovic
@pentest_soka I think to bypass the "Credential Hardening" of Elastic, you could try some ASR exclusions such as WerFault.exe and co (although there are built-in detections for the most common exclusions)
Heres the decompiled version of the (likely) related ASR rule:
https://t.co/ns5Z90v2Y6
Happy to share that I will try to run my own business as a side hustle starting at the beginning of next year.
If you are a German follower and are interested or know someone, please feel free to reach out to me.
Some info, details etc. can be found here:
https://t.co/arkVEZ2yJp
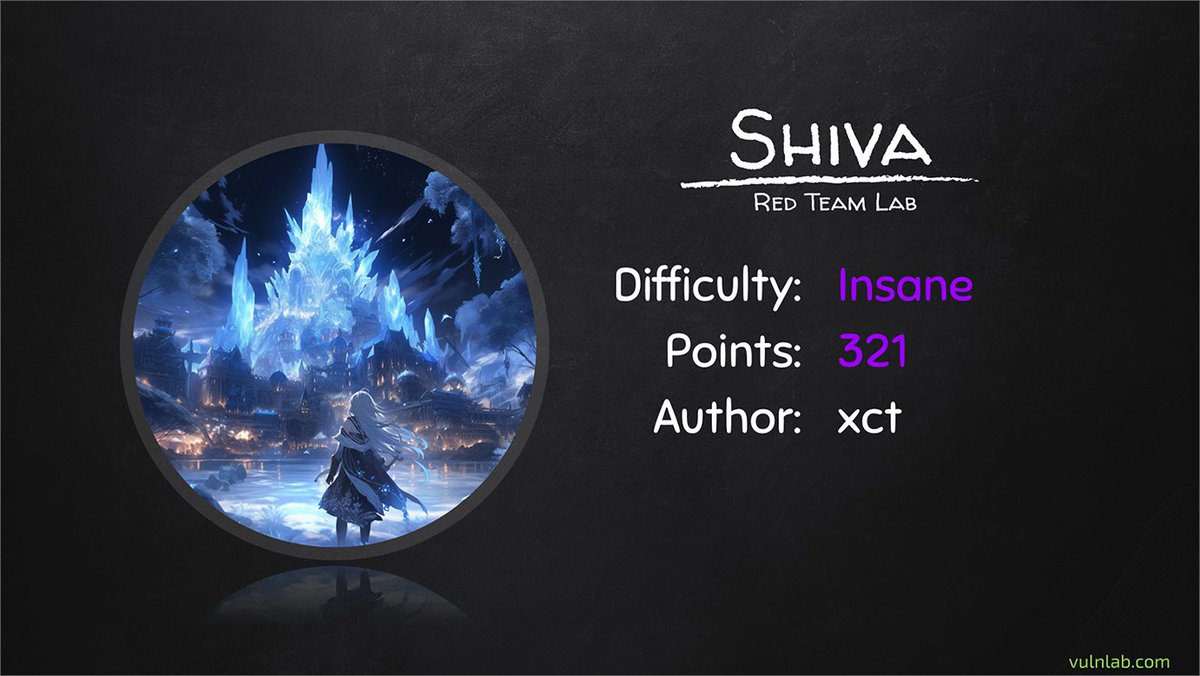
A new Red Team Lab, Shiva, is coming to Vulnlab next week! This time you get to test a hardened Hybrid-AD environment that involves:
- Hybrid-AD with 10+ machines & active users
- Cloud exploitation
- SIEM, EDR on Clients & Servers
- Common enterprise software
- No CVEs
In our latest post, @breakfix details how we were able to publish a malicious VSCode extension to the marketplace and leverage it for initial access during a red team https://t.co/mAHpQM2uCp https://t.co/nBzdsCSzrw
Creating Windows hacking labs has gotten a lot easier with this new tool I've developed: It's a reverse engineering of Microsoft's hidden downloading API - fully automated to always grab the most up-to-date Windows ISO so you never have to do it again! 🚀 https://t.co/IjTzjk3n0L