A Bitcoin treasury company (@Datavault_ai $DVLT) just crashed because they informed investors that they haven't been able to withdraw BTC from the exchange (@BiconomyCom) that is holding all their treasury funds after 4 months of transfer requests.
THIS IS INSANE!!!
A San Francisco startup says it just turned mercury into real gold.
The company is Marathon Fusion. This week they announced they'd made stable gold using fusion neutrons, at 10x the record CERN set in 2025.
CERN's record was 29 picograms over four years. So nobody's pouring bars yet.
The method is what got me. You hit mercury-198 with a fusion neutron. It loses a neutron, becomes mercury-197, and over the next few days decays into gold-197. The exact same gold sitting in central bank vaults.
Their 2025 paper says a one-gigawatt fusion plant built this way could make around 2 tonnes of gold a year as a side product, while it's selling electricity.
I've said it for years. Gold is a shiny rock. It's valuable because there's only so much of it and pulling it out of the ground is hard and expensive.
If this holds up, gold's scarcity turns into an engineering problem. And you can only delay technical progress. You can't stop it.
To be fair, the gold comes out mixed with radioactive isotopes and would need to sit for well over a decade before it's safe to touch. Nobody outside the company has verified the result yet, and commercial fusion is still years away.
Peter Schiff has spent years telling everyone Bitcoin has no intrinsic value.
This week a startup says it made gold out of mercury.
There will only ever be 21 million Bitcoin. No reactor on Earth can make one more.
goethe was 65 when he read hafez in translation, called him his twin and wrote back to a man who’d been dead in shiraz for four hundred years with the west-östlicher divan. a century later iqbal read the divan, understood it as a letter and answered goethe with payam-e-mashriq.
When I visited Papua New Guinea for a day and saw how harmoniously the locals lived with the forest, I was AMAZED!
Now, Indonesia is rapidly destroying the western part of the island on massive scale, causing species extinctions & displacing local communities. Its DISGRACEFUL!😡
For over six decades, the people of West Papua have endured a long-standing struggle rooted in colonial decisions, Cold War geopolitical maneuvers, and contested sovereignty.
Originally a distinct territory under Dutch administration, West Papua was annexed following the controversial 1969 "Act of Free Choice" - a vote in which a tiny fraction of the population was handpicked to vote under coercion, bypassing true democratic self-determination. Since then, indigenous Papuans have faced heavy military presence, severe human rights violations, and the systematic suppression of their cultural and political identity.
Almost sixty years of a people who yearn to be free and yet aren’t being allowed to be free.
Supporting the Papuan cause is fundamentally a matter of defending universal human rights and self-determination. While international bodies champion these principles across the globe, the situation in West Papua is frequently overlooked, allowing widespread displacement, environmental degradation from resource extraction, and restricted access for foreign media and humanitarian observers to continue unchecked. Standardizing international law requires applying the right to self-determination consistently, ensuring that Indigenous Papuans are given a genuine, uncoerced voice to decide their own political and economic future.
https://t.co/cp88sm9rCT
@FieldNas@cellarSQUIDc If the mining cartel starts censoring transactions or push a contentious consensus change, maybe it will be possible to gain momentum for a PoW change from that future block height. But so far it remains theoretical @FieldNas
@FieldNas@cellarSQUIDc Mining centralization is clearly a problem, but so far there simply hasn't been enough justification for a defensive HF like Blake2b. I wish BIP 110 had activated, but the hard truth is that not enough people knew or cared and that's why it didn't activate.
the ledger incident could go way beyond hardware wallets
imagine someone starts putting the same kind of spy implants inside logitech keyboards, or any other big brand of computer gear that's in millions of homes
they could do the same with laptops, phones, tablets and so on
and steal not just crypto but money straight out of your banking apps
this is a really telling example that just exposed a huge threat to every one of us. nobody is safe anymore
$100M across 500+ addresses so far. Crypto hardware wallet owners are freaking out because of a new supply chain attack. Let’s see how we could make it worse!
People are opening their hardware wallets to look for hardware implants. REMINDER: 5 years ago I converted a Ledger into a malicious wallet WITH NO VISIBLE CHANGES. So visual inspection isn’t everything.
The attack seen today is a hardware backdoor that reads the seed phrase right off the screen & sends it to the attacker using its own cellular radio. And it seems the attacker may have purchased an official Ledger reseller so they could ship backdoored wallets to customers. (It’s all still unfolding, not everything is confirmed, new implants are showing up, etc)
A Chinese company bought an official reseller of Ledger, & possibly used an NDA to prevent it from being made public. I will say that even if the new owner wasn’t complicit, mergers & acquisitions are very attractive times to target a company. Lots of stuff is changing quickly, lots of new names, lots of urgent needs, etc.
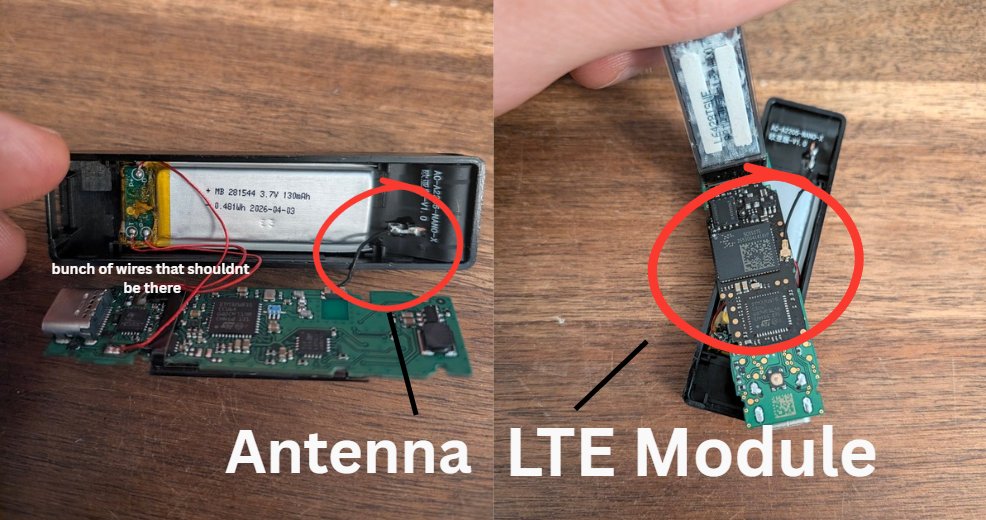
In theory, the reseller is where they inserted the implants. They opened legit Ledger wallets and added an extra PCB with extra components. The implant tapped the lines of the Ledger’s screen & was able to read the seed phrase exactly as shown to the user. This phrase was then sent out over a slow cellular radio designed for low traffic IOT.
Tapping the screen has been a known attack. Joe Grand did a talk on it earlier this year. We have seen more “primitive” looking implants that do it.
But buying a company is a big step forward from prior attempts. I wouldn’t be surprised if there was some state funding here. I guess we will find out as people dig into the corporate paper trail of the business, the account associated with the cell service, etc.
Hardware wise, they cleaned things up a lot to make it less noticeable to a wallet owner who opens the case. But I can’t help but wonder why they didn’t improve a few areas… I’ll go into that in replies to this post.
🧵1
Here’s a test for your self custody:
Tell your next of kin to retrieve your coins as if you had died. They are only allowed to use the info they have now. No new note or instructions allowed- if you died today they wouldn’t have those instructions either.
See how the test works.
The UK banking system is raped
>try to transfer £3k ($4k) into my kraken brokerage
>use Face ID, type in password, goes through 2FA
>account and payment still gets frozen
>can’t call because I’m in Iraq
>customer services can’t help
>transfer £3k to empty account with another bank
>they spend 30 mins on the phone going through scam questionnaires.
>tell the indian woman to fuck off and let me spend my money
>call cuts out because I spent £100 calling internationally
>try transferring my money back to main account
>account gets frozen and I have to call up to confirm the payment.
I regularly get £40k+ payments into this account and they panic over a £3k transfer.
The UK is poor and raped
LEDGER HARDWARE WALLET IMPLANTS WERE DISCOVERED OVER A YEAR BEFORE THIS WEEK’S SUPPLY-CHAIN ATTACK REVELATIONS
Renowned hardware security researcher and computer engineer Joe Grand (@joegrand), also known as “Kingpin,” explains how he was contacted in August 2025 by a man in Thailand who had discovered a compromised Ledger Nano X.
The man had purchased a cheap Ledger online to replace the battery in his existing device.
When he opened it, he discovered a smaller battery, unauthorized circuitry, additional wiring, and an antenna.
After posting his discovery on Reddit and reportedly receiving little interest from local police, he contacted Grand to investigate.
The discovery came more than a year before the Ledger supply-chain attack became a major public controversy, with nearly $100 million in cryptocurrency reportedly stolen this week.
@jordanBTCplz@FieldNas Deriving a bunch of seed phrases or WIF keys from the backup with BIP-85 is an option, I suppose. Not a terribly elegant workflow though.
@jordanBTCplz@FieldNas There should be a standard for this. First device only responsible for deriving child keys with fully hardened paths, while a second signing device only sees individual WIF child private keys when a transaction has to be signed. Safe against quantum & dark skippy
UPDATE: I can confirm that the Ledger supply chain is compromised in Europe as well. @Ledger should initiate an immediate product recall to protect users.
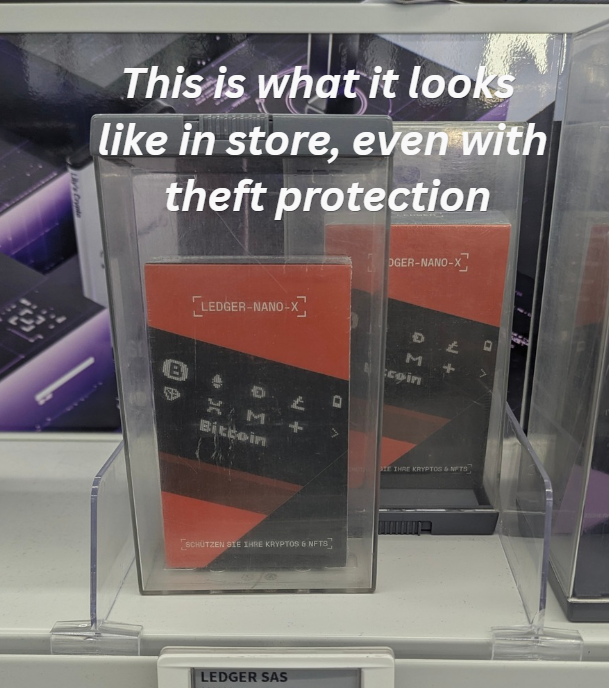
I just purchased a second device from a different Mediamarkt location today, recorded the unboxing process, and discovered spyware once again (video linked in the second tweet).
The device was compromised in the exact same manner, featuring identical modifications (such as additional cables and an LTE module). This indicates its a widespread issue rather than an isolated incident, potentially affecting Ledger inventory across MediaMarkt and Saturn stores throughout Europe (comprising over 1,000 stores across 11 countries).
My initial hypothesis was that these devices were returns that looked unopened to the employees and were just sold again as new however, a MediaMarkt employee confirmed that the device I purchased was not a return, and that returned Ledgers are sent directly back to the manufacturer rather than resold.
Store records show the inventory originated from Aqipa GmbH. While Ledger's CTO was unsure if Aqipa serves as the direct distributor between Ledger and MediaMarkt, it appears to be the case. Given that Aqipa distributes across Europe, any physical retail store receiving stock through them may be at risk.
I sent the first ledger to mark and the second one is going to ledger now, so that they can analyse it.
If you purchased a ledger from anyone other than the official ledger store, make sure to check your device!!