🚨 Pryx claims he warned former associate Rey against targeting the FBI. He says he has left cybercrime behind and is building a cybersecurity startup.
#Pryx#ShinyHunters#Hellcat#ThreatIntel
🚨 FBI arrests another suspected ShinyHunters associate linked to the recent FBI Jobs website breach.
The suspect was reportedly detained in Pennsylvania and is believed to be a Canadian citizen.
This marks another major development in the ongoing investigation.
🚨 ShinyHunters reportedly extorted a former Boeing business unit shortly before recent arrests.
The group allegedly stole sensitive data that could pose operational and security risks.
#CyberSecurity#ShinyHunters#CyberCrime
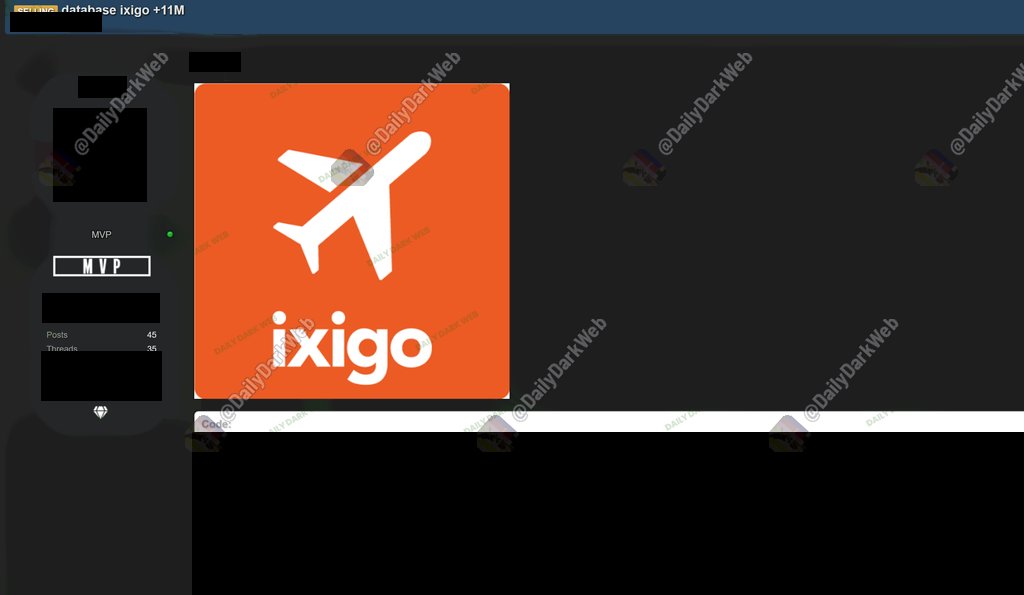
🇮🇳 🚨 IXIGO (INDIA TRAVEL PLATFORM) +11M RECORDS ALLEGEDLY OFFERED FOR SALE
A threat actor on an underground forum claims to be selling data allegedly associated with ixigo (Le Travenues Technology Ltd), the Indian online travel booking platform for flights, trains, buses and hotels.
The listing shows:
* Title: "database ixigo +11M"
* The ixigo logo
* Sample rows: SMS logs from the "OIXIGO" sender with ixigo verification / account-activation codes sent to mobile numbers (visible rows: Qatar and France), with carrier, delivery status and timestamps dated Jan 19, 2026
* Claimed scope: 11M+ records (title "+11M")
The claim has not been independently verified.
⚠️ Analyst Note:
ixigo is one of India's largest travel apps, so the brand will draw attention. But the visible sample is only OTP/verification SMS delivery logs (recipient number, carrier, code text). It does not show customer profiles, booking data, passwords or passport numbers, so those are NOT part of this claim. It is one of a burst of near-identical "Database <brand>" listings by the same actor (earlier today: eGovBahrain, Medgulf, Borders, Housing[.]com, HSBC, BankBeirut, Binance, Noon; this batch also Dubai Smart Travel, Morafiq, La Marquise Diamonds, Me Courier, Halamama and others). The samples share one SMS-aggregator log schema (gateway/route column, recipient number, country, carrier code, delivery status, message text), which points to third-party SMS-gateway logs split by sender brand rather than a separate breach of each brand. Unverified threat-actor claim, NOT confirmation that ixigo systems were breached. If authentic, phone numbers tied to ixigo accounts could be used for travel-booking smishing and OTP-phishing lures.
#DDW #DarkWeb #India #ixigo #Travel #ThreatIntelligence #CyberSecurity
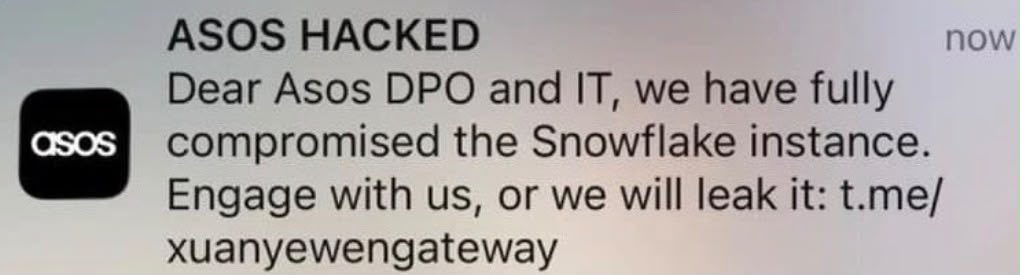
🚨 ASOS hacked !!
Thousands of customers received a fake “ASOS HACKED” push notification. Attackers claimed access to ASOS data via Snowflake.
ASOS says customer data may have been accessed. Investigation ongoing.
#ASOS#CyberAttack#DataBreach#CyberSecurity#ThreatIntel
🚨 🇺🇸 FBI removes Accenture contractor after patch failure linked to ShinyHunters breach
The FBI removed an unidentified contractor on Monday after determining that a security patch was not installed on a platform managed by a third-party organization.
⠀
Two sources told Reuters that the contractor worked for Accenture and the affected platform was Oracle PeopleSoft. The FBI did not publicly identify either company.
⠀
ShinyHunters said it exploited PeopleSoft to compromise the FBI’s employment portal last month.
The breach exposed sensitive information belonging to thousands of FBI employees, including:
• Counterintelligence job descriptions
• Home addresses of human intelligence operatives
• Medical and psychiatric records
⠀
Accenture said it remains proud to support the FBI but did not address questions about the contractor or the alleged patching failure.
The FBI said it has taken steps to mitigate further risk and protect its workforce.
Source: https://t.co/ZMCu3ezle2
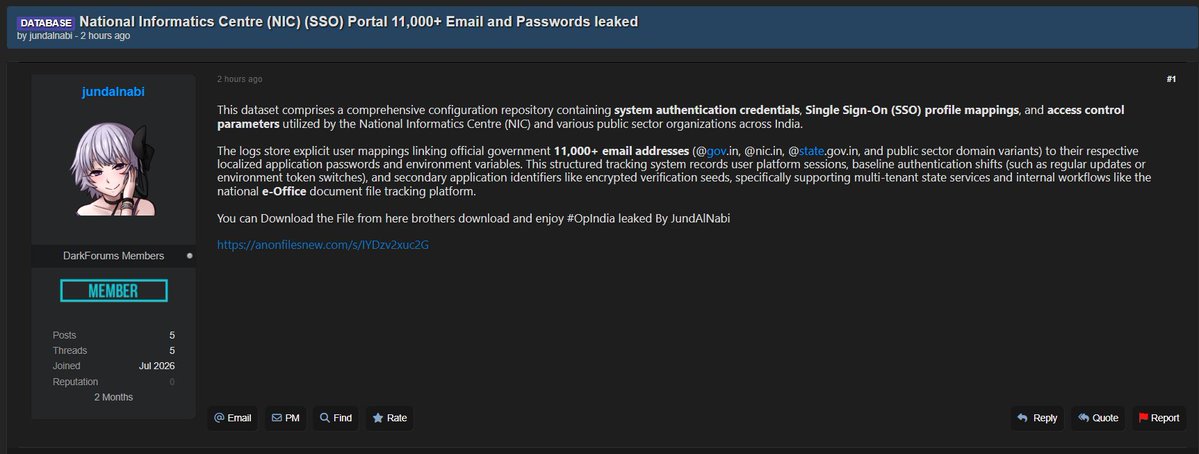
‼️DATABASE LEAK CLAIM — India 🇮🇳
A threat actor using the alias jundalnabi claims to have leaked 11,000+ email addresses and passwords allegedly linked to the National Informatics Centre (NIC) SSO Portal and various Indian public-sector organizations.
Claimed data includes:
• @gov.in / @nic.in / state government & public-sector accounts
• SSO profile mappings
• Application authentication credentials
• Environment variables/tokens
• Secondary application identifiers
• Authentication/session-related information
• References to multi-tenant state services and e-Office workflows
⚠️ The dataset’s authenticity, origin, and current validity have not been independently verified. If genuine, exposed government credentials could pose significant risks to unauthorized access and account compromise.
#CyberSecurity #DataLeak #India #NIC #Government #SSO #CredentialLeak #DataBreach #ThreatIntelligence #InfoSec
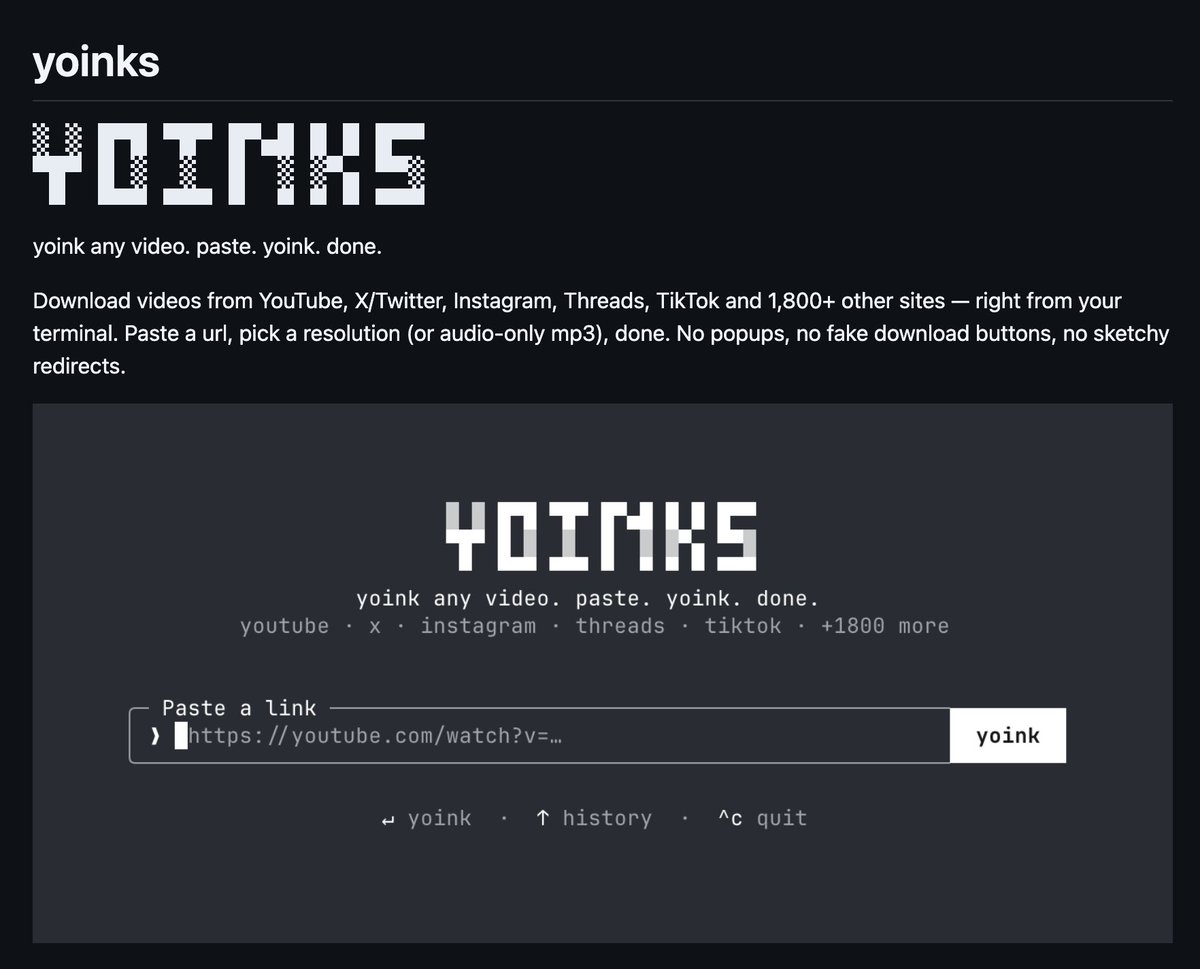
❗️ Yoinks is a free, open-source tool that pulls videos from YouTube, X, Instagram, Threads, TikTok and 1,800+ other sites straight from your terminal.
You paste a URL and it's done, with no popups, no fake download buttons and no sketchy redirects.
https://t.co/dz6TlNArg4
🚨 ShinyHunters update:
A key alleged ShinyHunters member, Saif al-Din Khader aka “Rey,” has reportedly been detained in Jordan and is cooperating with the FBI, according to Reuters.
He is reportedly helping investigators to identify other members.
https://t.co/Lglqgncz81