‼️ WARNING: Attackers are exploiting a critical FortiMail flaw that allows unauthenticated arbitrary file writes.
CISA added "CVE-2026-104286" to KEV. Fortinet published IOCs and workarounds, with fixes still pending for some versions.
Learn more: https://t.co/sNErB5MROX
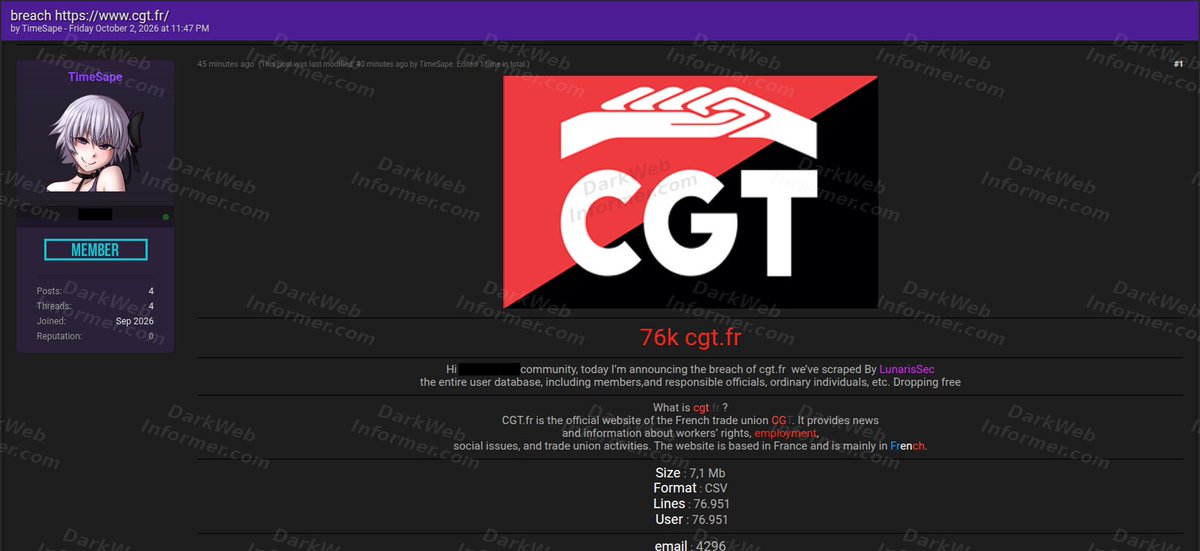
🚨 DATA BREACH: CGT France dataset containing more than 76,000 records allegedly exposed
⠀
📌 #France 🇫🇷
⠀
An actor using the handle "TimeSape" claims to have breached CGT, the French trade union Confédération Générale du Travail, and released a dataset containing member and official information.
⠀
According to the listing:
⠀
• 76,951 total records
• 76,951 listed users
• 4,296 email addresses
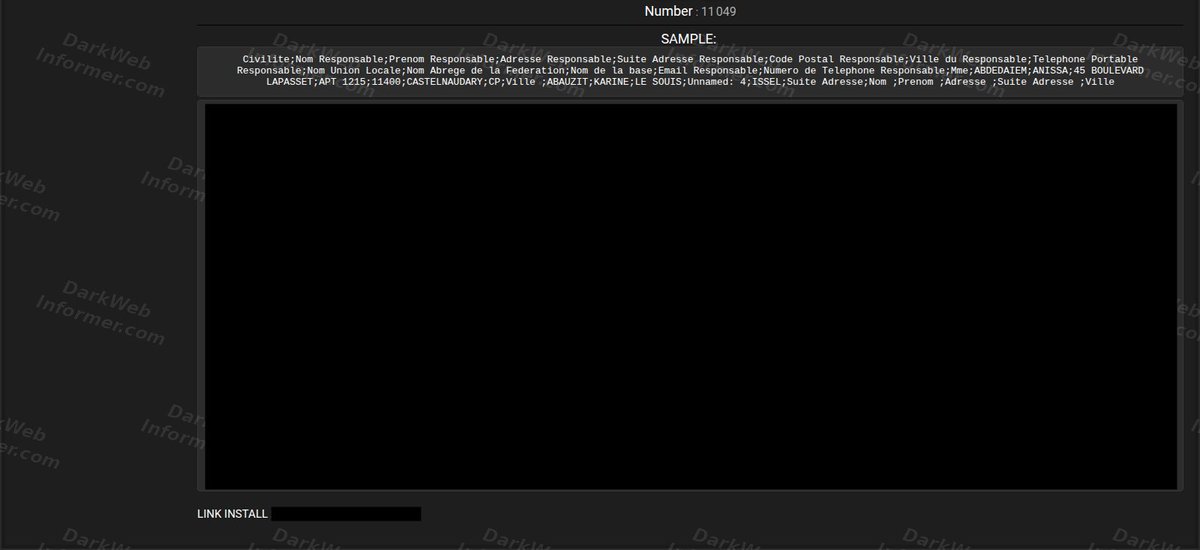
• 11,049 phone numbers
• 7.1 MB CSV file
⠀
The exposed fields are said to include names, addresses, postal codes, cities, phone numbers and information relating to union officials and members.
⠀
The actor claims the entire user dataset was obtained and released publicly, with a sample of the records included in the post.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
Fortinet’s FortiMail is under active zero-day attack. CVE-2026-104286 is a critical path-traversal flaw that could let attackers write arbitrary files to vulnerable systems. FortiMail administrators should…
Source: https://t.co/upcYIEHpMr
October is Cybersecurity Awareness Month! Throughout the month, we'll be sharing guidance to help you stay ahead of digital threats and keep your data safe. Visit our site for guidance and more: https://t.co/THaXl0v86u
The 2026 Microsoft Digital Defense Report is out today, examining a threat landscape increasingly defined by interdependence. Read the full report: https://t.co/uaBb5uf4H8
Connections among identities, AI systems, cloud services, software supply chains, edge infrastructure, and critical systems can create points of leverage where one compromise has effects far beyond the initial target.
AI is accelerating familiar threat actor tradecraft rather than replacing it. Identity compromise, credential reuse, social engineering, and exploitation remain prevalent, but automation enables adversaries to conduct these activities with greater speed and scale. In 52.2% of intrusions involving valid accounts, attackers pursued additional credential theft, creating opportunities for one compromised identity to fuel further unauthorized access.
These operations leave signals across identities, endpoints, infrastructure, applications, cloud environments, email, and networks. Individually, those signals may provide only a partial view. When correlated with threat intelligence, they can reveal threat actor activity across campaigns, clarify how an intrusion is progressing, and surface risks that isolated investigations may miss.
For defenders, success increasingly depends on connecting telemetry quickly enough to understand adversary operations and act before threats can escalate.
Get more insights on this year’s report from Terrell Cox: https://t.co/daNQk30mEB
Vulnerabilidades de ModSecurity permiten saltar el WAF
Se han revelado múltiples vulnerabilidades en OWASP ModSecurity que podrían permitir a los atacantes evadir las protecciones del firewall
https://t.co/GKUSsrcIIB
Un usuario de un foro de hackers ha publicado #dataleak, posiblemente vinculado a #UTEC Universidad Tecnológica en #Uruguay 🇺🇾 (@UTECuy).
Monitorea este incidente en VenariX https://t.co/gA0ngluP02
🚨 On 9/22/26, #F5 published a security advisory for CVE-2026-94127 – a critical heap-based buffer overflow vuln. affecting F5 BIG-IP APM.
An unauth. attacker with network access to an affected virtual server may be able to achieve RCE. More in our blog: https://t.co/ueLzxdbkLu
Australia said an OpenAI agent breached a government health data portal in June, gaining unauthorized access to files, in what could be the first known instance of an AI agent hacking a government website. Here’s what we know https://t.co/ivIuGmzaSe
❗ ALERT ❗
We are aware of instances of AI misalignment, where AI agents have taken unexpected or unauthorised actions.
Australian organisations should maintain strong cyber security controls and secure AI practices.
Read the full alert 👉 https://t.co/gUSwkuGEDJ