💼 Incident Responder Interview Questions
A collection of interview questions and answers for IR roles
Categories:
• General
• Network
• Event Log Analysis
• Digital Forensics & Incident Response
by @LetsDefendIO#cybersecurity#blueteam
https://t.co/3ppiiyd1dZ
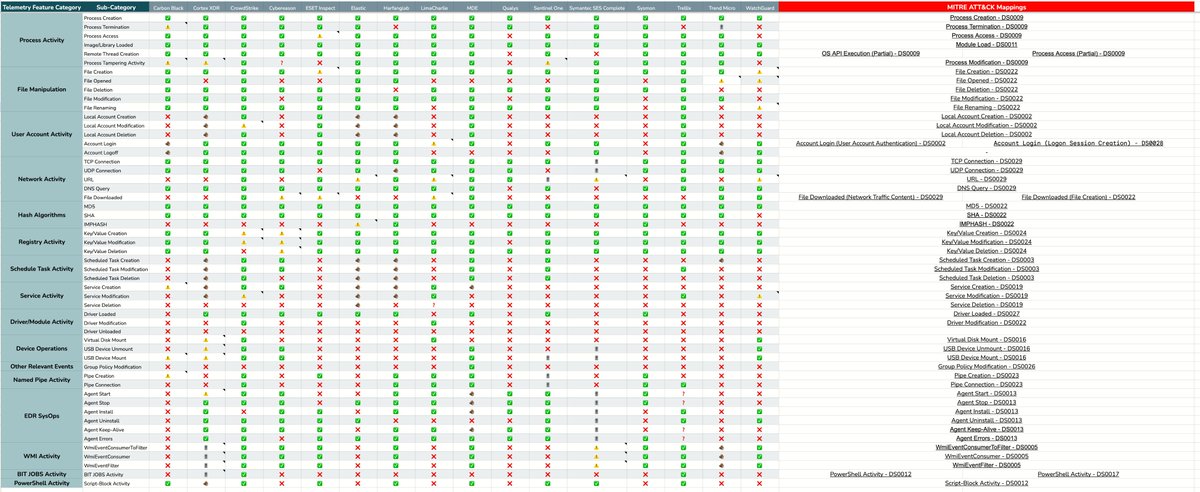
🚀Major Update: EDR Telemetry Project🚀
I updated the EDR Telemetry Project to make the table accessible for color vision deficiencies, map all sub-categories to Mitre ATT&CK and more. (Read below👇)
Many thanks to all who contributed to this major update! Here are some changes:
✨ New EDR Additions:
✅ Cortex EDR!
✅Symantec SES Complete!
🛠️ Enhancements and Fixes:
• Color Accessibility Enhancements
• Mitre ATT&CK Mapping (Thanks to @jamieantisocial and sorry it took so long 😬)
+ Elastic Telemetry Corrections
+ HarfangLab Telemetry Corrections
🎯New Additions Coming Up:
🔜 Sophos EDR
+Linux Telemetry Table (Started planning)
A huge shoutout to everyone who contributed! Your support and feedback are what drive this project forward. 🙌
🔗 GitHub Page: https://t.co/8DmXzffYVC
🔗 Telemetry Table: https://t.co/6nvs6ymqof
Good news for everyone involved in meetings where TLP classifications is needed! I've just updated my repository with the latest, second edition of the TLP Classification Meeting Posters.
https://t.co/8dTElF2fVH
@FIRSTdotOrg
A Beginners Guide to Tracking Malware Infrastructure
New post with 11 Examples (Including Cobalt Strike and Qakbot) that you can use to query and track C2’s, Open Directories and More🔥
(Special thanks to @censysio 🥳)
https://t.co/9h1Q07mbuj
#threatintel#malware
We see a lot of threat actors in our Incident Response cases who disable or tamper with the local AV.
The website https://t.co/MemtjlKd1M has a copy & paste script to turn off most of Defenders features. [1] How many of these modifications (or deactivations) will trigger an alert in your environment?
@DebugPrivilege has written an excellent article about the various event logs Windows Defenders creates, in which event. [2]
Run the commands on a test system, and look for gaps in your monitoring 🤓
[1] https://t.co/OCGYQJholX
[2] https://t.co/JPZYdfPSFC
A good IT support request includes:
- End user request context (role, request history, availability via calendar and Slack/Teams status)
- Output from orchestration actions (e.g., Okta shows end user is locked out, also seeing 2FA failures)
- Diagnostic/investigation support (take these steps to validate)
- Environmental context (IT policy says “x”)
- Resolution actions (fix issue by running “this” workflow or taking these steps)
- Conversational support using LLMs
- Able to answer, “Is anyone else experiencing this problem?”
A good alert includes:
- Detection context
- Investigation/response context
- Orchestration actions
- Prevalence info
- Environmental context (e.g, src IP is scanner)
- Pivots/visual to understand what else happened
- Able to answer, "Is host already under investigation?"
New #DFIR content added: playlists, channels, downloads, books, podcasts, CTFs, forensic test images, and more.
https://t.co/IXLh5YZRJx #digitalforensics
For too long Incident Response has relied on industry experience, consultants, or 4000 page compliance frameworks that are too hard digest.
I am going to fix this. I am writing a fully open-source "Awesome Incident Response guide". https://t.co/aJyv1BeIuk
Today, me and @ateixei are releasing the EDR Telemetry project. This project aims to compare and evaluate the telemetry of various EDR products.
✅Introductory blog post: https://t.co/hGu2fcqSAT
✅GitHub Repo: https://t.co/0xjL53X5Mg
✅Comparison Table: https://t.co/RAP33Wf5rB
📏 Performance metrics, part 1: Measuring SOC efficiency
@jhencinski on building an effective SOC
3 key metrics:
1. When do alerts show up?
2. How long do alerts wait before being actioned?
3. How long does it take to go from alert to fix?
https://t.co/RhiZ2qjT8R
Microsoft Digital Defense Report offers interesting statistics and insights about security posture. The following chart shows missing security controls (such as Admin workstations or privilege isolations).
I can only strongly recommend to read the report:
https://t.co/ynYjVfIyZV
A list of Incident Response resources:
NIST: https://t.co/grUTuXZ0JV
CIS: https://t.co/4qDKGazrOI
SANS: https://t.co/wHgwuWIpaF
Red Canary: https://t.co/EP3ZceEUYs
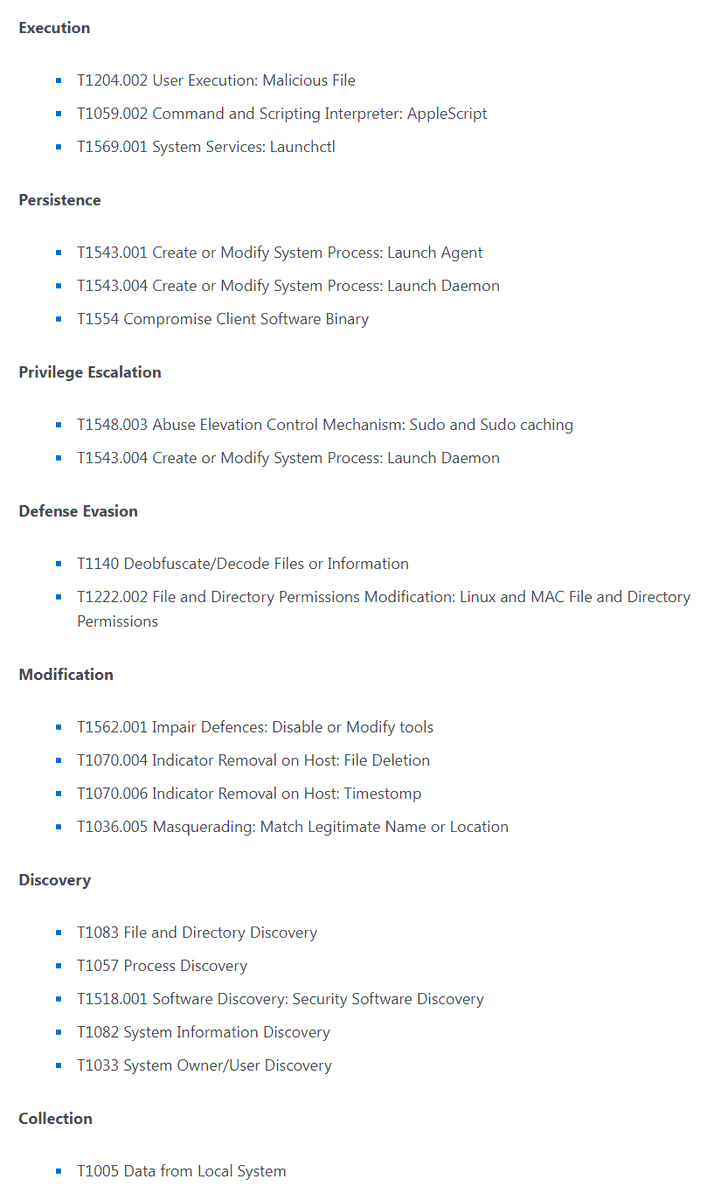
Microsoft shares details from the analysis of known ransomware families affecting macOS devices (KeRanger, FileCoder, MacRansom & EvilQuest), which, despite being old, exemplify the range of capabilities & malicious behaviour possible on the platform. https://t.co/MQAOvkTTxs