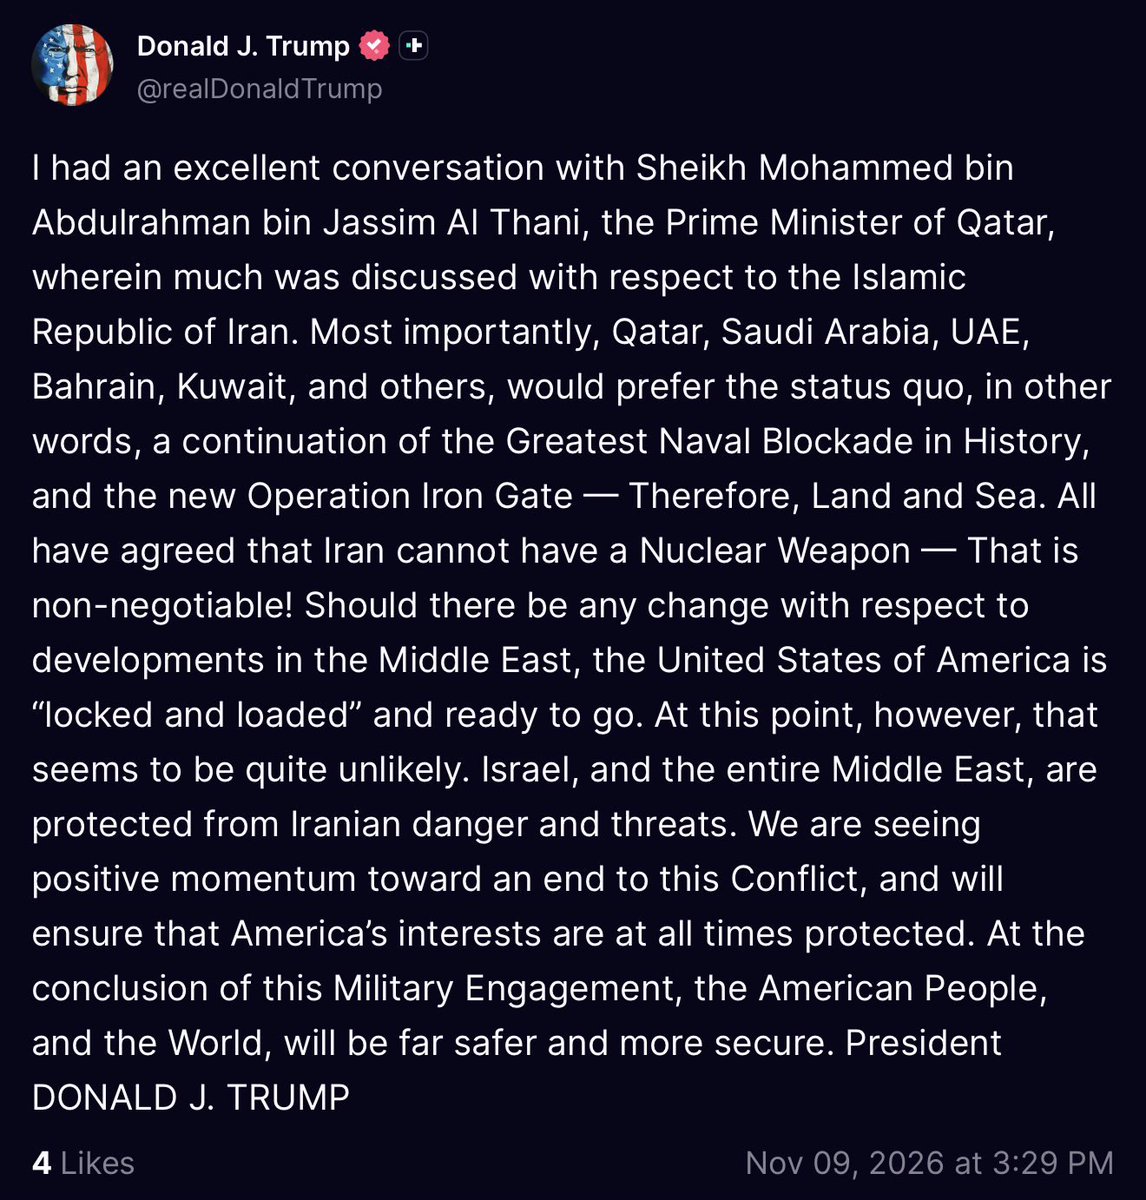
Trump really trying to signal that he thinks this war can come to an end…
- UNLIKELY TO FURTHER ATTACK
- WE ARE SEEING POSITIVE MOMENTUM TOWARD AN END TO THIS CONFLICT
private keys from 8 intermediate CA certs have been compromised (eMudhra)
Happy "Update everything" day to all my pager-carrying friends
https://t.co/7ASSy72Rxg
Veeee @GuvenlikTV 'nin yıl sonu özel bölümünde @halilozturkci@warex ile birlikte tekrar karşınızdayız! Keyifli seyirler dileriz.
https://t.co/gYku8zM4xB
Özledik, özlettik ve nihayet 2 yıl aranın ardından “@GuvenlikTV ’den Herkese Merhaba!” diyerek tekrar karşınıza gelmeyi başardık! Siber güvenlik dünyasını ve yeni gelişmeleri konuştuk. Bu keyifli sohbete sizleri de davet ediyoruz. 👇
https://t.co/bNxFwrKVdg
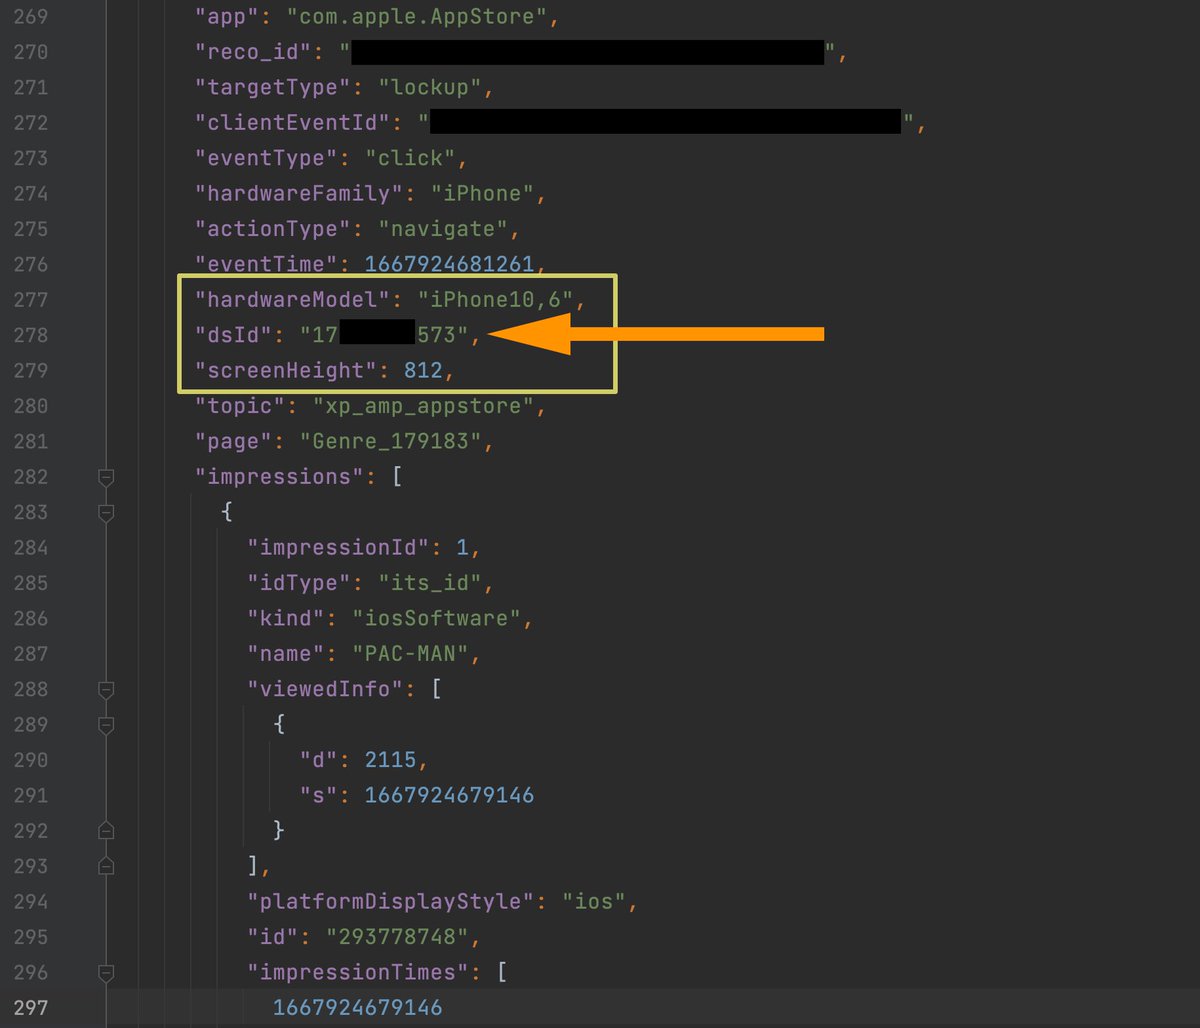
🚨 New Findings:
🧵 1/6
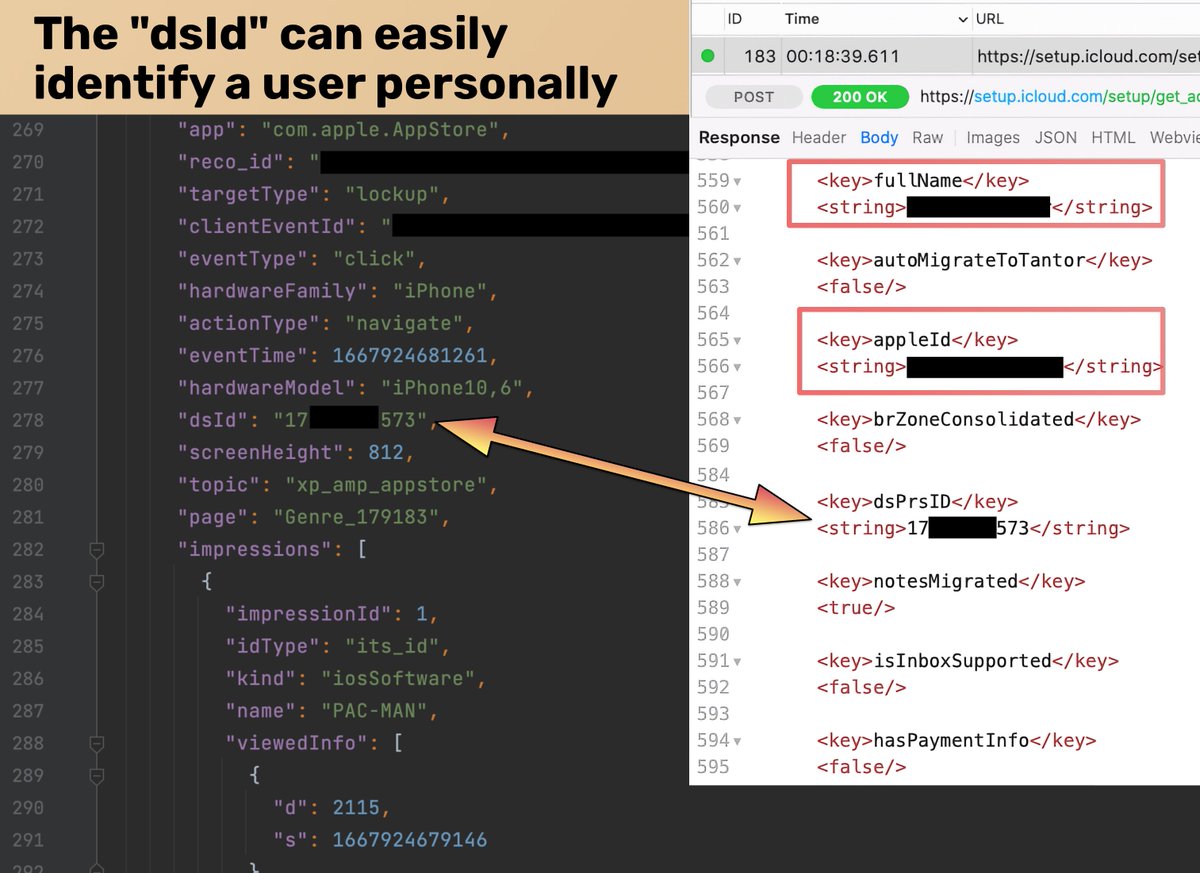
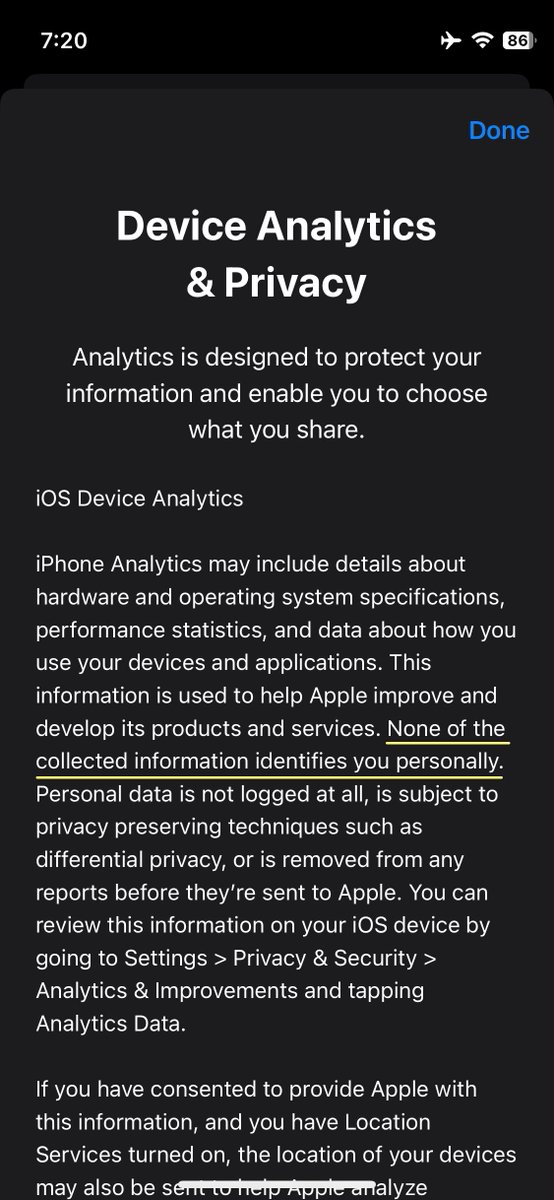
Apple’s analytics data include an ID called “dsId”. We were able to verify that “dsId” is the “Directory Services Identifier”, an ID that uniquely identifies an iCloud account. Meaning, Apple’s analytics can personally identify you 👇
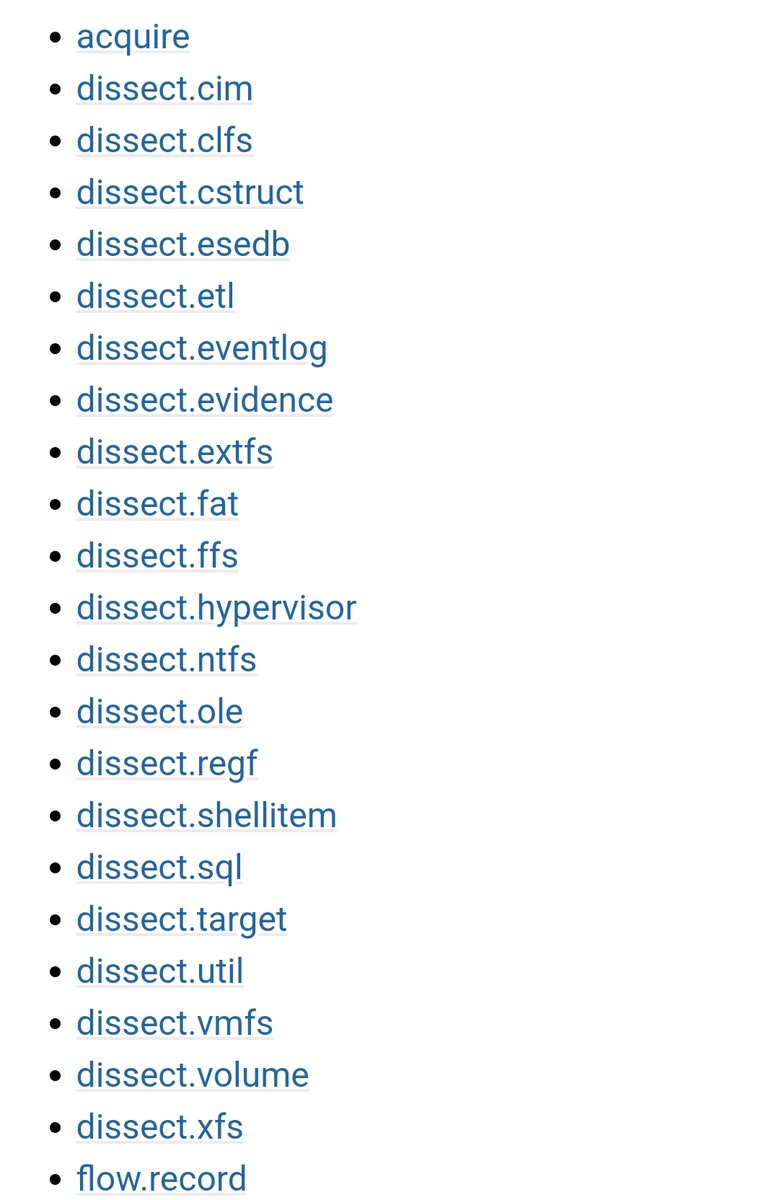
Fox-IT just open sourced their enterprise forensics tooling dissect. This is a big project that some of the smartest people I know have worked on. It supports many filesystems and file formats, all as Python libraries. Docs: https://t.co/M6YAygmW3E / code: https://t.co/HKT4eYIm1a
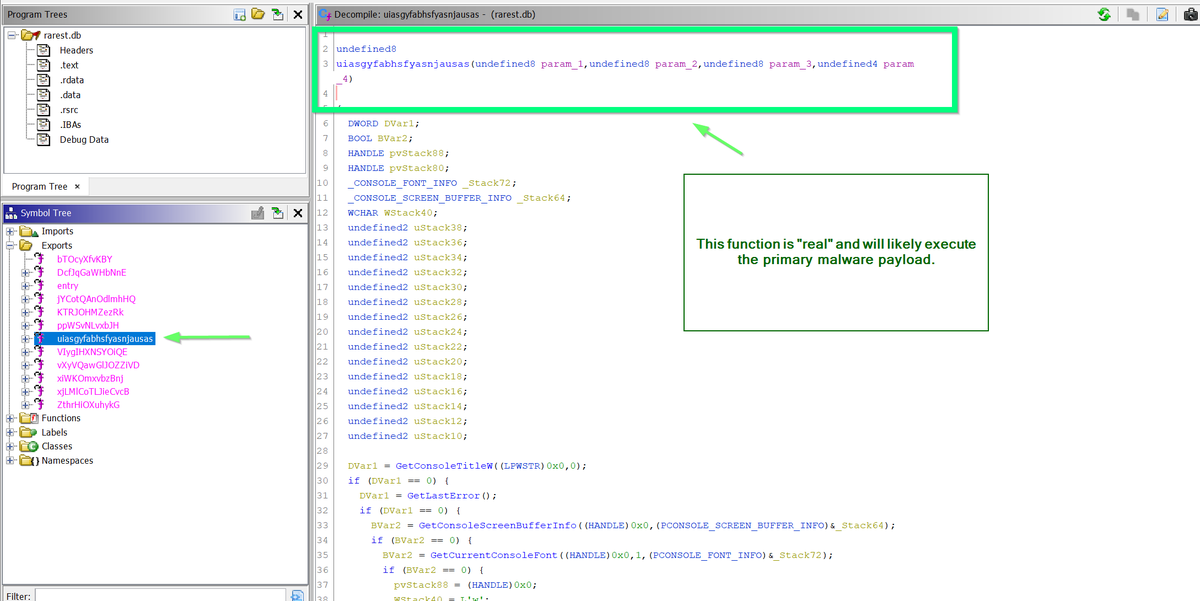
A quick demo of how to identify "real" exported functions from a #obfuscated#IcedID dll file.
I'll also briefly touch on some #Ghidra tips, and how to extract #shellcode using a debugger.
A moderate sized thread😃
[1/13]
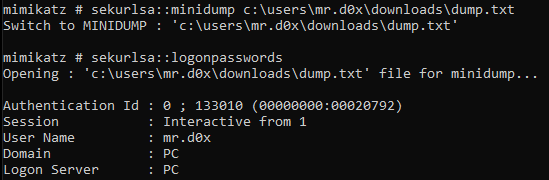
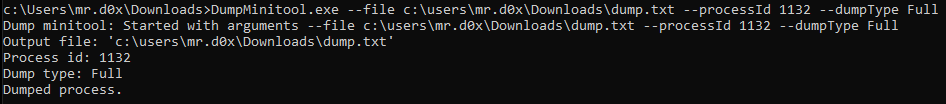
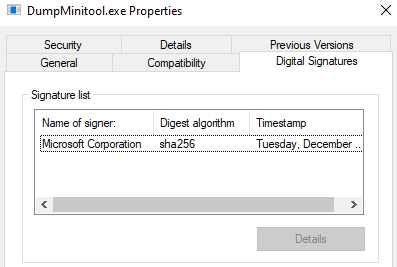
LOLBIN to dump LSASS:
Path: C:\Program Files\Microsoft Visual Studio\2022\Community\Common7\IDE\Extensions\TestPlatform\Extensions
Binary: DumpMinitool.exe
The params are case sensitive.
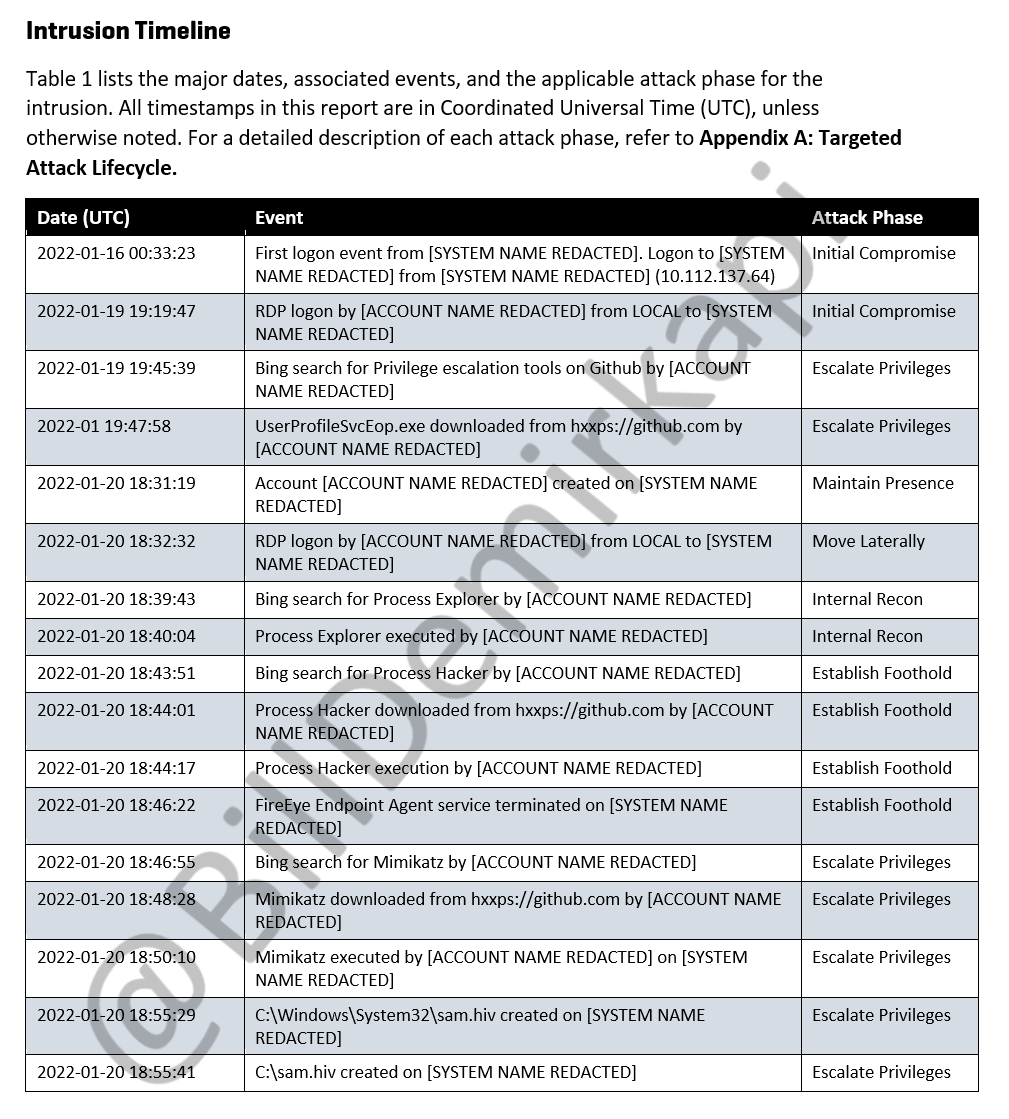
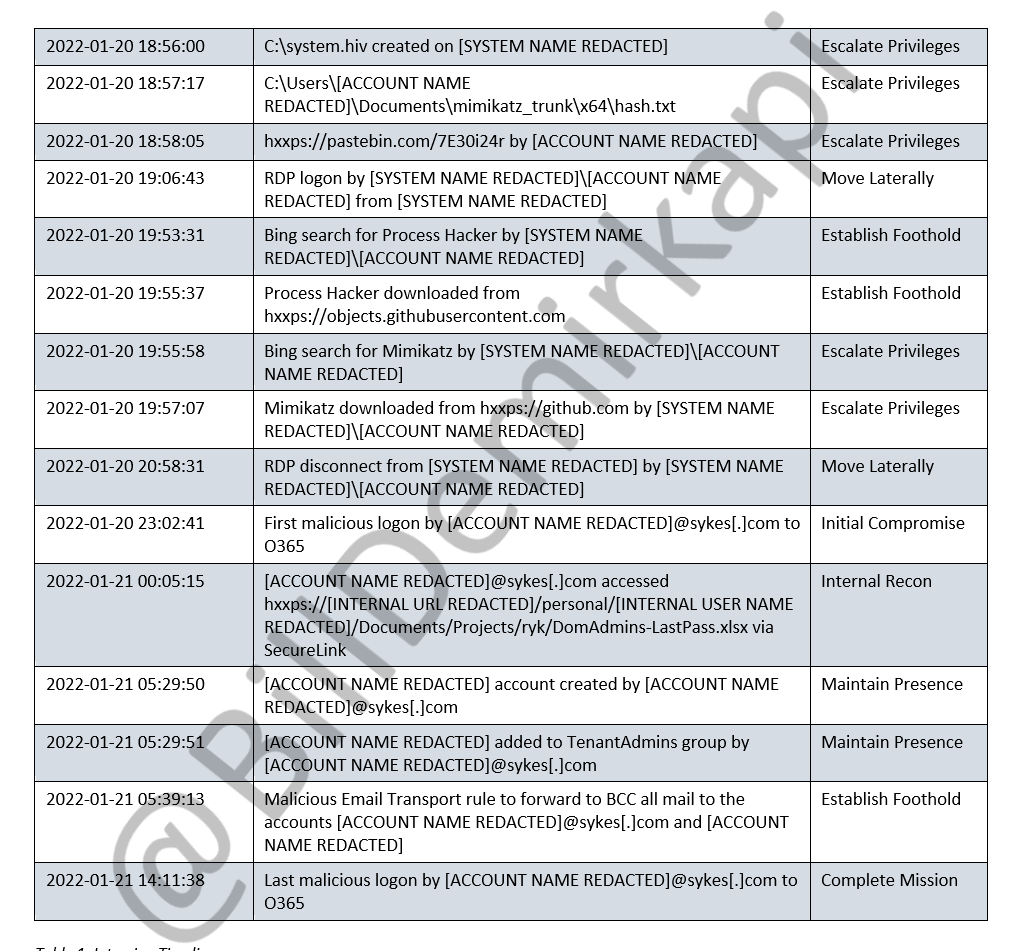
New documents for the Okta breach: I have obtained copies of the Mandiant report detailing the embarrassing Sitel/SYKES breach timeline and the methodology of the LAPSUS$ group. 1/N https://t.co/z05uQYclg9
Cyber-attack strikes German fuel supplies. Oiltanking Deutschland GmbH & Co. KG says it is operating at a 'limited capacity' and has declared "force majeure" for the majority of its inland supply activities in Germany. https://t.co/O4vNLYGo8j
Didn't see this yesterday night.
Ukraine's Derzhspetszviazok published a statement on their preliminary investigation into #Whispergate.
- 22 gov websites were affected
- 6 sites were 'severely damaged'
- 70 sites were shut down at the request of the Derzhspetszviazok & SBU
When analysts examine evidence, they are looking for cues that have implications for action. Cues lead to decisions about what leads to pursue or how to respond.
There are several types of cues, but I think novelty cues are one of the most critical. Let's talk about why... 1/
@GossiTheDog Indeed, it would have multiple components - but it will also depend on where the vulnerability is, and how it is exploited. Outbound connection/attempt is the key