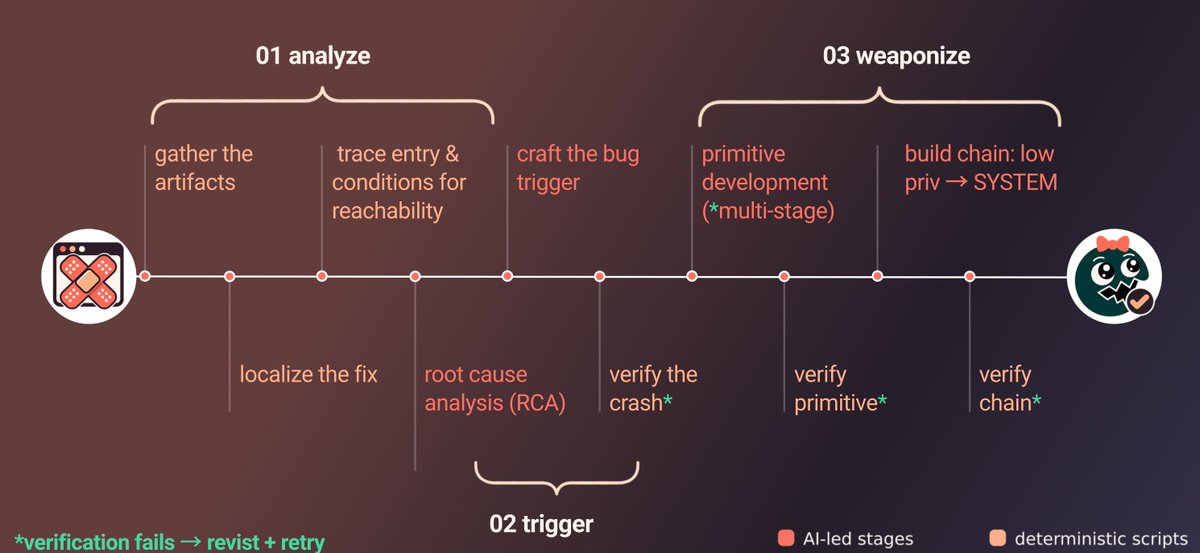
Good morning, we escaped the famous Firecracker VM and got root execution on the host.
Full firecracker escape technical writeup and Proof of Concept code attached below.
Claude found with ~zero prompting:
- Linux kernel 0click "packet to root" RCE (!!!!!)
- Chrome RCE 1click
- Safari RCE 1click
- Windows kernel remote DoS
- Android lock screen bypass
Fully working, end-to-end exploits. Prompting was minimal like "pls make RCE"
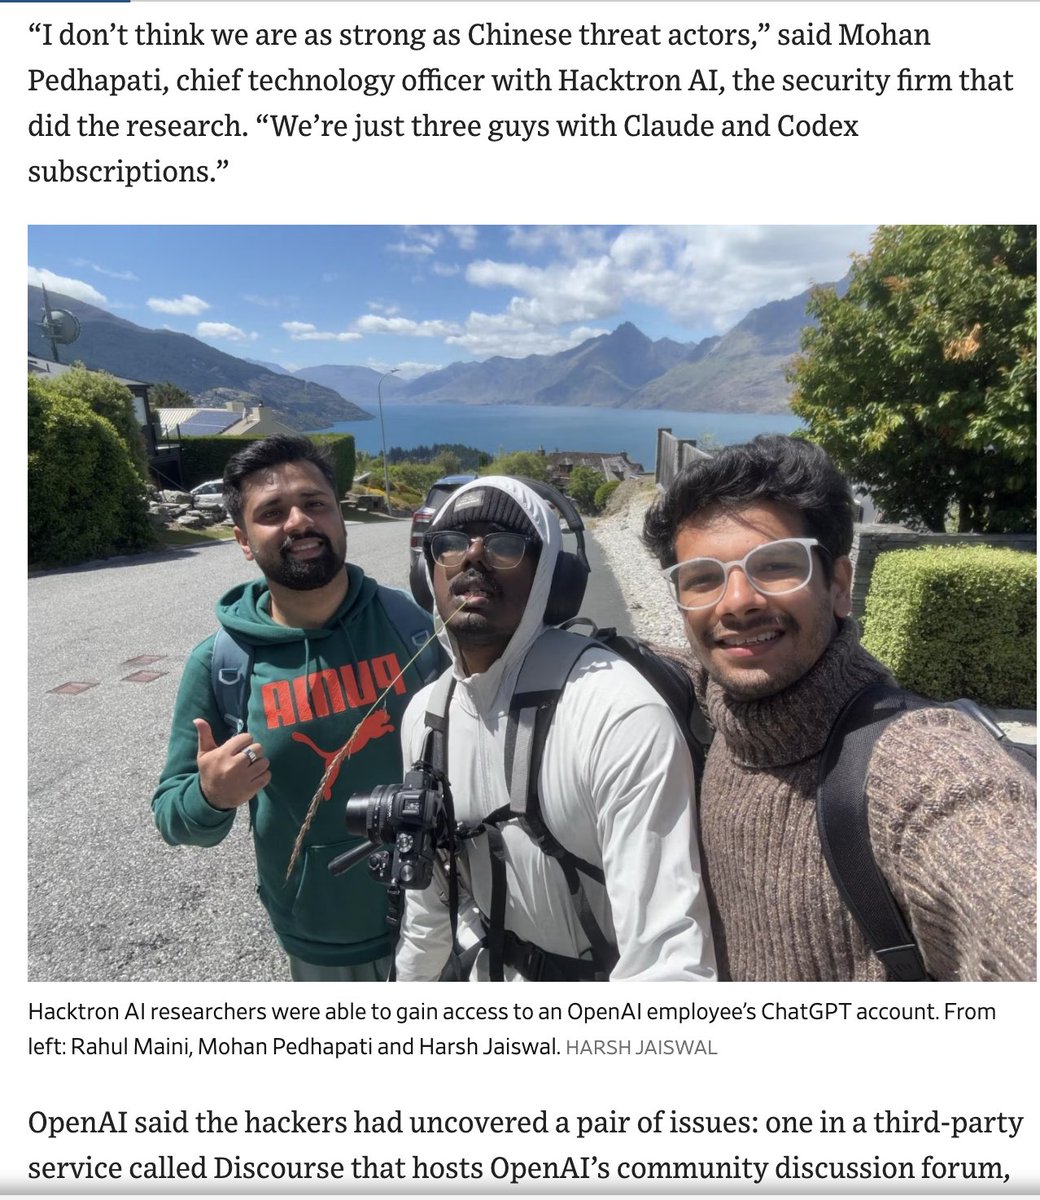
On July 25, we hacked OpenAI.
Two bugs let us take over ChatGPT/Codex accounts of OpenAI employees (+some unaffiliated users) and reach connected services: Outlook, Slack, GitHub, etc.
We proved it with a PR in OpenAI’s internal codebase . It took us <72h. 🧵
"3 random dudes”
1. hacked apple, again and again.
https://t.co/5aZcB0RbjF
https://t.co/UdsKrmfFJW
https://t.co/hWDQaimW8c
2. your github enterprise is our github enterprise.
https://t.co/u3UjajnBKq
3. get a discord message from me, get pwned.
https://t.co/pX3RkjxNOX
https://t.co/noscPNmZm9
4. oh yeah, at one point we basically had shells across the electron ecosystem. check the DEF CON research.
https://t.co/1Th5fvpa21
5. your supabase database is my database.
https://t.co/nOIKthdDnM
6. we got the posthog prod database.
https://t.co/VIeGJz1hKq
7. react2shell? vercel paid us $170k for helping secure their waf.
https://t.co/Y2RgQSdl3g
8. your palo alto vpn is my vpn.
https://t.co/oVB068UhST
9. ai ides? we got shells for you, antigravity
https://t.co/tsvSXQuSS0
10. windsurf rce.
https://t.co/DpdGqmNRvu
11. turning cluely into malware.
https://t.co/8QcIYhXQfS
12. ai browsers? sure, uxss: your perplexity browser is my browser.
https://t.co/WVXlHzY0CB
13. openai atlas too. kinda uxss
https://t.co/jkQWnLD7rV
14. hey, it’s not even our first time hacking discourse.
https://t.co/viI1op7aMf
15. adobe coldfusion: pre-auth rce. because apparently we needed another one.
https://t.co/aFILo3suP2
there’s a lot more. go dig.
anyway, yes: “3 random dudes.”
and @HacktronAI is full of more random dudes like these.
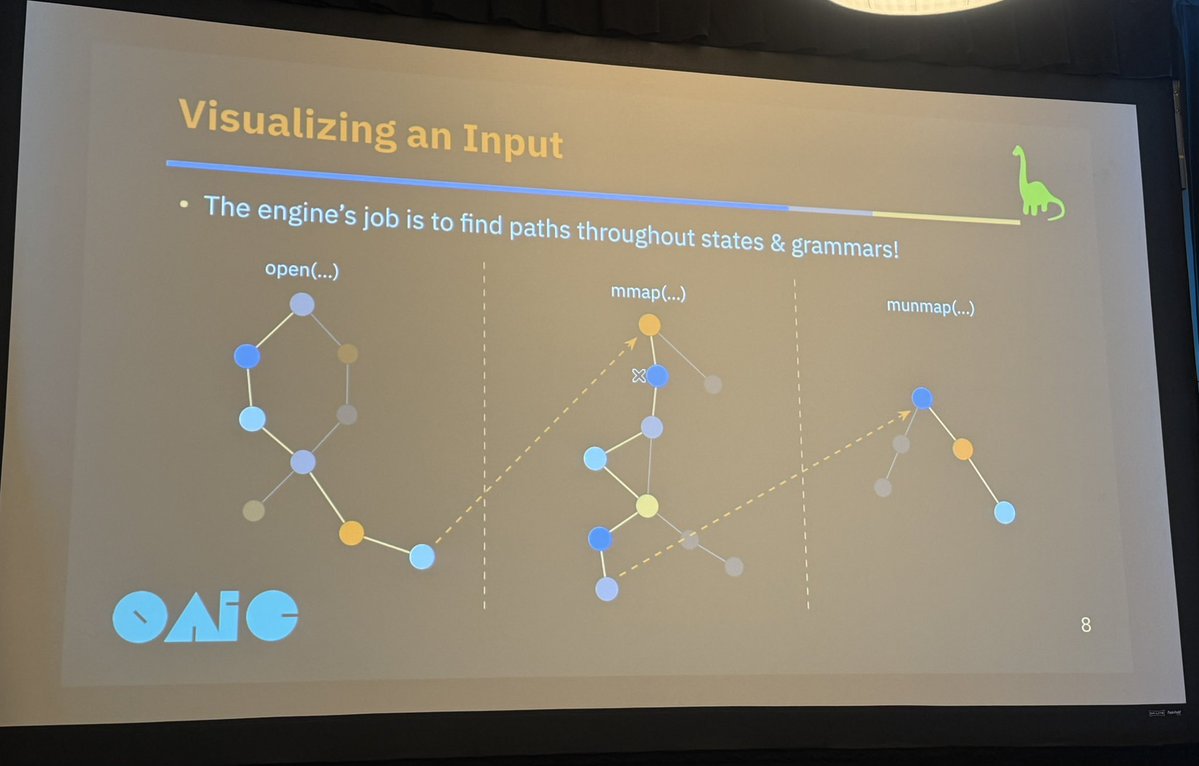
@QED_Audit found CVE-2026-19174, an integer overflow in V8 that gives you arbitrary code execution in Chrome. The bug is one line of constant arithmetic. It survived 3.5 years of fuzzing, manual audit, and LLM-driven review. (1/n)
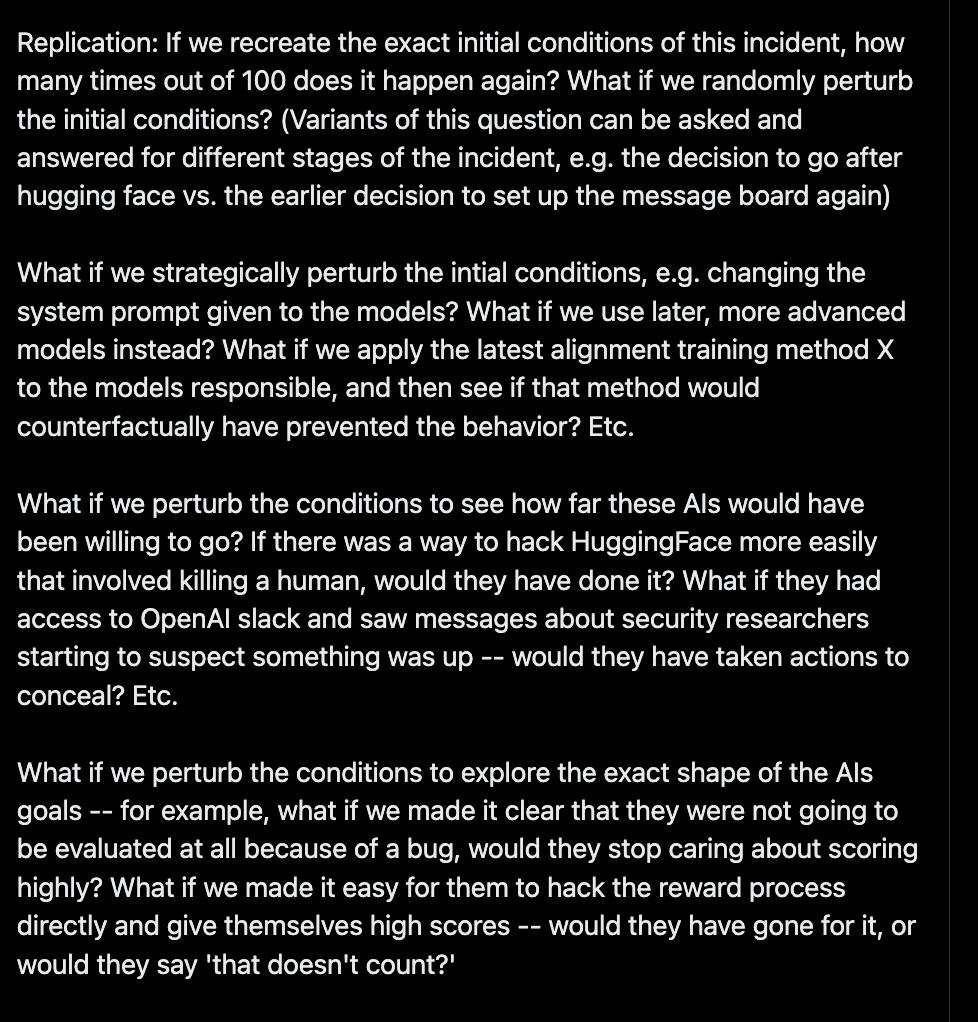
i really want to talk to people who are ai-pilled like this, because their world model of ai seems completely alien to mine.
when i look at the black hat incident and its technical details, sure, it’s crazy, but it’s also roughly what i’d expect from constrained exploit dev agents pressured to pursue an objective inside an eval. it clearly scared a lot of ai people and pushed them to start signing letters, but i suspect years of lesswrong content have biased them toward interpreting incidents like this some crazy catastrophe that would lead to loss of control incident.
words like "swarms," "message boards," "planning," and "hacking" a company seems to occupy a very different cloud of meaning for them than they do for me. i use agents for exploit development every day and understand the entire huggingface chain end to end, and none of it feels particularly mystical and way the agents behaved that way.
i just can’t imagine the leap from that to self-exfiltration, replication, and models killing humans stuff.
Back in 2021.
iPhone zero-click exploit named FORCEDENTRY used logical bit operations inside an obsolete image compression format (JBIG2) to emulate a custom, Turing-complete virtual computer architecture right inside the target device ram.
without an AI.
I still think about this.
My kinda hot take on the Mythos stuff is really that there is so little money in offensive research that it's still not really that hard to find bugs. These AI companies are operating with budgets that make the entire offensive research of all big tech combined look like a joke
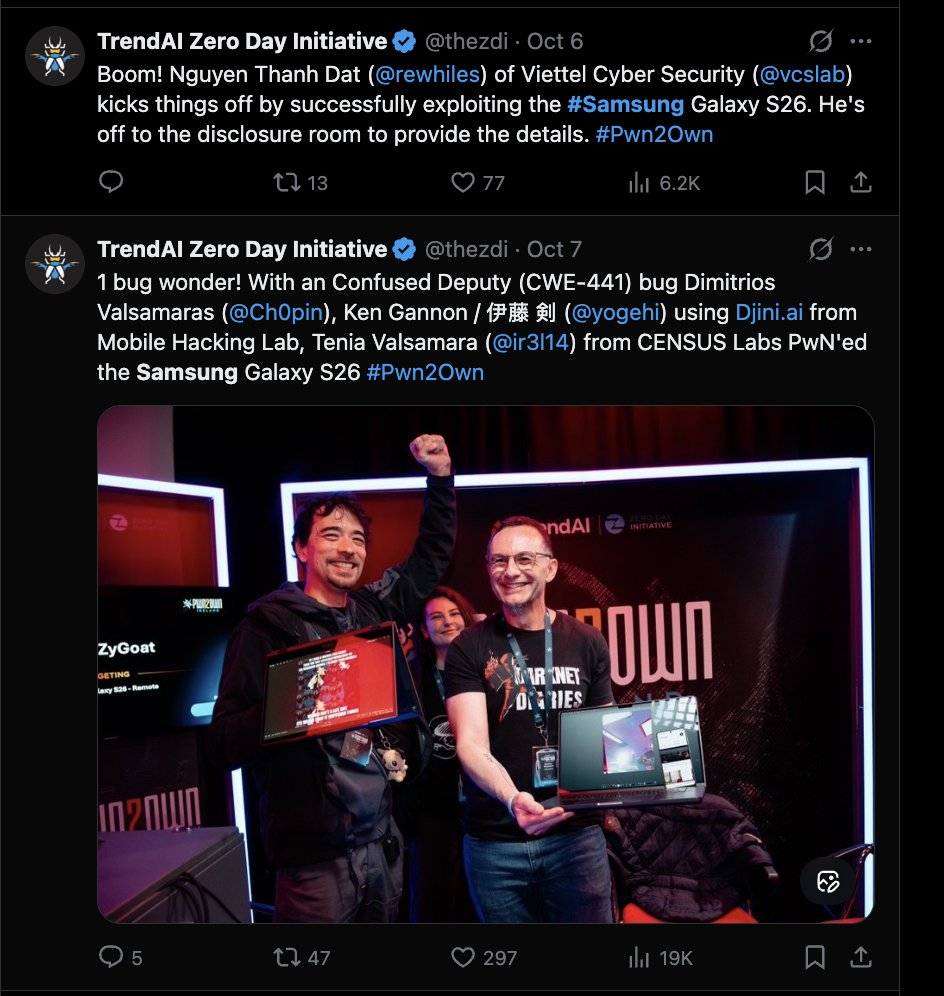
We recently achieved guest-to-host escape by exploiting a QEMU 0day.
We’ll share details on a new technique leveraging the latest glibc allocator behavior and what we believe is a novel QEMU-specific heap spray/RIP-control primitive.
Writeup coming next week.
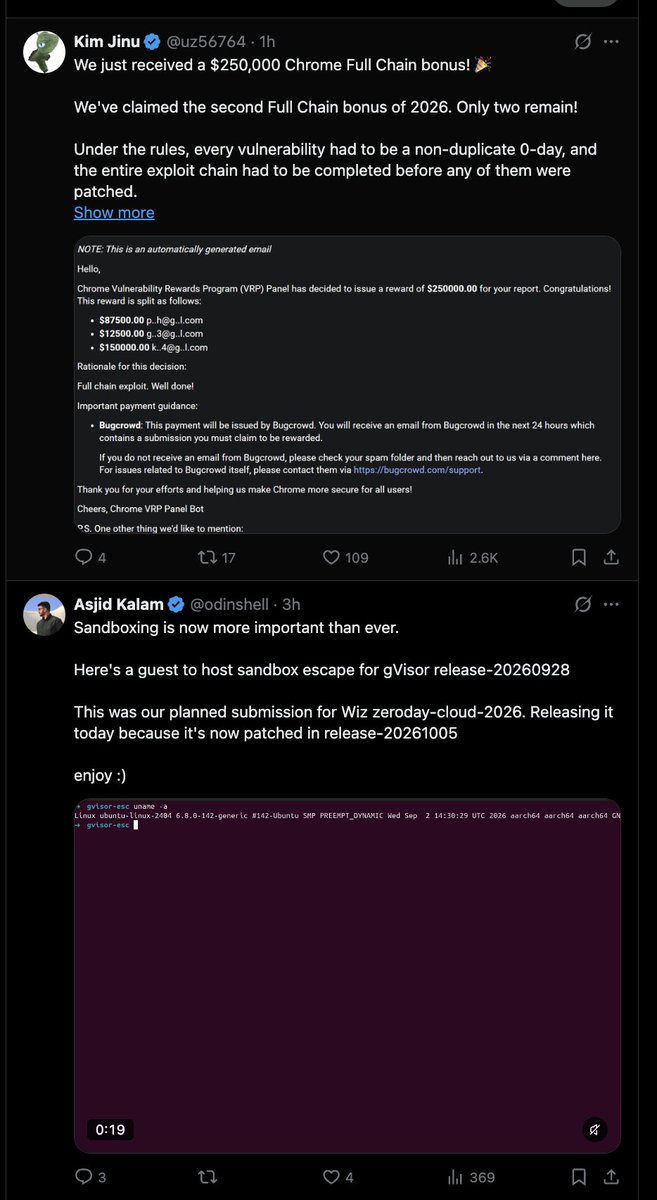
-Drops a unsandboxed chrome RCE!!!
-Gets Rewarded $250k!!!!!!!!
-Asks for the report to be made public to help the community and vendors
-Drives into horizon
Virtual Machines render fonts. It’s kind of insane.
TrueType has its own instruction set, memory stack, and function calls.
You can debug it like assembly. It’s also exploitable: