Cyber is having a moment
Across 21 major software companies, including Apple, AWS, Microsoft, and Google:
- Reported critical vulnerabilities never cleared 100 per month in four years
- Since spring they've jumped to over 600 per month
Charts of the Week: https://t.co/4dgNGwG5Nx
cc @github@GitHubSecurity this mass issue creation campaign looks to be actively ongoing as of a few minutes ago. flood of new bot accounts. site leads to copy-paste CAPTCHA scam, looks like a mix of the original lummastealer lure and my poc (so, uh, sorry)
LinkedIn is now using everyone's content to train their AI tool -- they just auto opted everyone in.
I recommend opting out now (AND that orgs put an end to auto opt-in, it's not cool)
Opt out steps: Settings and Privacy > Data Privacy > Data for Generative AI Improvement (OFF)
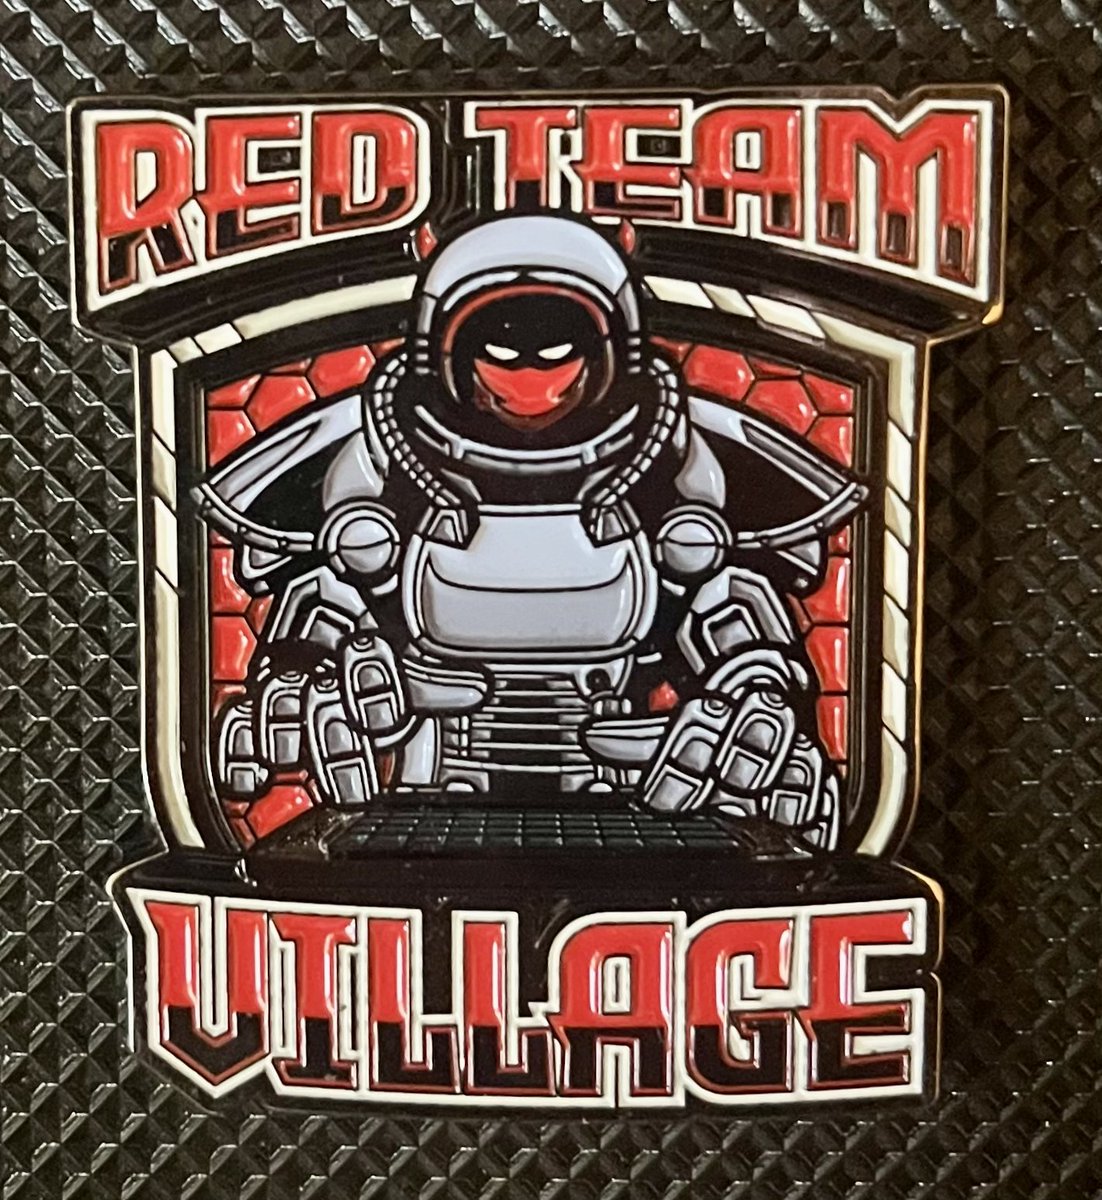
We're excited to show off our limited edition RTV coin for #DEFCON 31. Want to get your hands on one? Let's have a contest to name this year's mascot. Like, rt, and comment with your submission, we'll pick a winner next week. #RTV@defcon#dystopian#fallout#powerarmor
@UK_Daniel_Card I like what you are doing with this and think it is a pretty good initial list.
For what it's worth, I would add WAF and DDoS protection as capabilities.
Probably more important--a centralized inventory of assets. (It's hard to protect what you don't know you have.)
I was on a conf call and someone mentioned having to share password for some process. Someone else joked don't let Security (me) hear that. It was lighthearted, but I emphasized sharing passwords is a system design problem, we can't just say don't do it and not fix the root cause
@manicode 100% agree. The CIS already ranks "inventory" as #1 requirement for years. Knowing which systems are vulnerable/exposed should be at least in the top 3 in my opinion.
I still think that filtering known attacks should come first but I am open to debate :).