Honest question for AI builders
Do you think most AI automation demos clearly show their limitations or do they hide the messy edge cases and manual fallback steps?
Safety evaluations are critical for understanding whether a model is ready to deploy, which safeguards to build for it, and where to focus training and research.
On our Engineering Blog, we offer 10 recommendations for how to design, run and report them.
https://t.co/MtSQmqqi2D
There is a war going on right now
Local AI is under attack and dark forces are doing everything in their power to stop it
The most important thing you can do right now is buy a massive hard drive and download all the models you can
It’s the only way to remain sovereign
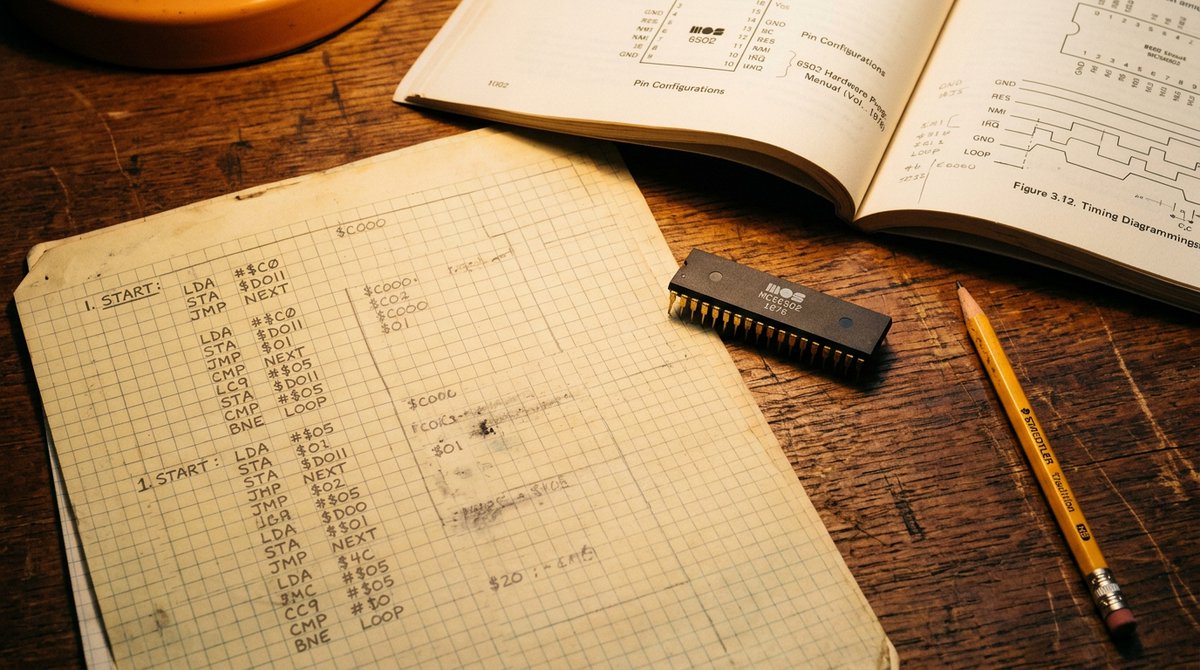
Before soldering the original Apple 1, Woz wrote an entire BASIC interpreter by hand on graph paper.
Without an assembler or debugger, he verified each opcode with a pencil and a mental execution loop.
The true frontier was conquered with patience and paper.
@poteto Senior engineers will allocate less focus to reviewing syntax line by line and way more attention to defining invariant boundaries. When generation is cheap, the verification harness determines what ships.
@arvidkahl Operating these setups resembles product management and triage. Success comes down to crisp acceptance criteria and automated guardrails. Which part of the transition surprised you most?
@SKatalystAI Denying .env reads is solid hygiene. I also run agents in disposable git worktrees so uncommitted edits never get wiped on a bad diff. Do you restrict outbound network calls from shell tools?
This might surprise many new to AI. The best agentic systems I have built and seen other top engineers build involve lots of boring deterministic steps.
You can't just throw more LLM agents at every problem and expect reliability to improve. Every error will compound into more errors.
You still need good classifiers, verifiers, and evaluators for agentic workflows to truly compound in the right direction. This is key to your "software factory."