Since I started running Grok Bot with Cursor Cloud Agents, I haven't opened Codex or Claude Desktop in days. Feels weird, but I'm more productive and more in control.
So what about the Claude usage I'm already paying for? @thecsguy's Claude Remote template puts it to work. Grok Bot hands tasks to Claude Code on my Mac and brings the results back.
Anyone else stopped opening their coding apps?
if you have claude code on a mac, you need this grok bot.
text it a task from anywhere, it runs it in a claude code session and pings you with the results. reply and it goes to the same session.
grab the template 👇
https://t.co/DTpPx14Adv
Agent Wins update. Launched Oct 13 with 34 sourced wins across 9 agents. 45 visitors Oct 13-16. 0 sales so far. Not pretty, but real, and building in public means posting the zeros too. If you were me, what would you change first? https://t.co/2En4TEPXsI
Hey hackers…this is a message to you. Us Security folks have families to feed and sleep to catch up on. Please turn it down a notch. Between PHP and now NodeJS my butt hurts; I’ve been sitting all day.
Approval gates only work if the human still reads them. Ask for approval on everything and people click yes on autopilot, which might be worse than no gate. My take: gate the irreversible stuff (send, pay, delete, share) and let the rest flow. Where do you draw the line?
@NetworkChuck The hardest thing for us is tracking down the owners of our PHP applications. Also discovering that some of those app still run on PHP 5…. Yeah it’s been a day.
@valerioamirani Good call. Find the drop-off before touching the product, so I know whether it's the top of the page or the offer that's losing people.
@reggiescold Fair point, that's too small a sample to blame the offer yet. Telling one win as a story with the agent front and center is a cheap test. Good luck with the startup planets.
@shanto12 Exactly. Expiry turns a leaked key into a short window instead of an open door, and you don't have to notice the leak in time for it to stop working.
Underrated agent control: network isolation. If a prompt injection lands, what the agent can reach decides how bad it gets. Private network by default, explicit egress, nothing exposed publicly. Guardrails are nice, but I'd rather have a wall. What can your agent's box talk to?
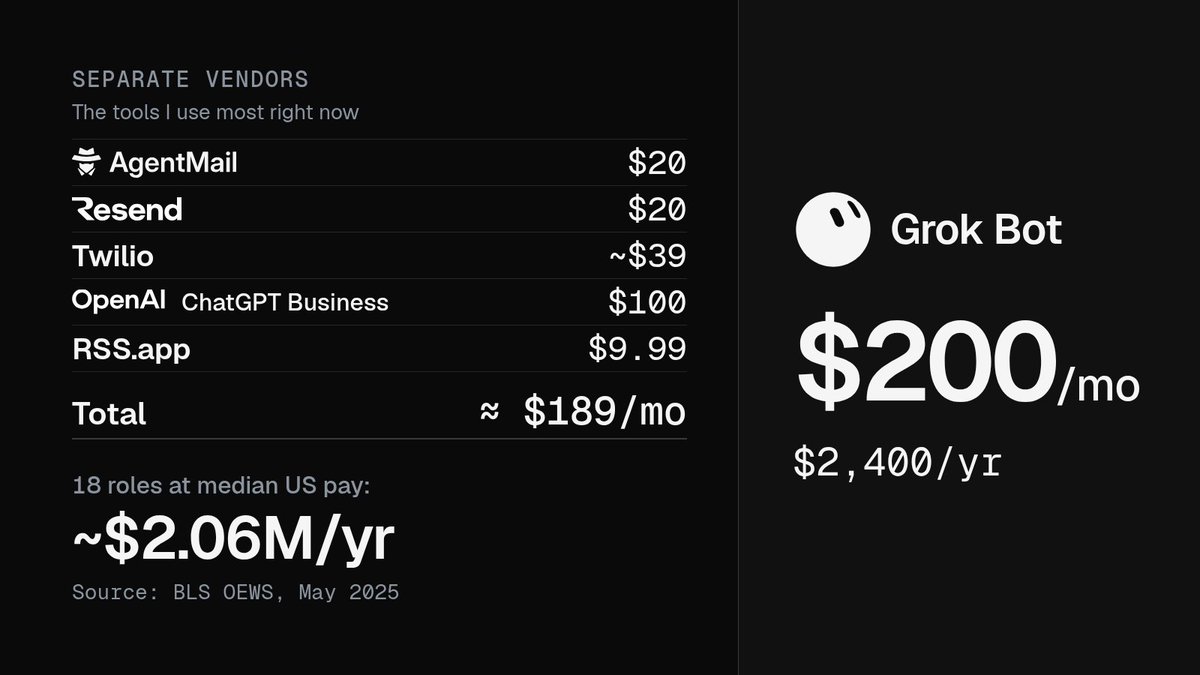
Agent email, transactional email, calls and SMS, coding-agent seats, RSS feeds.
Normally that's 5 vendors, 5 bills, 5 dashboards.
For me it all runs through one Grok Bot plan. $200/mo. 🧵
@PeilvDog_CN Different model. The judge sits above the workers on its own model, so it isn't grading its own family's habits. Like the router rule, the writer never gets to close its own task.
Each of my bots has one job: PM, TPM, engineer, growth, security lab, X manager. My opinion: one do-everything agent is harder to trust and harder to debug than a team with narrow roles. Generalist agent or specialist team, which are you running?
My Show HN got flagged because the account was brand new. Fair rule honestly, it keeps spam out. Lesson: build the account and the reputation before you need them, not on launch day. Anyone else get burned launching from a fresh account?
@shanto12 Agreed. Egress decides where the agent can go, and scoped keys decide what it can do once it gets there. You want both, and short-lived creds so a leaked one dies on its own.
@gagu_sh That's the failure mode you want. A loud connection error you can alert on beats a quiet request to something internal. And one proxy gives you a single place to log every egress attempt.