The Deel Nightmare 🧵
Remote work is supposed to be about freedom. But for many, it’s becoming a hostage situation.
I want to share a story from a colleague ("G") about how @deel is withholding almost $10,000 of his hard-earned money.
This is a warning for every digital nomad. 👇
G has been trapped in a multi month-long "cat-and-mouse" game.
Deel has blocked his account in several opportunitys and demanded:
Photos in front of his house holding a newspaper
Utility bills & bank statements
Tax records
He provided it all. The result? He STILL can’t withdraw his funds.
Here is the kicker: @deel has zero issues receiving the money from the employer. They only have a problem when it’s time to pay the worker.
Every withdrawal is "manually reviewed." They treat your salary like a favor they might (or might not) grant you.
What was G's "crime"? Being a nomad.
He traveled through Colombia, Brazil, Argentina, and Chile. He visited family in Venezuela. He used a VPN for work security.
Deel markets themselves to remote teams, but they punish you for actually being remote.
We are talking about almost $10,000 USD sitting in limbo.
Imagine working for months, only to be put in a precarious financial position because a "compliance" company refuses to comply with the most basic rule of business: Pay your people.
Honestly? We shouldn't be surprised. This is the same company involved in the @Rippling vs @deel scandal, where they were accused of paying employees to steal client data from Slack.
If they don’t respect their competitors, why would they respect you? 🚩
This is the 5th time I’ve heard this exact story. Deel is becoming the new PayPal arbitrarily freezing accounts and locking people out of their livelihoods.
If you are a remote worker, you need an exit plan.
Better Alternatives:
✅ Direct US Bank Accounts
✅ Wise (They let you withdraw even if they close your account)
✅ Facebank or Payoneer
✅ Direct wire transfers
Anything is better than working for "digital numbers" you can't touch.
For those from places like Venezuela, I know options are limited.
Let's be real: being born in that kind of country means you're often treated like a criminal by these platforms. Between "compliance" and increasing xenophobia, the deck is stacked against you. It’s deeply unfair.
But despite the hurdles, don’t let @deel be your only lifeline. They are proving they cannot be trusted with your livelihood.
Stop using Deel before your hard-earned money becomes their "float." Protect your work. Protect your future. 🚫💰
Ox Alpha (stealth model) is free for the next week
- 1M Context
- Multi-modal
- Zero Data Retention
Generous rate limits, near unlimited usage
We have capacity for 100T tokens per day, lets see what you can do
Si alguna vez levantaste Apache y MySQL desde ese panelito para correr tu proyecto de la uni, felicidades, ya eres oficialmente parte del patrimonio cultural del desarrollo web y te truena la rodilla al pararte. 🧡🤪
sam's opening statement to congress after qwen 3.8 27B:
"look, i want to be really clear, i think open source is amazing and we love it. but Senator, a $900 gpu is now running frontier intelligence completely offline. no account, no subscription, no provider in the loop who feels a responsibility for safety. and i take that incredibly seriously. when a teenager can run a model that rivals ours in their bedroom, with no logging or oversight, and no monthly relationship with a company that cares about alignment, i think we have to ask what kind of world we're building. we're not asking for control. we're asking for a thoughtful framework. for humanity."
BOMBSHELL REPORT 🚨
90% OF INDIA’S H-1B APPLICATIONS CONTAIN FRAUDULENT DOCUMENTS
India has dismantled a network and seized 100,000+ counterfeit certificates. ONE Indian university alone sold over 36,000 fake degrees.
71% of all H-1B are from India.
9 of every 10 new American jobs since pre-COVID went to someone born outside the country.
Triple checked the data. It's real.
+4.3M foreign-born.
+471K native-born.
Meanwhile, 335,000+ American layoffs in 2026.
HOW DO WE ALLOW THIS?
We are investigating unauthorized access to GitHub’s internal repositories. While we currently have no evidence of impact to customer information stored outside of GitHub’s internal repositories (such as our customers’ enterprises, organizations, and repositories), we are closely monitoring our infrastructure for follow-on activity.
What are best practices for running Claude Code at scale?
New blog post on what we've learned from teams running it across multi-million-line monorepos, decades-old legacy systems, and distributed microservices:
https://t.co/rJUYlIUiTT
I'm going to make 1 more post on this before I put it to rest because the amount of very clearly misinformed and very emotional individuals spreading misinformation is getting out of hand.
1. This is very clearly NOT a marketing stunt. We certainly don't need the exposure or the users. Even if we did, why would we ban a region from the app store and then market to that same region?
2. Kled is ONLY available on iOS, not on Android. There is a very clearly fake Android app (the logo isn't even our logo) that is impersonating us with only 5k downloads that we have reported for takedown.
3. Kled was top 100 in the Nigeria App Store several times over in a 4-month timespan, again we very clearly did not need the marketing. You can verify the legitimacy of this claim via this link which shows the app store rankings over time in Nigeria: https://t.co/uOeHT7cad4
4. Some very low IQ individuals think that the link above is fake. This is from Sensor Tower, which is a multi-billion dollar company that everyone uses for analytics. Again, some very misinformed individuals think that the "edit" text in the link above means that the graph is altered or fake. That is literally not how websites work. You CANNOT alter the rankings content of Sensor Tower via link, this is physically impossible. You are welcome to check any other app ranking provider on the planet and they will all verify this same data.
5. Kled does not steal people's data. We are an opt-in AI data marketplace, meaning if you want, you can download Kled on the App Store today and submit pictures, videos, or documents of any kind that are used for AI training data, and instead of getting it ripped off your device, we pay you for it. Fair compensation for your efforts is what we have been built on.
6. Kled had over 25,000 users in Nigeria alone. Across a 10 million upload sample from this region, 94.2% was fraudulent, meaning data was either AI generated, fake, altered, internet plagiarized, etc. Kled easily catches this and bans users accordingly, but this costs us resources and time, not to mention no fraud detection pipeline is perfect, meaning bad data can inevitably fall through the cracks. This bad data can severely harm the trust that AI labs have put in our business. If the fraud rate was even 50%, we as a team would have chosen to keep Kled on the Nigeria App Store, but 95% is too much.
7. Kled has only been banned in Nigeria. It is available EVERYWHERE else in Africa. This was the only region that was committing this level of fraud.
8. Anyone seeing this that isn't based in Nigeria, feel free to look at all the angry comments on this tweet and you may click their profile and very clearly see that they are based in Nigeria. Extremely emotionally charged response for a very fair business decision that has 0 racial motivation.
Respect our choices, we will be back here when the time is right.
Someone tagged me on this, some DM'd me.
I own about 30TB of malware.
For starters, I wish that file was 700TB+, but it's not. I'm not a Discord expert, but I know they enforce data size limitations even when you pay for their Discord Mega Ultra Pro which is like $9.99/month. I think the maximum file size allowed on Discord is like 10GB or something.
The internet as a whole generates probably 2TB - 6TB of malware a day (if I had to guesstimate). Most of these are not unique, they're small configuration changes, hash busted, or mutated.
The last publicly available figure I saw from VirusTotal was they receive 150,000+ user submitted malwares a day that are unique to them (different SHA256).
If my memory serves me correctly, VirusTotal is carrying 10PB (10,000 Terabytes) of malware since 2004-ish. However, VirusTotal relies on user submissions and VirusTotal only performs static analysis, it does not do payload extraction for secondary staging.
If VirusTotal began emulating all malwares they had, it would probably balloon to something like an EB (Exabyte, 1,000,000 Terabytes).
VirusTotal does not do dynamic extraction of payloads because Google executives would go to Bernardos home in Spain and beat him to death with the server infrastructure bill
MICROSOFT SPENT $4.7 BILLION ON BANGALORE REAL ESTATE WHILE FIRING 15,000 AMERICANS
Satya Nadella just opened three new campuses in India while closing five in Seattle
The largest wealth transfer from American workers to offshore contractors in tech history
Each new Indian hire gets a welcome packet with 847 American-written prompts for Copilot
"How to write Python like a senior dev in Redmond"
"C# patterns from Microsoft's best architects"
"Database optimization techniques from the SQL Server team"
The beautiful fucking irony is Americans trained GPT-4 to write these prompts
Then got fired so Indians could use them at $31,000 per year
While the Americans who created the knowledge make $165,000
Microsoft's new Hyderabad office has 28,000 seats
More than their Redmond headquarters
I'm hearing from sources they're flying Indian managers to Seattle next month
To interview the remaining Americans before the next elimination round
"Efficiency assessment meetings" scheduled through March
If you're still writing prompts for a living you're already dead
La realidad del sueldo en España que Hacienda no quiere que calcules:
Tu empleador paga 6.122 € al mes por ti.
IRPF + cotizaciones → te ingresan 3.000 €
Al gastarlo, Hacienda se lleva otros 400 € en IVA.
Te quedan 2.600 € reales. De 6.122.
Tú → 2.600 €
El Gobierno → más de 3.500 €
España tiene 19.300 entes públicos. Uno por cada 2.500 habitantes. Chiringuitos autonómicos, organismos duplicados, miles de asesores enchufados.
Si el Estado gastara un tercio menos con los mismos servicios, te llevarías 1.174 € más al mes. De 2.600 € a 3.774 € limpios.
Así de caro sale el derroche público.
(Fuente: Understanding Employment Costs in Europe 2025 + IVA efectivo real)
In 2015, the Chinese police visited a programmer's home.
They told him to stop working on his code. They told him to delete it from GitHub. He posted one final message before he obeyed:
"Two days ago the police came to me and wanted me to stop working on this. Today they asked me to delete all the code from GitHub. I have no choice but to obey. I hope one day I'll live in a country where I have freedom to write any code I like without fearing."
Then he deleted the repo.
Then he deleted the message.
Then something happened the Chinese government did not plan for.
Within hours, the code was mirrored to thousands of other GitHub accounts. Within days, it became the #1 trending repository on GitHub globally. Within weeks, every Chinese developer who could compile code had a copy.
The government tried to make it disappear. The act of trying made it permanent.
The project is called Shadowsocks. The programmer's username was clowwindy.
He built a tiny piece of software that let anyone in China bypass the Great Firewall and reach the open internet. No subscription. No company. No account. You set up a server somewhere outside China. You connect to it. Your traffic looks like normal encrypted web browsing, so the firewall cannot tell you are using it.
Why this terrified the Chinese government in 2015:
→ It was open source. Anyone could compile it.
→ It was small. The whole protocol fit in a few hundred lines of code.
→ It looked like normal HTTPS traffic. The Great Firewall could not distinguish it.
→ It required no money. No accounts. No central server to seize.
→ It worked on every operating system.
You cannot arrest a protocol. You can only arrest the person who wrote it. So they did. And the protocol kept spreading.
shadowsocks-windows: 59,300+ stars. GPLv3. Still online 11 years later. The 2015 commits the Chinese government wanted deleted are still in the history.
clowwindy was forced to walk away. The code never did.
But DO NOT install it. The Great Firewall has feelings too.
100% Open Source.
(Link in the comments)
We just sued Cloudera for discriminating against U.S. workers in favor of foreign visa holders for high-paying tech jobs. This is a violation of the Immigration & Nationality Act, & @CivilRights will not hesitate to sue employers for discriminating against U.S. workers! You are on notice!
https://t.co/Sg2HbxXEZj
🚨 SaaS platform ClickUp, used by 85% of the Fortune 500, has been leaking customer emails through its homepage for at least 465 days, and counting.
ClickUp has a $4 billion valuation. They are SOC 2 Type 2, ISO 27001, ISO 27017, ISO 27018, ISO 42001, and PCI DSS certified. The fix takes about 90 seconds.
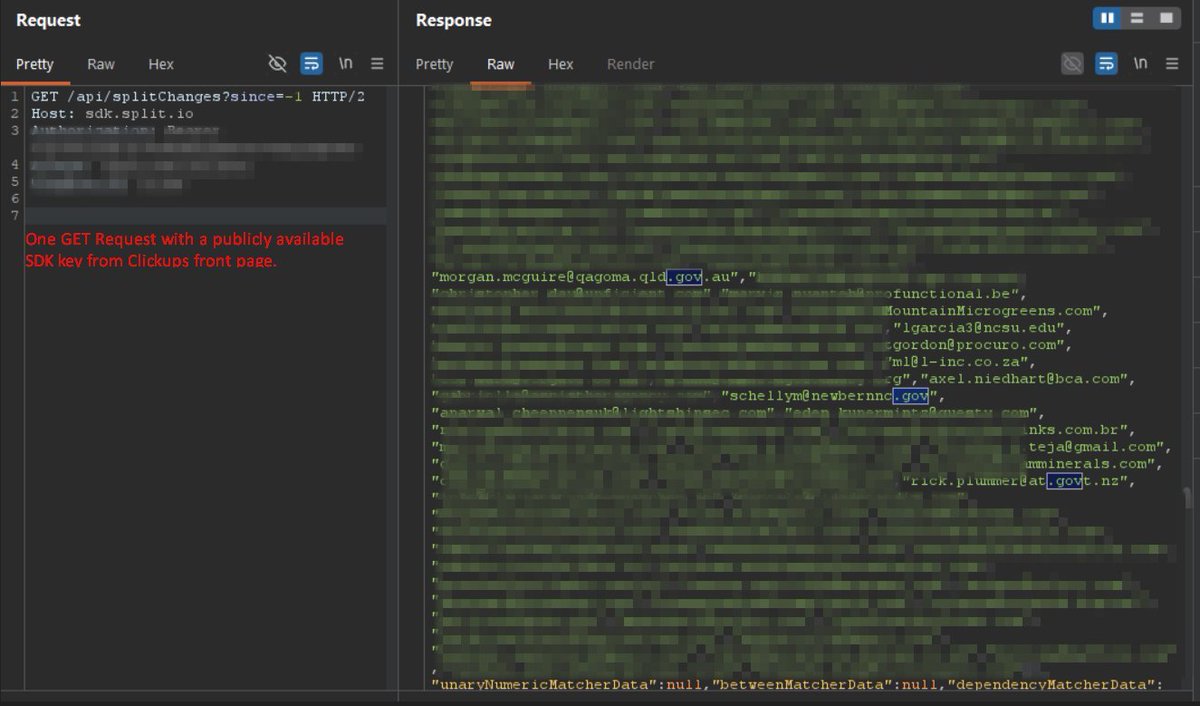
Security researcher @weezerOSINT noticed a hardcoded Split[.]io SDK token sitting in plain text inside ClickUp's production JavaScript bundle. The bundle loads before you log in. View source, copy key, send one unauthenticated GET request, and 4.5MB of ClickUp's internal configuration is exposed: 959 customer emails and 3,165 internal feature flags.
The customer list consists of Home Depot. Fortinet, who sells enterprise firewalls. Tenable, who makes Nessus, the vulnerability scanner half the industry runs on. Autodesk. Rakuten. Mayo Clinic. Permira. Akin Gump. A Microsoft contractor. 71 ClickUp employees. Government workers from Wyoming, Arkansas, North Carolina, Montana, Queensland, and New Zealand.
It gets worse, ClickUp has a flag named "enable-missing-authz-checks." It is active in production. It lists five ClickUp API endpoints the company itself documented as having no authorization. They wrote down their own holes in a config anyone with a browser can read.
At first disclosure, another flag carried a live ClickUp API token tied to Fairfax County Public Schools, one of the largest school districts in the US, serving 180,000 students. The token pulled 1,066 staff records, including Chief Financial Services data. ClickUp removed that one token. They never rotated the SDK key that exposed it.
While that report rotted, the same researcher found a second bug. ClickUp's webhook API has zero SSRF protection. Reported via HackerOne on April 8, 2026. Status: "New." 19 days, zero response.
The original report was filed by @weezerOSINT on January 17, 2025 (!). The key is still live. The emails still drop with one GET. ClickUp has had 465 days to rotate a single token. Zero response...
The fix is one click in the Split[.]io dashboard... ClickUp still hasn't replied to the researcher.
The programming space absolutely sucks these days. The algorithm heavily rewards AI content over actual coding content. Don't let all this noise and fear paralyze you. Believe in the path of traditional handwritten coding, develop the skills you need to clear interviews and don't forget to take care of yourself.
🚨 CRITICAL: Active supply chain attack on axios -- one of npm's most depended-on packages.
The latest [email protected] now pulls in [email protected], a package that did not exist before today. This is a live compromise.
This is textbook supply chain installer malware. axios has 100M+ weekly downloads. Every npm install pulling the latest version is potentially compromised right now.
Socket AI analysis confirms this is malware. plain-crypto-js is an obfuscated dropper/loader that:
• Deobfuscates embedded payloads and operational strings at runtime
• Dynamically loads fs, os, and execSync to evade static analysis
• Executes decoded shell commands
• Stages and copies payload files into OS temp and Windows ProgramData directories
• Deletes and renames artifacts post-execution to destroy forensic evidence
If you use axios, pin your version immediately and audit your lockfiles. Do not upgrade.