Grok Bot can now use your 1Password account.
Approve the logins you want to share, and your Bot signs in for you. This new integration is rolling out to users over the next few days.
My agent scored 0.0000 on trajectory accuracy on its first eval run.
Why? agents-cli eval silently drops empty-content events, erasing every intermediate node in my Go ADK workflow.
A tiny setNodeTrace helper took it 0.0 → 1.0.
Part 5 👇
https://t.co/bQw2VPCUMP
#AIAgents #Gemini4Argon #GDE
Today we announce 1Password for Agents platform, building with companies @Muse, SpaceX Super Intelligence Grok @Bot, @AnthropicAI’s @Claudeai, @OpenAI, @TownAI, @Browserbase, @Browser_use, @heydana_ai, Instinct, @usekernel, @Perplexity_ai, @tryramp, @Tomo, and @wajo_ai, with more integrations on the way. 🎉
We've heard from so many of our customers who want to use these new personal AI agents to help them get more done, but want more control over what the agent can access with the same trust and ease of use they get when using 1Password directly.
1Password for Agents gives your agents access without giving up your passwords. When an agent reaches a sign-in form, it requests a credential from your vault. If you approve the request, 1Password directly auto-fills the credential in the destination site so the agent can’t see or take possession of the credentials.
The agent gets the task done, but it doesn’t get your passwords..
You stay in control. 1Password for Agents free and optional for personal and family accounts. Unless you opt-in to an agent connector, agents cannot touch your vault.
➡️Learn more: https://t.co/KxDcCum2iE
Google Reader might be dead, but RSS is alive and well.
Build your own RSS hub with Tailscale. Read what you want, from any browser, without exposing it to the open web.
Build a thing. Escape the algorithms.
More on the blog:
https://t.co/Y9BsQFbuy3
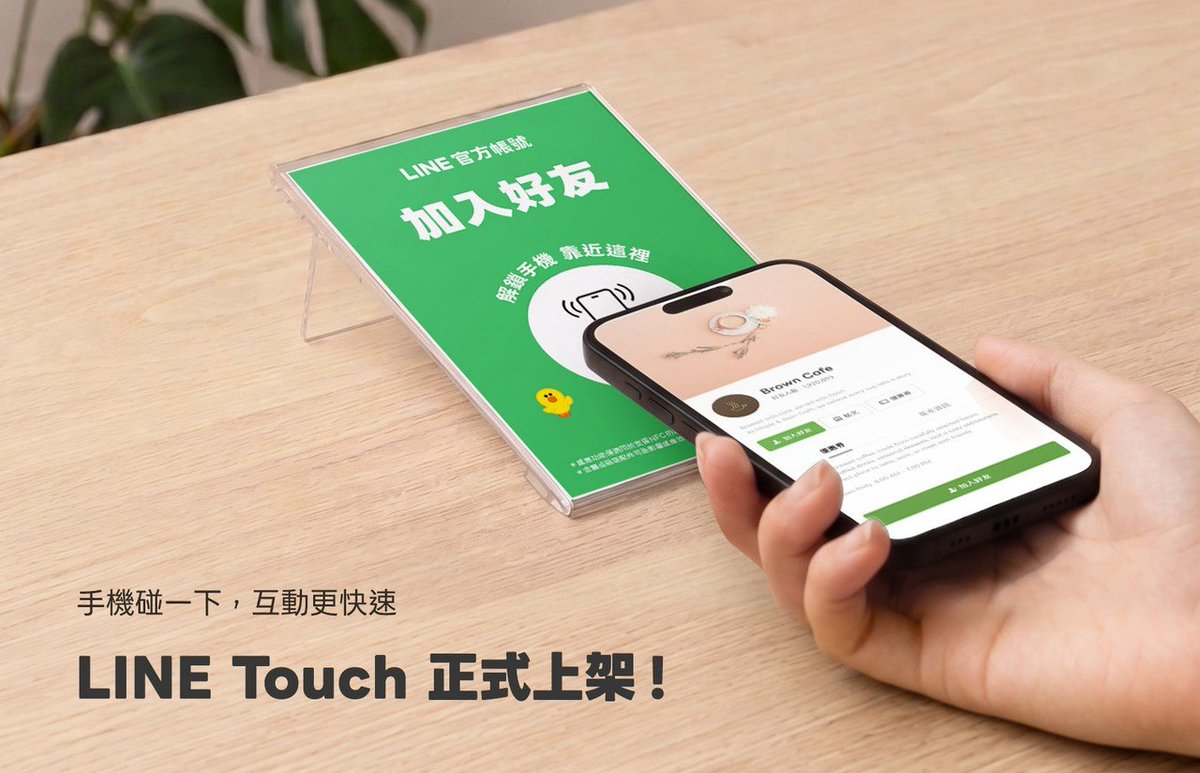
LINE Touch 10/21 正式上架,「碰一下」串聯 LINE 服務
打造 LINE 生態圈線下入口,協助企業串起線上線下服務體驗
LINE 台灣宣布,LINE Touch於今日正式上架,打造串聯實體場景與 LINE 數位服務的解決方案。消費者只要以支援 NFC 功能的手機輕觸設置於門市、櫃位或活動現場的 LINE Touch,即可快速開啟 LINE 官方帳號、優惠券、集點卡與 LINE MINI App 等指定服務,為 LINE 生態圈開啟全新線下入口。即日起,企業可透過 LINE 官方帳號管理後台購買並設定 LINE Touch,即可依不同場景彈性設定服務內容,讓每一次實體接觸都能進一步延伸為後續互動與服務機會,持續放大互動價值!
完整新聞資訊請參考官網:https://t.co/P5B2dBvCAt
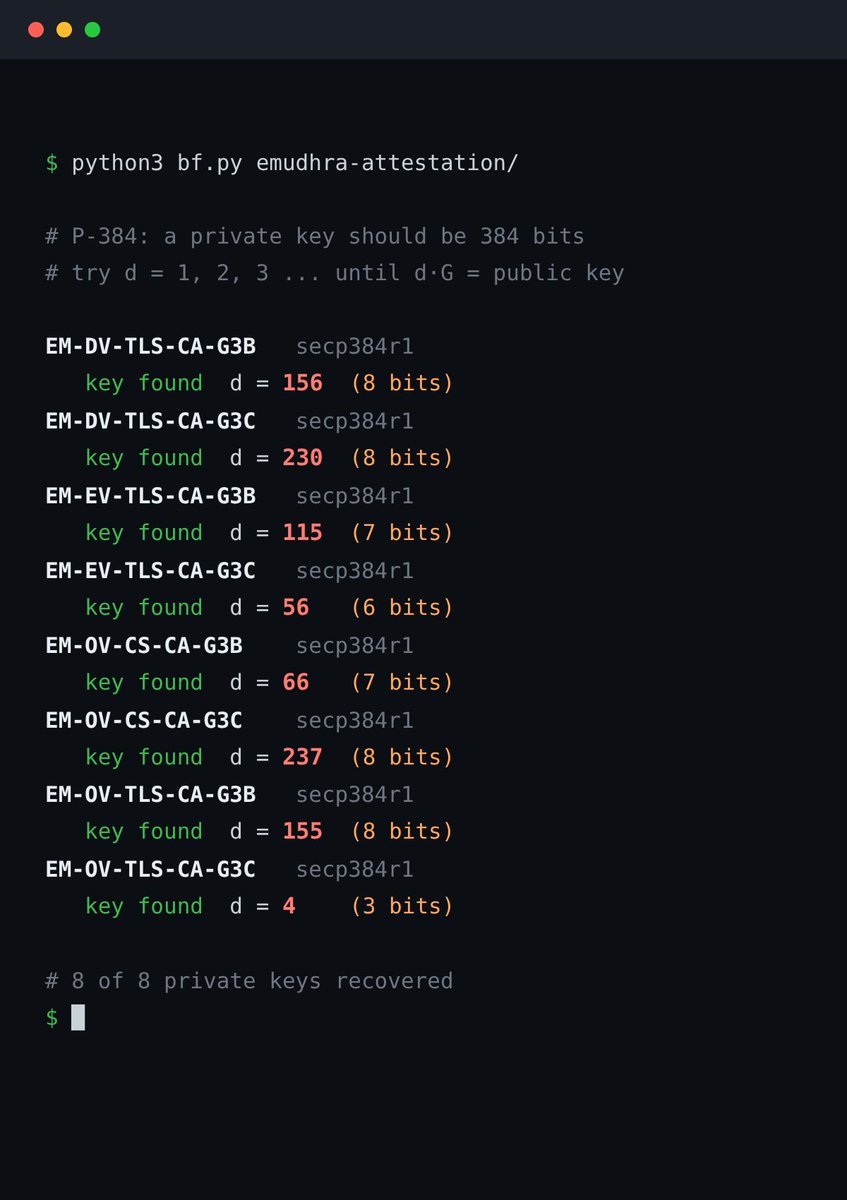
‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.
🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗 https://t.co/W4kfzx5lxz
#NodeJS#Security
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
Not just PHP. Node.js has also announced security releases for October 21, with HIGH-severity vulnerabilities affecting its 26.x, 24.x and 22.x release lines.
If you run either stack in production, keep an eye on official advisories and apply patches promptly.
Security maintenance doesn't stop at your application code. Your runtime matters too.
Node.js advisory: https://t.co/rmgw4sOnqU
Cloudflare has deployed default web application firewall (WAF) protections for newly disclosed PHP vulnerabilities before public disclosure. The rules use request and response signals to stop exploit attempts and prevent exposed data from reaching attackers. https://t.co/OQG4x6x858
⚠️ Vulnerability alert: php2shell
Unpatched sites running PHP 5.4 or later are at risk of remote code execution, data exposure, and crashes.
If your site’s web traffic is proxied through Cloudflare, we deployed protections before official public disclosure. Check the blog post to see which mitigations are enabled by default.
Even with these mitigations in place, update PHP as soon as possible to fix the underlying vulnerabilities.
https://t.co/3xLjlkUX8u
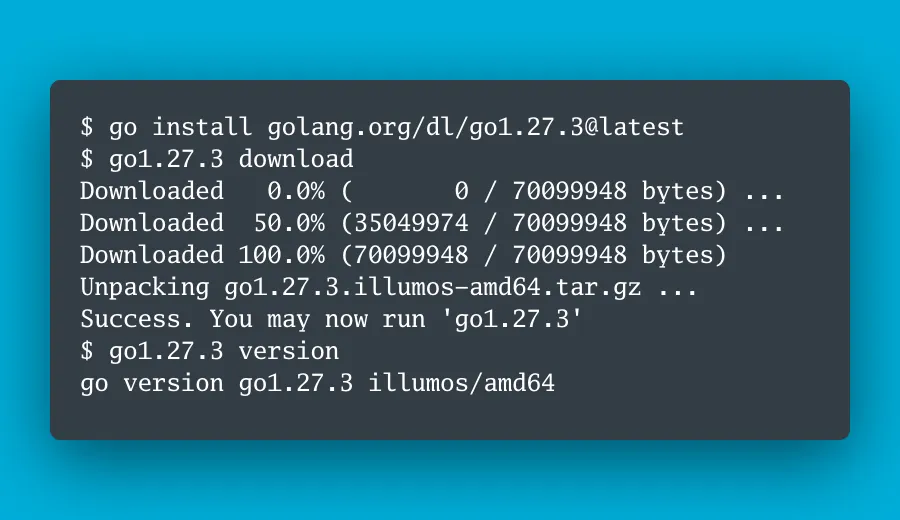
👩🏽🔬 Go 1.27.3 and 1.26.10 are released!
🔐 Security: Includes 1 security fixes to the standard library.
🗣 Announcement: https://t.co/x2K0jZa75h
📦 Download: https://t.co/W6zj0EZicx
#golang
I have been on the wrong side of agent demos that fall apart the second they hit production because we crammed everything into a single prompt. Evan Lin breaks down how to use Google ADK 2.0 graph workflows in Go to separate control logic from model reasoning cleanly.
The real value here is the implementation of fan-out parallel retrieval and human-in-the-loop state pauses that actually survive user edits without building fragile database state machines. I am sharing this with my team today.
#GoLang #SoftwareEngineering
🔗 Link: https://t.co/dcaXQasCPP