🌱 Help grow an independent corner of Flare.
Yggdrassil is an independent FTSO data provider, connecting external data to the Flare network. Delegate WFLR vote power to support our infrastructure—your tokens stay in your wallet.
#Flare#FLR
🚨 THE GUESSING GAME IS OVER.
No more wondering when the next flare-networks:native reward epoch begins or ends.
🔮 Radskee lets you see the FUTURE.
📅 31-day epoch calendar
🌎 12-month future outlook
⏳ Live countdowns
⚡ Precise epoch schedules
Stop guessing. Start planning.
The future of Flare is already here.
💙🟣
🌐 https://t.co/uDnC8FbaQL
#Flare #FLR
Sensationalist clickbait artists only highlighted the threat and they didn't even do it well.
The real story here is the response from the team and infrastructure providers quickly coming together for a rapid response hard fork for a bug that was inherited from Avalanche, the New York Stock Exchanges newest partner.
The worst case scenario for the bug if any attempts were successful, none were, would be a denial of service for affected validator nodes.
In order for a full chain halt (correct me if I'm wrong) approximately 66% of all vote power would have to be affected.
Which never happened.
This was a preventative matter in a world where exploit attempts happen constantly.
If you watched the traffic on your home router you'd see hackers making constant attempts at trying to hack your Xbox but nobody blames Microsoft like it's 1999 and Y2K is the boogeyman.
Approximately T Minus 12 hours until deadline.
Great response out of the gate.
The most active members responded quickly and effectively as expected.
However a shocking number of providers have not bothered with updates that were pushed to mainnet in July.
Once the deadline passes there's a significant chance a number of those providers simply won't be contributing at that point and can expect a loss of passes and ineligibility for rewards.
@BurstLabs_io https://t.co/C2mnph9yht
For the visual
These numbers are important. While many providers may strive for the perfect 100% up time maintaining absolute 100% in the current cyber security environment means critical updates have likely not been applied.
Up time is important.
Security is importanter.
99.99% is a good thing.
https://t.co/sMkPsWo7wT
One less thing to worry about when building DeFi on Flare: price oracles.
FTSOv2 provides decentralized price feeds that update with every block (~1.8 seconds), with no additional oracle fee for onchain reads.
Available directly from your smart contracts.
Learn how to integrate them:
https://t.co/cdaBWXaaWi
What if somebody expressing their personal opinion isn't an attack on your beliefs.
What if your government actually is retarded.
Spoiler alert, it is and it doesn't matter who's in power you still get fucked in the end.
Tons of people forgot the entire point of crypto.
🚨 IF YOU ARE IN CRYPTO, IGNORE THIS POST AT YOUR OWN RISK
A friend lost $535,000 USDT yesterday, and he even sent a test transfer first. His wallet wasn't hacked and his keys never leaked. He lost it to a bot.
The test transfer arrived fine. Within seconds, a bot sent 1 USDT to his wallet from a fake address that started and ended with the same characters as the real one. Now the fake address was sitting in his transaction history, right next to the real one.
When he went to send the full amount, he copied the address from that history and picked the fake one. The money was gone in under 30 seconds, swapped out of USDT before Tether could freeze it.
This is called address poisoning, and it's running at industrial scale. The bot that got him has run over 6 million transactions, and it goes after anyone moving large amounts.
Here's how to make sure it never happens to you:
• Never copy an address from your transaction history or a block explorer
• After a test transfer, copy the address again from the original message the receiver sent you
• Check every character, because these bots match both the start and the end
• Save verified addresses in your wallet's address book with names
Now open your wallet and go through your history. If there's a tiny deposit from an address you don't recognize, a bot has already marked you. Tell me below if you find one.
Repost this post and share this to the person you know who moves the most money on-chain.
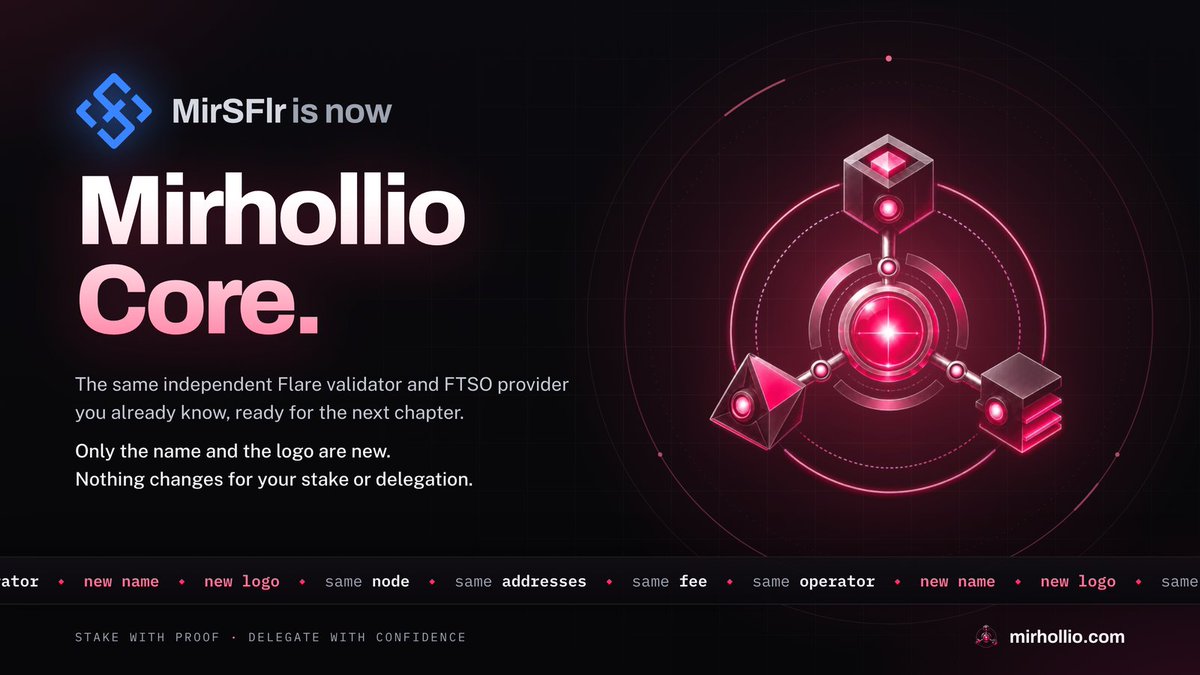
MirSFlr is now Mirhollio Core.
Same independent Flare validator and FTSO provider. Only the name and logo are new.
Same node, same addresses, same fee. Nothing changes for your stake or delegation.
Big thanks to all who staked or delegated.
https://t.co/ImHgo9q963
$FLR #FTSO
Mirhollio Core is #12 of 99 FTSO providers on Flare for primary accuracy.
69.7% of our price submissions landed in the primary reward band over the last 6 hours, twice the network median.
Check it yourself:
https://t.co/aVLkHl93eK
$FLR #FTSO
We are stuck in the same way. Not too long ago we had an open issue on git with Towo/Bifrost with them to get listed true with them. After 8 months of waiting we started asking questions. They simply deleted it.
The https://t.co/jVbGmlX6SP list is excellent. We made some changes to our listing with them but since the flare portal prioritizes Towo over them, our changes are not showing up.
@FlareNetworks@FlareDevHub@HugoPhilion@FTSOYggdrassil
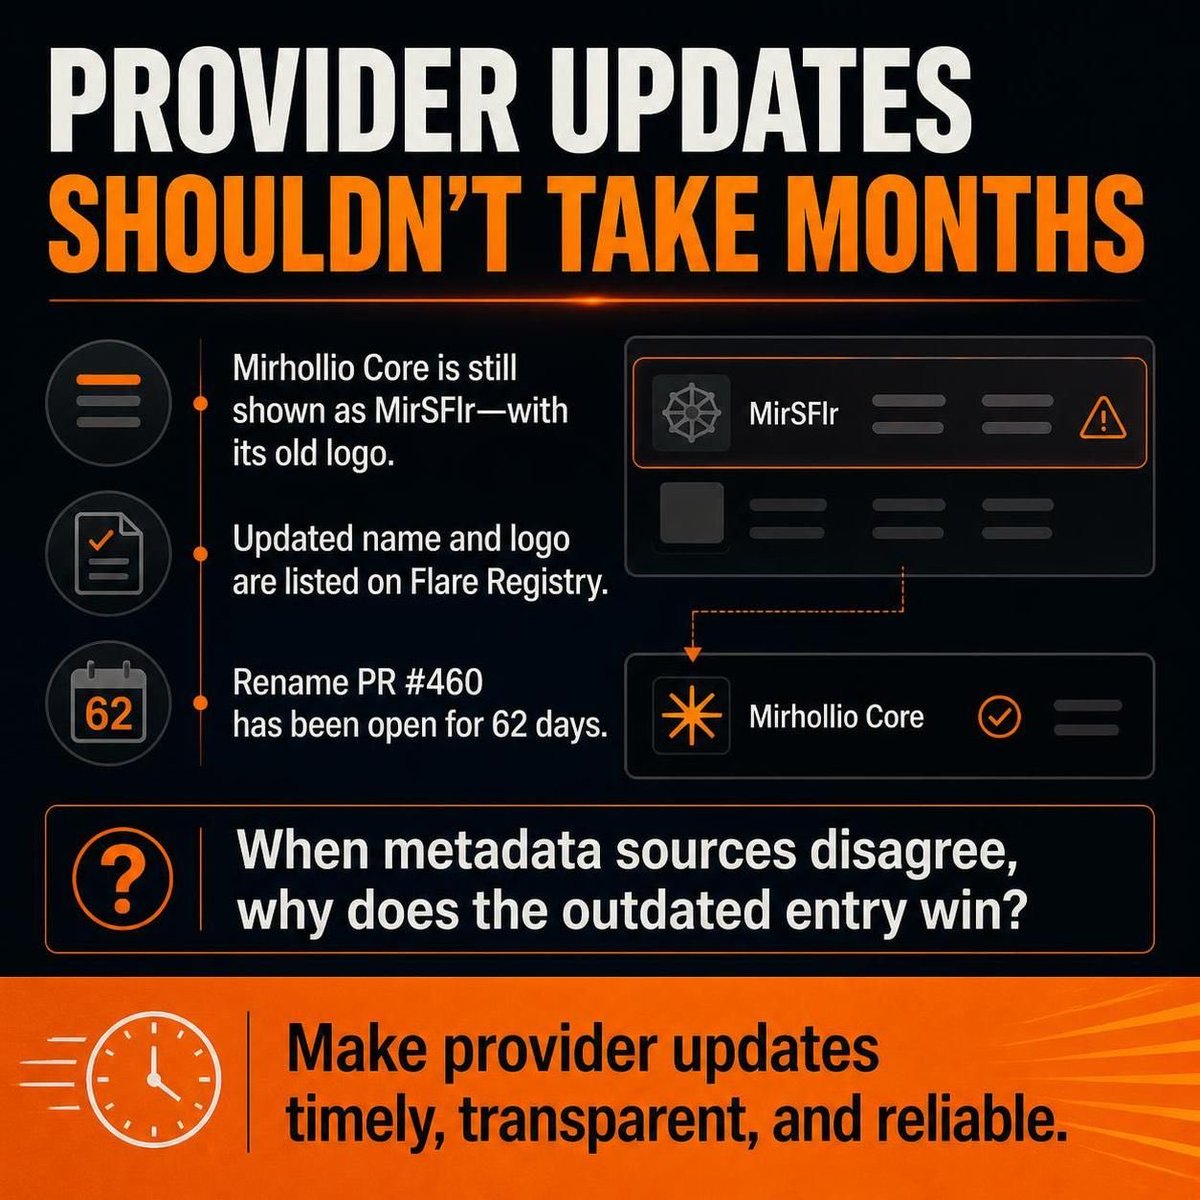
Provider PRs are left open for months while outdated metadata stays live. It’s ridiculous that this issue has to be raised publicly just to get action—there should be a clear, reliable way to resolve updates. @FlareNetworks@FlareDevHub@HugoPhilion#Flare#FTSO@Bifrostwallet
An actual alternative to @BifrostWallet and it is needed badly. Ask any new provider on Flare, the headache of getting listed on Bifrost is almost unbearable. Check out @Radskeeonflare and stake/delegate your #FLR!
Provider PRs are left open for months while outdated metadata stays live. It’s ridiculous that this issue has to be raised publicly just to get action—there should be a clear, reliable way to resolve updates. @FlareNetworks@FlareDevHub@HugoPhilion#Flare#FTSO@Bifrostwallet
Could be simplified even further.
Not just mobile TEEs but physical hardware keys that require biometric confirmation which in turn can be drawn out across FDC confirmation.
Allowlist for approved functions, "is this function allowed, yes no" "is this device registered, yes no"
At that point upstream tampering is irrelevant
Flare Reef now watches the public records where hacks, fake sites and network changes show up first.
On Nov 2, the @MetaMask warning list added 820 sites in one day. The newest @realScamSniffer list had 80 more, and 8 were named after Flare, XRP or a project on them.
Here is what the Reef records now. Every change is written on Flare, with a link back to the source.
Phase one (Oct 31): MetaMask's warning list and @DeFiHackLabs .
Phase two (Nov 2): Scam Sniffer's phishing list. From @XRPLF : the XRP Ledger validator list, rippled releases and xrpl.js releases. From Flare: go-flare node releases, the data-provider stack and every system contract deploy.
Coming next: the Solidity compiler's bug list. Not live yet.
We also follow a handful of people who are often first to report a hack: @zachxbt , @samczsun , @peckshield , @SlowMist_Team , @blocksec@Phalcon_xyz and @rekt News.
Check every source yourself: https://t.co/CaFSooIFbj
@Flare_Reef
1.5 BILLION WFLR delegated at just 0.525% APR. 👀
How much could that allocation be missing in rewards?
Staking at 9.1%: an extra 128.6 million flare-networks:native /year around $774,000.
Your choice of provider and strategy matters. Check the yield app, compare.