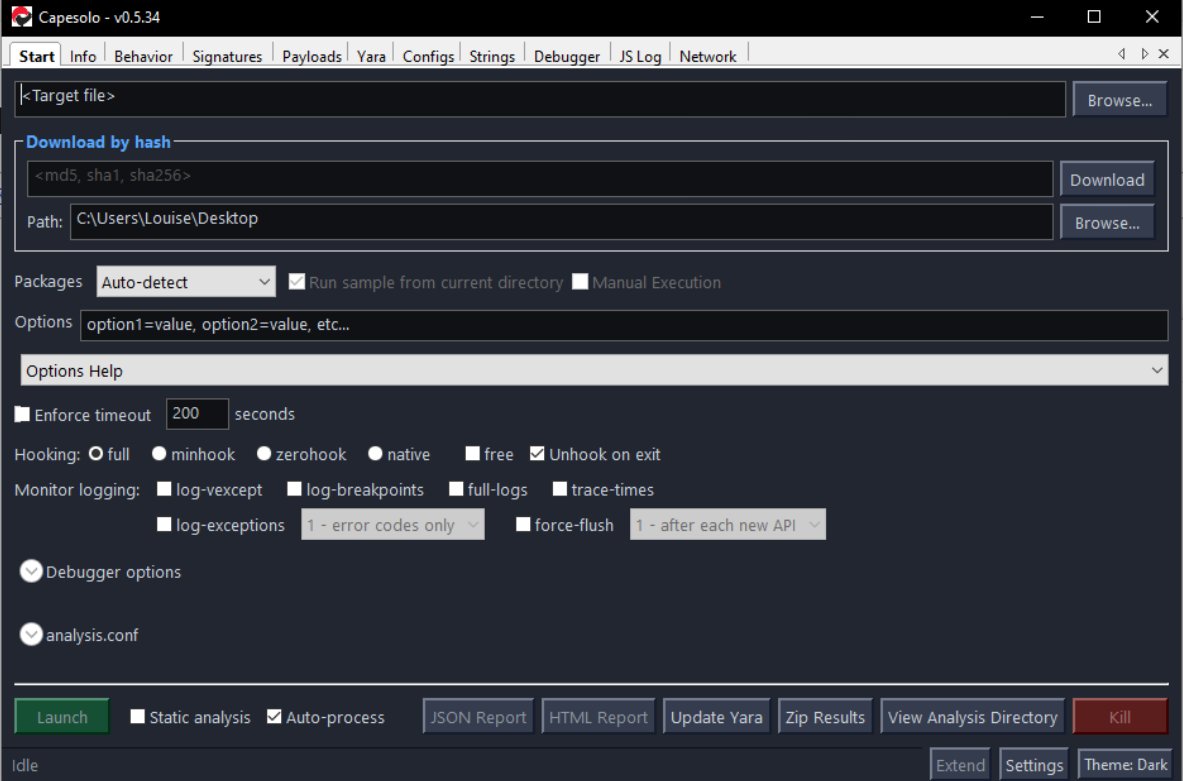
10 years ago today CAPE Sandbox was released...
Today we are proud to announce its desktop partner-project CAPEsolo: https://t.co/1voRdgbqOb 🎉
All the power of the sandbox in a desktop application 💪
pip install capesolo
👋 How do you find all the global admins in an M365 tenant?
You are going to want to bookmark this 💀
✍️ Answer
If you use the portal it's easy (just go to the Roles blade)
But if you need to use the API (take a deep breath 👇)
1️⃣ Check the license on the tenant
2️⃣ In an Entra ID Free or P1 tenant
→ /roleAssignments
3️⃣ In Entra ID Premium tenants
3️⃣•1️⃣ Get all PIM Eligible global admins
→ /roleEligibilityScheduleInstances
3️⃣•2️⃣ Get all PIM Permanently Active users and use assignmentType = Assigned to filter out 'Eligible' users that are currently activated.
→ /roleAssignmentScheduleInstances
4️⃣ If any of these are groups, then iterate through the group to get all members inside the group
We use this frequently in Maester for finding privileged users.
Full code at https://t.co/zwME9aPAl1
Or you can simply use this in your scripts 👇
🔥 Install-Module Maester -AllowPrerelease
🌟 Get-MtRoleMember -Role GlobalAdministrator
I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: https://t.co/jD6EaGtsn3
A lightweight tool that injects a custom assembly proxy into a target process to silently bypass ETW scanning by redirecting ETW calls to custom proxy https://t.co/sK15dRqCMD