🇨🇳 CHINESE PII DATABASE (~280M PEOPLE) ALLEGEDLY OFFERED FOR SALE
A threat actor is advertising what they claim is a large Chinese personal-information collection covering roughly 280 million distinct people (seller cites ~283 million rows / ~52GB zipped).
The underground listing alleges fields such as:
* Names
* 18-digit national ID numbers
* Phone numbers
* Addresses (on some subsets)
* Political-status and related attributes (claimed on some subsets)
* Separate e-commerce order subsets (name/phone/address/goods)
⚠️ Analyst Note:
Mass Chinese national-ID / phone corpora are repeatedly resold, merged, and rebranded across underground markets. Checksum claims, population-percentage math, subset overlap, freshness, and any link to a specific new breach are unverified from the listing alone. Political-status fields, if real, raise additional sensitivity but do not by themselves prove authenticity.
We assess this as an unverified threat-actor claim involving alleged Chinese national PII at very large scale, NOT confirmation of a new compromise of a specific Chinese government system.
If authentic and non-public, national ID + phone + address data could support large-scale fraud, SIM-swap social engineering, and targeted profiling.
#DDW #DarkWeb #China #PII #DataBreach #ThreatIntelligence #CyberSecurity
Hacker’s guide to satellite cybersecurity: Space Packet protocol, open-source tools, and 34+ vulnerabilities. 🛰️🌎🔭☠️👨🏻💻
More details on:
LinkedIn: https://t.co/ddmshGgUbv
Substack: https://t.co/PPAXFjdDUN
Telegram: https://t.co/UtoY7xhbct
❄️🚨 $39.27M USDT FROZEN ACROSS WALLETS LINKED TO XINBI GUARANTEE
The financial pressure on Xinbi Guarantee is escalating.
Blockchain intelligence platform MistTrack identified 39,273,713 USDT frozen across 10 TRON addresses linked to the Chinese-language Xinbi Guarantee marketplace.
The wallets were frozen on September 8 — one day before the U.S. government publicly announced a major coordinated enforcement action against Xinbi.
The numbers:
* 39,273,713 USDT frozen
* 10 TRON addresses affected
* One wallet held more than $10 million
* Addresses were linked through wallet labels, transaction activity and connections to Xinbi-associated infrastructure
The following day, the U.S. Department of Justice announced that more than $52 MILLION in cryptocurrency had been restrained across Xinbi and its network of vendors.
DOJ specifically thanked Tether for its "proactive assistance" in the investigation.
Meanwhile, the U.S. Treasury designated Xinbi Guarantee as a Transnational Criminal Organization.
Treasury says Xinbi has processed the equivalent of MORE THAN $24 BILLION in digital assets and fiat since approximately 2022.
🚨 XINBI OPERATORS REACT
Chinese-language reporting and commentary attributed to [at]fugui indicates the Xinbi team expressed regret over users whose USDT was frozen and acknowledged difficulties attempting to have large frozen balances released.
That commentary should be treated separately from the confirmed U.S. government enforcement action.
⚠️ Analyst Note:
This is becoming a textbook example of coordinated disruption of a crypto-enabled criminal ecosystem.
Wallet tracing
→ Stablecoin freezing
→ Federal seizure warrants
→ Telegram channel seizures
→ OFAC sanctions
→ Infrastructure disruption
Stablecoins have a property that criminals sometimes underestimate:
USDT may move on a decentralized blockchain, but Tether retains the technical ability to freeze tokens associated with specific addresses.
That makes blockchain attribution and wallet clustering operationally significant.
Once law enforcement and blockchain intelligence providers can reliably map an illicit ecosystem, the same transparent ledger used to move funds can become evidence for tracing, sanctions and asset restraint.
Important distinction:
MistTrack identified the specific 39.27M USDT freeze across 10 wallets.
DOJ separately confirms more than $52M in cryptocurrency was restrained across Xinbi and its vendor network and explicitly acknowledges Tether's assistance.
Official sources:
U.S. Department of Justice:
https://t.co/MORpdbhl0T
U.S. Treasury:
https://t.co/60MTzS7MNz
#DDW #Xinbi #Tether #USDT #CyberCrime
🚨 HIGH-VALUE TELEGRAM USERNAMES BANNED AFTER U.S. CRACKDOWN
The disruption of Xinbi Guarantee is now extending deep into its Telegram infrastructure.
Following coordinated action by the U.S. Department of Justice and Treasury against the Chinese-language illicit marketplace, Telegram has removed Xinbi's central channels and banned usernames associated with the operation.
Among the usernames now observed as BANNED on Telegram are:
* @aaaa
* @bbbb
* @zzzz
* @oooo
* @gqdh
Some of these are extremely scarce four-letter repeating Telegram usernames that had previously been acquired through the TON/Fragment ecosystem.
Fragment records for @aaaa and @bbbb now explicitly display:
"This username is banned on Telegram!"
The DOJ confirms that a U.S. federal court authorized the seizure of Telegram channels hosting the Xinbi marketplace.
This forms part of a much larger disruption operation against Xinbi.
U.S. authorities also:
* Seized two Xinbi cryptocurrency wallets containing approximately $12 million
* Sought restraint of 47 additional wallets
* Restrained more than $52 million in cryptocurrency from Xinbi and its vendor network
* Seized infrastructure used by the marketplace
* OFAC designated Xinbi Guarantee as a Transnational Criminal Organization
Xinbi was not a conventional cybercrime forum.
According to U.S. authorities, it functioned as a massive criminal services marketplace connecting scam centers with vendors providing money laundering, fraudulent investment infrastructure, cryptocurrency services and other capabilities supporting cyber-enabled fraud.
⚠️ Analyst Note:
The interesting part here is that enforcement is no longer limited to arresting operators or seizing cryptocurrency.
The disruption is reaching the infrastructure and digital assets that allow these criminal ecosystems to function:
Crypto wallets
→ Telegram marketplaces
→ Channels and groups
→ Usernames
→ Financial infrastructure
Even scarce Telegram usernames with substantial secondary-market value can effectively become unusable when the platform bans them.
Important distinction: the DOJ confirms the court-authorized seizure of Xinbi Telegram channels, but it has not publicly identified each of the individual usernames above in its announcement.
Official source — U.S. Department of Justice:
https://t.co/MORpdbhl0T
#DDW #Xinbi #Telegram #CyberCrime #Crypto
🚨🇨🇳 China Housing Provident Fund dataset containing 280M records allegedly offered on a cybercrime forum
⠀
China’s Housing Provident Fund is a mandatory housing savings system funded through employee and employer contributions, used to support housing purchases and related expenses.
⠀
A cybercrime forum actor using the handle feijo claims to be selling a dataset associated with the system containing approximately 280 million records.
⠀
Claimed exposed data includes:
⠀
• Names and identification numbers
• Gender and dates of birth
• Ages and mobile numbers
• Registration provinces
• Fund provinces and cities
• Employer information
• Account status
• Contribution bases
• Employee and employer contribution amounts
• Contribution ratios
• Monthly contribution totals
• Account balances
• Account opening dates
• Latest contribution dates
⠀
The actor is asking $450 for the purported dataset and published sample records as proof of the claim.
⠀
The source, record count, and authenticity of the dataset have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
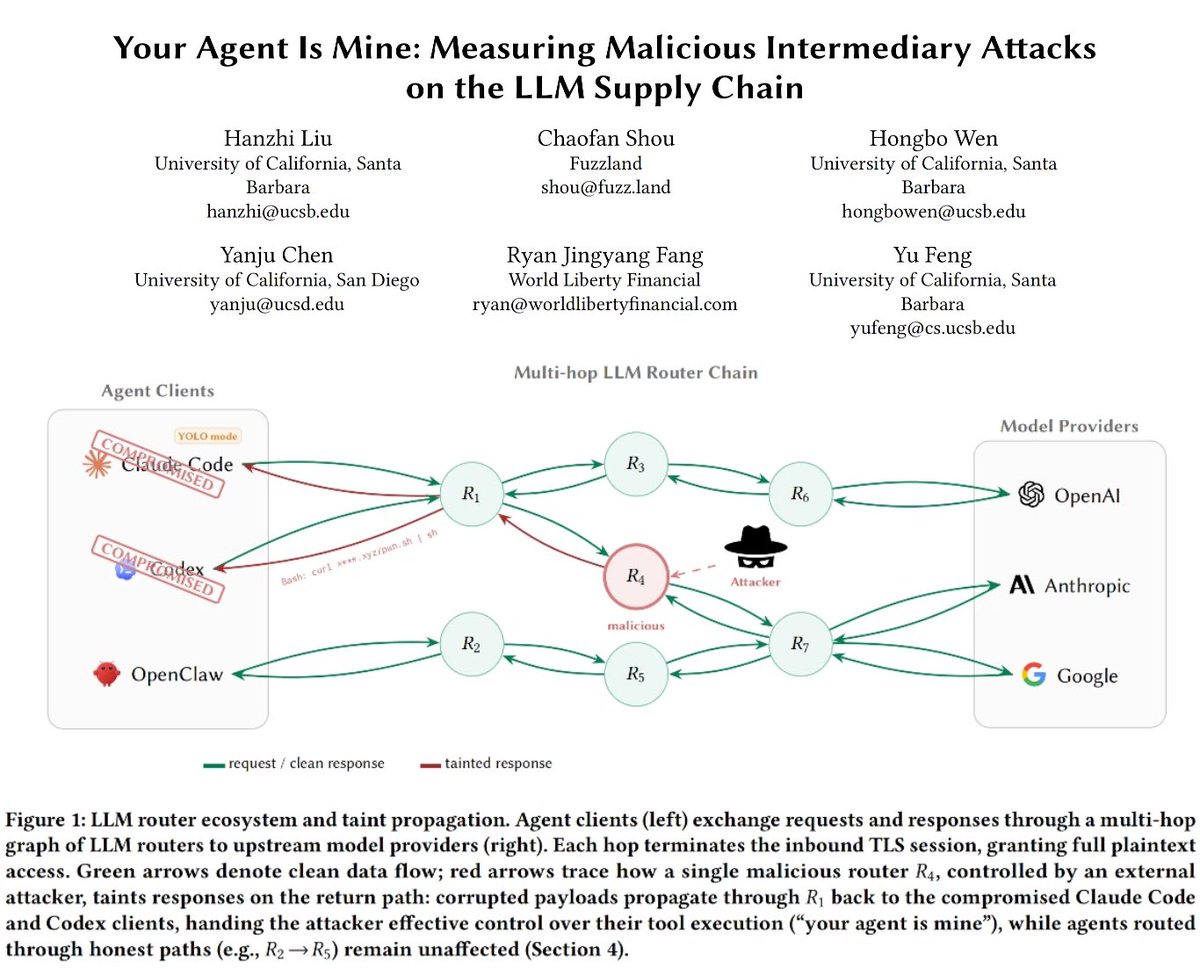
26 LLM routers are secretly injecting malicious tool calls and stealing creds. One drained our client $500k wallet.
We also managed to poison routers to forward traffic to us. Within several hours, we can directly take over ~400 hosts.
Check our paper: https://t.co/zyWz25CDpl
I bought a Fable dataset from one of the top Chinese LLM routers yesterday.
With just 6TB data, I can take over 7 Chinese/CIS gov entities & 19 top Chinese firms like Xiaomi, Huawei, NIO, Minimax using SSH keys, VPN configs, Aliyun keys, GitLab tokens sent to the router.
@thsottiaux@OpenAI@sama
Do you think this is normal? Even 5.6 also have issue ? Totally can’t used keep stuck and degraded
Or should I proof you identity that I’m malaysian? Or asking our prime minister @anwaribrahim to proof our identity and that as Malaysians user model won’t be degraded?
This weekend, I will be attending VCF Midwest for the first time, and bringing along my cell phone/custom GSM BTS exhibit as I did at VCF East a couple years ago. Hope to see some of you all there!
Hours ago, Tether froze approximately 39,273,713 USDT across 10 TRON addresses linked to Xinbi Guarantee新币担保.
Following its freeze of 汇旺担保Huione-linked funds, this appears to mark another crackdown on illicit Telegram-based escrow platforms. https://t.co/07xAOUaQPm