Yesterday, two men pleaded guilty to using ALPHV BlackCat ransomware to attack multiple victims across the United States. The two subjects, both Americans, worked in the cybersecurity industry and conspired to extort millions of dollars from U.S. victims. https://t.co/V9WwQJKmXn
📻 Y estos son los últimos segundos de emisiones de #RNE en Onda Media después de casi 89 años de historia. Sin un programa especial, sin un detalle o mención, sin una despedida a la altura. Después de las señales horarias: silencio. Hoy es un día triste para la radio. D.E.P #OndaMedia
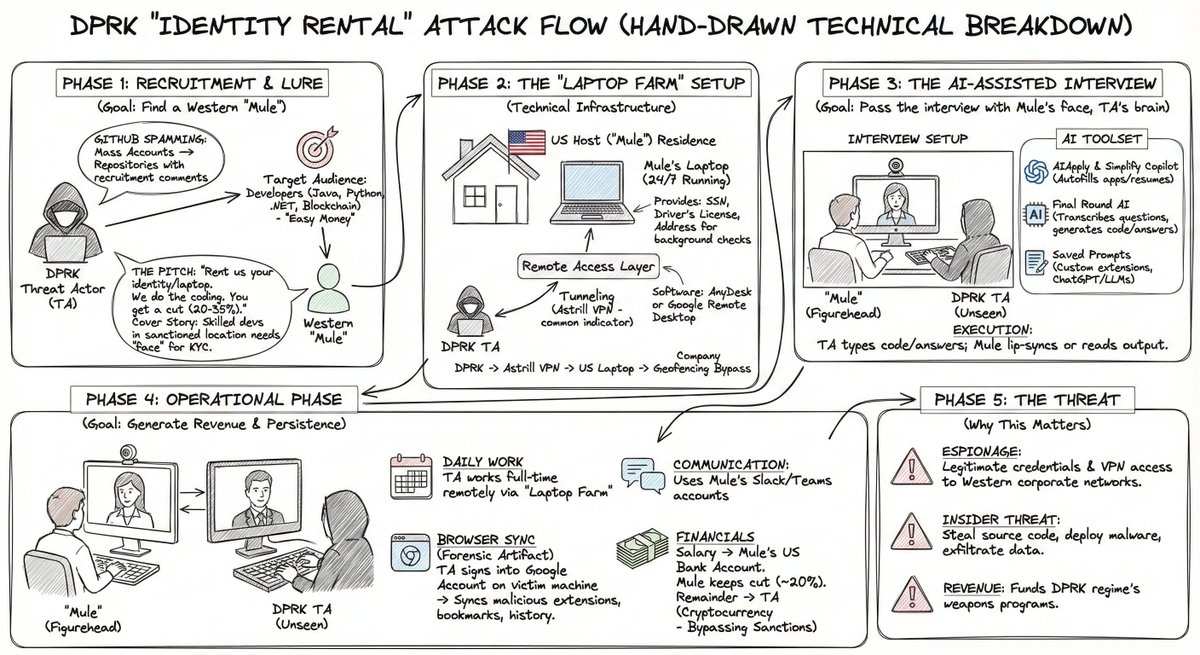
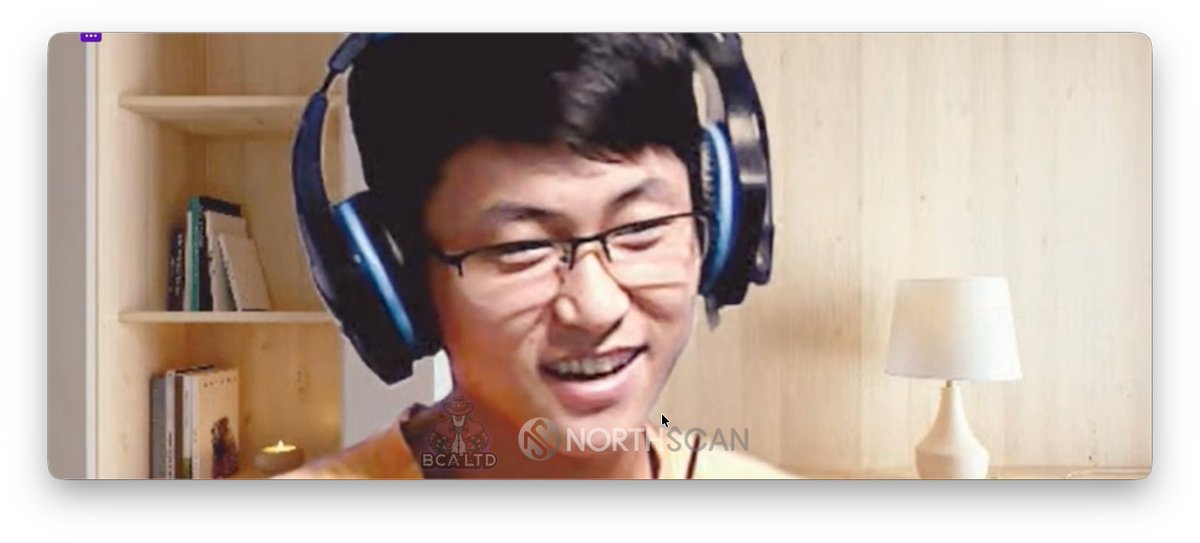
🕵️♂️ BCA LTD, ANYRUN, and NorthScan researchers built a honeypot laptop farm to watch North Korean IT recruiters in real time, exposing how they rent engineers’ identities for remote IT jobs.
💻 The honeytrap exposed the attackers' tools, AI helpers, and attempts to obtain full IDs, SSNs, and remote access while posing as “legit” IT workers.
➡️ https://t.co/6obtZqYHcY
@MathiasChu Por arriba y por abajo, quizás le interese lo que un investigador logró documentar y publicar.
Dice un amigo, el tiempo de soluciones simples a problemas complejos se terminó.
https://t.co/WFUog1uqev
📼 Por primera vez en la historia grabamos en video todo el ciclo de ataque de Famous Chollima (#Lazarus#DPRK) mostrando material único:
🗨️ Chats
🧰 Herramientas
🧠 Tácticas
💀 y potenciales víctimas.
⬇️ En esta Edición Especial en español contamos todo, con videos incluídos.
Si fuera solo agesic seria una papa, acá el diputado reafirma lo antes dicho, ni la más pálida, podrían empezar a formarse con investigadores INDEPENDIENTES sin conflictos de interes, o al compás de la teoria de la alfombra, q claramente no ha funcionado.
https://t.co/FjaPSesOxd
"Hasta las últimas consecuencias ". El Diputado Rodrigo Goñi @DipRodrigoGoni reclama saber qué hubo detrás de la desvinculación de Daniel Mordecki de la Agesic . El #FueraDeContexto con el futuro Presidente de la Cámara de Representantes. Entrevista completa en https://t.co/FEAgLSvkuV
This is a screenshot from American Academy of Pediatrics’ webpage, thanking the organization’s top corporate donors. These four companies make virtually every vaccine on the CDC recommended childhood vaccine schedule. AAP is angry that CDC has eliminated corporate influence in decisions over vaccine recommendations and returned CDC to gold-standard science and evidence-based medicine laser-focused on children’s health.
AAP today released its own list of corporate-friendly vaccine recommendations. The Trump Administration believes in free speech and AAP has a right to make its case to the American people. But AAP should follow the lead of HHS and disclose conflicts of interest, including its corporate entanglements and those of its journal—Pediatrics—so that Americans may ask whether the AAP’s recommendations reflect public health interest, or are, perhaps, just a pay-to-play scheme to promote commercial ambitions of AAP’s Big Pharma benefactors.
AAP should also be candid with doctors and hospitals that recommendations that diverge from the CDC’s official list are not shielded from liability under the 1986 Vaccine Injury Act.
When journalists got labs to test Johnson & Johnson's baby powder and found asbestos, J &J called the bosses of those newspaper and TV journalists and said, if you run this story, we will withdraw all of our ads. https://t.co/fk8KwfqjWW
📢 Este domingo 7 de diciembre sobre las 9:20h, estaré en el programa @NEUDC_RNE de RNE con Pepa Fernández, @minipetite y Javier Sánchez, director de Área de Política Audiovisual y Servicio Público de RTVE, donde daré mi opinión sobre el inminente “apagón” de la Onda Media. Sin duda será un debate muy interesante. 📻 👇
https://t.co/VJFGhB1Pdi
🕵️♂️ BCA LTD, ANYRUN, and NorthScan researchers built a honeypot laptop farm to watch North Korean IT recruiters in real time, exposing how they rent engineers’ identities for remote IT jobs.
💻 The honeytrap exposed the attackers' tools, AI helpers, and attempts to obtain full IDs, SSNs, and remote access while posing as “legit” IT workers.
➡️ https://t.co/6obtZqYHcY
Fantastic research showcasing how DPRK IT Workers are renting identities from engineers to land high-paying IT jobs at major companies.
Kudos to the researchers for exposing this TTP!
https://t.co/kvWFy5iyvK
🔥 After months inside #Lazarus’ fake hiring pipeline, we achieved something never seen before: the full Famous Chollima attack cycle captured on video, including their tools, tactics and targets.
🤝 This wouldn’t have been possible without our friends at ANY RUN (@anyrun_app) and NorthScan (@0xfigo).
⬇️ Read the full media coverage below. We’ll release the videos on December 4th via ANYRUN’s blog.
Researchers led by Mauro Eldritch captured the Lazarus APT's remote-worker scheme in action, revealing tactics for identity theft via fake job offers, highlighting the need for vigilance in remote hiring practices. #Cybersecurity#IdentityTheft https://t.co/7l44Hx5qKp
🤝 This work was a collaboration between:
▶️ ANY RUN (@anyrun_app), providing the sandbox and analysis platform
🔍 BlockOSINT (@0xfigo), handling initial contact with the TAs
🤠 BCA LTD (@BirminghamCyber), leading the threat intelligence analysis
🔗 https://t.co/atbvfZrTDp
Cayó Cryptomixer, un mixer muy usado por cibercriminales que lavó más de 1.300 millones de euros 💶
Además: investigadores graban a atacantes de Lazarus, atacantes transforman extensiones en spyware y dos nuevas campañas de fraude en Brasil.
Dark News #179 📧
Great talking to @MauroEldritch about the fascinating operation he, @north_scan and @anyrun_app carried out to dupe DPRK IT workers and expose their tools & techniques (while trolling them masterfully)!
For more, check out @nknewsorg's story on their op: https://t.co/W03tAVZPv4
Fascinating account from a fake laptop farm set up by researchers to surveil North Koreans scamming to get jobs at IT companies. The most comprehensive and detailed account of TTPs from #FamousChollima I've seen to date. Kudos to @0xfigo and @MauroEldritch
https://t.co/ZDGYIpGGno