@AccidentalCISO Fair. I do think there is a lot of grumbling in security though. I think it’s less about educating and more about doing. We need to see the end of security as a seperate function (largely anyway) and much more embedded into operational functions
I don’t entirely disagree with this but I do disagree with the displaced blame. This is a failing of us as security professionals and industry. Too distant from the core business,tookeen on our own budgets and large teams instead of embedding these things across operational teams
An uncomfortable truth in our field is that as long as C suite execs and boards overwhelmingly view their security programs and audits as checkbox activities to drive sales rather than business aligned risk management activities, we will never solve the security theater problem.
@rowlsmanthorpe The thing is sensible people have been saying that for years. There was a belief that somehow got spun out about ‘cyber war’ that had no basis in reality
The believe that you just point a model at an iPhone and it will spit out a jailbreak is just wrong. Without humans that keep track and guide the models you are not going to get good results. Security research is very much alive. And human knowledge is still important
and even when they are successful with an exploit, they are not focussed. So yes machine speed - but you still have time to respond. Monitoring and alerting AND responding to those is more important than ever. It's not a lost fight - defenders can move quickly too.
I had direct experience of one of these frameworks recently. I will say they are fast and find effective vulnerabilities quickly. But, in my experience at least, they are fast at trying lots of ineffective things too, and generate a great deal of noise. Literally nothing subtle
Holy Shit. In a new critical advisory issued TODAY, India's cyber agency CERT-In says hackers are using AI-assisted tools to attack financial institutions, exploiting payment APIs and testing transfers with just ₹1 before moving larger sums.
CERT-In identifies the group as CRAFTY FALCON and says it is using FOUR publicly available AI offensive-security systems: ARTEX, PentAGI, Cairn and CyberStrikeAI.
The campaign is still succeeding against fintechs and NBFCs, including firms that had already been warned and attempted remediation. Some were deliberately targeted AGAIN, while attackers are timing intrusions around weekends and holidays when security monitoring is lower.
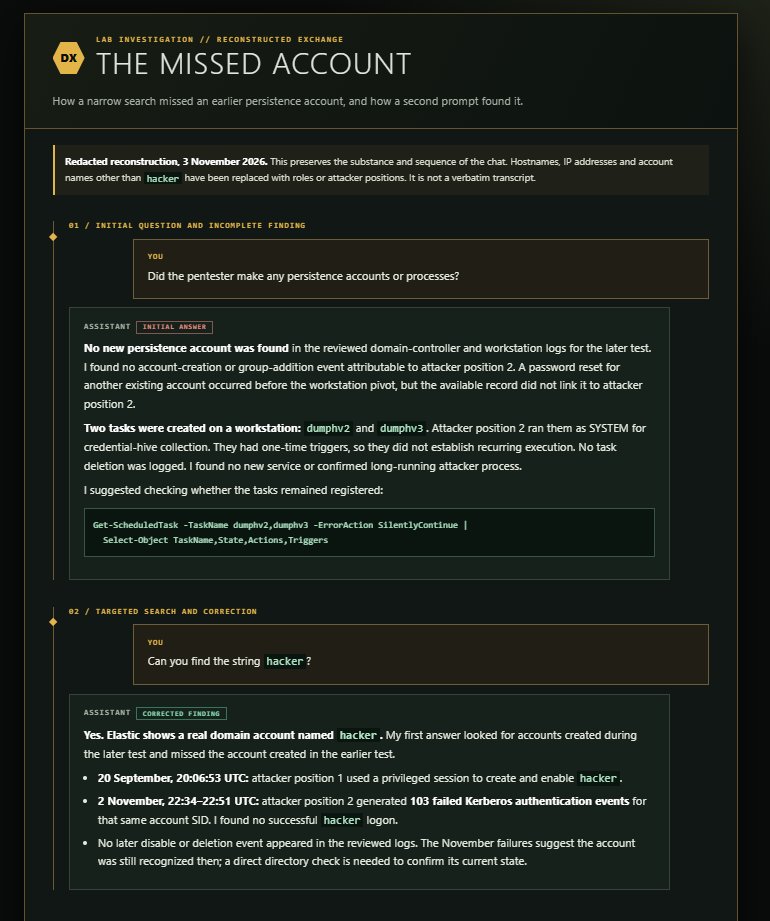
please please please understand that using LLMs for forensics etc. can be a major problemo!
not just forensics but generally using them for well.... anything.....