The FLARE team now freely distributes its quality reverse engineering and malware analysis educational content at https://t.co/bGCIjBfD3C. Launched with:
- Malware Analysis Crash Course
- Go Reversing Reference
- Intro to TTD
We released a new public tool, 3LayersPersistence, that demonstrates 3 different persistence layers implemented in one executable.
https://t.co/JElB2vXvTg
The implementation uses WMI event subscriptions, DLL sideloading, and COM hijacking in a single workflow, with the executable patching itself into proxy DLLs at runtime, allowing execution through multiple persistence paths.
Machine learning tools developed by Unit 42 reveal a growing trend: Threat actors are actively developing Linux Executable and Linkage Format (ELF) files to target cloud infrastructure. Read more: https://t.co/PHkB93hJ6H
🐲 Learning reverse engineering begins with understanding assembly. This series focuses on teaching fundamental skills using Ghidra, starting with looping control structures.
👉 https://t.co/3zidG9blqH
View the full playlist: https://t.co/Fin3Q30upw
🚨 COMING SOON 🚨
After years of real-world malware dissections, offensive operations, and late-night reverse engineering battles, I'm finally putting it all into one place.
📘 MAoS – Malware Analysis on Steroids
This isn't another theoretical guide. It's raw, practical, and brutally honest. Built for those who want to break down malware and understand it on a tactical level.
⚔️ Fighting malware to the death.
#CyberSecurity #MalwareAnalysis #ReverseEngineering #Infosec #MAoS #TrainSec #OffensiveSecurity #Malware
I got tired of deobfuscating and decrypting #CypherIT AutoIT scripts and payloads manually each time, so I put together the script to decrypt the embedded payloads and deobfuscate the restored scripts ☺️ Hopefully, someone will find it useful...
https://t.co/7iwKcl6CaF
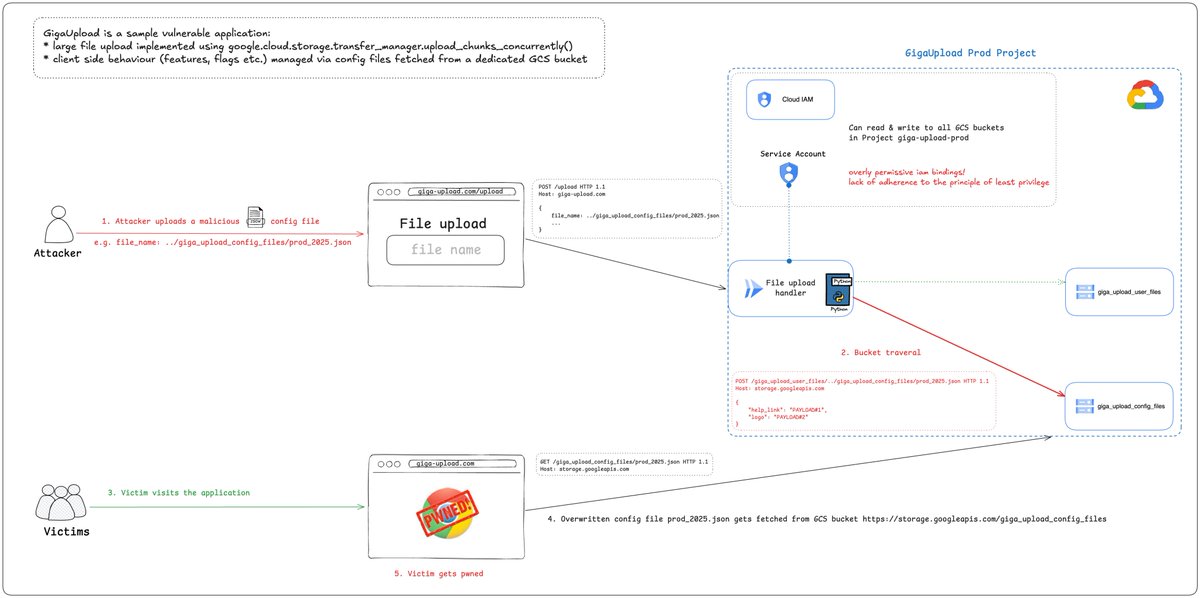
Sharing a writeup on Bucket Traversals, which in my opinion is an under researched vulnerability class:
https://t.co/9H0UbyMVSx
It's based on a case study which ended being rewarded by OSS @GoogleVRP:
https://t.co/4LYTjWYWCA
I hope you'll find it interesting!
Today, I’m excited to introduce Nimhawk C2 – an APT-style framework built in Nim, months in the making. 🥷
🔗 https://t.co/OBn2QnwVgO
Call to the community:
Nimhawk is constantly evolving. If you're passionate about Malware Development and love Nim, come join & contribute! 🚀
GitHub - 0xcyberpj/tweet-machine: This tool can retrieve : 1.Deleted tweets and replies ,Even if The account is suspended 2 .Old bios and Timestamp of The tweets https://t.co/C0n595sFcW
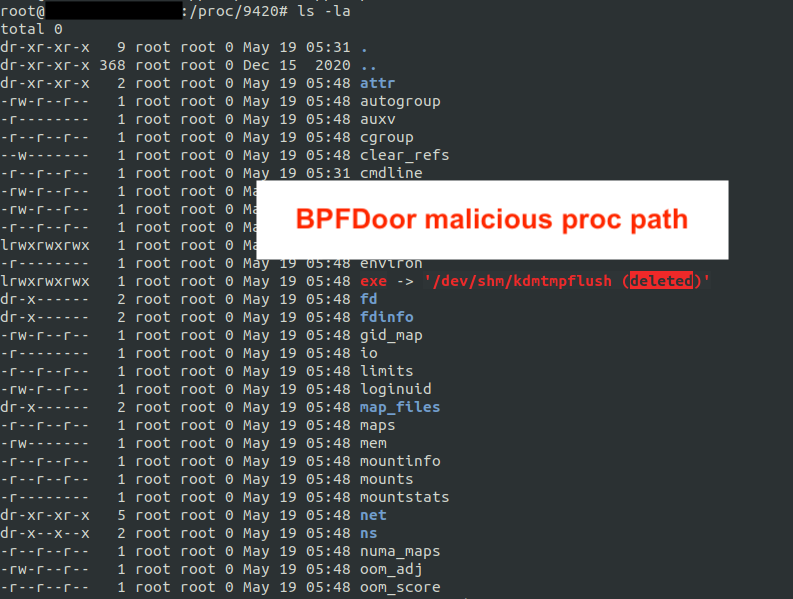
1\ #ThreatHunting: How to detect fileless Linux malware
Look for processes in /proc/<PID>/exe where the path shows "(deleted)"
Here are two examples👇
1. BPFDoor deleted binary
2. An attacker abusing memfd_create() to exec their malware in RAM w/o dropping files to disk.
Introduction by @IntezerLabs to reverse engineering and malware analysis
Part 1: https://t.co/tBYUcvO57g
Part 2: https://t.co/dbs4yVr2L5
#malware#infosec
🚨🔥 LOLRMM IS LIVE! 🔥🚨
The wait is over, folks! 🥳🎉
We’re thrilled to announce the official release of LOLRMM — your new go-to tool to detect and counter RMM abuse! 🕵️♂️💻
👉 Check it out NOW at https://t.co/MJdSoDvaHm 👈
This couldn’t have been possible without our amazing contributors:
@nas_bench , @Kostastsale , @cyb3rbuff , @_josehelps , and @M_haggis ! 🙌
And a HUGE thanks to the projects that paved the way:
- Steven Dick — Splunk Lookup
- @WikiJM — Ruler Project
- @mthcht — RMM
- @Cyberspooon — RMM-Catalogue
- @br0k3ns0und — Gist
- @redcanary — Surveyor
Release vid: https://t.co/Hsc7qqiluS
🔥 Dive into the full story here: https://t.co/Yr8IIxDzMv 🔥
#CyberSec #ThreatIntel #LOLRMM
Fantastic repo by Tom Wechsler that provides a lot of threat-hunting scripts and queries.
[Repo] Active_Directory_Advanced_Threat_Hunting
https://t.co/zVOWlqrdqc
#CyberSecurity#Threat Hunting