Lost my phone at the office and spent 30 minutes turning the place over. Find My was disabled by MDM.
Out of ideas, I asked Claude how I could find it. It suggested tracking the Bluetooth signal strength, then wrote me a meter in about a minute.
I walked around watching the number climb. Found it.
Apparently you can just make the tool you need now.
Code: https://t.co/fmnISzHfZ2
Fortinet CVE-2026-24858.. is this even real life anymore?
”An attacker’s valid FortiCloud session, tied to their own device, gets accepted as legitimate for other users’ devices.”
If you're new to #dfir and want a pro tip, schedule your PTO during Eastern Orthodox Christmas (Jan 7th), and Chinese New Year (Feb 17-Mar 3) #IYKYK#infosec#ransomwareattack
The complete lack of useful information and writing that seemed like they were trying to hit a word count made this almost comical. But they had the gall to put the CISO as the author. 🤦
If the NVD has more useful information than your notice, you're doing it wrong.
Oracle’s Saturday security release did not give any information about whether the latest flaw in E-Business Suite (CVE-2025-61884) has been exploited.
Oracle Warns of E-Business Suite Bug https://t.co/8fnIlgVFhm #decipher#deciphersec
The U.S. Secret Service has announced that, following a monthlong investigation, it has carried out an operation which resulted in the dismantling of a network consisting of more than 300 SIM Servers and 100,000 SIM Cards at multiple sites across New York and New York City, all within a 35-mile radius of this week’s United Nations General Assembly.
According to officials, the network could interfere with emergency response services, conduct encrypted communication, jam cellular networks in New York, as well as disrupt official communication from and eavesdrop on the U.N. General Assembly, capable of sending over thirty-million text messages per minute, anonymously. The official said the agency had never before seen such an extensive operation.
The Secret Service believes that the scale of the equipment discovered suggests the network could be part of a nation’s surveillance operation, with initial analysis of the data on some of the SIM Cards having identified ties to at least one foreign nation, as well as links to criminals, including the members of Cartels, already known to be operating in the United States. Cybersecurity experts have stated that only a handful of countries could pull off such an operation, including Russia, China and Israel.
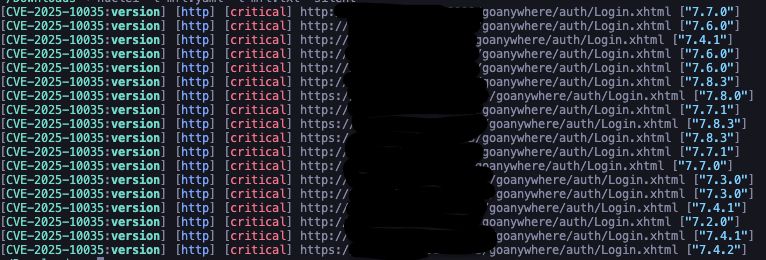
🚨 Critical — CVE-2025-10035 (CVSS 10.0): Fortra has disclosed a deserialization flaw in the GoAnywhere MFT License Servlet that can allow remote command-injection.
I've created a #nuclei script to detect vulnerable instances at scale:
https://t.co/tgEvGaFAJh
Keep at it long enough, and this is an inevitable outcome. Such a terrible to waste to go from being a smart kid with so much potential to facing a lengthy prison sentence, all without even leaving his home (probably his bedroom in his,parents’ home, at that).
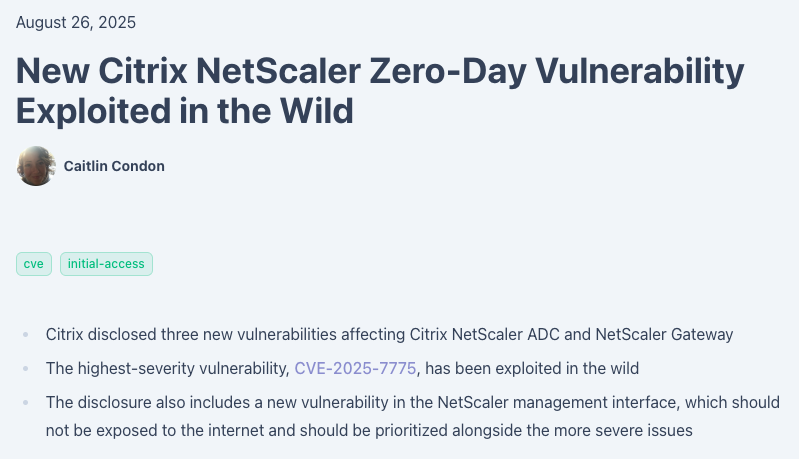
Citrix has disclosed three new vulnerabilities in NetScaler ADC and NetScaler Gateway, including CVE-2025-7775, which is already being exploited in the wild. More from VulnCheck VP of security research Caitlin Condon here: https://t.co/iaXHYzizCC
@NinjaParanoid And the reason that the industry has lost the definition between RT and basic testing is because most orgs aren't ready for real RTs because they lack security fundamentals. Like, brother you do not need an APT simulation, you have open RDP, no EDR, unpatched VPNs, etc etc.
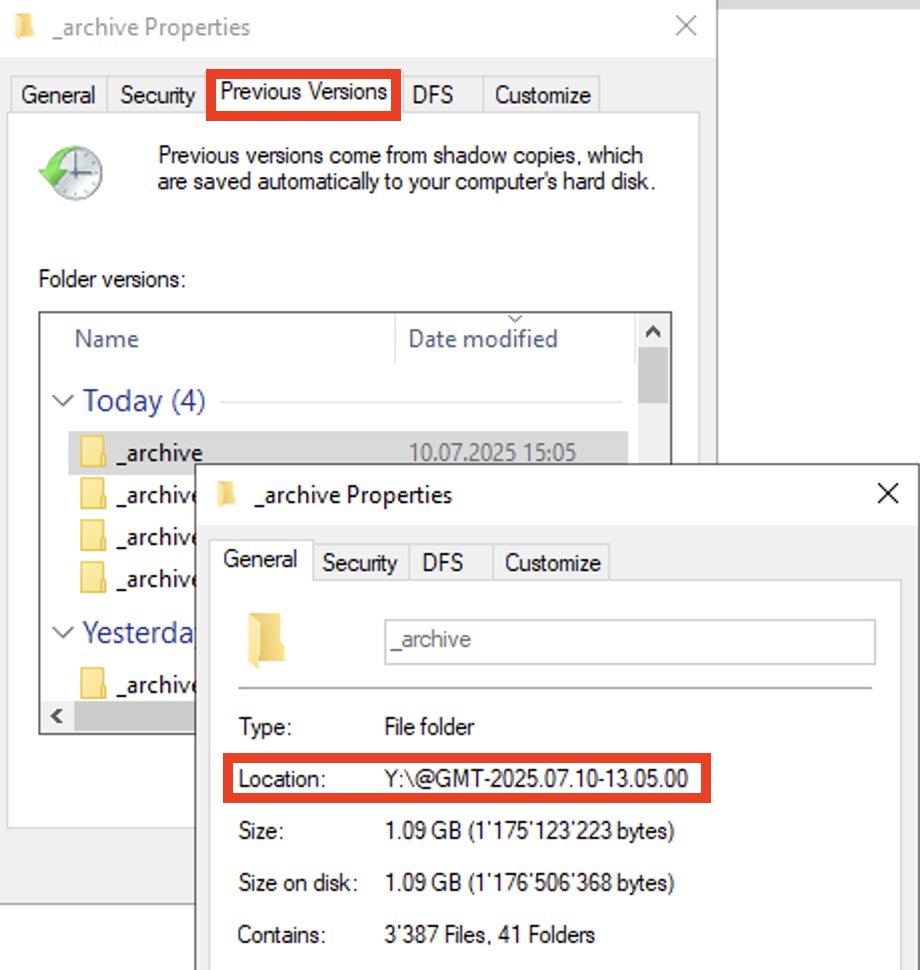
During a recent incident response case, we observed the following file access: \\localhost\C$\@ GMT-2025.06.21-10.53.43\Windows\NTDS\ntds.dit
This is a clever method of accessing a Volume Shadow Copy (VSS) snapshot. Many EDR and detection systems typically monitor for commands such as 'vssadmin list shadows', and may trigger alerts based on their use.
However, by leveraging the "Previous Versions" feature in Windows (see screenshot), attackers can select a snapshot, view its properties, and enter the '@ GMT' path directly in Explorer. This allows them to browse the snapshot's contents without needing to use the command line.
Because this technique doesn't rely on typical shadow copy commands, it may evade detection by your EDR or SIEM solution. You might want to test it in your environment to identify and close this potential detection gap 🦸♂️🦸♀️
Mandiant is now aware of multiple incidents in the airline sector that resemble Scattered Spider. The industry should button up its call centers where this actor has had a lot of success with social engineering. https://t.co/70PHV7gx5S
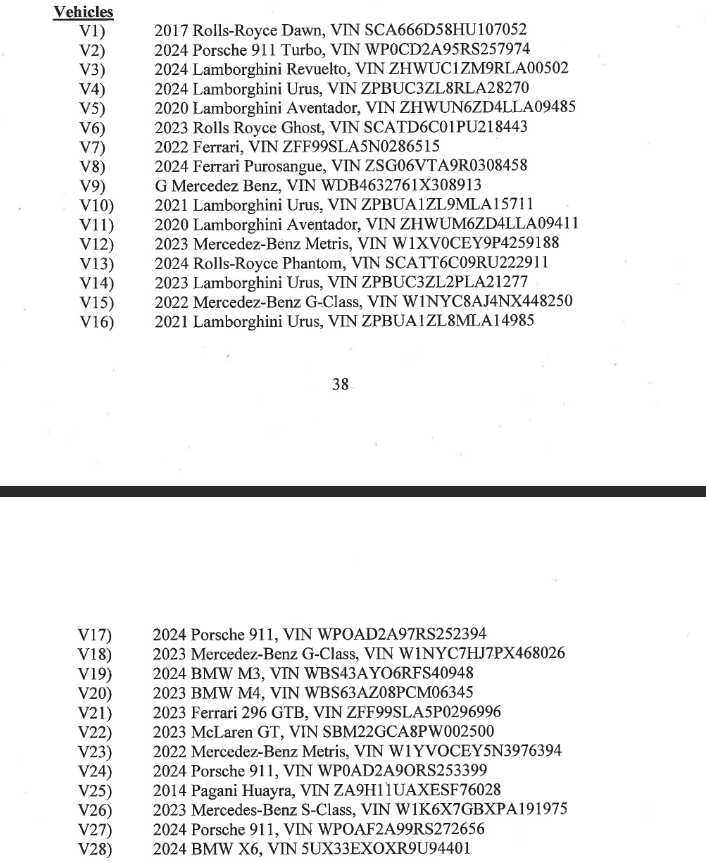
Today the United States Department of Justice announced the indictment (and in some cases additional charges) for 12 individuals. The defendants are charged in RICO conspiracy for over $263,000,000 in cryptocurrency theft, money laundering, and home break-ins.
Each individual listed was (in some capacity) involved in the COM(munity) scene.
This is the first time, to the best of our knowledge, a group of primarily English speaking, loosely affiliated, cybercriminals are in a RICO case.
RICO, the United States "Racketeer Influenced and Corrupt Organizations Act", passed in 1970, is generally reserved for organized crime. It was designed to combat organized crime and allows prosecutors to charge individuals involved in an ongoing criminal enterprise.
RICO charges are not a joke. These are extremely serious charges.
RICO charges allow multiple people to be tied to a conspiracy and amplify any/all charges. A single RICO charge is worth 20 years in Federal Prison and can extend to life in prison.
The United States Department of Justice slapping COM-scene people with a RICO charge is a sign they're not playing around with cryptocurrency fraud.
The individual indicted are as follows:
- MALONE LAM a/k/a "King Greavys", "7", "$$$", "Kg", "Anne Hathaway"
- MARLON FERRO a/k/a "Marlo", "GothFerrari"
- HAMZA DOOST a/k/a "Scyllia", "¢"
- CONOR FLANSBURG a/k/a "OO", "Green Room", "d0uu0b"
- KUNAL MEHTA a/k/a "Papa", "The Accountant", "Shrek", "Neil"
- ETHAN YARALLY a/k/a "Rand", "15%"
- CODY DEMIRTAS a/k/a "K O", "Kody"
- AAKAASH ANAND a/k/a "Light", "Dark"
- EVAN TANGEMAN a/k/a "E", "Tate", "Evan | Exchanger"
- JOEL CORTES a/k/a "J"
- [Unidentified 1] a/k/a "~_~", "Squiggly", "CHEN"
- [Unidentified 2] a/k/a "Danny", "Meech"
- TUCKER DESMOND
The full article, released by the Department of Justice, defines the roles of each individual, the charge they carry, a total sum of money stolen and/or items illegally acquired using stolen money, and additional (unlisted) co-conspirators.
Note: per the RICO charge, if the Judge rules the individual was involved in widespread fraud or violent crime, individuals may face a punishment of life in prison. Hence, each person listed may eligible for life in prison
Time being faced:
- MALONE LAM: 60 years
- MARLON FERRO: 60 years
- HAMZA DOOST: 40 years
- CONOR FLANSBURG: 40 years
- KUNAL MEHTA: 40 years
- ETHAN YARALLY: 40 years
- CODY DEMIRTAS: 40 years
- AAKAASH ANAND: 60 years
- EVAN TANGEMAN: 40 years
- JOEL CORTES: 40 years
- [Unidentified 1] - 60 years
- [Unidentified 2] - 60 years
- TUCKER DESMOND - 20 years
In another great body of research from @the_emmons, this disclosure chains 3 new vulns in SonicWall's SMA 100 appliances to go from a low privileged account to full RCE as root!! Awesome work as always 🔥🔥🔥