To all my Windows DFIR friends out there! 🔥
Have you ever wished for a single Windows forensic artifact parsing tool that could parse just about anything, while being blazing fast, stable, well-organized, memory-safe, standalone, and cross-platform?
Well, I certainly have!
So, I spent the past month obsessively building one! 😎
Say hello to "Juntei" (准胝)! 🎉
https://t.co/3Xf7ZbXYyo
https://t.co/ntazHaljHw
Think of it as "Hayabusa, but for non-EVTX artifacts!"
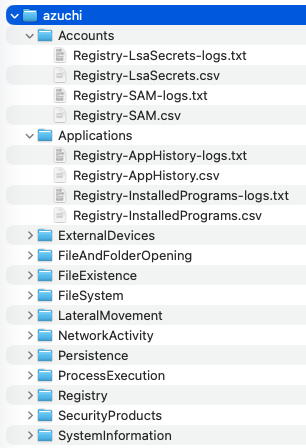
It can scan regular directories, VHDX, and E01 files directly, without even having to mount them.
I just ran a performance test on 30 Windows triage data collections (125 GB total), and my MacBook Pro M4 cranked out 40 GB of parsed data in less than 5 minutes! 🚀
It's trivial to use. Just run the "auto-parse" command, and Juntei will automatically parse all supported artifacts for you.
Want a super timeline? No problem! Simply run "super-timeline" against the parsed output directory, and you're good to go!
But here's a little warning! ⚠️
The "SUPER" in super timeline is no joke! 😂
At the moment, the generated timelines can be about 5 times larger than the parsed data directory!
So here's my recommendation: Run Hayabusa first to pinpoint when an incident occurred, then filter your timeline to the relevant time period.
By the way, JSONL super timelines are generated in a Timesketch-compatible format by default, so you can import them directly!
For analyzing CSV output, I highly recommend IRFlow Timeline!
I've created dedicated templates to ensure the different field types are correctly recognized and displayed.
https://t.co/iczzGaD7NV (Wait for v2 to be released, or use one of my forks!)
macOS:
https://t.co/wh51vxwcOU
Windows:
https://t.co/Vav5rnVJ2v
Linux:
https://t.co/yAg9aBk4sp
I hope you enjoy using it! 🔥
If you find Juntei useful, please help spread the word to your fellow DFIR friends!
And don't forget to give us a star on GitHub! ⭐ 🙏
Enjoy! 🤗
Started posting some stuff for this. https://t.co/fKuaWiMsx8 starting with markdown files that helped guide the agents, and various parts of the workflow. More to come as I go through it all
Exploiting Reversing (ER) Series | Article 10: iOS Security Research (part 01)
223 pages, free. The first article in the series aimed at iOS itself, and the opening of a multi-part sequence.
Published on:
https://t.co/VlebcByqKG
This article will be published on https://t.co/GBDi0lO8Zd next week.
I would like to thank Ilfak Guilfanov (@ilfak) and Hex-Rays SA (@HexRaysSA) for the continuous support.
Hope you enjoy the read!
#iOS #Apple #VulnerabilityResearch #ExploitDevelopment #ReverseEngineering
The nineth article (38 pages) of the Malware Analysis Series (MAS) is available on:
https://t.co/2RTyR4Foqj
I would like to thank Ilfak Guilfanov @ilfak and @HexRaysSA for their constant and uninterrupted support, which have helped me write these articles.
Even though I haven't been on this subject for years, I promised that I would write a series of ten articles, and the last one will be released on next week (JAN/15).
Have a great day.
#windows #shellcode #malware #reverseengineering #reversing #idapro #malwareanalysis
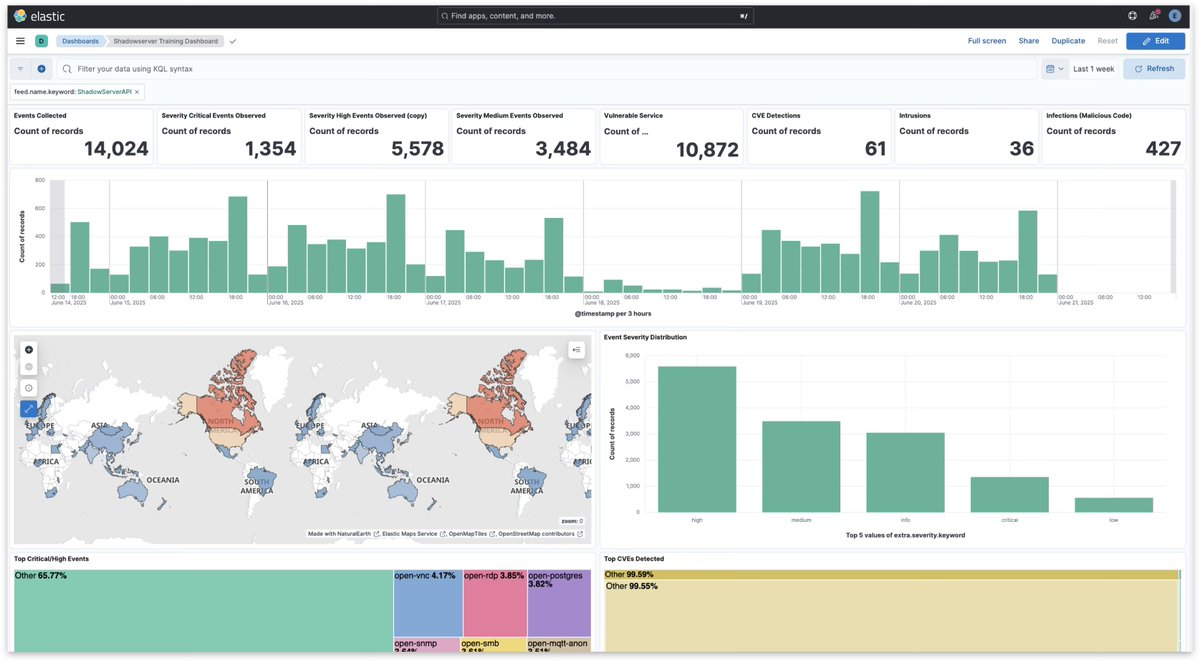
We published a "Shadowserver-in-a-box" platform based on IntelMQ + ELK that can ingest, process and visualize our threat/vulnerability/victim data feeds. Available as a VM or Docker image for free download. Use it for training or in production!
https://t.co/nBPIbUqXGV
Giveaway - Our instructor-led advanced bootcamps for sharpening your Red Team skills start this weekend.
Attacking and Defending Active Directory - Advanced Edition (CRTE) starts this Friday.
Advanced Windows Tradecraft - Evasion Techniques for Red Teams (CETP) starts this Saturday.
I am giving away one seat for each of the bootcamps. To participate, please Follow @nikhil_mitt and @AlteredSecurity, Like, Comment and Repost.
We will announce the random winners on Wednesday.
https://t.co/Kd0RNoINWc
#RedTeam #Evasion
We’ve all heard the proposition: "Replace your frontline with LLMs to save costs." But is it actually a good strategy?
In the latest episode of Behind the Binary, Kevin Harris explains why this is the worst possible place for automation.
🔥 "I have heard many times about how people want to replace all of tier one incident response... and that is exactly the worst possible place to put AI tooling."
When your "predictive text engine" makes a mistake, it does it with 100% confidence. In incident response, that’s a recipe for disaster.
Want to hear the full conversation? Listen now on Apple 👇
🎧 https://t.co/SMu0R4oAtB
🦔 📹 New Video: Can office files be malicious without Macros?
➡️ VSTO Add-Ins
➡️ External Templates
➡️ Checklist for Office analysis
#MalwareAnalysisForHedgehogs
https://t.co/qQFvEZs5fv
Open Klara released - your own private cloud Yara scanner!
Together with our community member Gajesh, I would like to announce the fork of the KLara project into Open Klara!
We aim to maintain, support and fix future bugs.
Open KLara is a community-driven fork of the original KLara project by Kaspersky Lab, aimed at helping Threat Intelligence researchers hunt for new malware using Yara.
Think of it as your own private Yara scanner where you can setup malware / clean collections on multiple distributed servers and fire up Yara rules, everything centralized with a nice web interface / UI.
For more info, check https://t.co/AszkevTtvz
Happy hunting!
Beyond stoked to get a signed copy of Jaron’s new book, "Threat Hunting macOS" 📚😍
Jaron is one of the go-to voices in macOS threat hunting & malware research, so do yourself a favor and grab a copy: https://t.co/L8ocjG2hqy
#OST2 has a ton of material relevant to RE. And our https://t.co/nrdXukMwmK introduction to IDA as a debugger class instructor, Christina Johns @bitmaize, is working on "RE2001: Introductory Static Analysis of C-based programs", which will unlock many new classes!
If you're interested in learning more about time-travel debugging (TTD), consider joining my upcoming webinar with VirusTotal. You can register here:
https://t.co/gHxuDcbcz5
Going to cover some basics from my recent blog :)
https://t.co/8PphJjKJ2a