⚡ Microsoft Teams to Warn Users About Malicious Links Hidden in QR Codes
Details: https://t.co/OeWGgDsem3
Microsoft is extending Teams security to detect malicious links hidden inside QR codes and warn users after a message has been delivered. The update adds QR code checks to existing Microsoft Defender for Office 365 protections, giving users clearer warnings and security teams more data to investigate suspicious messages.
The new protection checks Teams messages containing QR codes after delivery. Defender extracts the web addresses stored inside those codes and checks whether they point to malicious content. If a dangerous URL is found, Teams displays a warning on the affected message in both internal and external conversations.
#cybersecuritynews
One of the simplest (and most impactful) bugs to look for is switching out the algorithm on JWT tokens to "none". Here are the steps:
🟧 Decode the JWT and set the header to {"alg":"none","typ":"JWT"}.
🟧 Change the sub claim to {"sub":"administrator"}.
🟧 Strip the signature, keeping the trailing dot so the token ends in .
🟧 Send it!
Try it yourself here 👇
https://t.co/GFazIhaTcw
You don't need a USB. You need to look like one.
Emulate the device, Windows fetches a signed package off Windows Update and runs vendor code as SYSTEM. Arbitrary code execution, LPE, standard user or empty logon screen.
DEF CON 34 talk w/ @Qm9yamFN.
Link at the first comment.
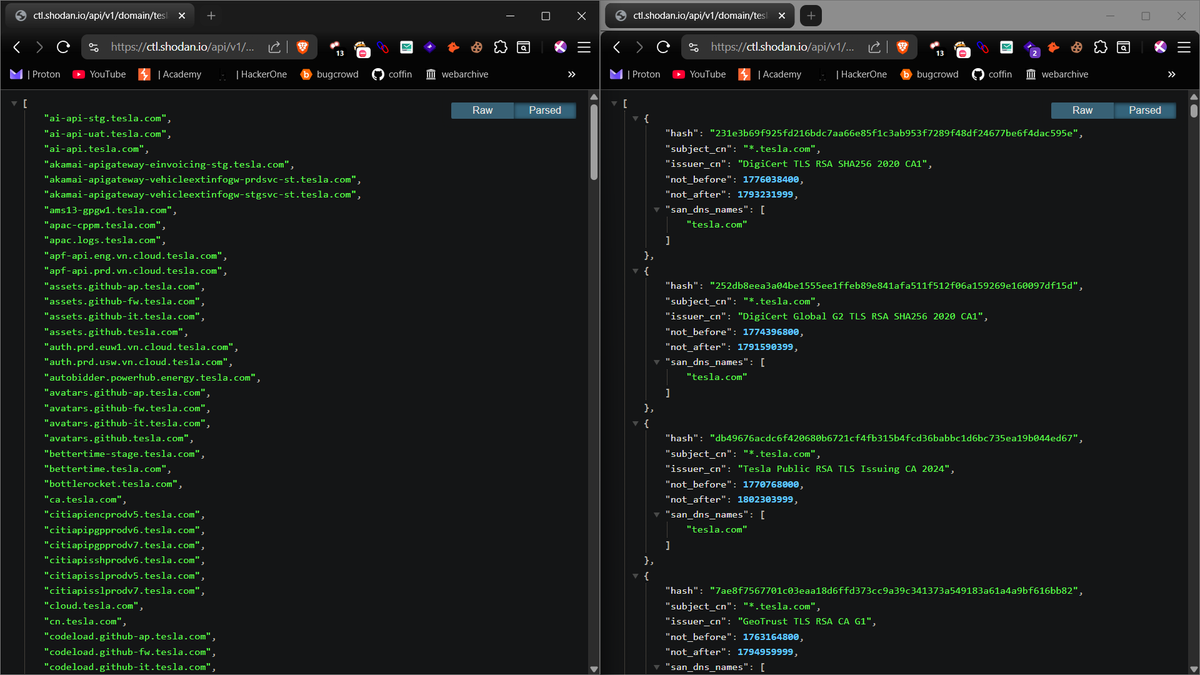
You can also use Shodan's Certificate Transparency (CT) API to enumerate a target's subdomains directly from the https://t.co/b8sFqTyruD database.
https://t.co/6vL6HjRSmi
/api/v1/domain/{domain} ~returns the certificates that match a domain
/api/v1/domain/{domain}/hostnames ~returns all hostnames associated with a domain
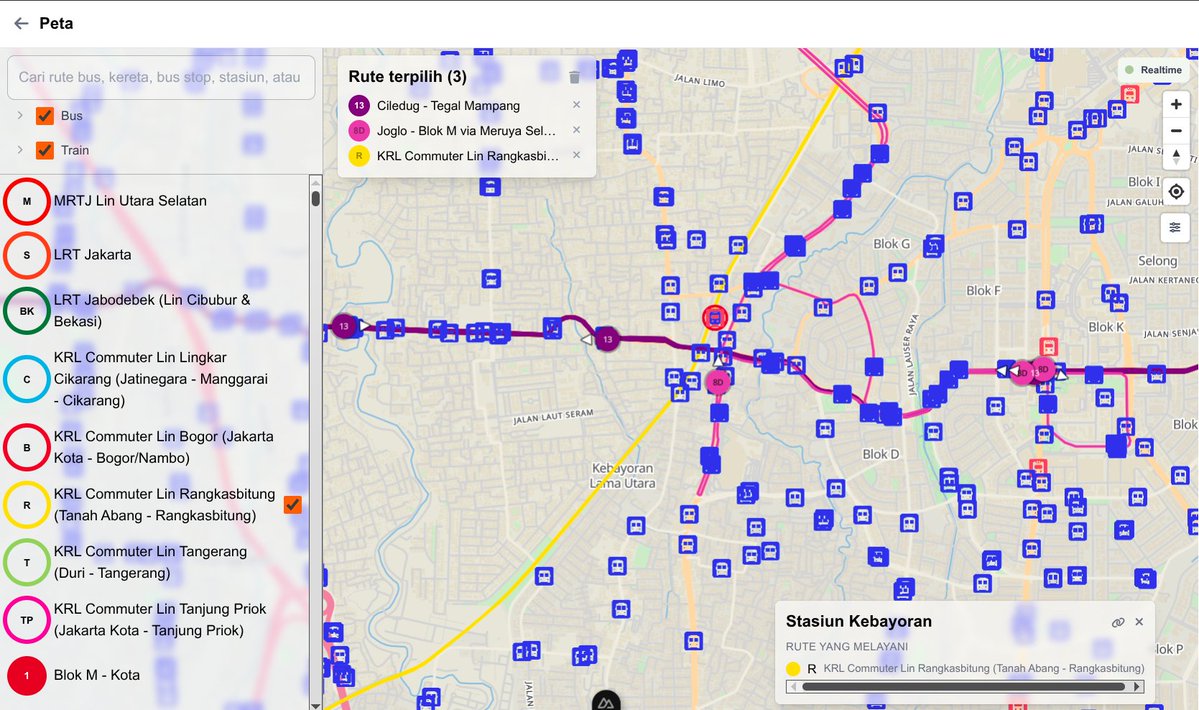
Hi warga pengguna transum. Aku baru aja buat app untuk melacak transum di Indonesia 🚌
🔗 https://t.co/hvnKdCs9s7
Selama ini kita harus install app beda-beda dari tiap provider (TJ, Mitra Darat, dll). Ribet kan? Makanya aku ngumpulin semuanya jadi satu.
eBook Open Source INTelligence (OSINT)
https://t.co/Dnr5gmb6hc
Disertai dengan source code python
https://t.co/rkvvCSvE3i
https://t.co/YhPH1sFAjC
Ditulis untuk para profesional dalam melakukan aktifitas intel di Internet :) ...
FREE @offsectraining training modules over at https://t.co/DZOYPd9BLw
Interactive HTML pages free for everyone to get to - with command per command, module per module
TOTALLY FREE FOR ANYONE AND EVERYONE
Sometimes standing for what you believe, means standing alone.
Bismillah.
Just released an open-source tool for automating VirusTotal-based recon and attack surface exploration.
InshaAllah it can help with asset discovery, correlation, recursive subdomain enumeration, URL discovery, and JavaScript analysis.
https://t.co/tbefCw4tXN
A Detailed Guide on Ligolo-Ng
🔥 Telegram: https://t.co/upuP8k8ckB
✴ Twitter: https://t.co/Za7rYILz6E
Ligolo-Ng is a modern tunneling and pivoting tool used by penetration testers to perform lateral movement and access internal network services through compromised machines. It enables secure communication channels between attacker and target systems.
📚 What You’ll Learn in This Guide
⚙️ Introduction to Ligolo-Ng
🧰 Installation & Setup
🖥️ Ligolo-Ng Server Configuration
💻 Ligolo-Ng Agent Setup
🌐 Creating Tunnels
🔁 Network Pivoting
📡 Accessing Internal Services
🧪 Scanning Internal Network through Tunnel
�� Article:
https://t.co/RVcDpWZvQD
#CyberSecurity #EthicalHacking #Pentesting #RedTeam #Pivoting #InfoSec
Introducing HTTP/2 Bomb: a remote DoS in nginx, Apache httpd, Microsoft IIS, Envoy, and Cloudflare Pingora. A single client pins 32GB of server memory in 10s. Found by Codex.
Blog post: https://t.co/WO9MeExoun
PoCs: https://t.co/NpVgEHBHPl
WHAT THE HACK HAPPENS IN THIS YEAR!
cPanel & WHM - Auth bypass (CVE-2026-41940)
here is the exploit POC: https://t.co/uLFJ5XqTc0
Join my bugbounty telegram chennal: https://t.co/J6uPf8H57o
#bugbounty#cpanel#cve
Spent more than 4 years me and Mr @wadgamaraldeen gathering and preparing full bug bounty methodology that you need to start bug bounty
I think You need to look at it , gathered alot of scenarios that can't be inside courses
Let's Do it
https://t.co/CaQ7eaxeow
#WebSecurity #AppSec #WebAppSecurity #Pentesting #PenTest #RedTeam #Vulnerability #VulnerabilityResearch #ExploitDevelopment #OWASP #OWASPTop10 #XSS #SQLInjection #IDOR #RCE #SSRF #LFI #bugbountytips #bugbounty #SecurityTesting
#BugBounty #CyberSecurity #EthicalHacking #InfoSec #HackerOne #Bugcrowd #SecurityResearch #OWASP
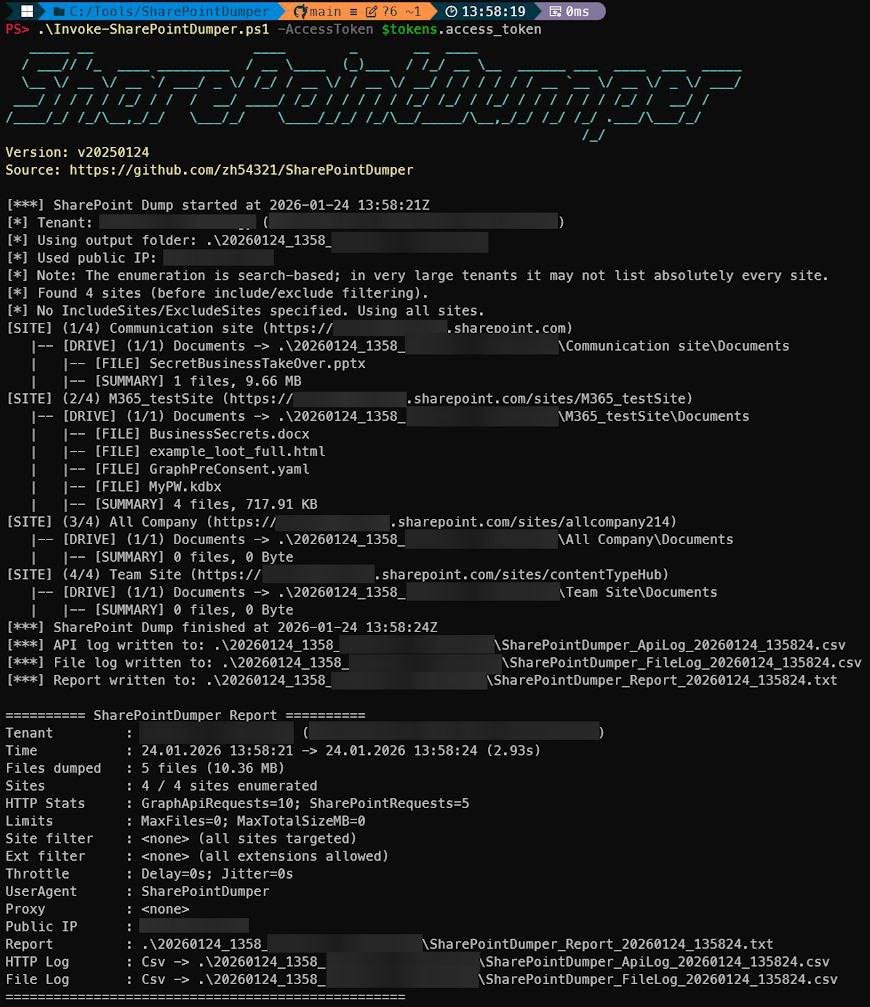
A tool for enumerating SharePoint via Microsoft Graph. It recursively downloads files and logs every HTTP request for correlation with SIEM and development of detection rules
https://t.co/mQOYuVgEtD
#blueteam#redteam#pentesting#windows
Red teamers + CTI analysts: this one’s for you.
Turn threat reports into adversary profiles using ATT&CK + AI workflows. Mar 26 with Jean-François Maes.
📅 10AM–12PM ET
🔗 https://t.co/mBwqq38YSn
#SEC565#RedTeam#ThreatIntel#AI
Claude Bug Bounty Hunter -
https://t.co/zCfJPWRXdG
Claude Code skill that turns Claude into your AI bug bounty co-pilot. Point it at any target and Claude maps the attack surface, runs your scanners, validates findings, and writes the HackerOne or Bugcrowd report — all from a single conversation.
#bugbounty #bugbountytips #ethicalhacking #claudecode #cybersecurity #hacking #infosec #pentest #hackerone #bugcrowd #opensource