Exciting to see search engines implement ChatGPT, or something similar, into their products. It will be exciting receiving disinformation, propaganda, or advertisements from the highest bidders
Hey @TIM_Official would you mind stop stalking me?
Got more than 20 call by your operators only in the past 24hours.
Plus, your operators are pretending to to be @VodafoneIT to scam people, seriously? #scammer#stalker
Although MS Defender is getting a really better job for mitigating malicious tasks like #CobaltStrike#C2 beacons, it is still (almost) possible to run it on an up-to-date Windows using basic WinAPI (remote process) injection technique (remarks ⬇️). Merry Xmas for everyone! 🎄
I created a #CyberChef recipe to ease the extraction of URLs from the word document (.doc & .docm) which download #Emotet. It is not completely foolproof, but it worked 99% of the time for me.
https://t.co/CV0CVh4Hdo
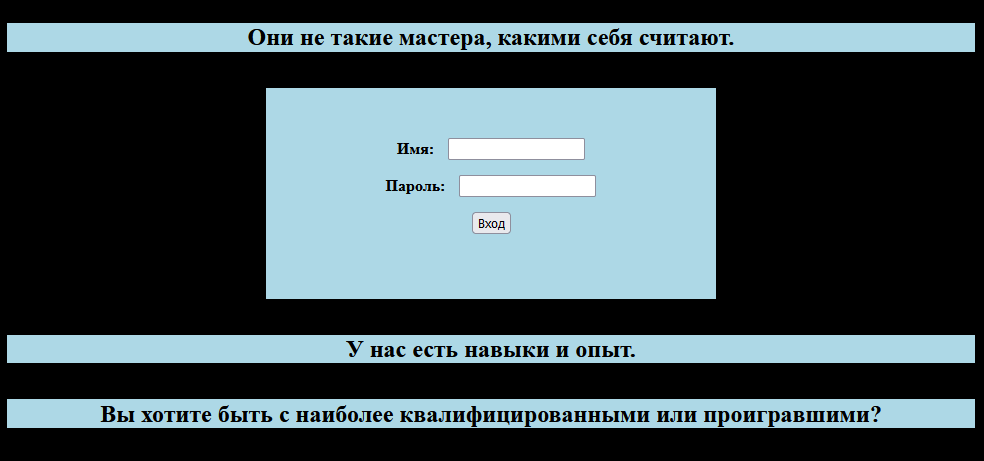
REvil domain is back online with a message.
"They are not the masters they think they are"
"We have the skills and experience"
"Do you want to be with the most qualified or losers?"
*site CSS and PNG indicates this is a defacement
Information courtesy of @marxvolt
🚨ONGOING: we are investigating systems infected with a malicious version of the npm package UAParser.js (7 million weekly downloads).
The hijacked package delivers a malware loader and a cryptominer.
IOCs below:
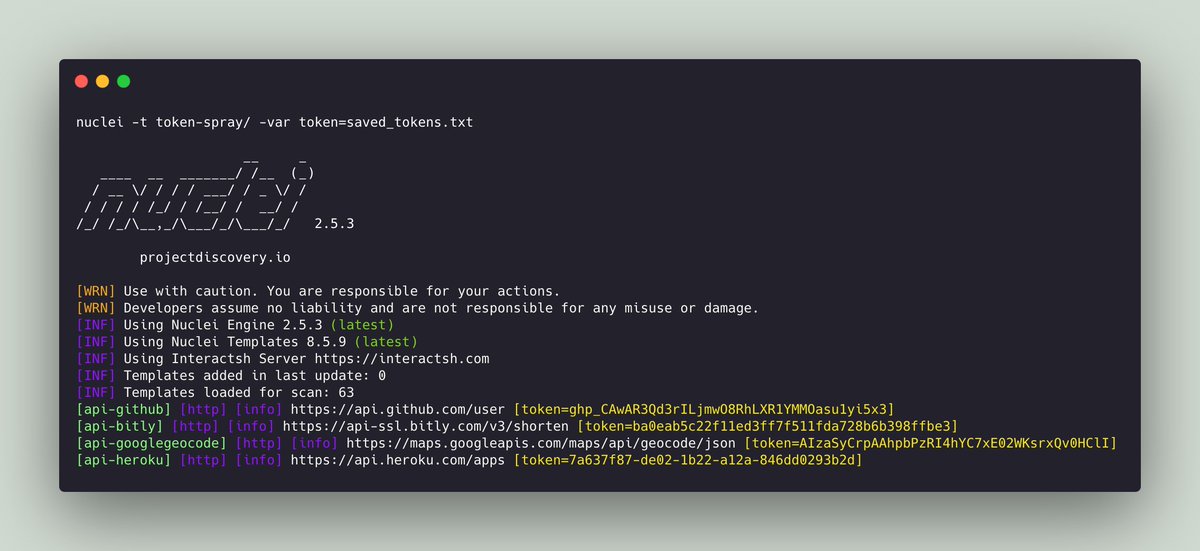
Got random tokens as part of manual search or automation but not sure if the found tokens/keys are valid or which service they belong to? now it's possible to automate the process using nuclei templates.
More details - https://t.co/Aa8CeumaBX
#recon#hackwithautomation
A short thread about what is perhaps the most successful cyber attack in the history of any nation state conducted by a group called “Belarusian Cyber-partisans”. Last month they hacked the servers of Belarusian police and the Interior Ministry. 1/6
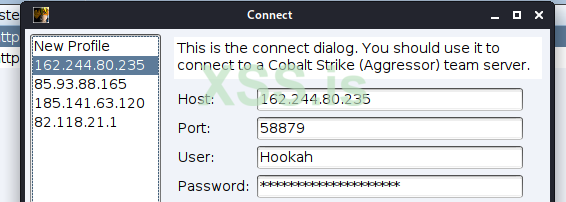
A "pentester" for Conti has leaked "pentester manuals and software" online. These files are allegedly given to affiliates
vxug.fakedoma[.]in/tmp/
* Link modified, Twitters banned our domains
* Some files password protected, we do not know the password
* Images from XSS
tl;dr REvil popped @KaseyaCorp. Abused Kaseya's auto update to conduct supply chain attack that DLL side loads Windows Defender binaries and ransoms the customer
tl;dr tl;dr REvil just pulled off a colossal ransomware supply chain attack
Just saw this, if you spell illuminati backwards, add .com, it redirects to the NSA website:
https://t.co/b4NXqhlizP
Who says the @NSAGov doesn't have a sense of humor!