🚨 Our latest #Ghidrathon release has out-of-box support for Python 3 modules that don’t support multiple Python sub-interpreters running in a single process. e.g. you can now use #PyO3 to run #Rust from #Python 3 from #Ghidra ��. Check it out https://t.co/T1z3igZ0ws
For too long has it been a mild inconvenience to not have the features of GEF in LLDB.
We at Foundry Zero feel you deserve better!
So we ported GEF features to LLDB.
You're welcome.
Read about it here: https://t.co/ZZzGqXlzUX
Find it here:
https://t.co/xgkH84TIuA
New #rustlang h2 release: v0.3.20 🦀
This includes several bug fixes found with additional fuzzing (thanks @f0rki!) Worth an upgrade.
https://t.co/eYV2qhBbAm
one day google is going to randomly kill 8.8.8.8 for no reason and a double digit percentage of the internet as well as major world governments will go down
To avoid incomplete and incorrect citations in papers, I wrote a script to automatically correct BibTex files: https://t.co/7RJxSPQLYX
Just one click: `bibtidy --file "test.bib" --output test_checked.bib`!
The summer school "Cyber in Sophia Antipolis" will take place from July 3rd to 7th
https://t.co/n4wCJVZ6jw
Topic is research on vulnerability discovery and exploitation.
🥁I am looking for students and postdocs:
PhD student // 3 years, fully funded // Fuzzing
https://t.co/7SkWN7RnaI
Postdoc // 3 years, fully funded // Complex software vulnerabilities
https://t.co/vzzjUaGTsC
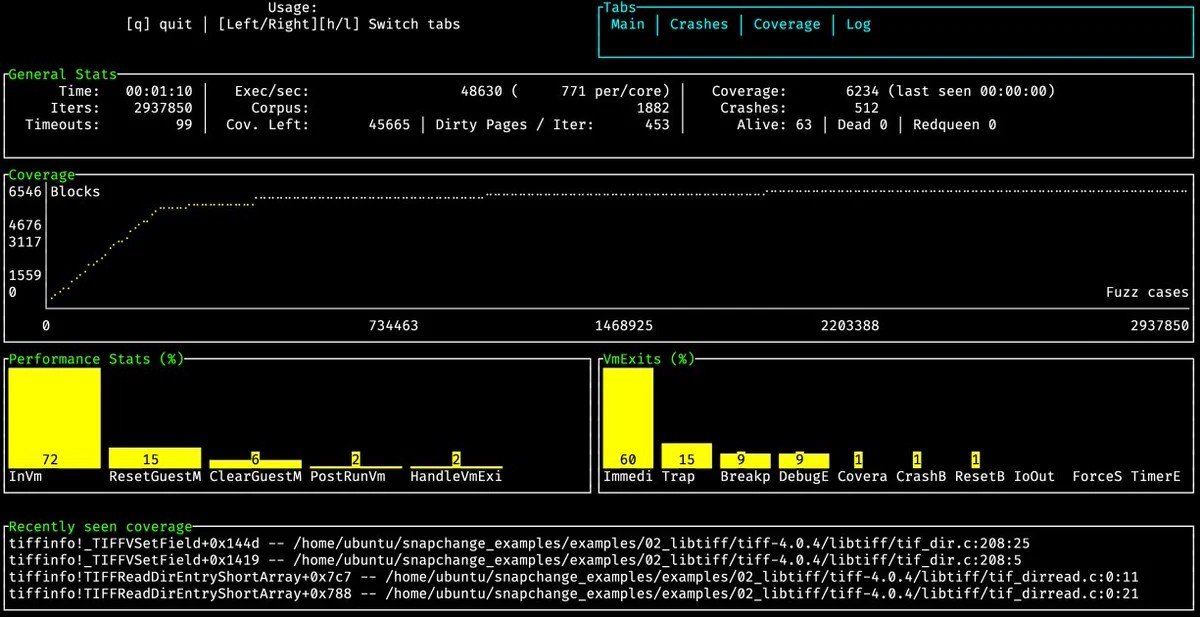
AWS open-sourced a fuzzer. "load a raw memory dump and register state into a KVM virtual machine (VM) for execution. At a point in execution, this VM can be reset to its initial state" https://t.co/yHDO2MiYlz
Today VirusTotal announced that each sample uploaded will be accompanied by "Code Insight". Code Insight uses Sec-PaLM, one of the generative AI models by Google, to explain what the malicious binary is doing.
Code Insight is available to all users.
tl;dr "they took my job"
This is also the main fuzzer driving our initative to secure and harden the Linux kernel for Confidential Computing 🔐!
And it's all on Github ⭐️!
https://t.co/NzJafyYuse
(5/x)
Since the paper is now accepted, time to drop some code :) https://t.co/OHeFH9kXeO
a high perf fuzzer for #ethereum smart contracts based on AFL++, a custom evm2cpp transpiler, a modified eEVM runtime, and a custom mutator for TXs. Oh and it also creates reentrancy exploits.
For example, EF/CF can actually synthesize an rentrancy exploit for the Uniswap/IMBTC incident. One just needs to configure EF/CF to fuzz all relevant contracts in combination.