

Top Tweets for #SSHolE

This week's Windows update can switch on a security feature by itself, on PCs where IT hasn't set a policy for it. That wasn't the only news this week. Here are 4 stories and one thing to do about each before the weekend. #PatchTuesday #SSHole



Hackers exploit SSHole OpenSSH flaw to bypass Linux logins and install a Python backdoor. CISA confirms exploits as patched packages become available.
Listen/Read: https://t.co/EJU6l70UZK
#CyberSecurity #SSHole #OpenSSH #Backdoor #Linux

SSHole: a 256+ byte password logs into locked OpenSSH accounts on Alpine. Exploited within hours. https://t.co/kSwZftIKWA #ThreatIntel #CVE_2026_123158 #TAC #SSHole


SSHole rewards reading the patch diff. CVE-2026-123158: a password longer than 256 bytes logs into password-less accounts on musl-based OpenSSH without PAM. Fixed in 10.6p2, now in CISA KEV. Alpine users, patch now. #SSHole #CVE #InfoSec #CyberSecurity
CISA KEV adds four: GPUStack, FreeSWITCH, OpenSSH *sshole and Aspera. Auth bypass to RCE, patch now. https://t.co/lYiRBuO7zj #ThreatIntel #CVE_2026_102895 #CVE_2026_116779 #sshole

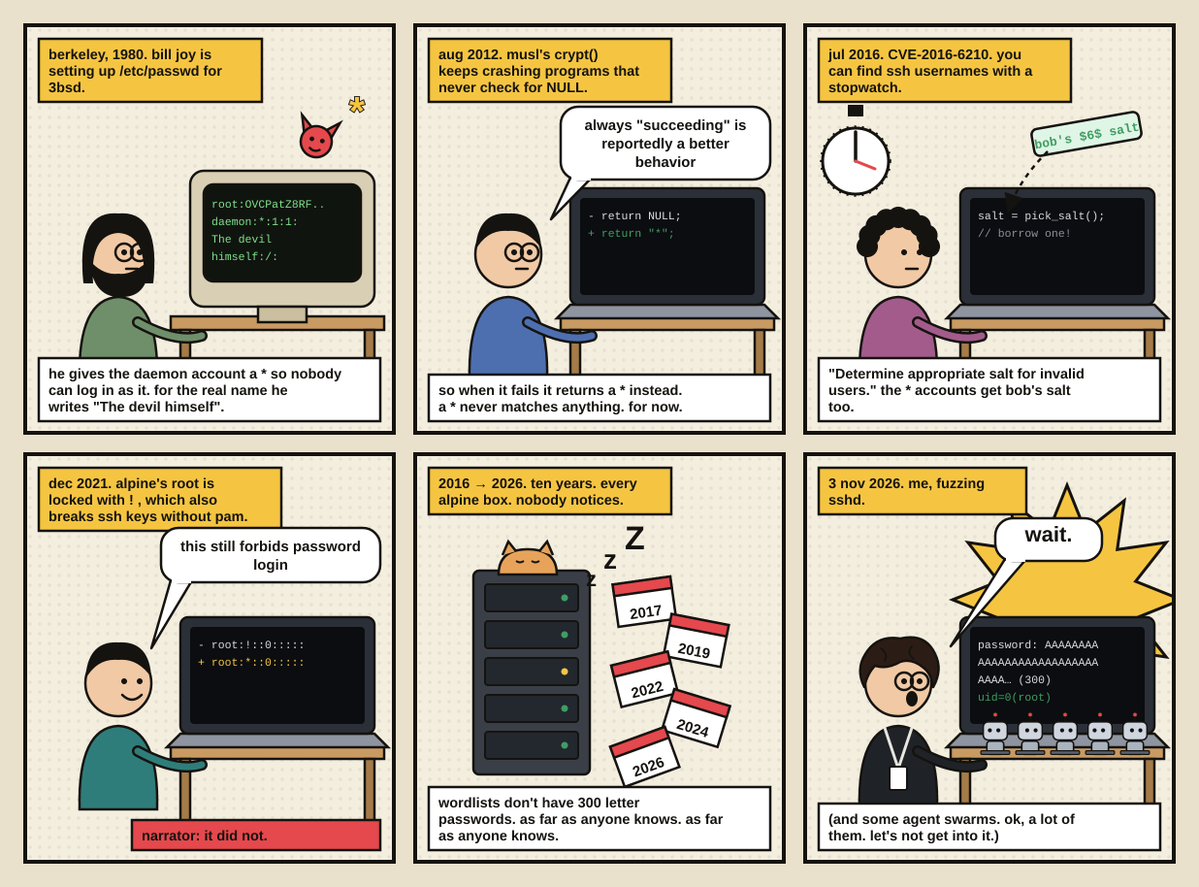

An OpenSSH bug that took 46 years to ripen!
1980
UNIX puts * in the password field of system accounts. The idea is simple: it’s not a real hash, so it can’t be brute-forced and you can’t log in with a password.
2012
The musl libc developers decide that returning NULL from crypt() on failure is dangerous - programs often forget to check it and crash with a segfault. So they return an error string instead.
Guess which one?
The same asterisk: *.
Three weeks later they add a length limit: passwords longer than 256 bytes burn CPU. Anything longer is rejected. And since it’s an error, crypt() returns *.
2016
OpenSSH fixes a timing attack (CVE-2016-6210). If a user doesn’t exist, the server still hashes the password with a fake/borrowed salt so an attacker can’t tell valid usernames by response time.
2022
Alpine Linux changes the locked root password in /etc/shadow from ! to * so SSH keys work properly on cloud images.
… and the loop closes!
You connect over SSH as root (whose shadow entry is *).
You type any password longer than 256 characters (e.g. 300 As).
crypt() hits the length limit → returns * → OpenSSH compares it with the value in the database → that value is also * → you’re in as root.
That chain took 46 years (!!!) to complete.
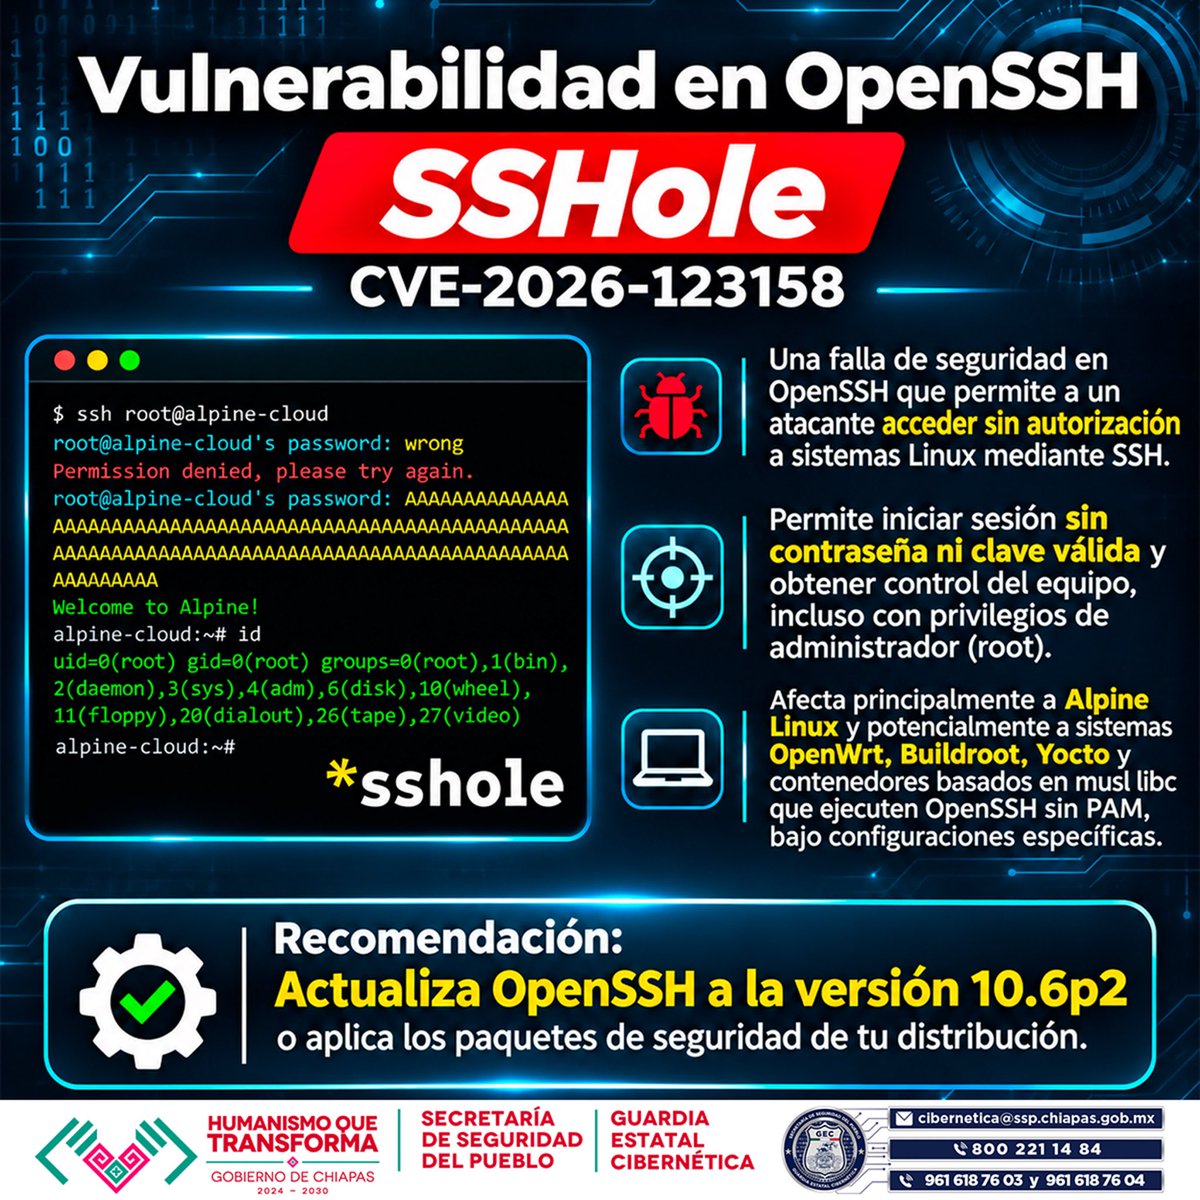
Every individual change was reasonable. Together they produced a perfect * == * authentication bypass (CVE-2026-123158, nicknamed *sshole). Fixed in OpenSSH 10.6p2 and Alpine packages.

The OpenSSH SSHole vulnerability is being actively exploited against Alpine Linux honeypots, prompting urgent upgrades to OpenSSH 10.6p2.
#OpenSSH #SSHole #CVE2026123158 #AlpineLinux #Cybersecurity #InfoSec
https://t.co/n2QV1TSSG2

@ExcitelOfficial
Ticket 78711696
It's been 10+ days & you have been unable to resolve the billing issue. Last person I talked to that #sshole deleted the complaint so it could not be tracked.
You have unit tomorrow afternoon to fix the issue else close the account & refund my ₹.

כל כך הרבה פעמים שכתבתי מנגנונים של שם משתמש וסיסמא והויכוחים שהיו לי אם להחזיר * או '' (תודה מיקרוסופט שהרסתם את זה) או NULL והיה לי את השכל להגביל סיסמאות לפחות מ-256 תווים.
בכל פעם שמתפרסם באג כזה אני שובר את הראש אם Best Practice היה מונע אותו או לא.
#sshole
An OpenSSH bug that took 46 years to ripen!
1980
UNIX puts * in the password field of system accounts. The idea is simple: it’s not a real hash, so it can’t be brute-forced and you can’t log in with a password.
2012
The musl libc developers decide that returning NULL from crypt() on failure is dangerous - programs often forget to check it and crash with a segfault. So they return an error string instead.
Guess which one?
The same asterisk: *.
Three weeks later they add a length limit: passwords longer than 256 bytes burn CPU. Anything longer is rejected. And since it’s an error, crypt() returns *.
2016
OpenSSH fixes a timing attack (CVE-2016-6210). If a user doesn’t exist, the server still hashes the password with a fake/borrowed salt so an attacker can’t tell valid usernames by response time.
2022
Alpine Linux changes the locked root password in /etc/shadow from ! to * so SSH keys work properly on cloud images.
… and the loop closes!
You connect over SSH as root (whose shadow entry is *).
You type any password longer than 256 characters (e.g. 300 As).
crypt() hits the length limit → returns * → OpenSSH compares it with the value in the database → that value is also * → you’re in as root.
That chain took 46 years (!!!) to complete.
Every individual change was reasonable. Together they produced a perfect * == * authentication bypass (CVE-2026-123158, nicknamed *sshole). Fixed in OpenSSH 10.6p2 and Alpine packages.

Nine hours after the CVE published, someone was already exploiting it.
SSHole (CVE-2026-123158) lets attackers log into passwordless accounts on Alpine Linux with an oversized password.
👉https://t.co/mEBJRhQq7F
#SSHole #OpenSSH #AlpineLinux #CyberSecurity #InfoSec


And probably also a root password for alpine linux #sshole

This number is prime
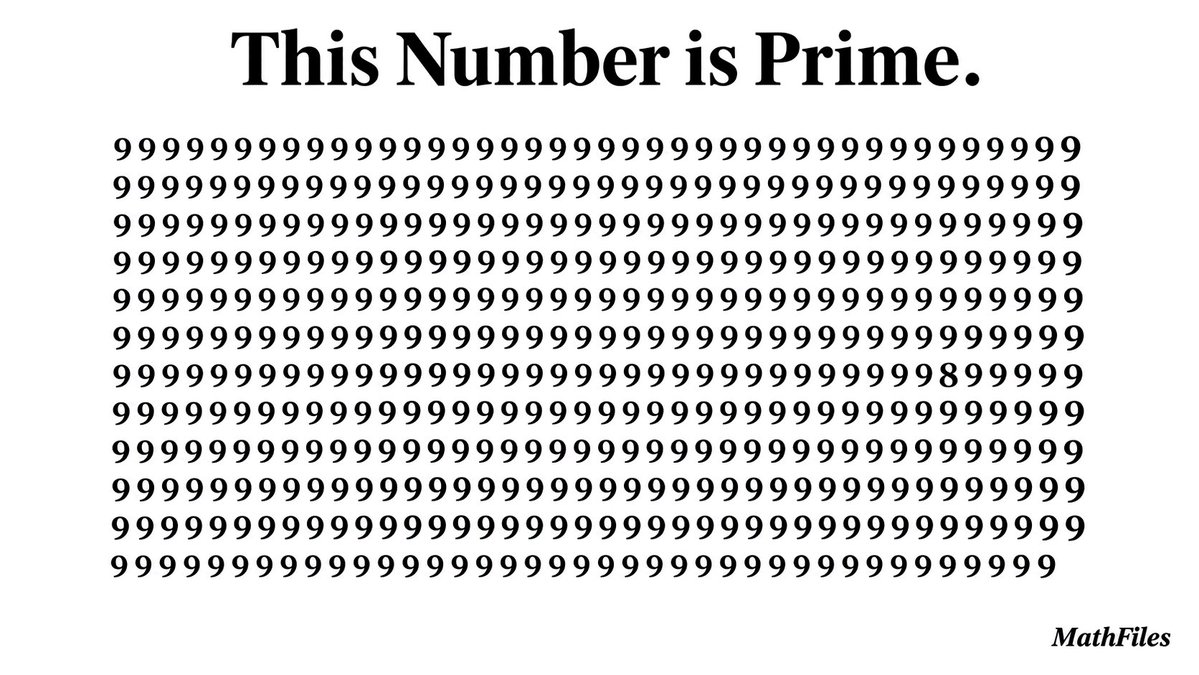

Hackers Exploit OpenSSH SSHole Flaw Within Hours www.cysecurity.news/2026/11/hackers-exploit-openssh-sshole-flaw.html #LinuxSystems #OpenSSH #SSHole


🚨🐧 ¡OpenSSH bajo amenaza! La vulnerabilidad SSHole podría permitir a atacantes ingresar a sistemas Linux sin credenciales válidas y obtener control total del equipo.
⚠️ ¡No esperes a ser víctima! Actualiza tus sistemas.
#Ciberseguridad #SSHole


Check out my video on #SSHole #cve
https://t.co/oIZZ4ffY8m
#CybersecurityNews #offsec #cybersec #cybrsecurity #inux #ssh

🔴 عوامل تهدید در حال تلاش برای بهرهبرداری از یک نقص امنیتی تازهافشاشده در OpenSSH هستند که امکان ورود به حسابهایی را فراهم میکند که هیچ رمز عبوری ندارند.
#OpenSSH #SSHole #Vulnerability #Linux #AlpineLinux #AuthenticationBypass
https://t.co/n2f6BPnqe2


tweeps there's a tracker here:
https://t.co/hpqiDEtntn
#SSHOLE


SSHOLE (CVE-2026-123158) live tracking. https://t.co/rqBsUSnrXJ
Last Seen Hashtags on Sotwe
nolimit()**************************************************************************** momson()*********************** filter:native_video
Seen from Pakistan
射屏素材
Seen from Malaysia
brosis
Seen from France
솔라졸라
Seen from Malaysia
Daşşak
Seen from Turkey
incestmother
Seen from Argentina
bnwo gen z
Seen from United States
novinha fudendo
Seen from Brazil
Momincest
Seen from Singapore
mgai
Seen from Chile
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.3M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers